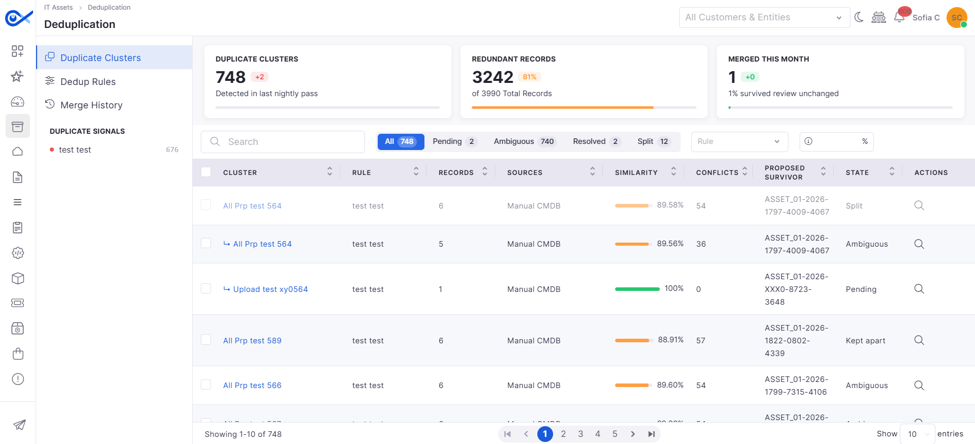
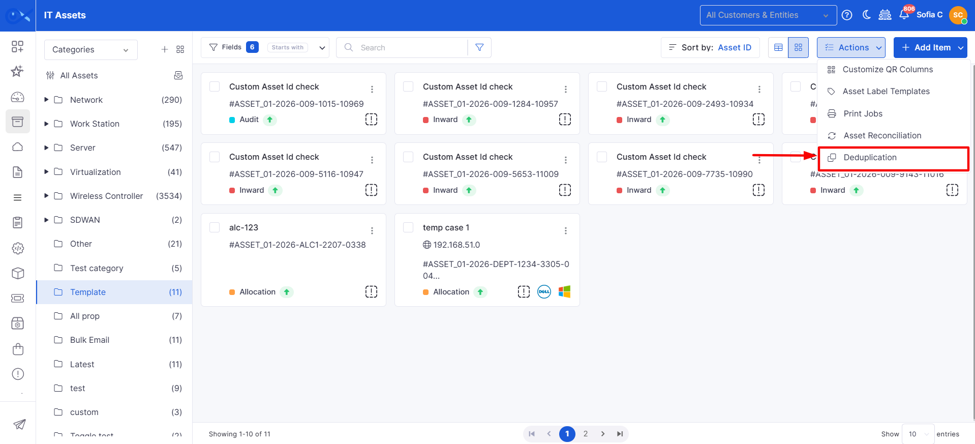
The Infraon Admin Guide is explicitly designed for administrators responsible for configuring, managing, and maintaining the Infraon platform. This guide focuses on modules and functionalities exclusive to the Management Admin role, such as system configuration, user management, and platform settings.
Why do I see only a few modules here?
This guide includes only those modules and features that are exclusive to Management Admin users, such as:
Platform Configuration
User & Role Management
System Settings
The remaining modules are shared between both users and admins. To avoid duplication and provide a clear, role-based experience, these shared modules are documented under the section.
If you’re an Admin looking for detailed documentation on all other modules:
Navigate to the for technician-level modules and operational features.
Use the left-side navigation menu to explore topics by module.
Use the search bar at the top of the page to quickly find specific content.
Administrators can customize employees' web addresses (URLs) to access the Infraon Infinity portal. This functionality provides greater flexibility and branding opportunities.
For instance, instead of using a generic URL provided by Infraon, administrators can create a custom URL that reflects your organization's name.
This customization enhances brand recognition and potentially improves user experience by making the helpdesk URL more easily recognizable to employees.
Admins can choose a user-friendly and memorable option, such as "EverestIMS" for your full company name or "EIMS" for a shorter version.
User's first login
User(s) can self-register on Infraon when they receive an invitation from the administrator(s). Click on the link, add details, and Voila! You are all set.
Please contact your administrator or manager if you cannot view any Infraon modules/pages.
When you first log in, Infraon offers options to customize your theme.
Please note that your Administrator/Manager has predefined your role-based privileges.
Know Infraon!
Once the initial customization is saved, you can use Infraon. Your default landing page looks like the below:
There are three default sections across all Infraon modules/pages.
Let's see these in detail:
Top Panel
The top panel has the below options to view:
Left Menu Panel
The left menu panel can be expanded to view menu labels.
Notification Icon
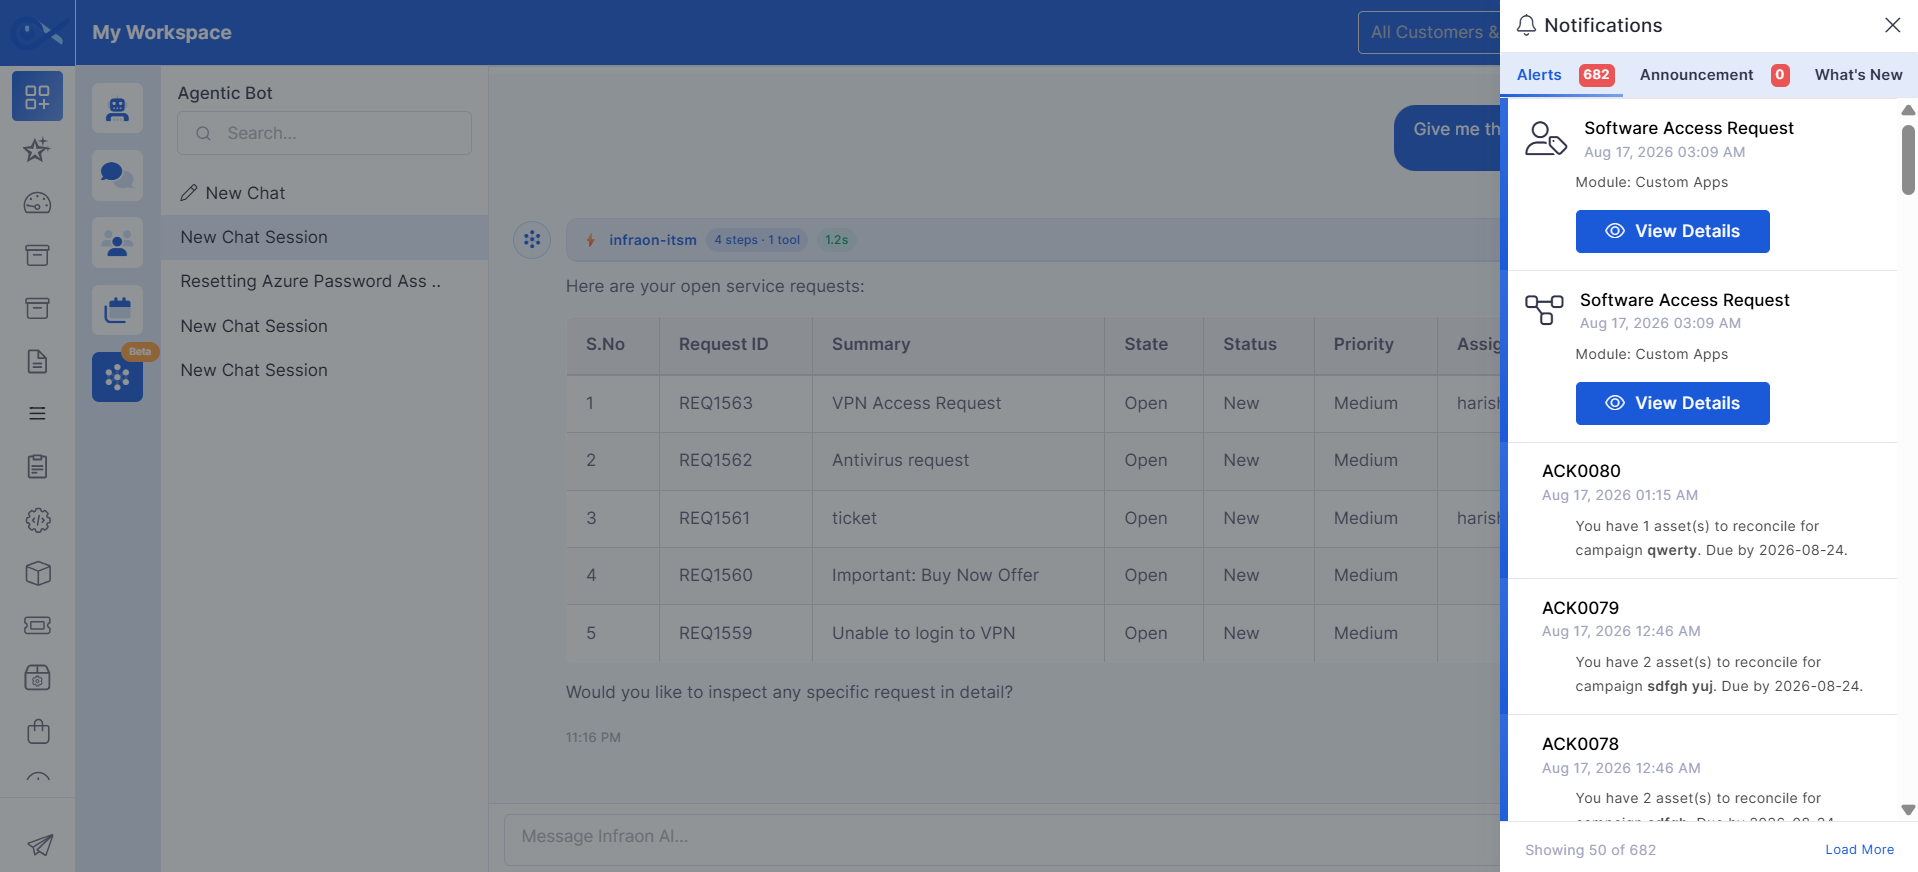
A notification icon, visible across all Infraon modules, displays your number of new alerts. Clicking this icon reveals a panel containing both informational updates and task-related notifications.
In the section, you can view messages from this panel, approve or reject requests, and check product updates. The panel includes alerts and information about recent changes or additions to the product.
Alerts
The Alerts tab displays notifications generated by the system for events that require user attention or provide updates on system activities. Alerts help users stay informed about approvals, asset activities, SLA events, workflow updates, and other configured notifications.
What's New
SW Metering Summary
Once Software Metering rules are configured and data is collected from agents, the Software Metering Summary page provides an aggregated view of application usage across devices. This view helps analyze how frequently applications are used, for how long, and across how many endpoints.
For each rule, the summary grid displays:
Label
Action
Description/ Example
Click the View icon to drill down into device-level usage details for the selected application.
This view displays:
Label
Action
Description/ Example
Click on the Usage Count value to open a detailed usage view for the selected asset.
This section provides:
Graphical Representation
View usage trends using a Bar Chart or a Line Chart
Displays day-wise usage distribution
Tooltip shows date and usage duration (hours/minutes)
Additional capabilities:
Switch between chart types for better visualization
Export the chart as an image for reporting and analysis
Mobile Device
The Mobile Device sub-module allows you to manage and monitor mobile assets, including Android and iOS devices.
Devices are automatically discovered when the mobile agent is installed and configured with the organization key. Once registered, the device is added as an asset and categorized based on its operating system.
The module provides visibility into device details, hardware information, installed applications, and location data (if enabled). It helps track mobile assets and ensures that device information is kept up to date through periodic agent synchronization.
Mobile device management is enabled through the mobile agent installed on the device.
Install the mobile agent on the device.
Usage Count
View only field, no actions can be taken
Number of times the application was opened on that device
Duration
View only field, no actions can be taken
Total usage time for that device
Process-Level Details
Date – When the application was used
Process ID (PID) – Unique process instance
Application Start Time
Application End Time
Each process instance is tracked separately, even for the same day
Rule Name
View only field, no actions can be taken
Name of the configured metering rule
Application Name
View only field, no actions can be taken
Tracked application under the rule
Usage Count
View only field, no actions can be taken
Total number of times the application was opened
Total Instance
View only field, no actions can be taken
Number of devices on which the application was used
Duration
View only field, no actions can be taken
Total usage time aggregated across all devices
Asset Name
View only field, no actions can be taken
Unique device where the application is used
Application Path
View only field, no actions can be taken
View Summary (Node Details View)
Additional capabilities:
Search and filter data by asset name, usage count, or duration
Ensures unique asset entries without duplication
Supports date range filtering for refined analysis
Usage Analysis
Executable path of the application
Enter the organization key during setup.
The device registers with the system and is added under the Mobile Device section.
Devices are automatically categorized into Android or iOS based on the operating system.
The agent periodically syncs data with the system to update device details.
Based on the configured settings, the agent collects and updates:
The collected data is displayed in the respective tabs within the mobile device details page. Any configuration changes are applied during subsequent agent sync.
The Mobile Asset View page provides detailed information about a selected mobile device. It displays device details, ownership information, hardware data, installed applications, and location information (if enabled).
The information is organized into tabs such as Details, Hardware, and Application, allowing you to view specific aspects of the device. Data displayed on this page is collected by the mobile agent and updated periodically during agent synchronization.
Mobile Asset | Basic Details
Label
Action
Description / Example
Search
Enter the keyword in the search bar
Search mobile assets based on asset name, IP address, or other identifiers.
Filter
Click the filter icon → Select field and condition → Apply Filter
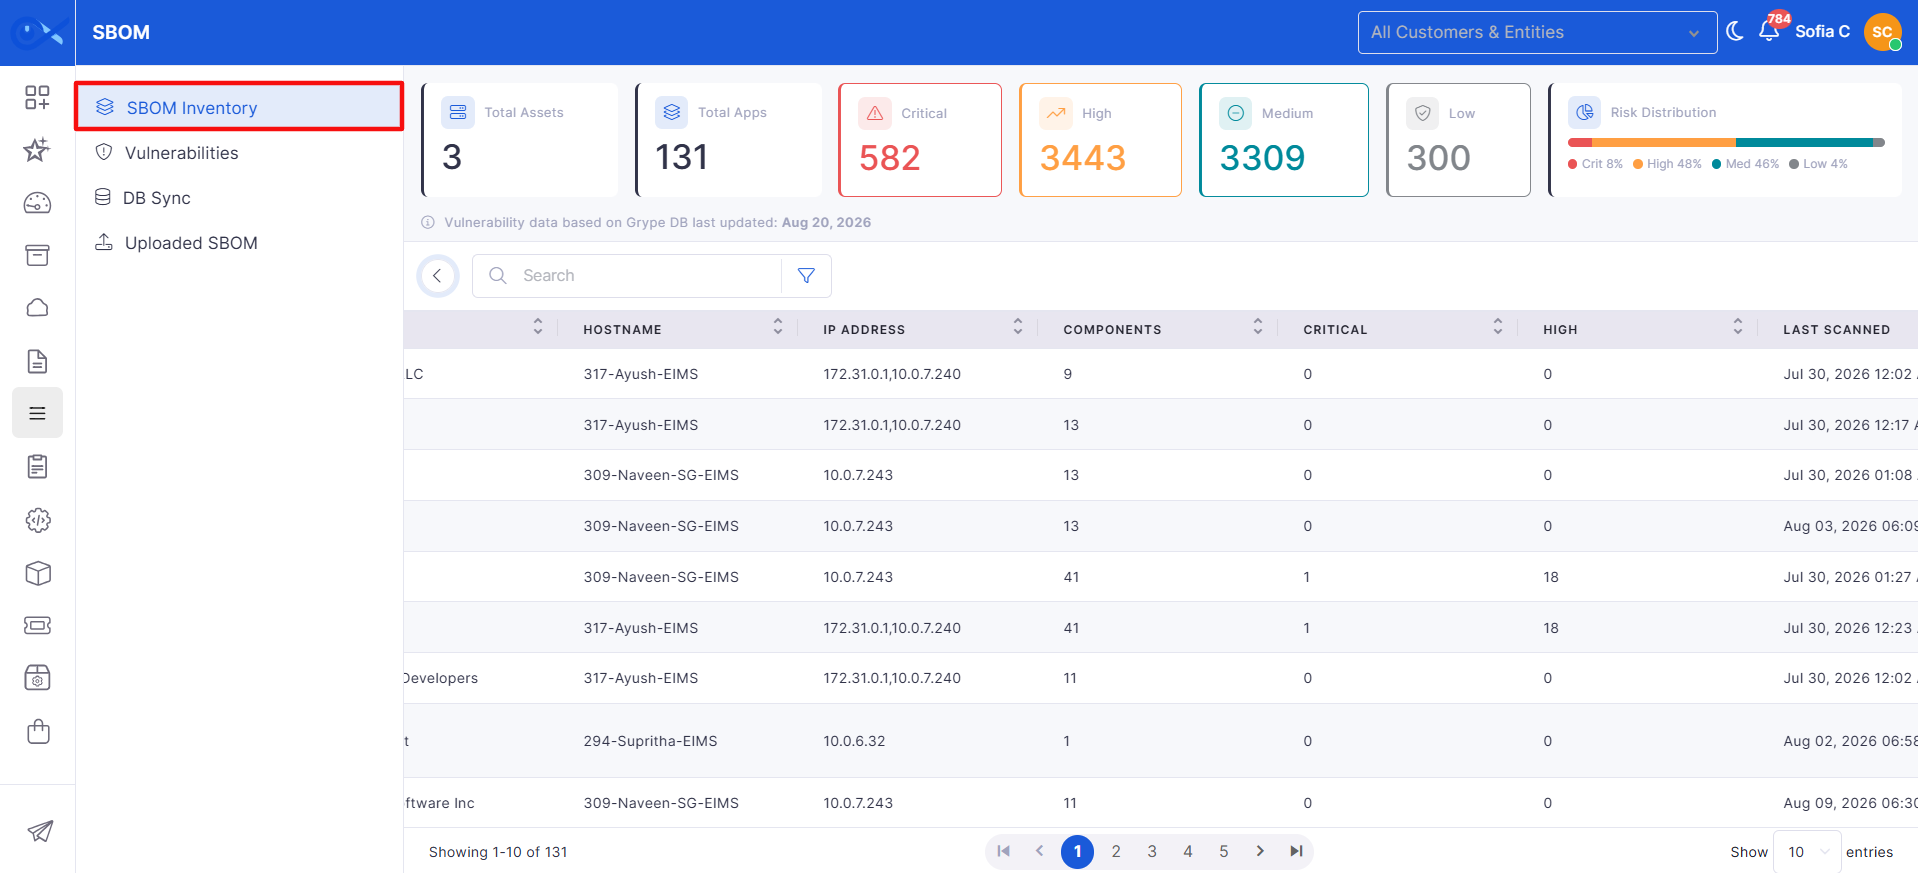
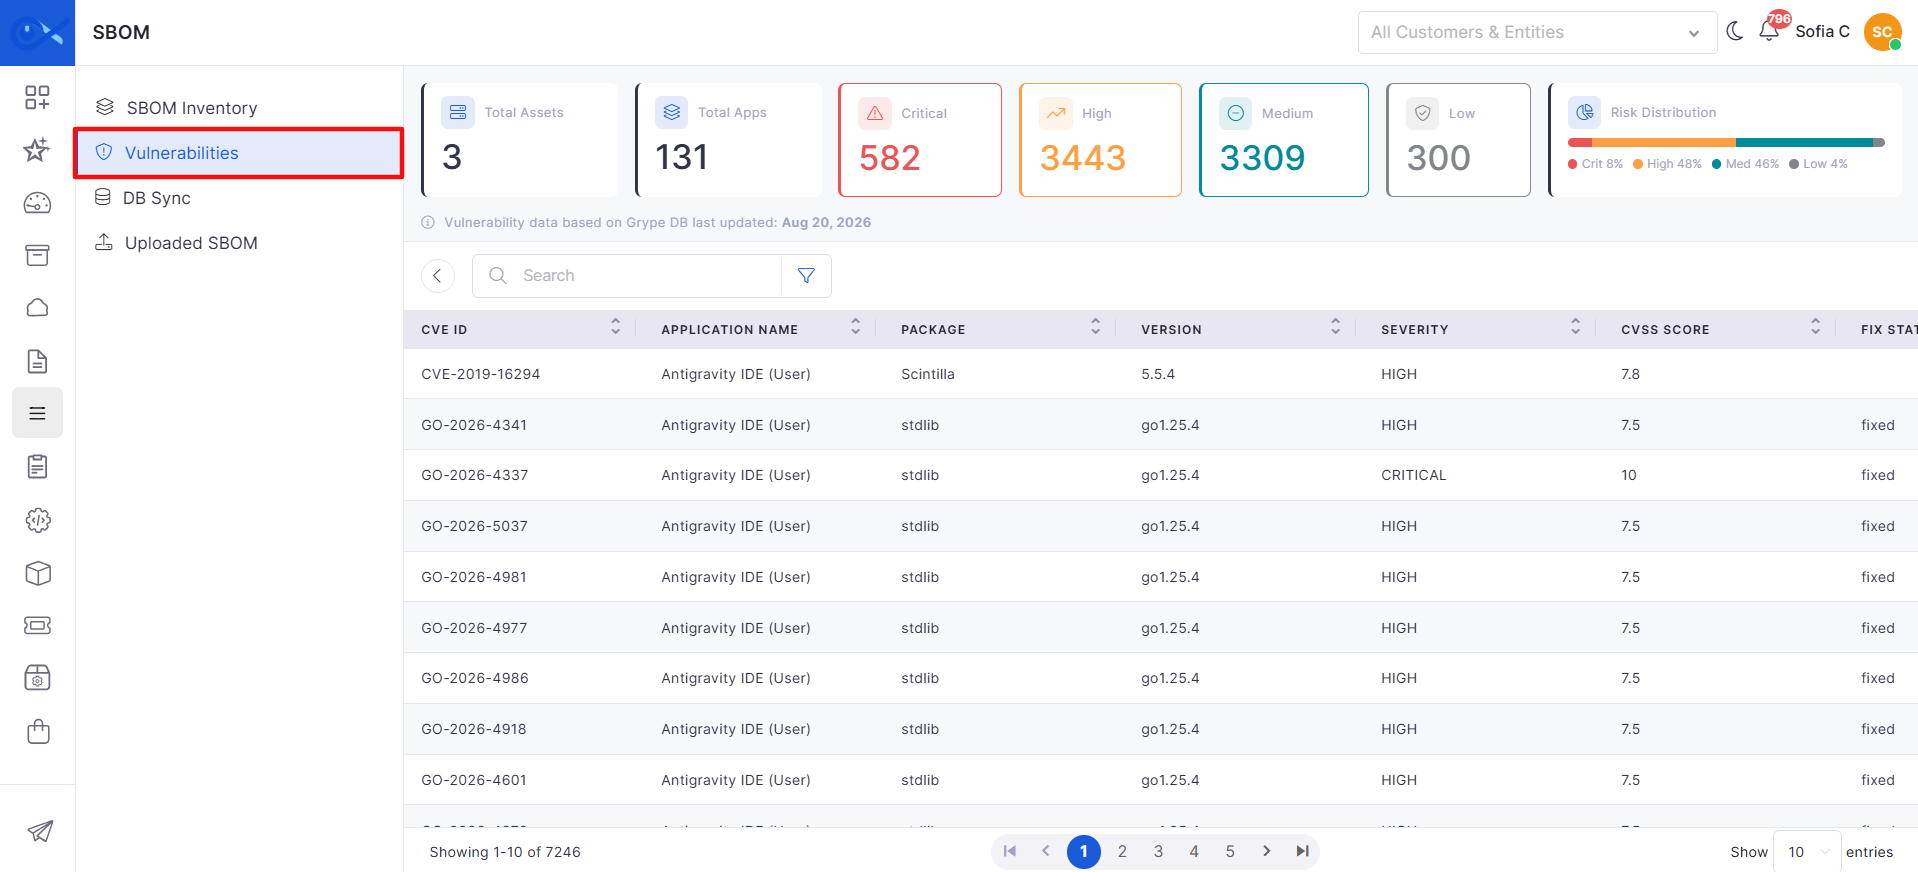
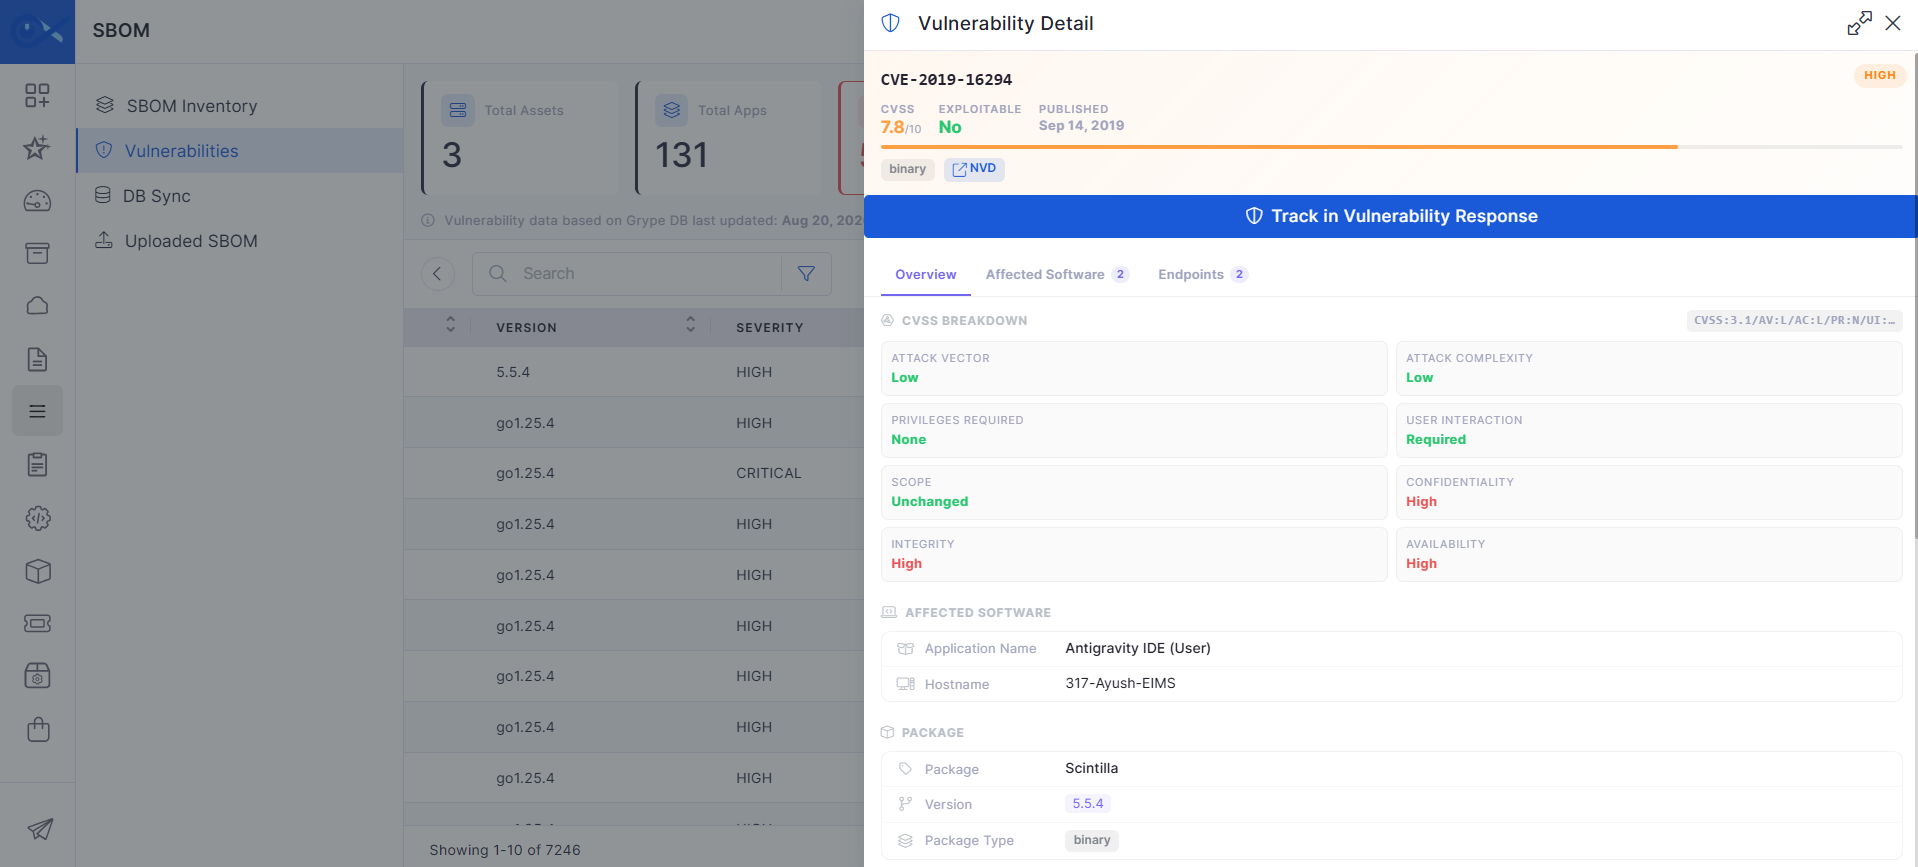
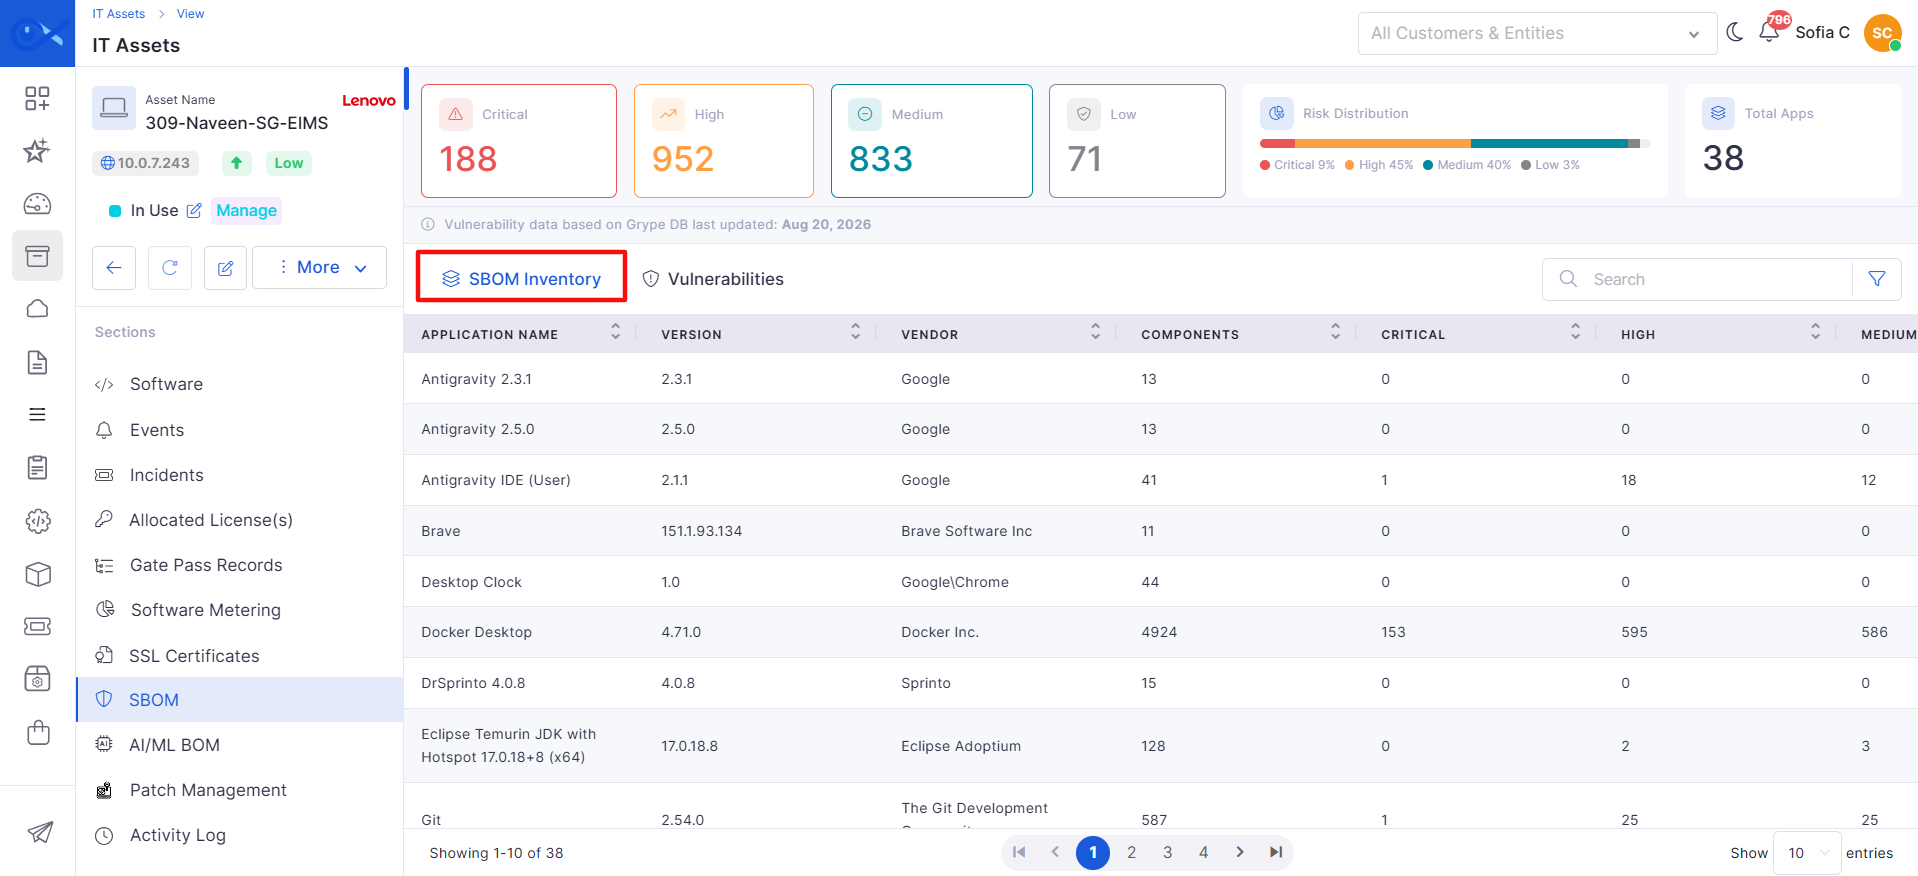
SBOM provides a consolidated view of applications, software components, assets, and vulnerability information, enabling users to review software composition and assess associated risks.
Top Panel Details
Label
Action
Description / Example
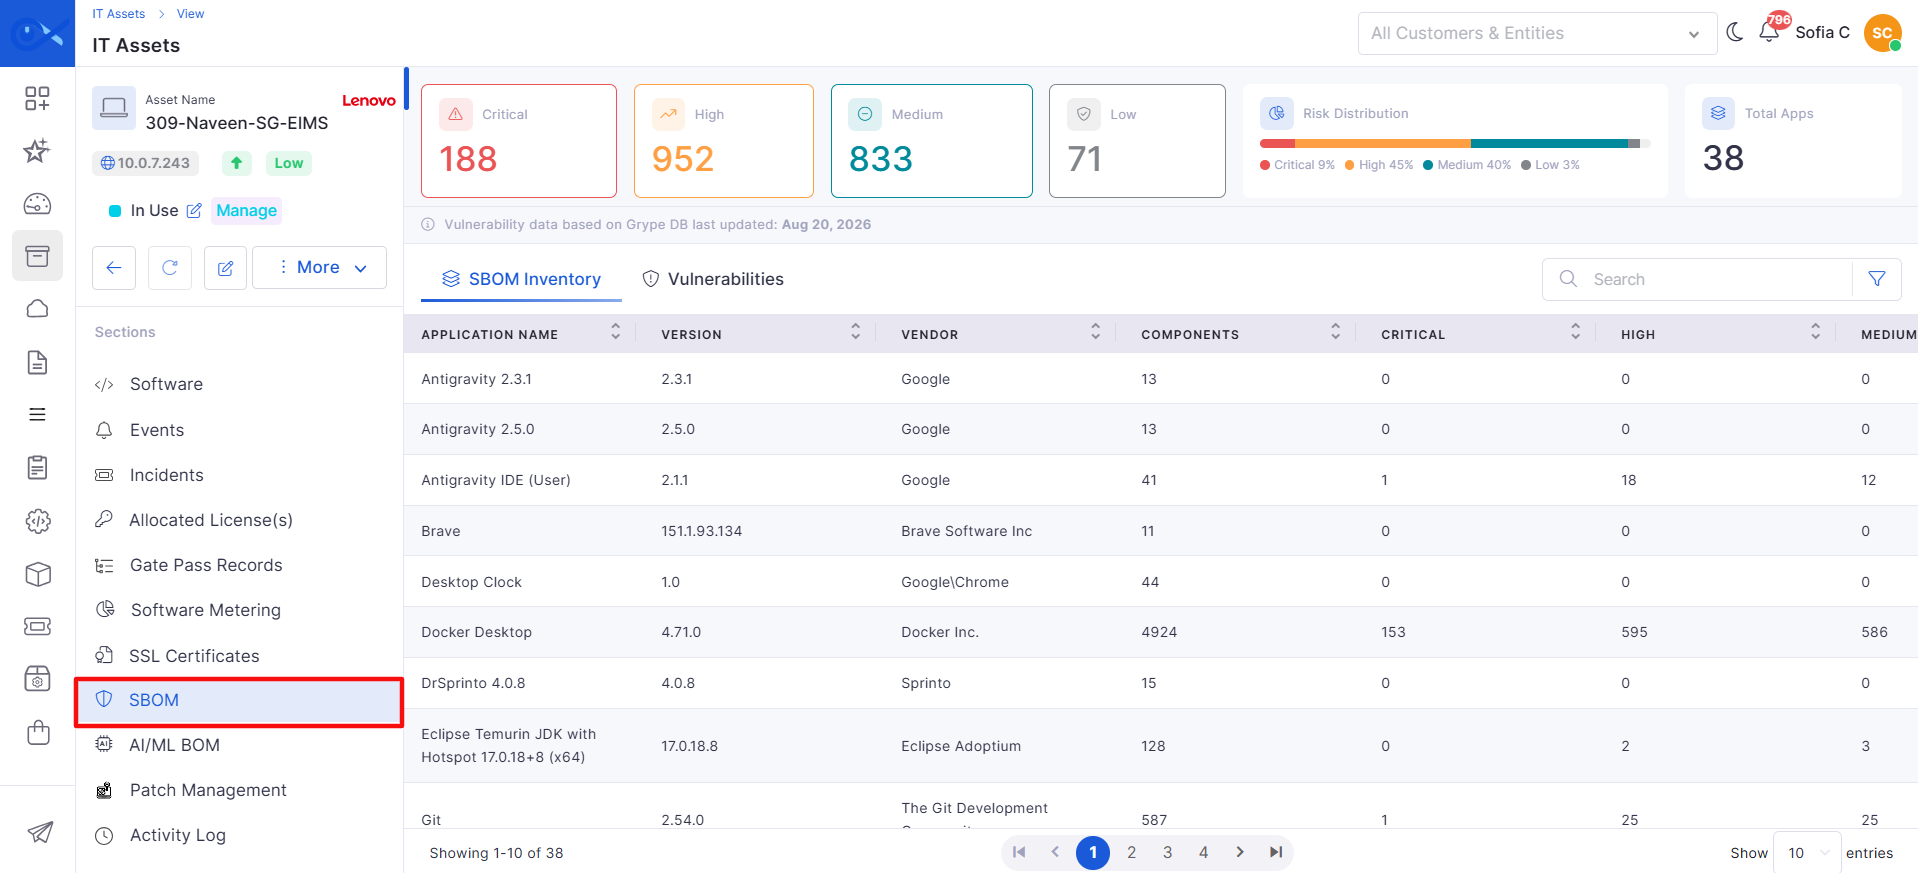
Critical
View
Displays the total number of Critical vulnerabilities identified across the scanned assets.
High
View
Displays the total number of High vulnerabilities identified across the scanned assets.
Medium
View
Displays the total number of Medium vulnerabilities identified across the scanned assets.
Low
View
Displays the total number of Low vulnerabilities identified across the scanned assets.
Risk Distribution
View
Displays a stacked bar chart representing the distribution of vulnerabilities across different severity levels.
Total Apps
View
Displays the total number of distinct applications identified across the scanned assets.
Total Assets
View
Displays the total number of assets that have been scanned.
Filter mobile assets using fields such as CI ID, Asset Name, Asset ID, Agent Name, etc.
Mobile Device Configuration
Click to open the configuration sidebar → Enable/Disable toggles → Click Save
Allows you to control what data the mobile agent collects at the organization level.
Location: Collects the installed location, current location, and location history to track assets.
Device Details: Collects device model, OS, and general device information.
Security Details: Collects security posture, vulnerabilities, and compliance-related data.
Sensor Details: Collects sensor data, including battery status and connectivity information.
SIM Details: Collects SIM-related information such as status and provider.
Hardware Details: Collects hardware-related data, including device status and recovery details.
Network Details: Collects network information such as IP address and network type.
Battery Details: Collects battery health, charging status, and related metrics.
Only the enabled configurations are collected and synced by the mobile agent.
Actions
Scan, Search Asset, and Add Asset
Search by barcode: type the asset's code.
To scan and search for an asset, click the 'Scan and search asset' option, then use your phone to scan the QR code to initiate the asset search.
Export
Click to choose the category.
To export the data, click the 'Export' button, then choose the desired category, and finally download the CSV file containing the selected data.
Bulk Edit
Go to the Infraon Asset Card page -> Actions -> Bulk Edit.
Select the Category.
Download the CSV file (Excel sheet) and enter the Asset details in the sheet.
Upload the same edited CSV file.
Click Next -> Import -> Proceed with Valid Records.
To edit multiple assets' information or details at once.
After completing the registration process, log in using the default credentials provided or opt for a Google account login.
For more details on login options, refer to the Login Settings.
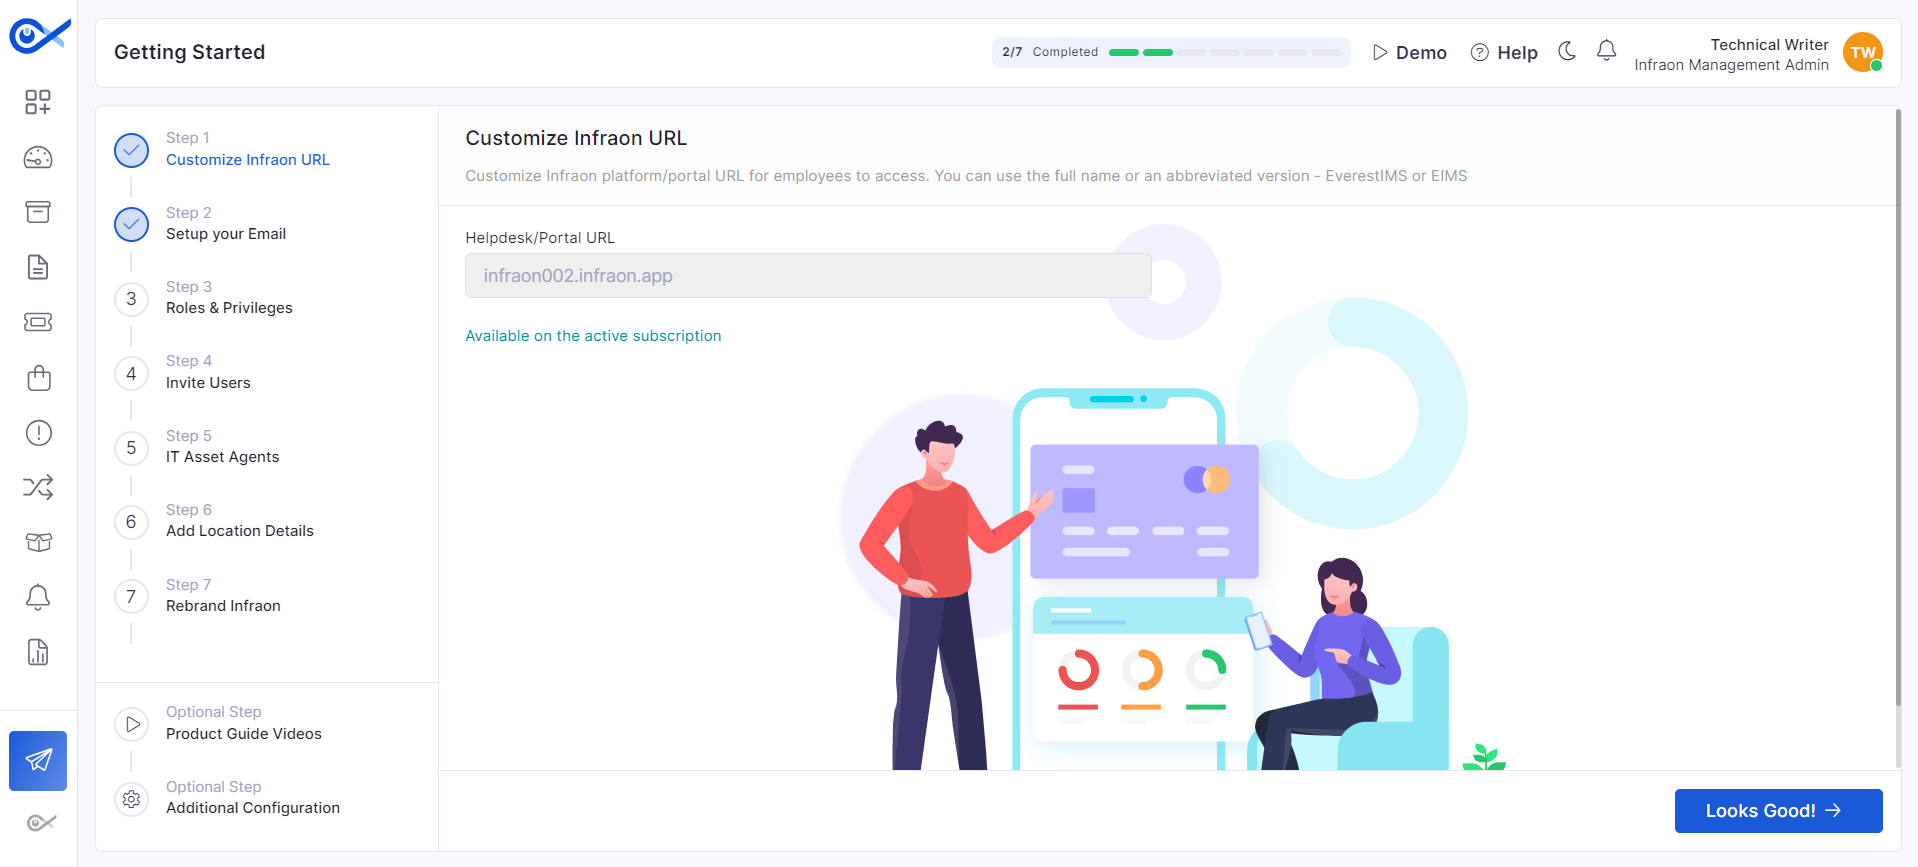
Once logged in, you will be directed to the screen below.
The' Getting Started' page lets you easily configure essential settings for new accounts. There are seven key steps in this process:
Customize the portal URL to allow your employees easy access to Infraon. Although it's recommended to stick to the default URL, you can modify it later if needed.
For more information on customizing the URL, refer to the module.
Configure a dedicated support email address to ensure all incoming communications are automatically converted into tickets. This address will also be used for all customer-related responses. You can set up a new email on Infraon's domain or link your existing mail server.
For step-by-step instructions, visit the module.
General Settings
The general settings module is a part of Infraon Configuration and is accessible by administrators and other users authorized by administrators.
This module of Infraon consists of three additional modules. They are:
Audits: Infraon monitors and records every user's actions. Only the administrator can access these audits.
Business Hours: Configure business hours to control SLAs and better efficient work allocation.
Tag Management: Tagging is a way of grouping assets, users, etc. Tags can be applied to multiple categories across Infraon.
Let's see each of these in detail.
Geomap
Geomap allows for visualization of the location of all the assets by associating a geographic area with GPS coordinates. It enables you to visualize the location of the assets and also provides information about their working condition.
Geomap makes managing assets, identifying opportunities, and providing quick service easy. If the technician's location matches the asset location, assigning the technician becomes straightforward, resulting in a quick resolution. Prompt service, in turn, enhances the customer experience.
Getting Started
This section will guide you through the initial setup and configuration of Infraon Platform, helping you get up and running with the platform's key features. Follow these steps to customize your Infraon experience and manage your product effectively.
Infraon utilizes a dynamic, role-based access control system, offering various default roles with pre-defined access levels such as view, add, edit, delete, and copy. Based on organizational needs, administrators can create new roles, modify existing ones, or delete defaults. Default role names can also be edited.
Adding users to Infraon is simple. You can invite users by entering their email addresses and assigning them roles. When adding multiple email addresses, separate them with commas. You can invite multiple users across different roles simultaneously, but only pre-defined roles can be assigned.
Learn more in the module.
This step allows administrators to deploy Infraon agents—such as inventory agents and data collectors—that efficiently extract data from desktops and network devices.
You can input your organization's head office, branch office, and other addresses here. Providing this information simplifies the alignment of users, assets, and services across multiple locations.
For further details, consult the Address Book module.
Personalize Infraon by customizing its appearance to match your organization's branding. You can change the theme, adjust the colors of the navigation bar and containers, and select your preferred language. Preview changes in real-time and save your favorite look.
A Software Bill of Materials (SBOM) provides an inventory of software applications, components, and dependencies identified across assets. It helps users understand what software is installed, which components are associated with each application, and the vulnerabilities identified in those components. The SBOM data is presented at the organization level in the SBOM module.
How does SBOM work?
SBOM data is collected from scanned assets and used to identify applications and their associated software components and vulnerabilities. For example, if an asset has 7-Zip installed, the SBOM inventory can show the application, its version and vendor, the components or dependencies associated with it, and the vulnerabilities identified for those components. Users can then select the application to view its detailed information.
What do you see on the screen?
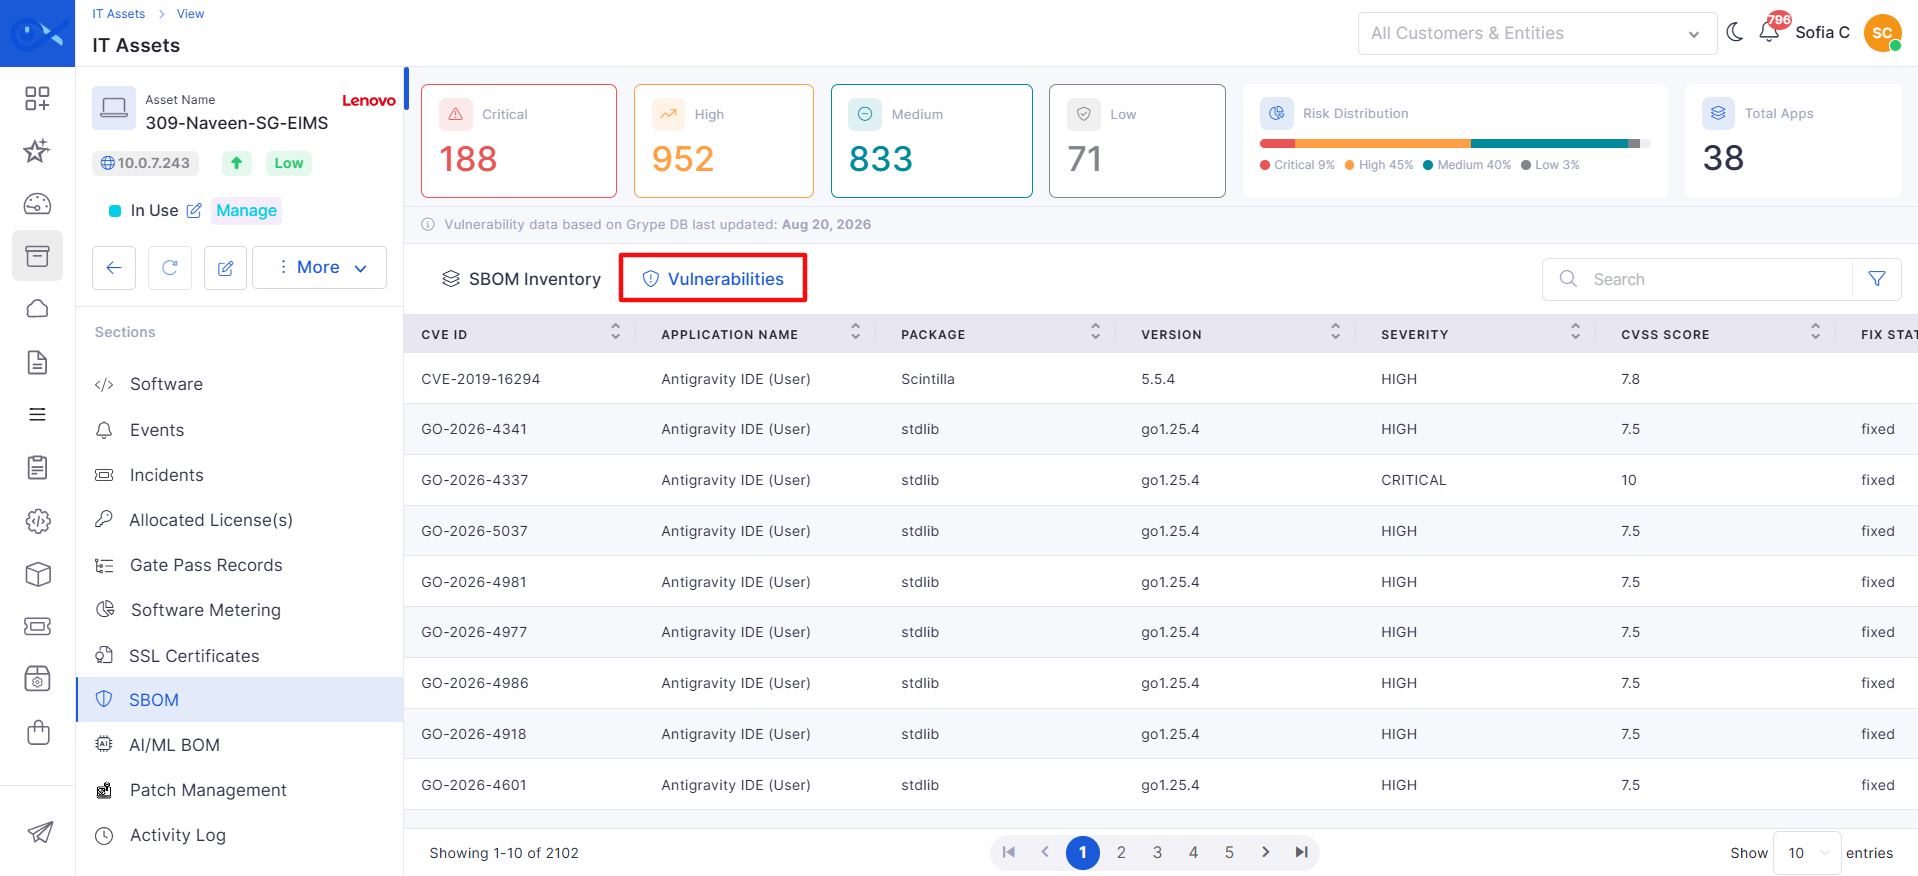
When you open the SBOM module, the SBOM Inventory page is displayed. The page contains summary cards at the top, followed by the inventory table. The left navigation also provides access to Inventory and Vulnerabilities.
SBOM Inventory | Basic Details
Label
Action
Description/Example
The inventory table provides application, asset, component, vulnerability, and scan information, allowing users to identify the software installed across scanned assets.
Label
Action
Description/Example
Column Details | Action Icons
Label
Action
Description/Example
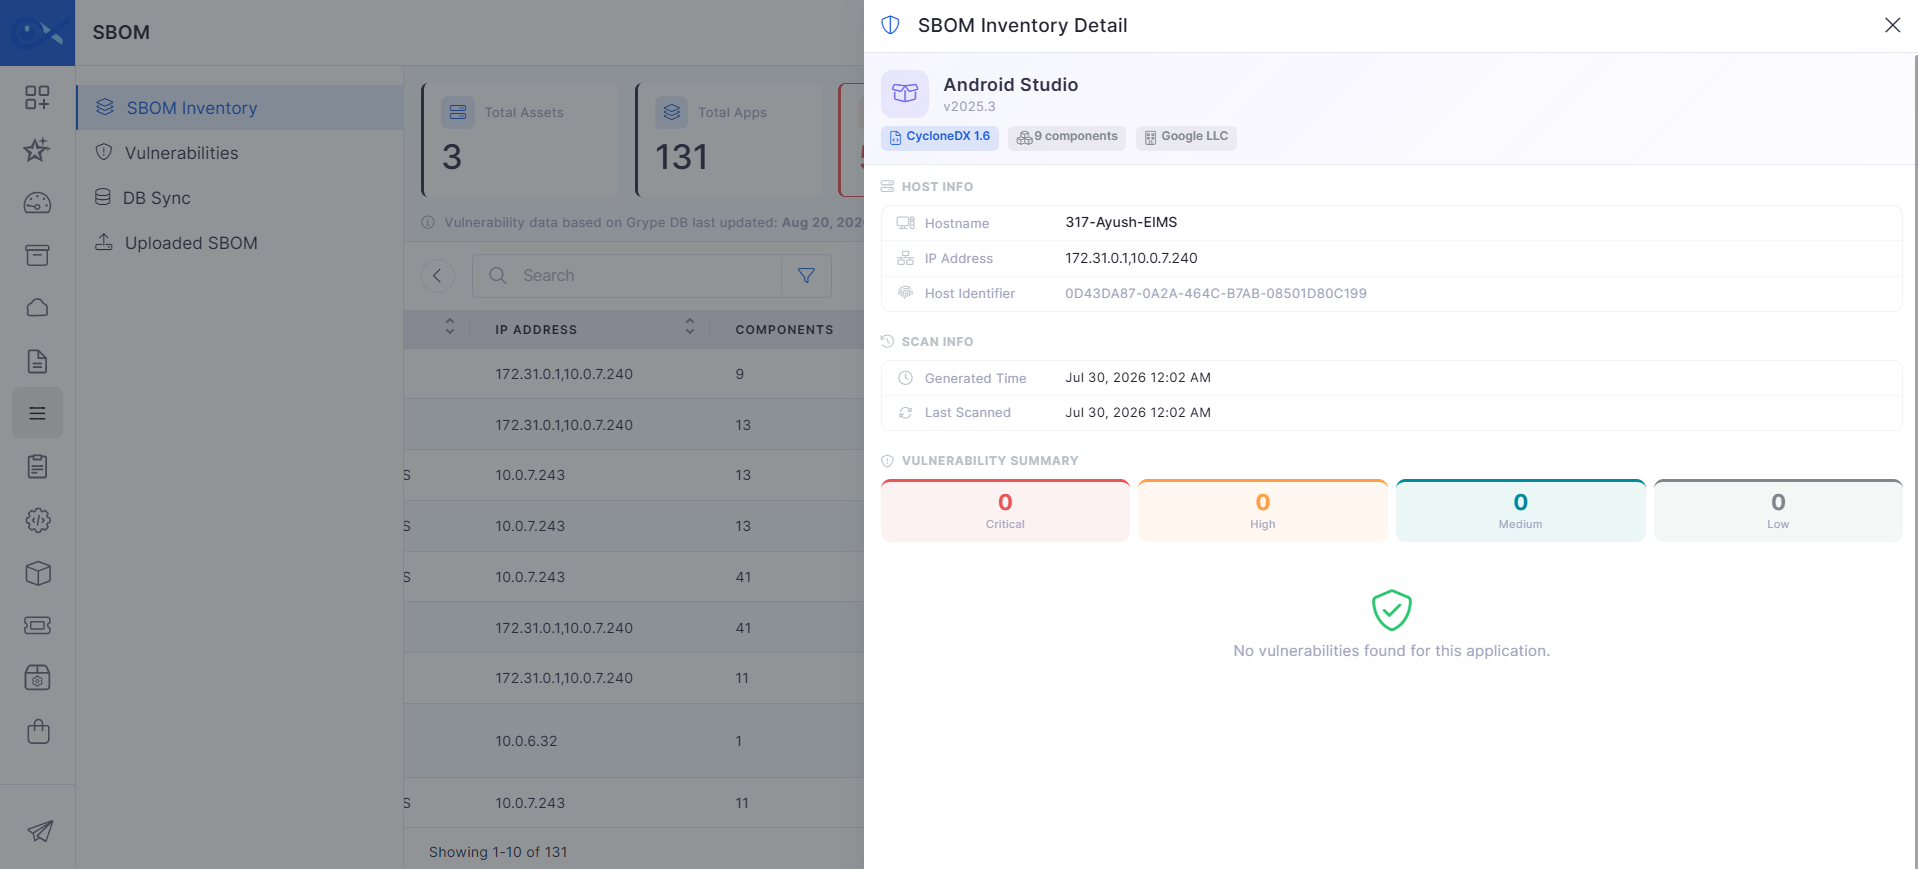
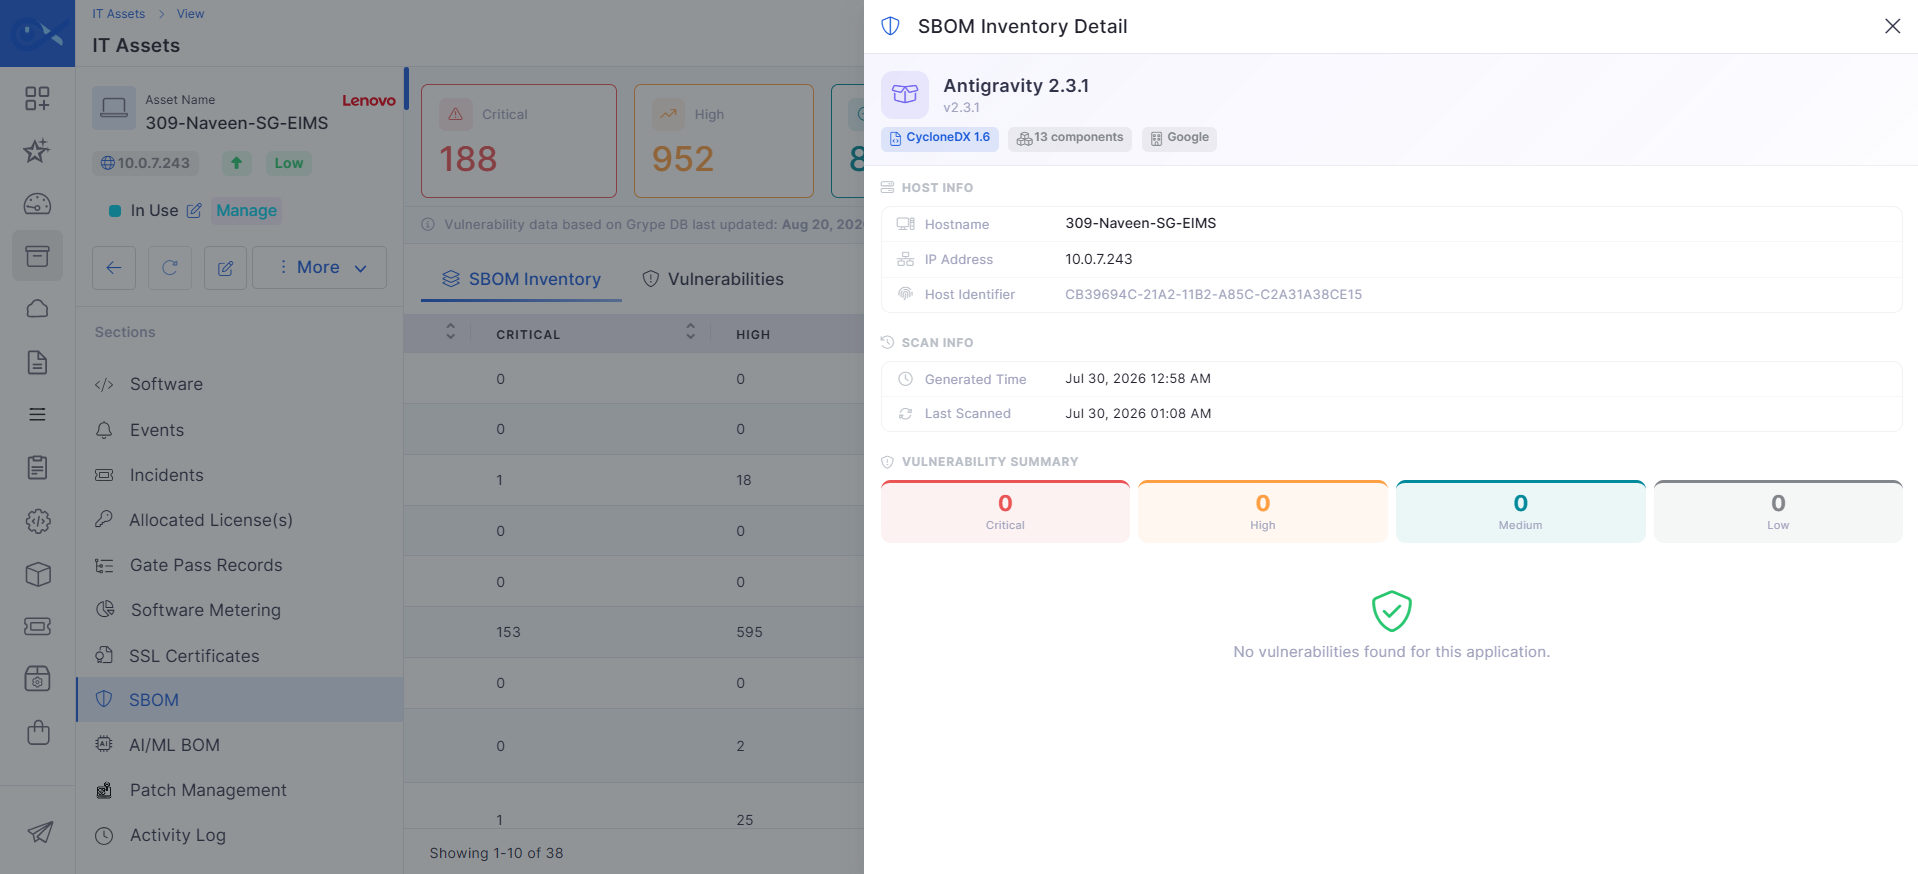
When View is selected, the SBOM Inventory Detail sidebar opens on the right and provides detailed information about the selected application, its host, scan details, and associated vulnerabilities.
Label
Action
Description/Example
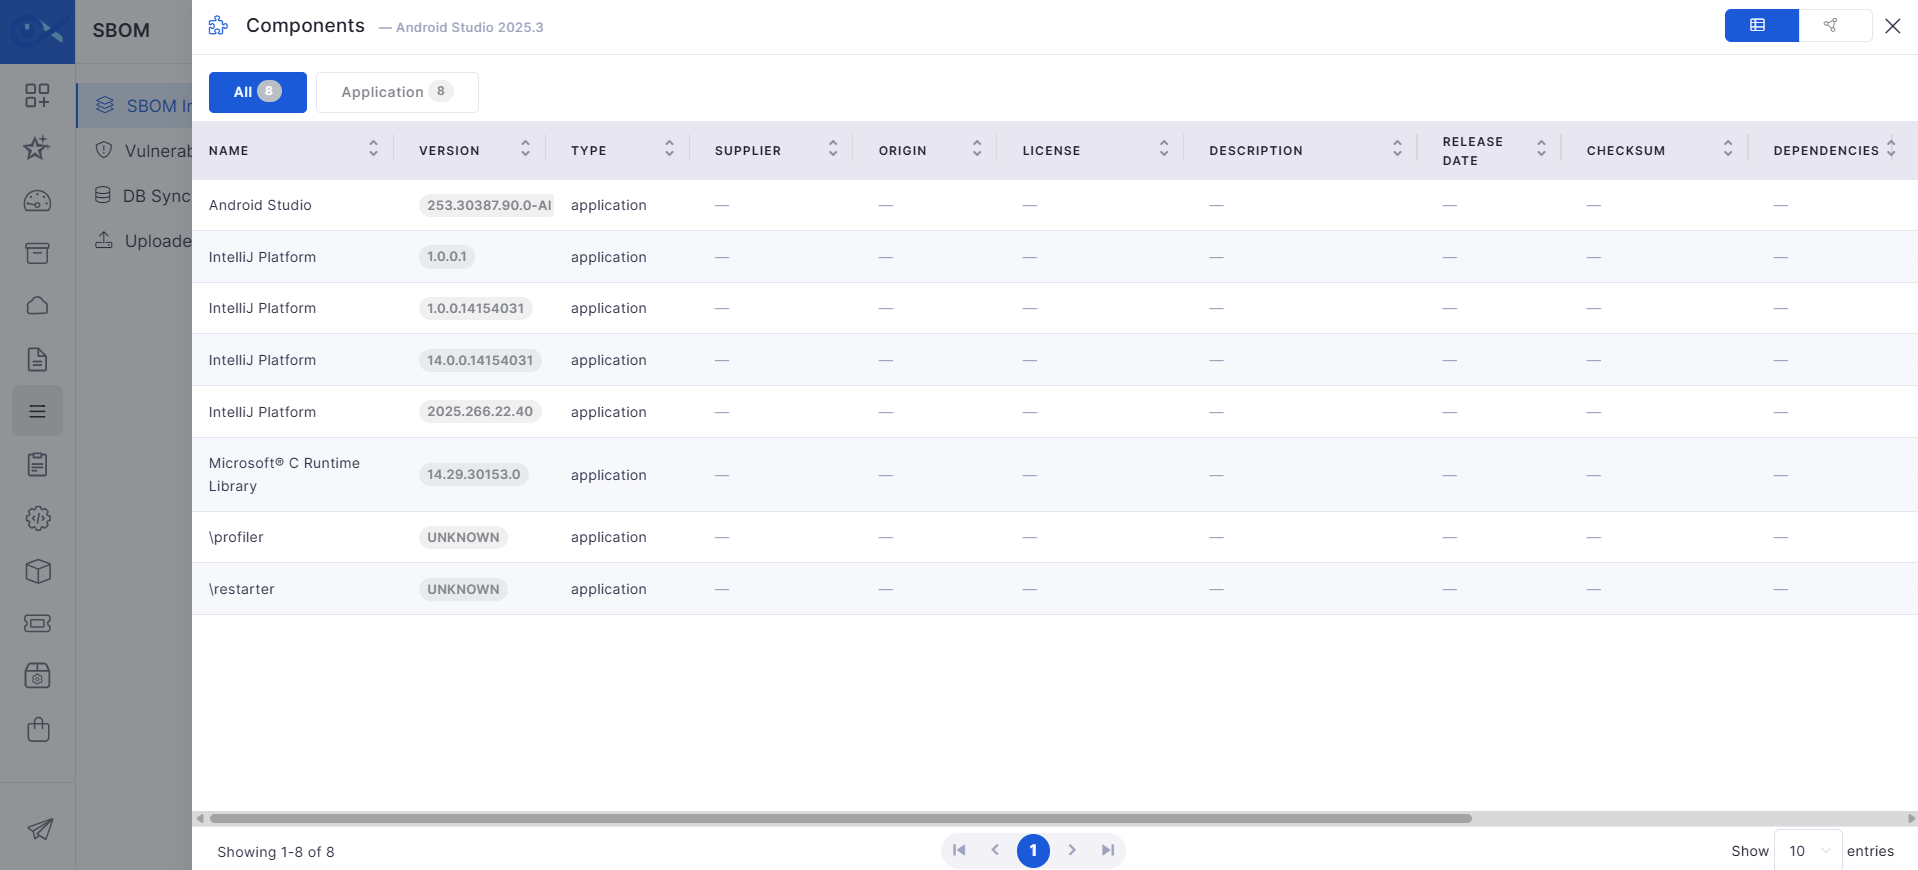
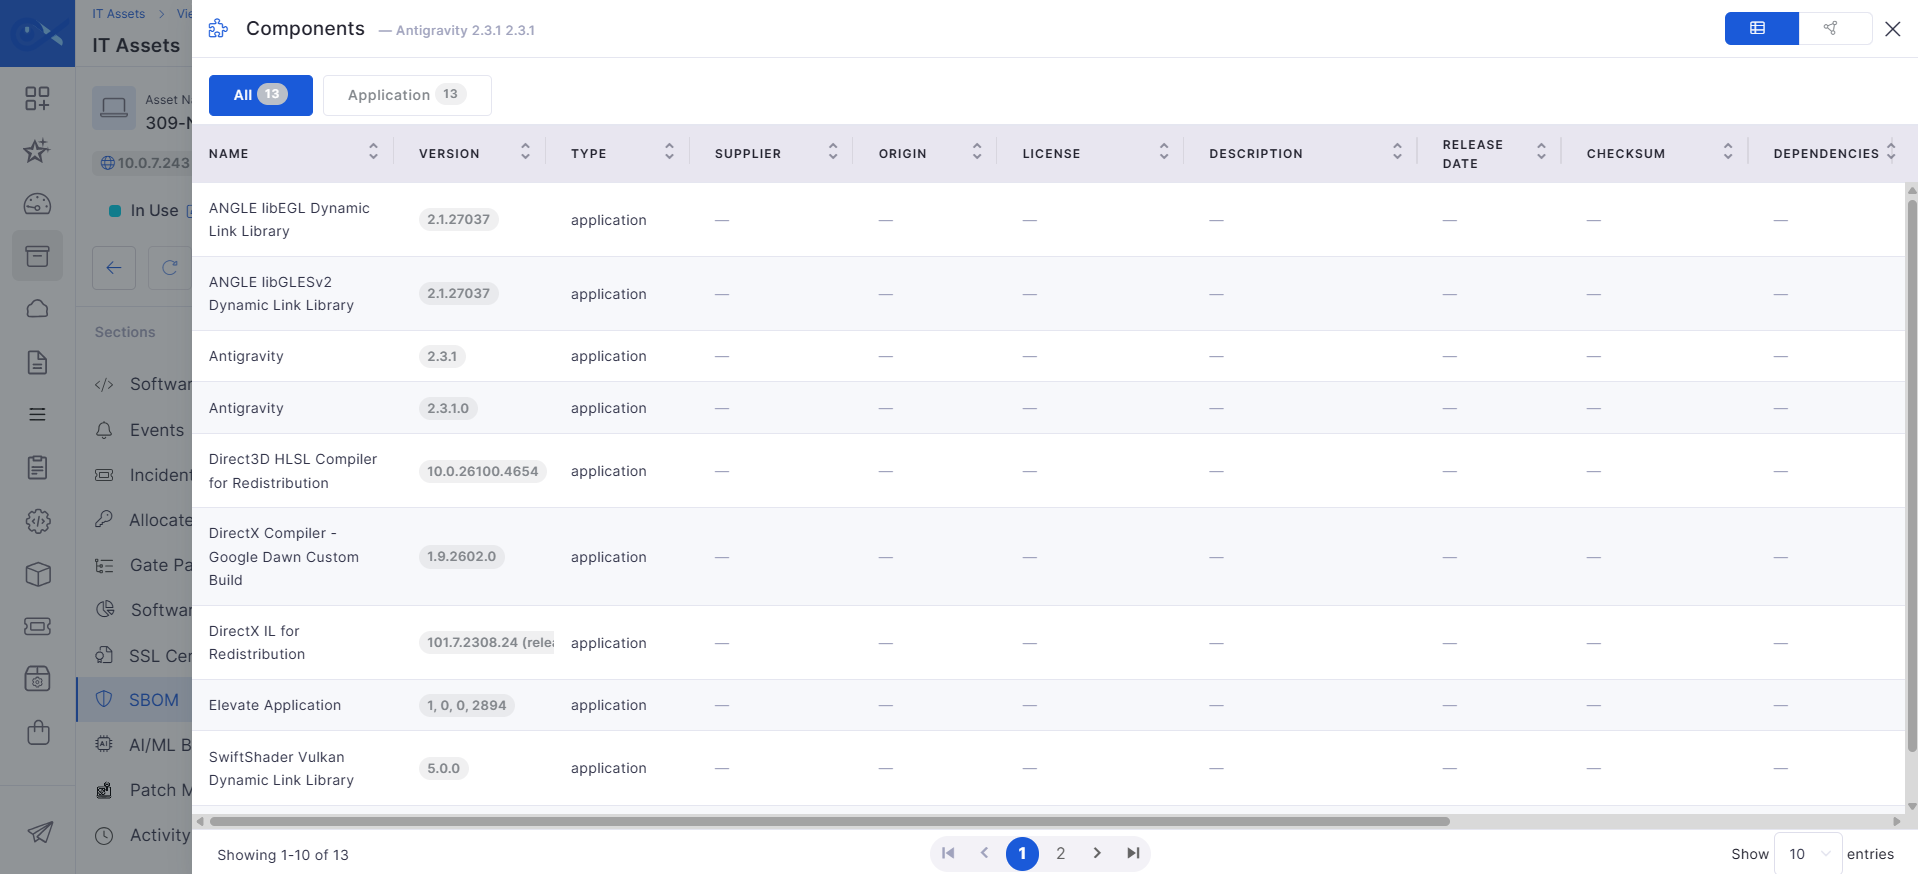
When View Components is selected for an application, the Components page opens and displays the software components and dependencies associated with the selected application. Users can switch between All and Application views and choose either Grid View or Graph View to examine the component information.
Component Details
The component details provide information about the component, its source, licensing, dependencies, and other SBOM metadata.
Label
Action
Description/Example
Software Assets
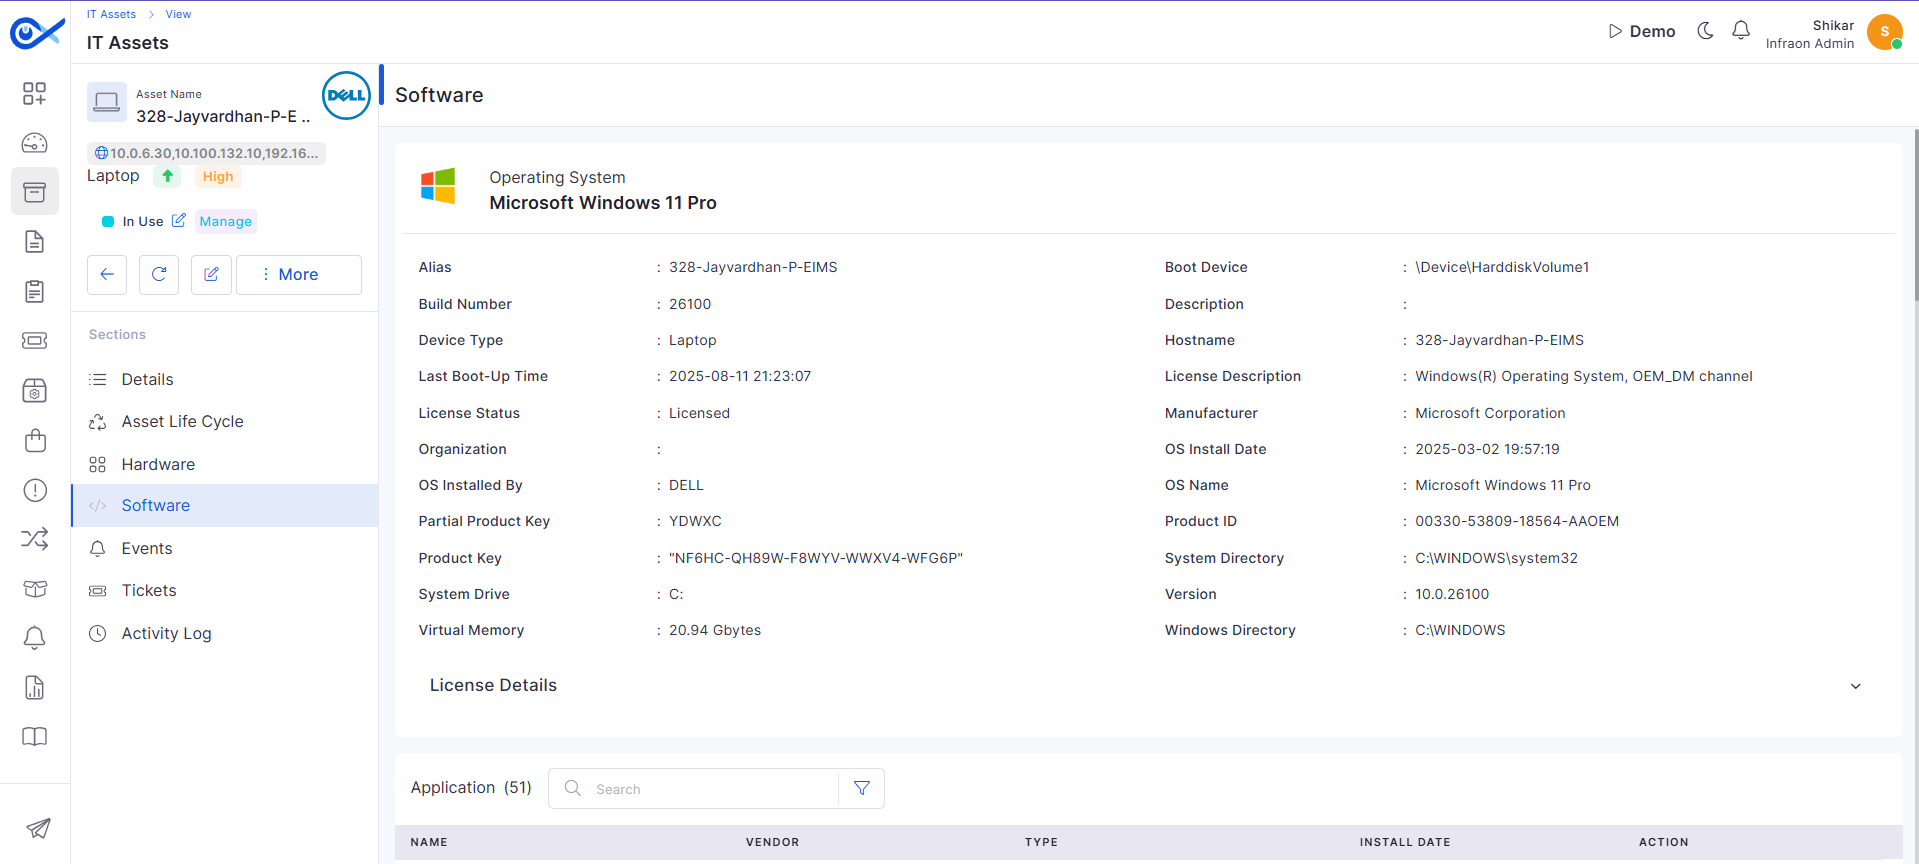
When devices are discovered using Infraon (inventory agent), the software installed in them is listed under the asset module as Software.
Download, view, and manage software entries, also blacklist/whitelist and uninstall software.
The discovered software is categorized based on the manufacturer. You have the option to blacklist or whitelist a specific software.
Check the Blacklist and Whitelist and Software License Management module for details.
Users
What do you see on screen?
Infraon Platform
The Infraon Platform is the central hub for configuring and managing various aspects of your Infraon Infinity environment. It provides a user-friendly interface for accessing and managing sub-modules that cater to different administrative tasks.
Let's see each one in detail:
Select
Select the inventory field on which the filter should be applied.
Condition
Select
Select the required condition to determine how the field should be matched.
Value
Enter/Select
Enter or select the value to be matched against the selected field and condition.
Vendor
View
Displays the vendor associated with the application.
Example: Google LLC
Hostname
View
Displays the hostname of the asset where the application was identified.
Example: workstation-01
IP Address
View
Displays the IP address associated with the host.
Example: 192.168.1.50
Components
View
Displays the number of software components or dependencies identified for the application.
Example: 312
Critical
View
Displays the number of Critical vulnerabilities associated with the application.
High
View
Displays the number of High vulnerabilities associated with the application.
Last Scanned
View
Displays the date and time when the application was last scanned.
Actions
Perform action
Provides actions to view inventory details, view components, and download the SBOM for the selected application.
Download SBOM
Download
Downloads the SBOM data associated with the selected application.
Scan Info
View
Displays the Generated Time and Last Scanned Time.
Vulnerability Summary
View
Displays the Critical, High, Medium, and Low vulnerability counts for the application.
CVE List
View
Displays the CVEs identified for the application along with their severity information.
Displays components associated specifically with the selected application.
Version
View
Displays the version of the component.
Example: 1.1.1
Type
View
Displays the type of software component.
Supplier
View
Displays the supplier or organization that provides the component.
Origin
View
Displays the origin or source from which the component was obtained.
License
View
Displays the license associated with the component.
Description
View
Displays a description of the software component and its purpose.
Release Date
View
Displays the release date of the component version.
Checksum
View
Displays the checksum associated with the component for identification or integrity verification.
Dependencies
View
Displays the dependencies associated with the component.
Properties
View
Displays additional properties or metadata associated with the component.
Notes
View
Displays additional notes or information provided for the component.
Package URL (PURL)
View
Displays the Package URL (PURL) that uniquely identifies the software package.
Grid View
Select
Displays component information in a structured grid/table format, allowing users to view the available component details in columns.
Graph View
Select
Displays the components and their relationships in a graphical representation, making it easier to understand component and dependency relationships.
Search
Search
Allows users to search the inventory using a keyword.
Filter
Filter
Allows users to refine the inventory results using Field, Condition, and Value.
Application Name
View
Displays the name of the application identified in the SBOM data.
Example: Google Chrome
Version
View
View
View
Opens the SBOM Inventory Detail sidebar for the selected application. The sidebar provides application details, host information, scan information, vulnerability summary, and the associated CVE list.
View Components
Navigate
Application Details
View
Displays the application Version, SBOM Format, Components, and Vendor.
Host Info
View
All
Select
Displays all components available for the selected SBOM inventory record, including associated dependencies.
Application
Column Details
SBOM Inventory Detail
Components
Field
Displays the version of the application.
Example: 124.0.6367.91
Navigates to the Components page for the selected application, where users can view the identified components and switch between the available All and Application views and different display modes.
Displays the Hostname, IP Address, and Host ID associated with the application.
Select
BOMS
Dashboard
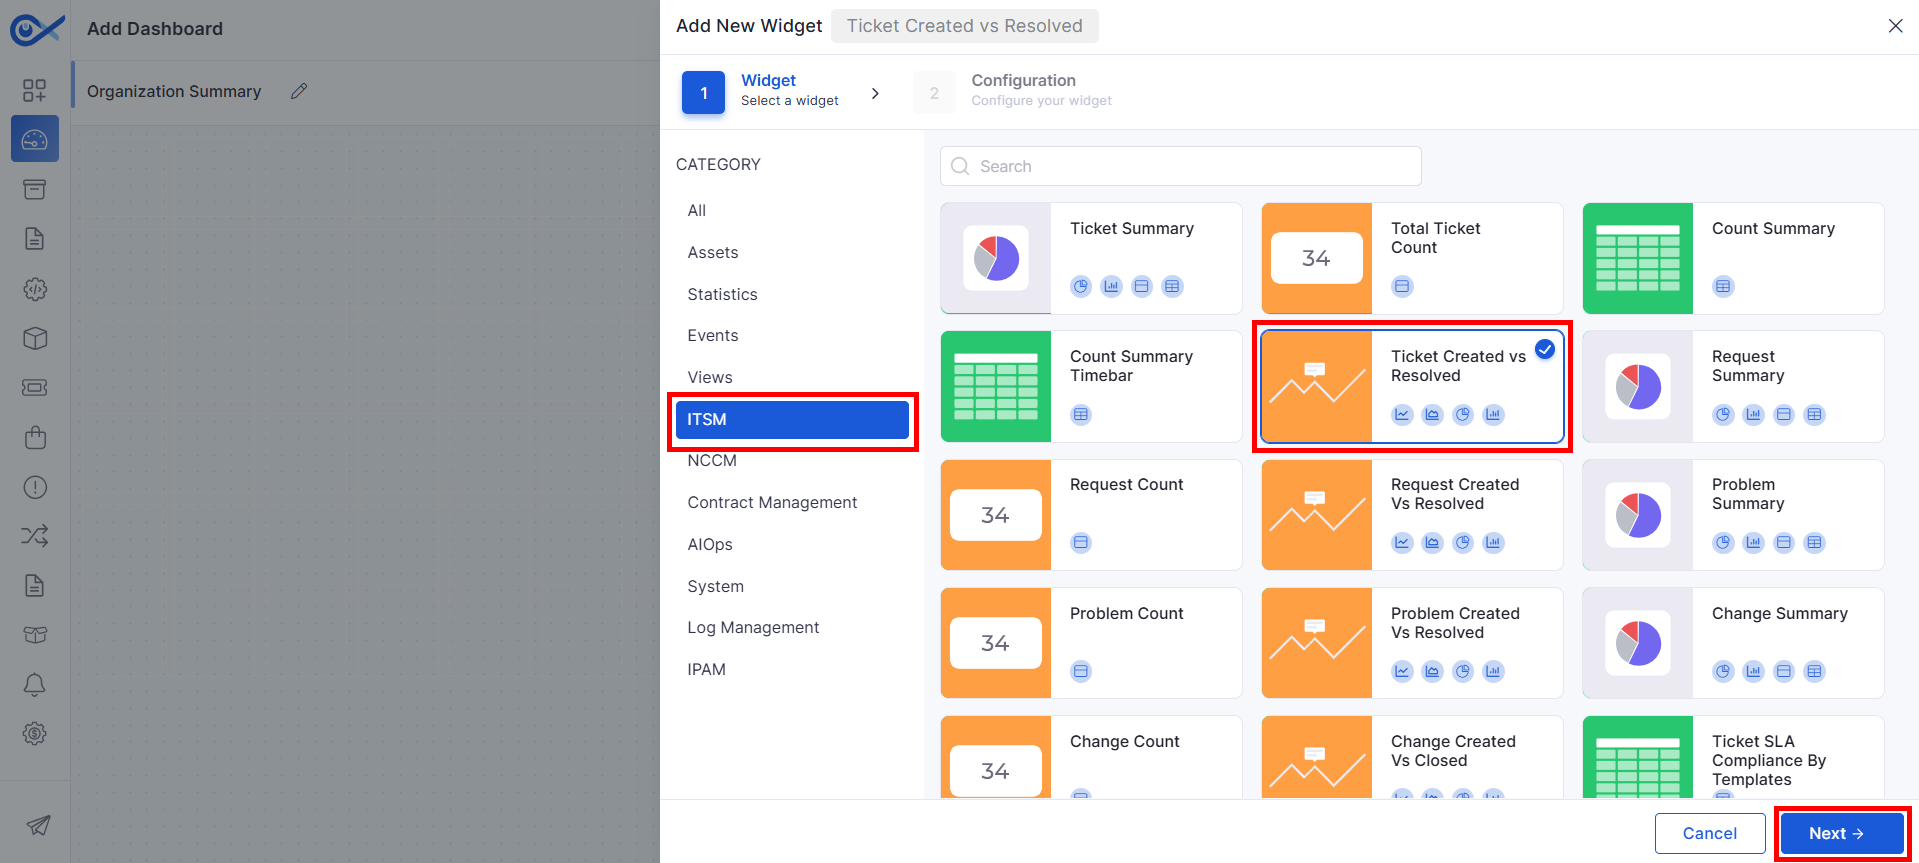
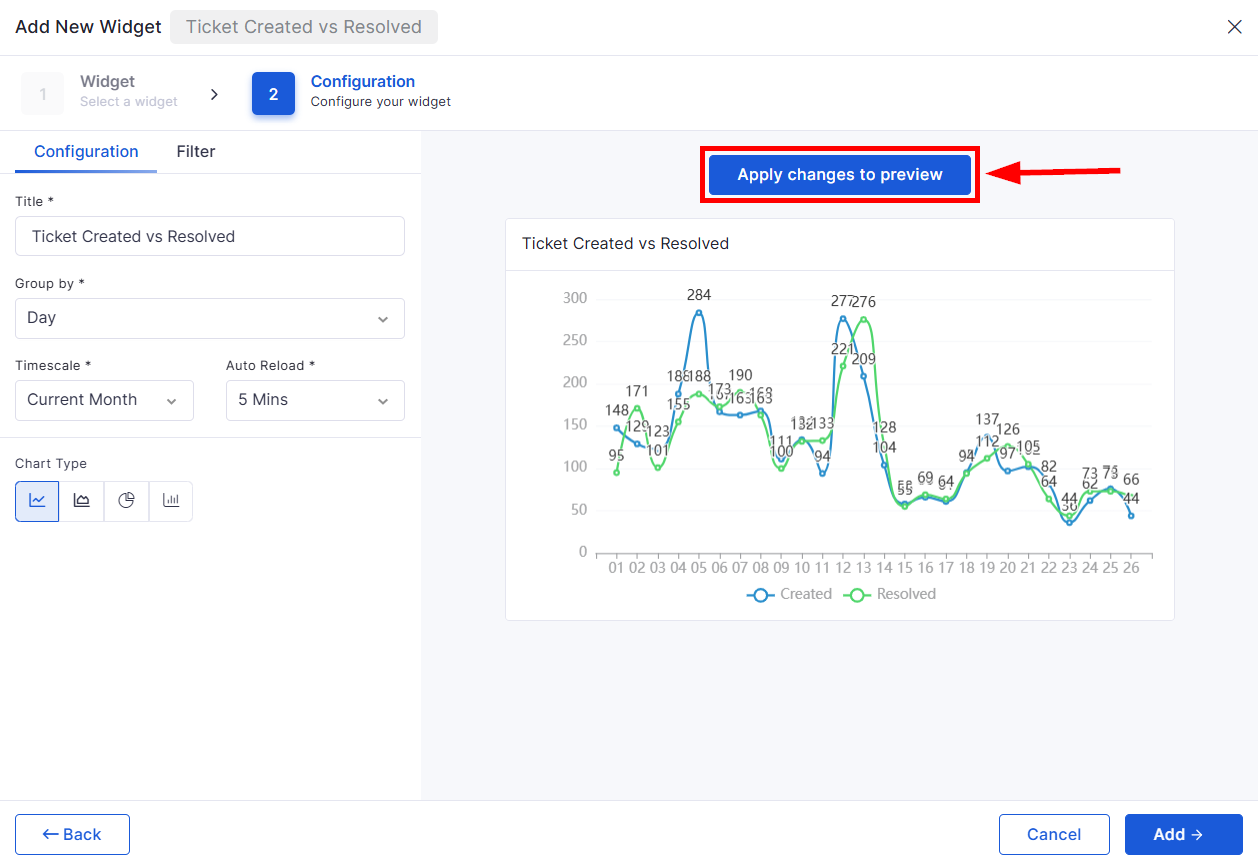
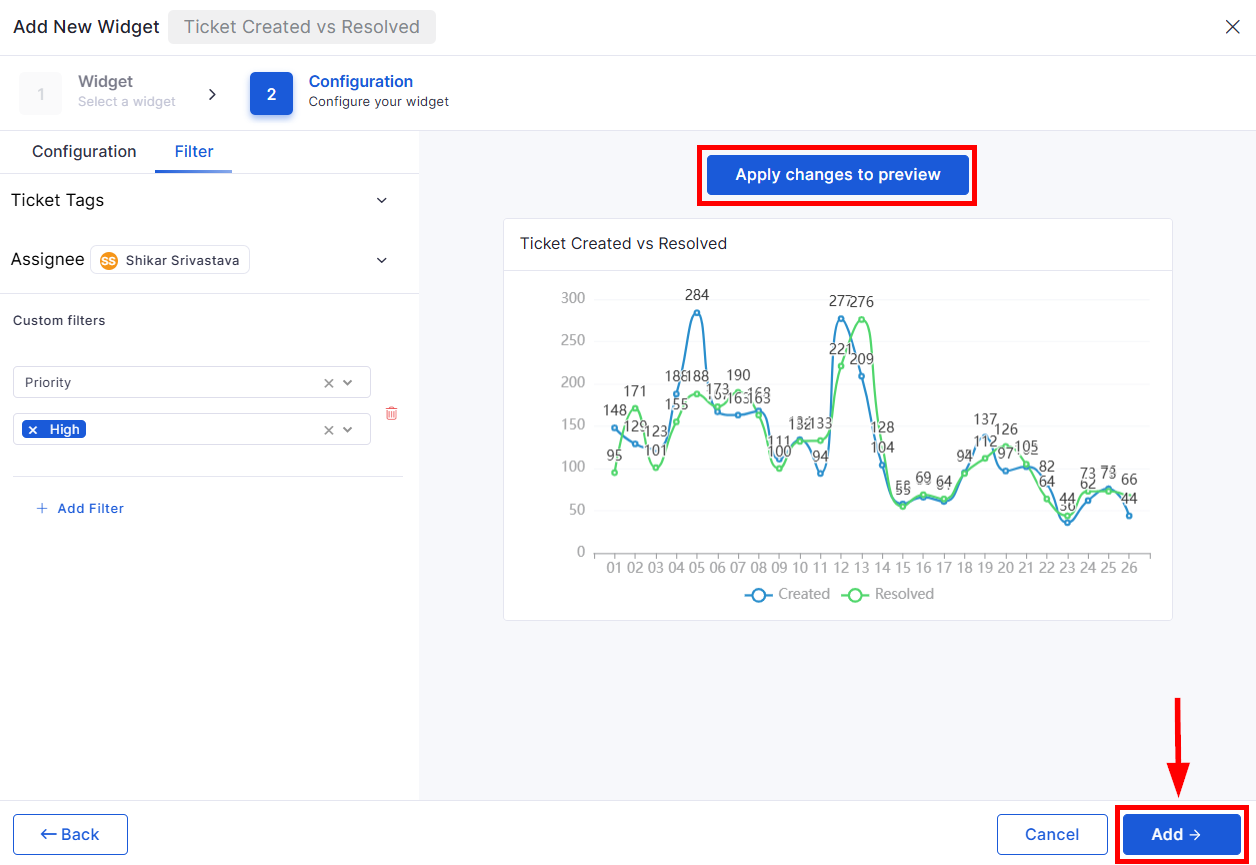
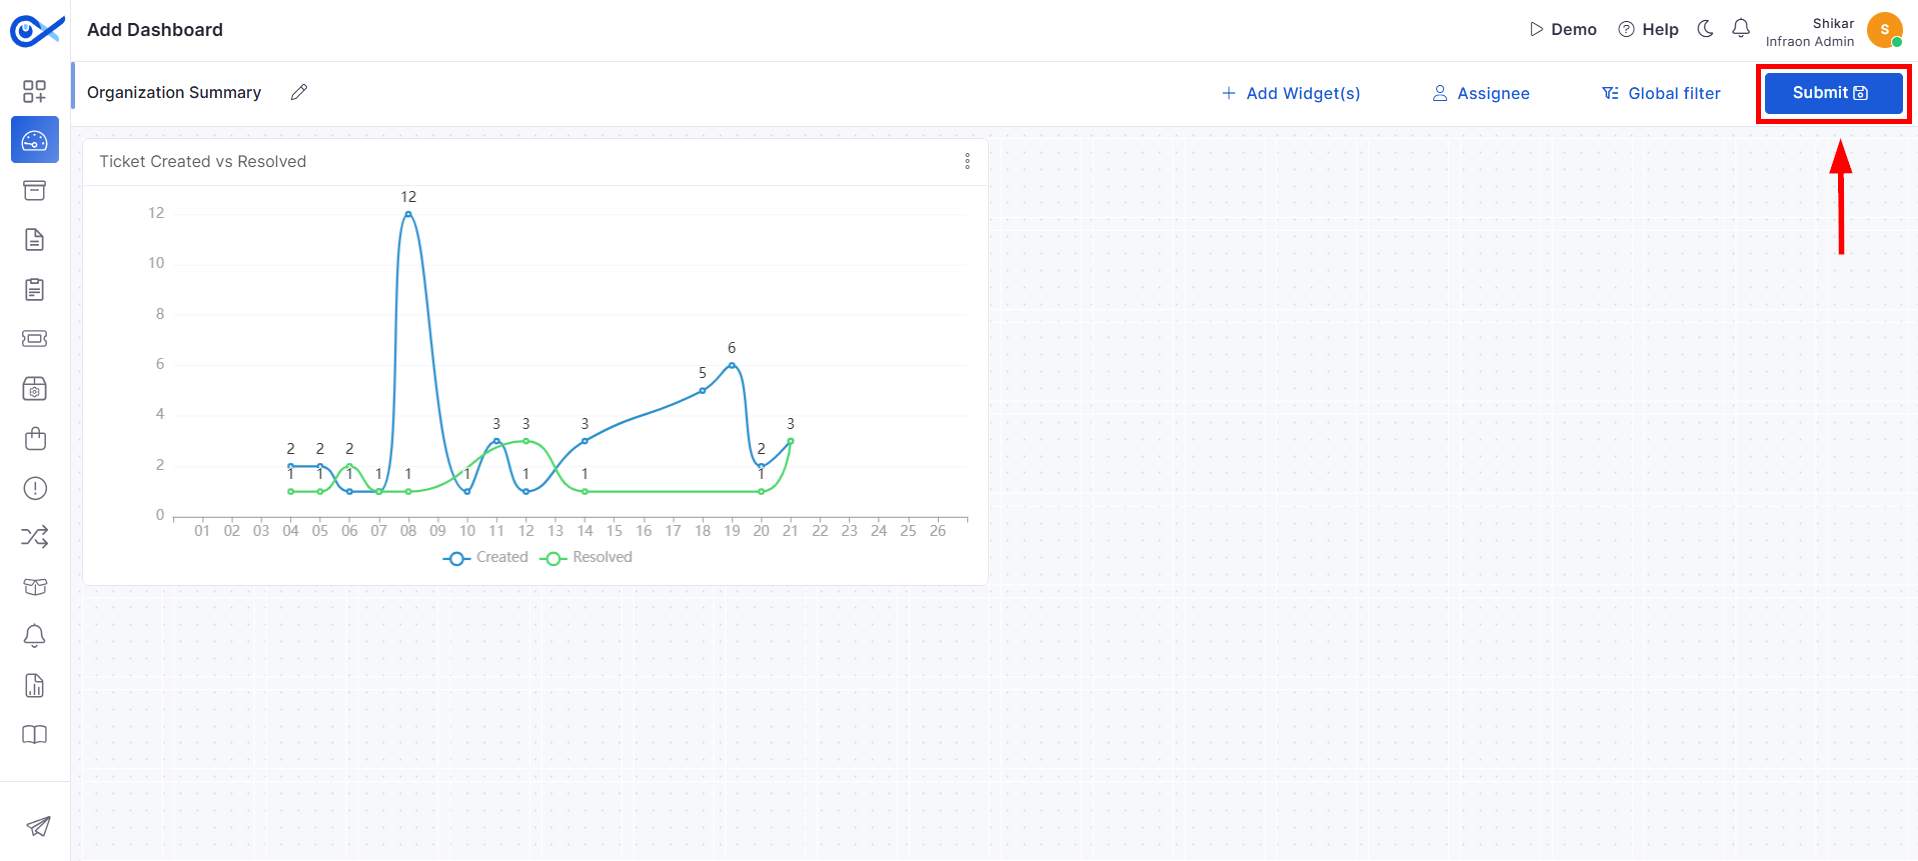
Dashboards are visual representations of critical data within Infraon. They provide concise yet detailed insights into monitoring and performance metrics.
Users can customize dashboards by adding relevant metrics and reports tailored to their specific needs. Dashboards can also be exported as PDFs for reporting and analysis.
Access to view and customize dashboards is controlled by role-based privileges that the administrator must enable. Access can be managed at both the User and User Group levels.
Before customizing dashboards, it is essential to understand the concept of Widgets, as these form the building blocks of every dashboard.
What You See on the Screen
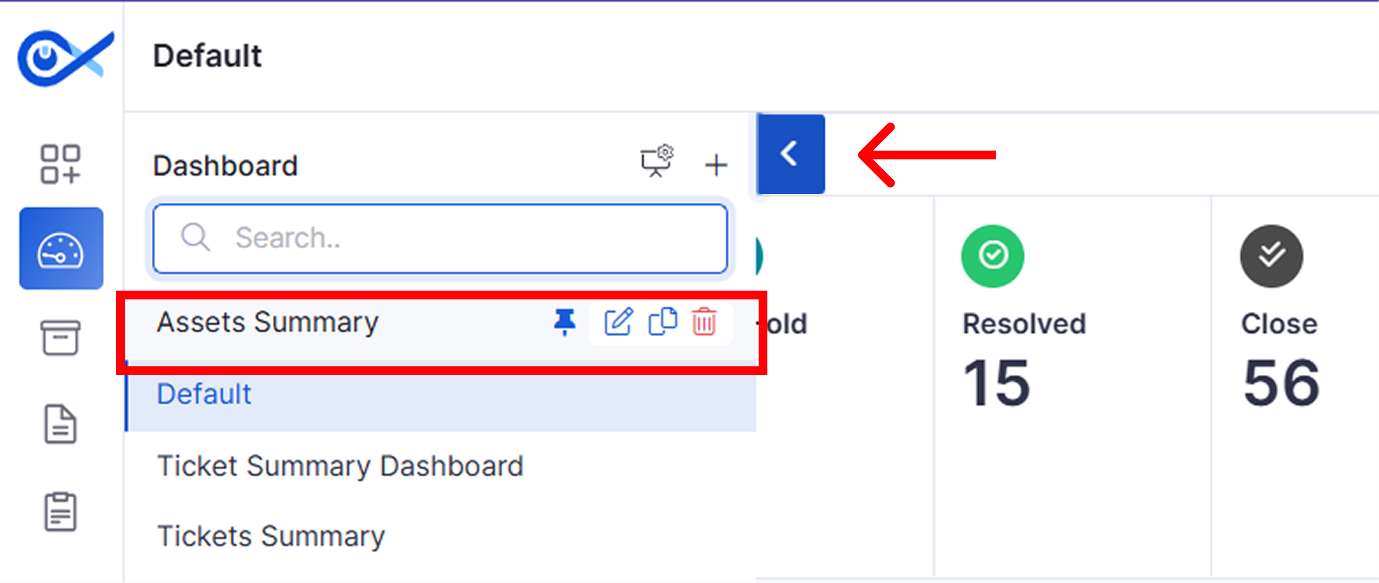
Click the arrow key in the left navigation panel to expand and access multiple pre-configured dashboards. You can also hover over dashboards to reveal action icons.
Action Icons | Dashboards
Infraon provides three pre-configured dashboards during platform onboarding. These serve as ready-to-use examples to help users understand dashboard functionality and layout.
Each dashboard contains dynamic widgets that auto-refresh based on the selected refresh interval. Widgets are clickable, allowing users to drill down and view complete details of the underlying data.
Additionally, users can download the displayed data in CSV format for further analysis for specific widgets.
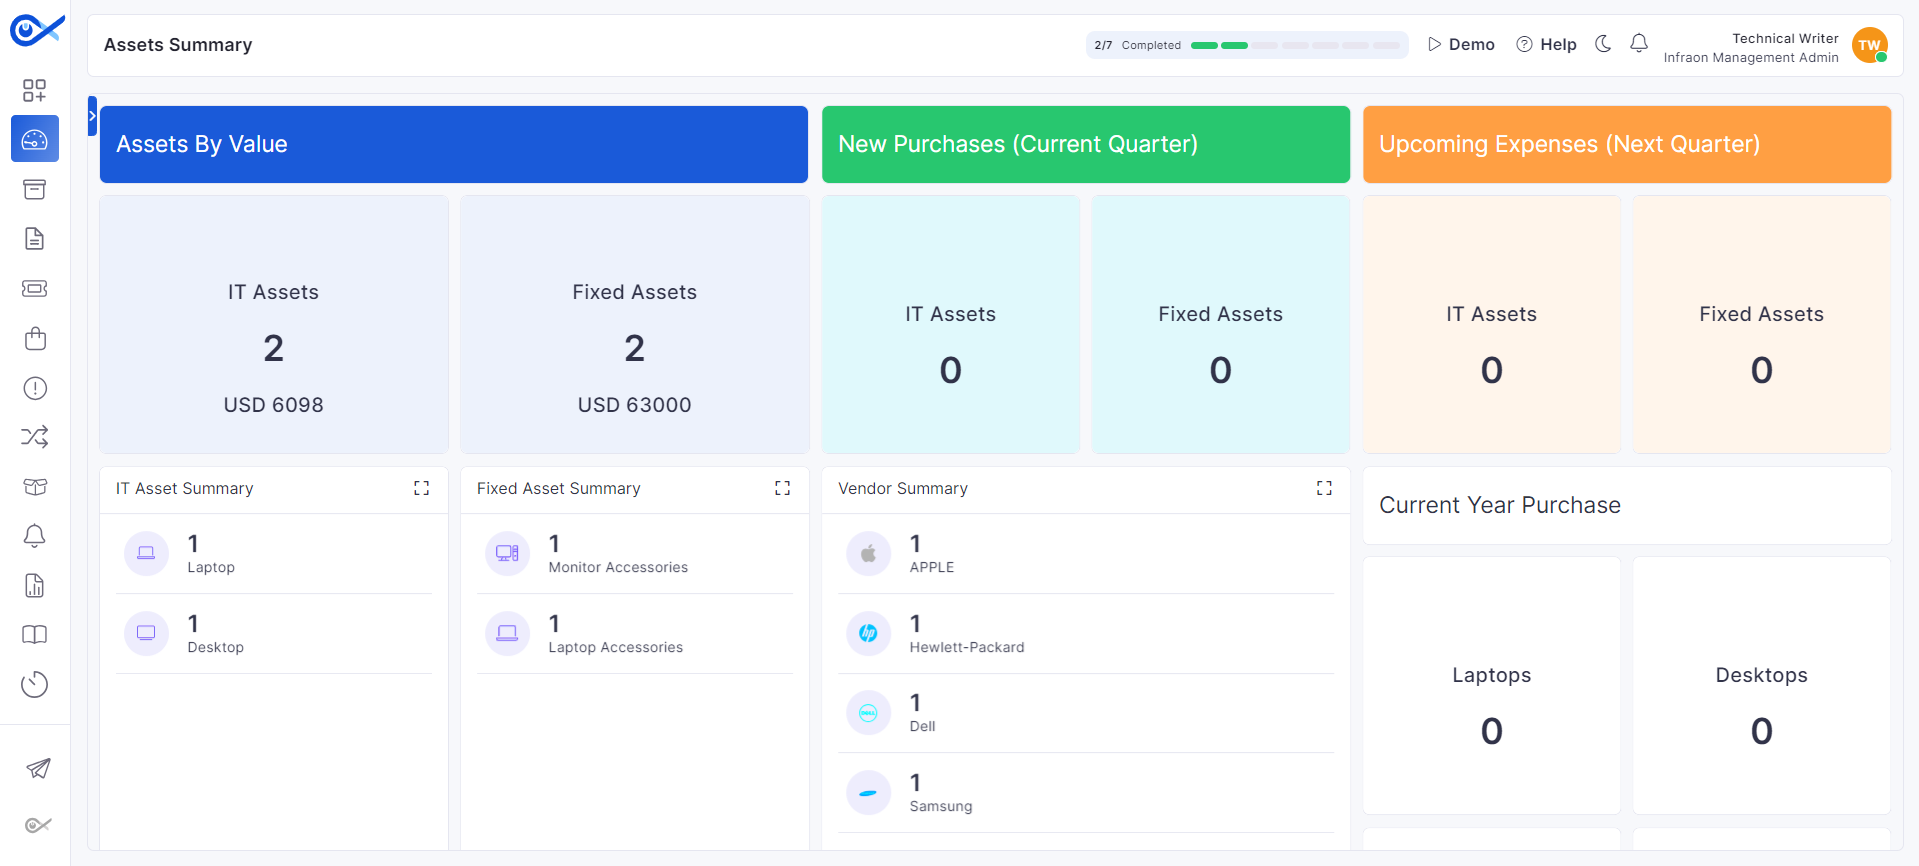
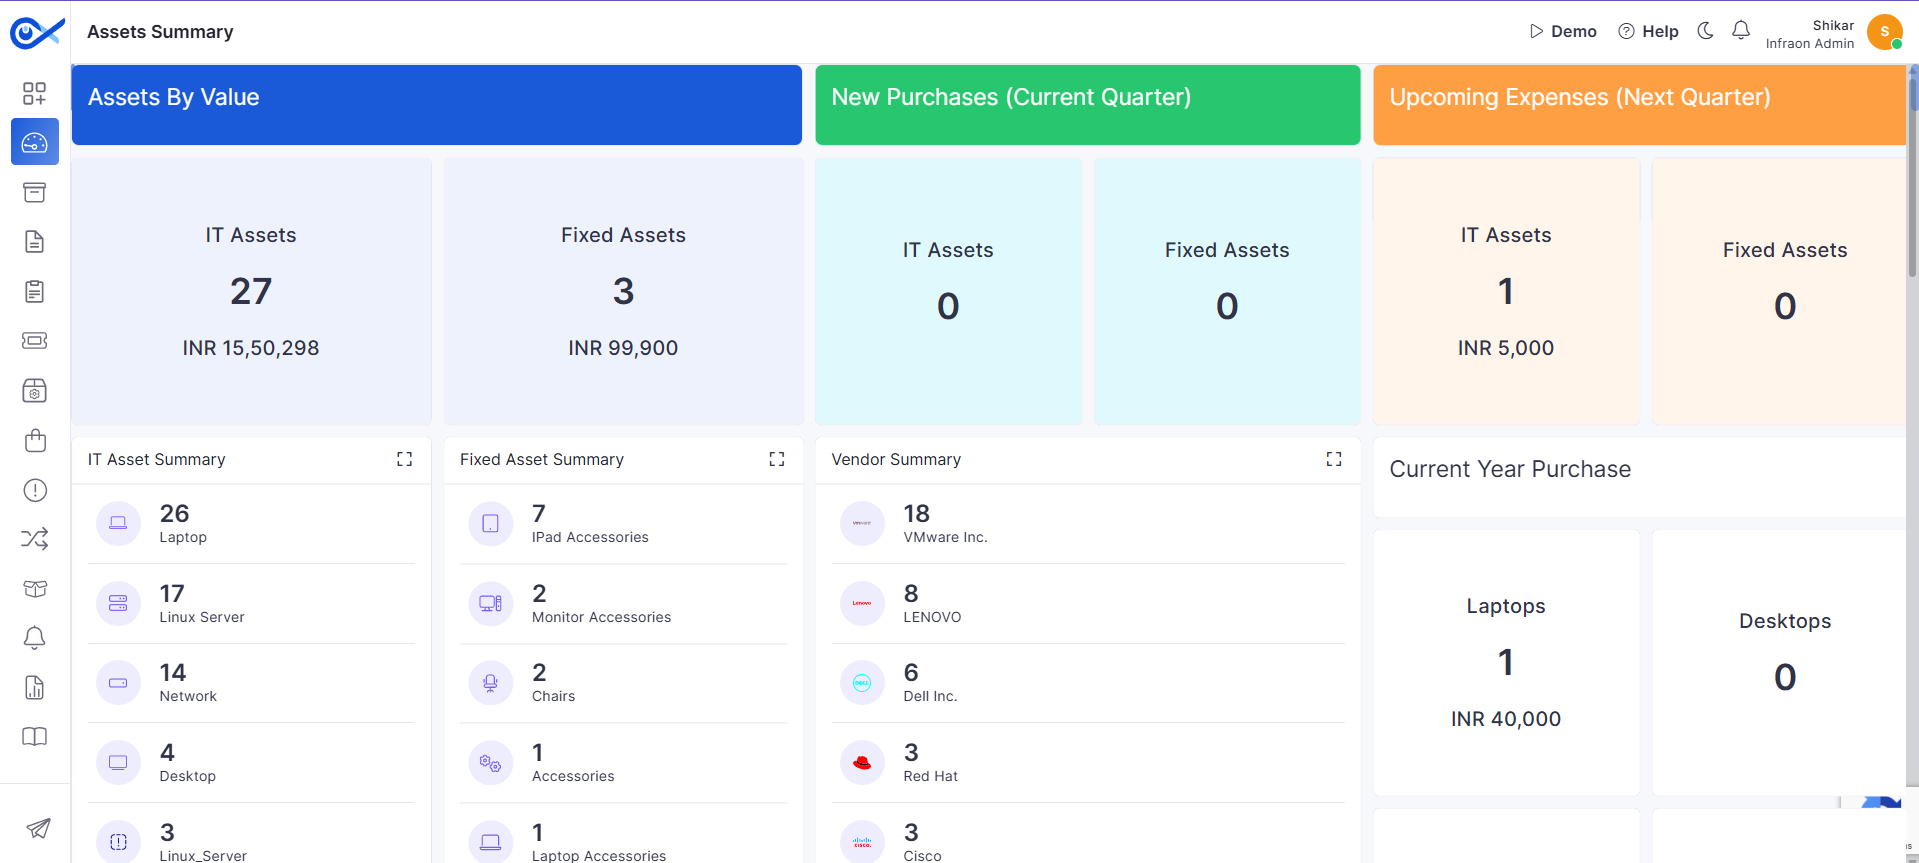
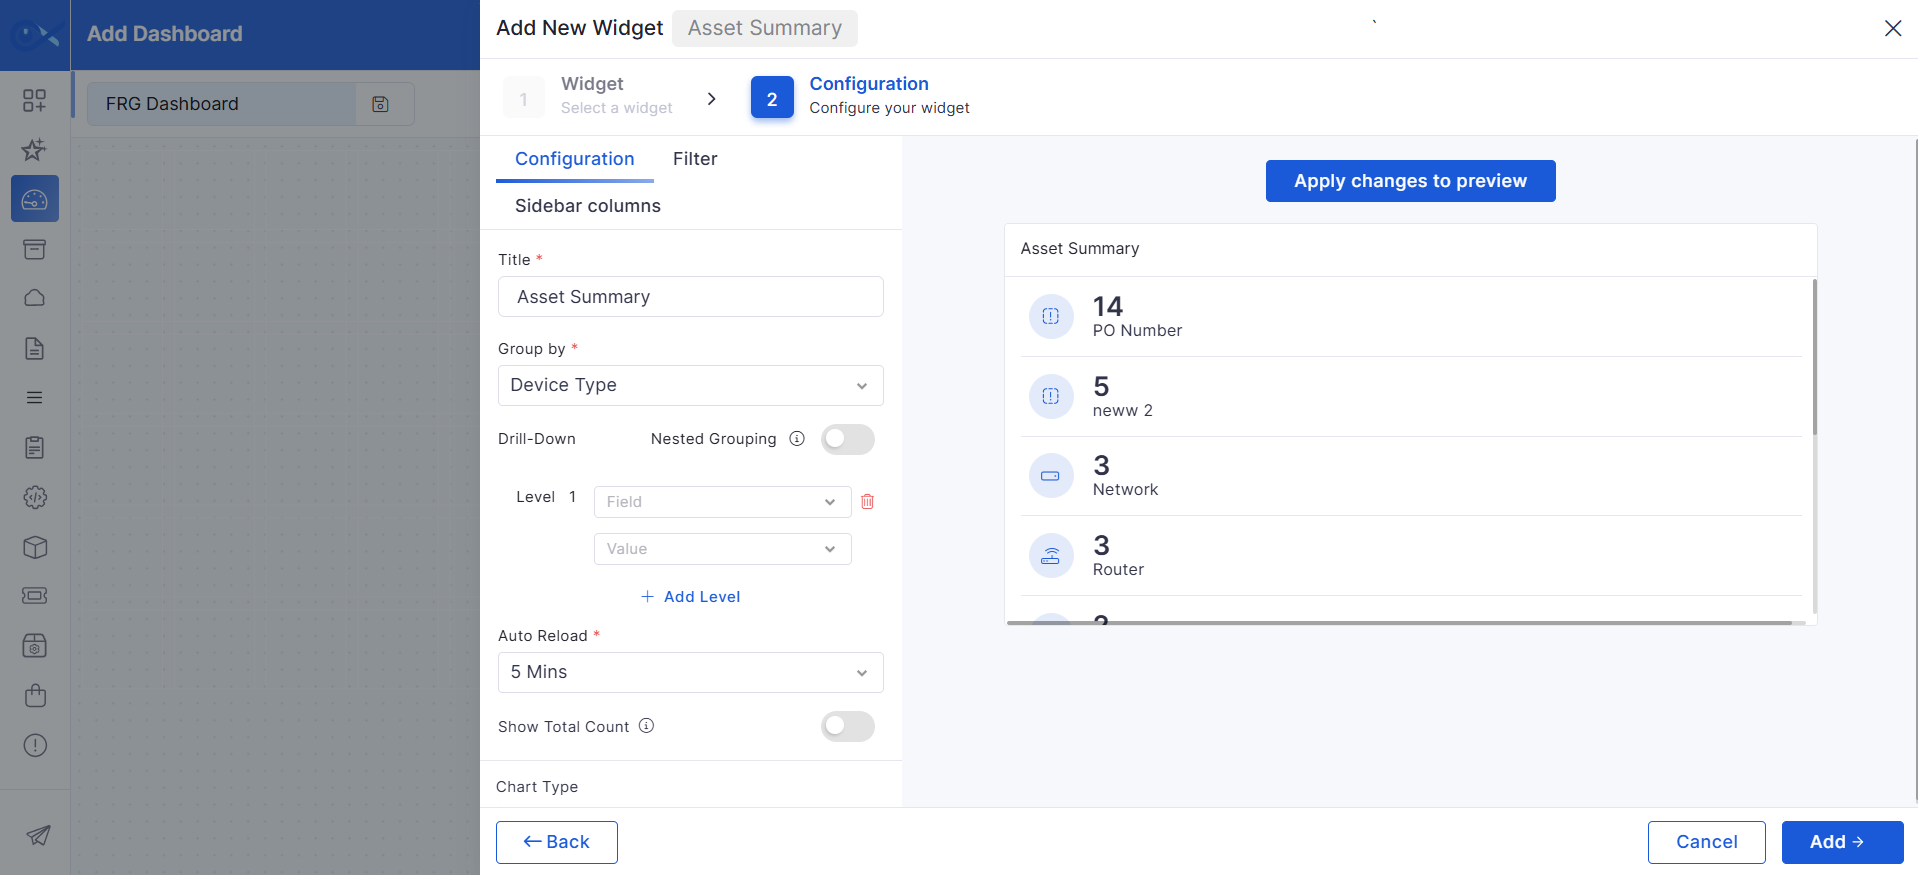
It enables organizations to manage asset lifecycles effectively, track expenses, and plan budgets proactively. The Asset Summary Dashboard delivers a comprehensive overview of IT and fixed assets, including purchase trends, financial summaries, vendor information, and asset distribution by value and location.
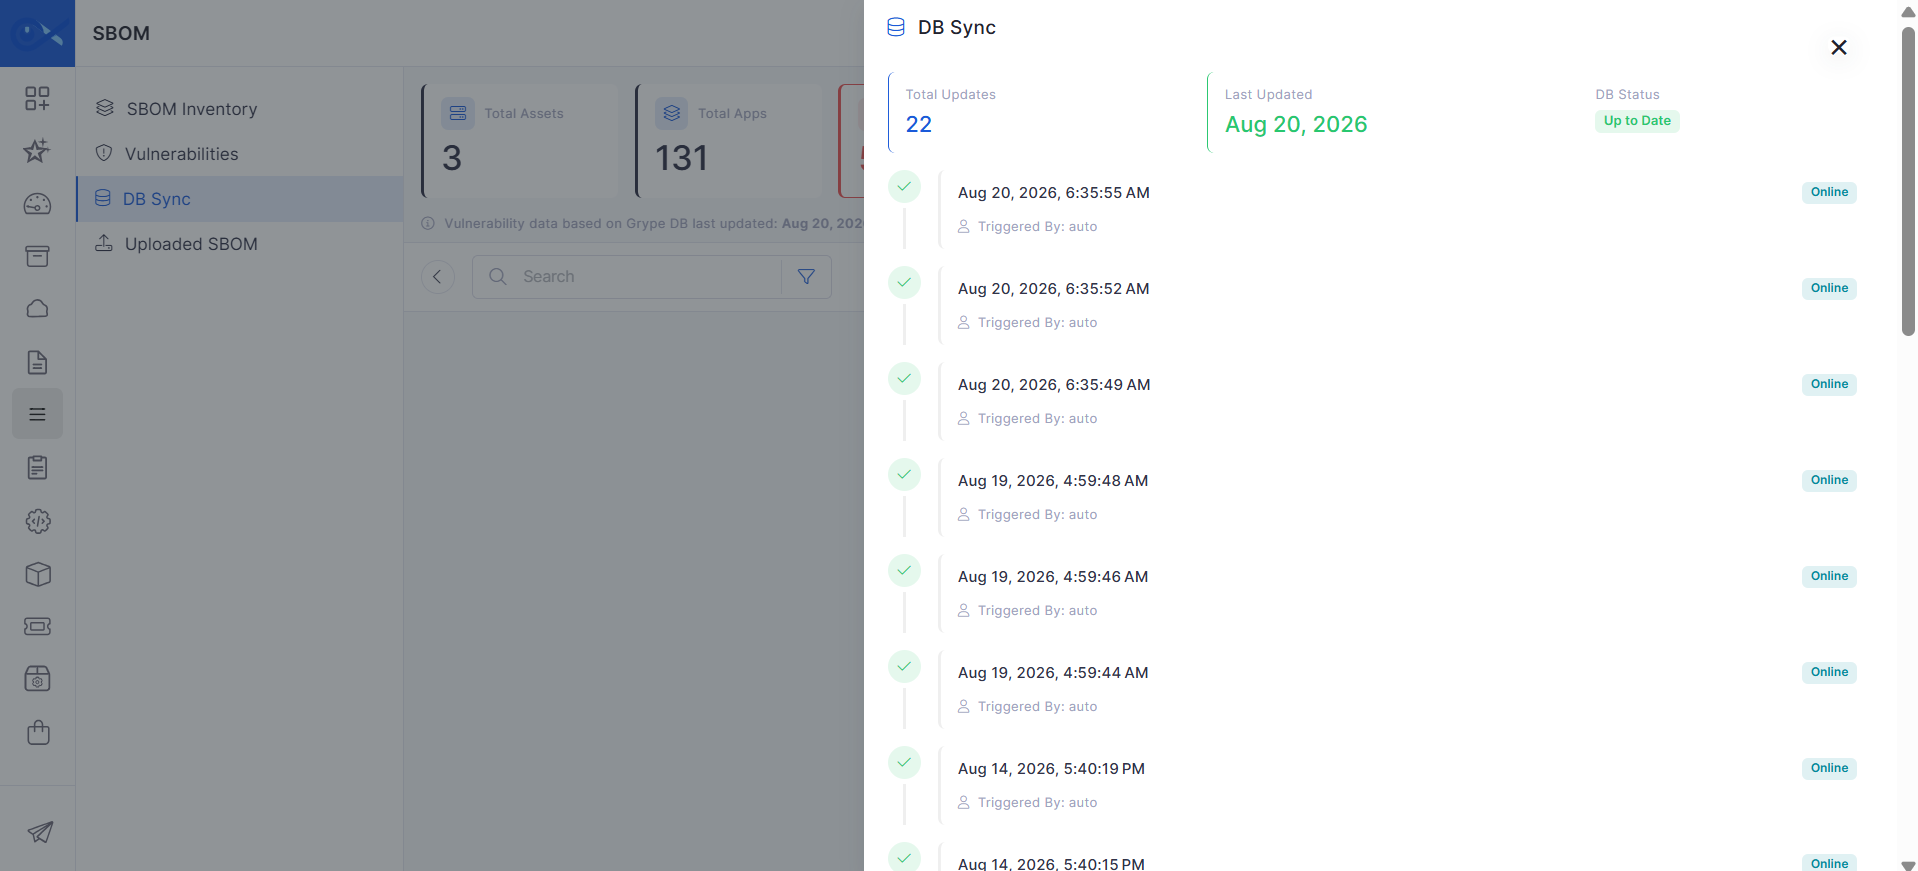
DB Sync
DB Sync allows users to monitor the synchronization status of the SBOM vulnerability database. It provides information about database updates, the latest synchronization time, database status, schema version, and the update source.
How does DB Sync work?
The SBOM vulnerability database is periodically synchronized to keep the vulnerability information up to date. The DB Sync page maintains a history of database updates and displays the current database status.
Use case: For example, if the vulnerability database is successfully synchronized, users can open DB Sync to verify when the database was last updated, check its current status, and view information such as the schema version and database build date. If the database becomes stale, the page indicates the stale status so that users can identify that the vulnerability data may require an update. The documented stale condition is when the database is more than 30 days old.
What do you see on the screen?
When you select DB Sync from the SBOM navigation, the DB Sync page/sidebar displays the database synchronization status and update history. It provides summary information at the top followed by details of previous database updates.
DB Sync Details
The DB Sync details provide information about the database version, build information, update status, and the source that triggered the synchronization.
Label
Action
Description/Example
CI Rule Configuration
The CI Rule Configuration empowers administrators to automate how Configuration Items (CIs) are discovered, categorized, and managed in your environment. Admins can select and configure specific rules based on different criteria to streamline CI management.
Department Rule
This rule automates department assignments for your Configuration Items (CIs). With this rule enabled, whenever a department is linked to an asset within the system (mapping can be enabled or disabled), a CI relation is automatically created. This eliminates manual assignment, ensuring accurate and up-to-date departmental ownership of CIs throughout your IT infrastructure.
Location Rule
The Location Rule automated location assignment for your Configuration Items (CIs). Similar to the Department rule, admins can enable or disable location mapping on assets. When enabled, this rule automatically creates a CI relation whenever a physical location is linked to an asset. This eliminates manual effort, guarantees CIs are accurately assigned to their corresponding locations within your IT infrastructure, and improves organization and location-based reporting.
Requester Rule
The Requester Rule automates by enabling or disabling requester mapping on assets. Admins can configure this rule to automatically create CI relations whenever a service is linked to a specific user. This eliminates manual assignment and ensures CIs are associated with the appropriate requester, providing valuable insights into departmental or user-based IT asset usage.
Software Rule
The Software Rule simplifies CI management by automating the creation of CI relations for discovered software. Admins can turn software mapping on or off on assets within the system. With this rule active, a CI relation is automatically created whenever software is identified or manually linked to an asset. This eliminates manual effort and ensures accurate tracking of software assets associated with specific hardware, improving overall visibility into your IT infrastructure.
The User Rule automates CI relations based on designated technicians or managing users within your ITSM system. By enabling or disabling "manage by/technician" mapping on assets, you can configure this rule to create CI relations automatically. Whenever a specific user is assigned as the technician or manager for an asset, this rule triggers the creation of a CI relation. This eliminates manual assignment, ensuring CIs are linked to the appropriate technicians, which can be crucial for service accountability and troubleshooting workflows.
User Rule
User Management
User Management is part of Infraon Configuration and is accessible by administrators and authorized users. It involves managing users and defining their role and access level across modules of Infraon.
Infraon's User Management module consists of six additional modules.
They are:
Users: Invite new users or edit/delete existing users.
Roles & Privileges: Create new roles or edit/delete existing roles and define privileges for roles.
Requesters: Create special accounts for end-users to view their requests.
Teams: Create teams of users with similar skills to assign tasks to easily enable collaboration and mutual support.
Department: Create departments, assign team members, and align them with managers.
Password Policy: Create a password policy to enhance security and meet compliance standards.
My Leave: View and apply for leave of absence from work.
Leaves: View Holiday List and leave categories as per organizational policy.
Let's see each of these in detail.
Useful for budgeting and procurement reviews.
Upcoming Expenses (Next Quarter)
Projects upcoming financial commitments for assets.
Helps plan budgets and avoid surprise expenses.
IT Asset Summary
Lists IT assets with key details (type, category, ownership).
Helps IT teams maintain inventory accuracy.
Fixed Asset Summary
Displays details of fixed/long-term assets.
Supports audits and compliance checks.
Vendor Summary
Shows vendor details and associated assets.
Helps manage vendor performance and procurement contracts.
Current Year Purchase
Summarizes all purchases made in the current year.
Provides annual procurement insights.
Agent Summary
Shows workload and asset-related activities of agents.
Useful to monitor asset-related responsibilities of staff.
Asset Location Drilldown Table
Displays asset details by physical location.
Helps track distributed asset ownership.
Asset Summary
General overview of assets within the system.
Provides quick visibility into total inventory.
Location-wise Asset Summary
Breaks down assets based on location.
/Displays a location-wise count of assets on the dashboard, helping users quickly view asset distribution, track inventory, and manage resources efficiently.
Label
Action
Description / Example
Configure Presentation
Click to configure
Enable Dashboard Presentation Mode. Select the dashboard and set time intervals (10–300 seconds) for automated rotation. This mode is useful for displaying dynamic assets or performance boards.
Add
Click to perform
Add a new custom dashboard.
Pin
Click to perform
Pin a dashboard to the top for quick access.
Edit
Click to perform
Modify or update the selected dashboard.
Clone
Click to perform
Duplicate the selected dashboard for reuse.
Delete
Click to perform
Remove the selected dashboard permanently.
Widget Name
Description
Use Case
Assets by Value
Displays asset distribution based on their monetary value.
Helps in financial tracking of IT and non-IT assets.
New Purchases (Current Quarter)
Pre-configured Dashboards
Asset Summary
Shows assets purchased in the current quarter.
Update
View
Displays an individual database synchronization event.
Update Time
View
Displays when the database synchronization occurred.
Status
View
Displays the status of the synchronization event.
Online
View
Indicates that the vulnerability database is available and operating normally.
DB Built Date
View
Displays the date when the vulnerability database was built.
Triggered By
View
Displays the source or process that initiated the database synchronization.
Business Unit
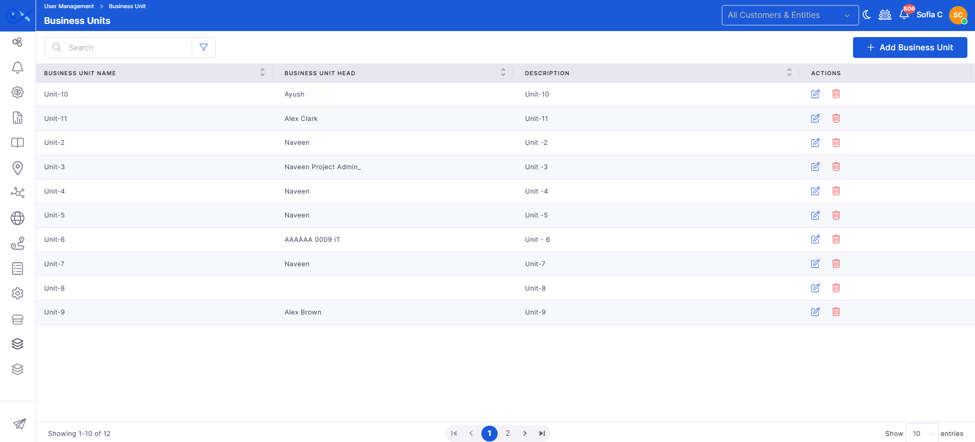
The Business Unit Management module allows administrators to create and maintain Business Units that are used within the budget. A Business Unit represents an organizational entity that can later be referenced during budget planning, budget allocation, and reporting.
How does it work?
Administrators can create Business Units by providing the required organizational information. Once created, the Business Units become available for selection when creating Business Unit Budgets and in other budgeting workflows. The module also allows administrators to view, edit, and delete existing Business Units.
What do you see on the screen?
Administrators can view the list of Business Units created in the system.
Label
Action
Description / Example
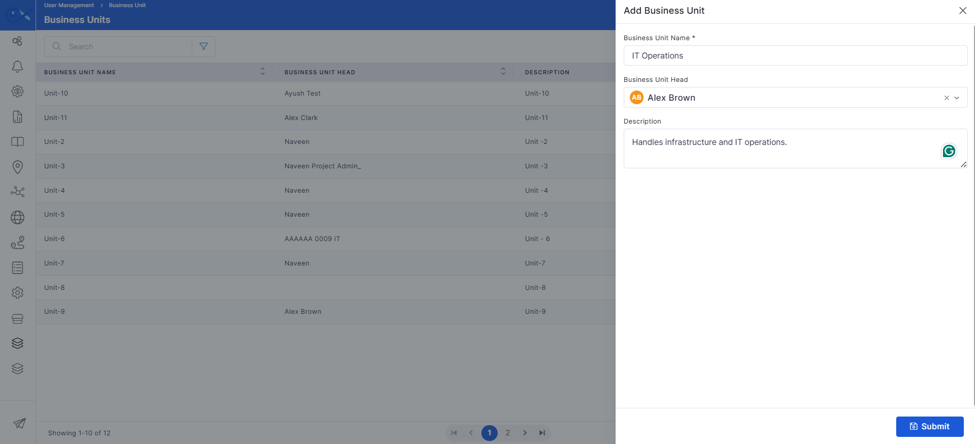
When creating a Business Unit, the administrator provides the following information:
Label
Action
Description / Example
Gate pass
It moves important IT equipment or valuable assets across different organizational locations. A gate pass becomes the essential tool for streamlined and secure movement. It is an authorization document granting permission for specific assets to leave and enter designated areas. This ensures transparent and accountable transfer, whether the asset is shipped between offices or fixed assets are handed over within a department.
Gate passes usually have a barcode or a QR code for convenience and security. This allows quick and easy checkpoint scanning, further enhancing control and record-keeping.
It typically includes information like:
Date and time of issuance: To track authorized movement within a specific timeframe.
Description of goods: Details about the items being moved, like quantity, type, and serial numbers.
Recipient and origin: Identifying who receives the goods and where the asset came from.
Admin’s signature: Authorizing the movement by designated personnel.
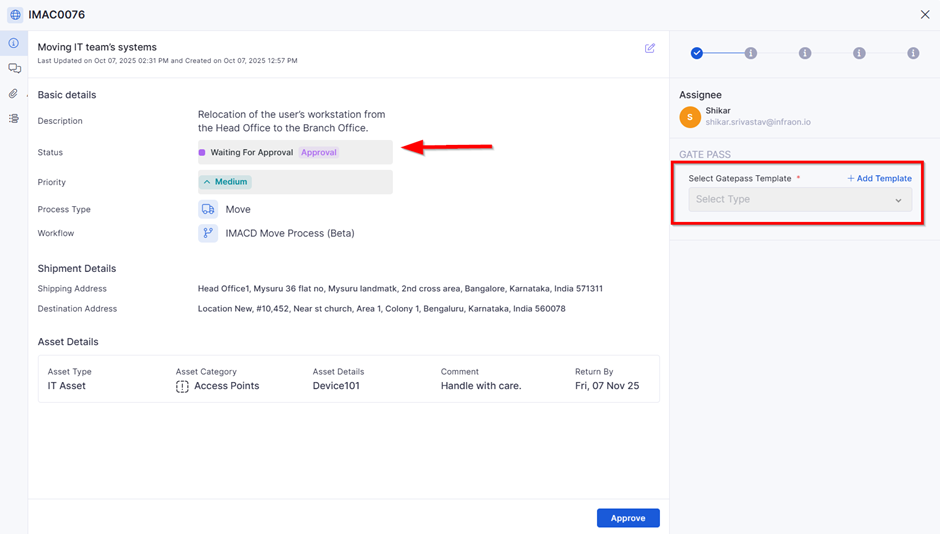
Follow the below steps to construct the gate pass of the respective asset for the IMACD process:
Clicking on the IMACD process ID.
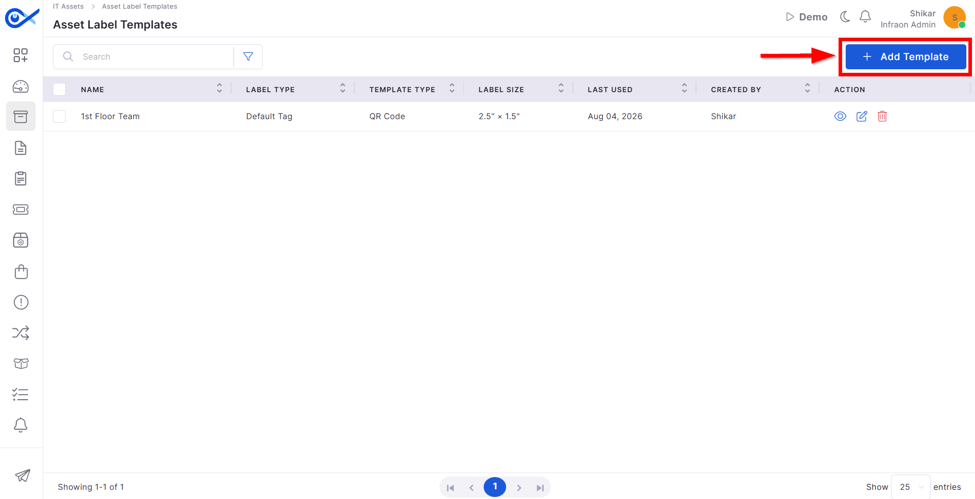
Navigate to the ‘Add Template’ section on the right panel of the page in the Gate Pass section.
Enter the below details:
Gate Pass| Fields
Label
Action
Description / Example
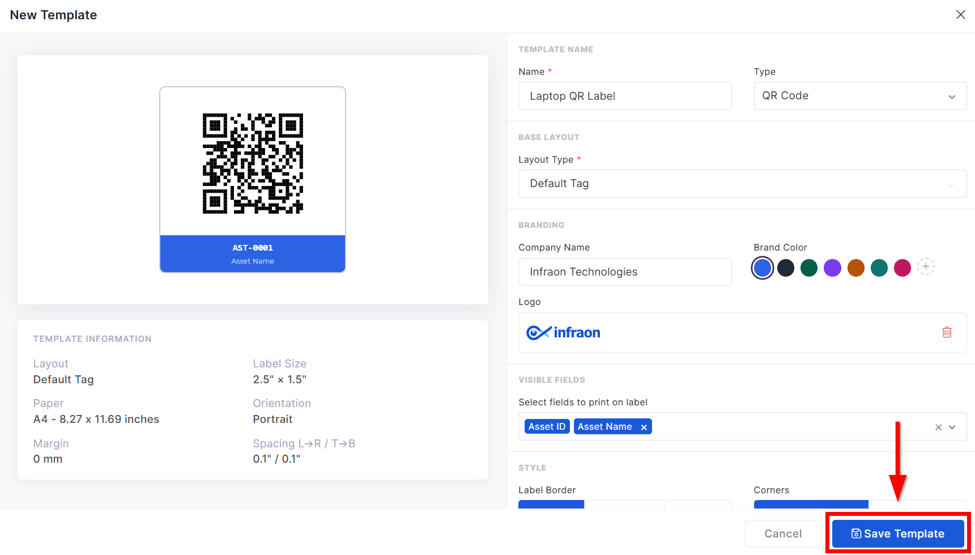
Select the type of scanning required, either barcode or QR code.
Once all the details are entered correctly, click on the Save option.
Asset Types
There are multiple types of assets in an organization. The first step of asset management is the categorization of assets. Broader categorization enables better management. The default categorization of assets within Infraon is as follows:
Asset Type -> Asset Category -> Asset Sub-Category -> Asset
The process of managing an asset depends on its type. Based on asset type, Infraon assets have been split into four modules.
IT Assets are physical assets or devices used in an organization's business activities that fall under the responsibility of IT staff. For example, computers, servers, routers, scanners, fax machines, printers, modems, hubs, and IoT (Internet of Things) devices.
Fixed Assets are any physical objects or vehicles you consider 'assets' to your organization. It can be easily converted into cash—for example, vehicles, machinery, equipment, etc.
Consumables are assets that organizations use. They must be replaced regularly because they wear out or are used up—for example, mouse devices, external keyboards, computer cables, printer toners, etc.
Software Assets are any functional software in an organization that requires service level agreement to ensure compliance with software licenses. For example, software assets may be internal or external, on-premises, or in the cloud.
Within these asset Types, assets are further classified into:
Categories – Categories are also referred to as 'parent' categories. A category is the first division of assets within the selected asset type. For example, within IT assets, there can be categories like laptops, desktops, etc.
Sub-Categories - Sub-categories are also referred to as child categories. The sub-category is the next level of asset division within the category. For example, if the categories are laptop or desktop, sub-categories within IT assets can be Dell, Lenovo, Apple, etc. Assets or asset items can be added here.
Refer to the and sections for details and instructions.
Expand the left menu panel.
Click on Assets
Select the respective asset type.
Click on the respective asset category or asset to view more details.
Assets can be added at the category and sub-category levels. Regardless of the asset type, the steps to view, add, edit, and manage assets are the same.
Data without perspective can be useless. To maximize the use of data, Infraon provides attractive and easily customizable reports that ensure data monitoring is appropriate for everyone within the organization.
Infraon reports provide a detailed analysis of the performance and fault-related data collected. Reports include:
Trending, pattern, and summary analysis to analyze past behavior.
Perform trend analysis and pattern analysis with historical data to help predict future behavior.
Infraon's default reports are highly configurable and flexible. Collecting, summarizing, and pruning historical data makes long-term data easily manageable. The combination of real-time and historical reporting aids in identifying trends, predicting system behaviour, and making well-informed management decisions to drive future expansions.
Infraon's timescale and data fields in the report filter the asset details at a granular level using the columns, timescale orders, and order by. Improvising asset report functionality, providing enhanced data analysis and filtering capabilities.
Infraon supports exporting reports and pre-configured auto-reports in PDF/Excel/CSV formats. Advanced real-time and historical reporting capabilities can be customized according to user preferences to help them view essential data.
CMDB View
Easily establish connections between assets and their respective locations or departments. Navigate to the asset, click 'relationship,' and choose 'upstream' or 'downstream.' Explore an intuitive dropdown menu with location and department options, which makes asset management more precise and streamlined.
Update CI relation and asset when user, requester, department, asset, or location is modified, and CI relation created based on the rule
Introducing CI Rule Configuration in CMDB! Customize rules for departments, locations, requesters, software, and users. Required rules are automatically added. Enable/disable CI visibility based on relationships and configurations for a tailored experience.
Select edit or delete
Allows users to delete or edit the Business Unit available.
Business Unit Head
Select a user
Selects the Business Unit Head from the list of existing users.
Example: John Smith.
Submit
Click Submit
Click the Submit button to save the Business Unit.
Business Unit Name
View
Identifies each Business Unit.
Example: IT Operations.
Description
View
Displays the description provided for the Business Unit.
Business Unit Head
View
Displays the user assigned as the Business Unit Head.
Business Unit Name
Enter a name
Mandatory field used to identify the Business Unit.
Example: IT Operations.
Description
Enter a description
Business Unit Creation
The Business Unit Name is mandatory, while the Description is optional and limited to 500 characters. The Business Unit Head can only be selected from existing users.
Action
Optional field used to provide additional information about the Business Unit. Maximum 500 characters.
Example: Handles infrastructure and IT operations.
Select Gate Pass Template
Select a template from the Select Gate Pass Template dropdown.
Allows the user to select an existing gate pass template for the asset movement.
Add Template
Click Add Template.
Instructions to add a Gate Pass
Note: Click the Add Custom Field to personalize your pass with additional information beyond the standard categories. This can help ensure smoother gate procedures and improve record-keeping.
Opens the Generate Gate Pass section, where the user can enter the required gate pass details.
Add Audit
Add New Audit
Use this option to create a new IT Asset Audit record for performing physical and/or logical verification of assets.
To add a new audit:
Navigate to IT Asset → IT Asset Audit Record.
From the top panel, select Add New Audit.
Configure the audit using the fields described below.
Add Audit | Audit Details
Label
Action
Description / Example
Click Next to proceed to asset mapping.
This step associates assets with an audit record. In this step, users select the IT or Fixed Assets that must undergo verification as part of the audit. Multiple assets can be linked to a single audit to ensure comprehensive coverage.
Assets are added through a dedicated selection window, where users can search, filter, and select the required assets. Once linked, these assets become part of the audit scope and are evaluated using the assigned audit checklist.
To add the asset, select Add to proceed.
Link Asset | Add Audit
Label
Action
Description / Example
Now select the assets to link them to the Audit records.
Links the selected assets to the audit record, adds them to the audit scope, and then moves the workflow to the Audit Checklist stage.
Here, users can select the required to configure the checklist that will be used for audit execution. The selected template defines the verification fields and checkpoints that auditors must complete for the mapped assets.
Once the configuration is complete, click Save to finalize and create the audit record in the system.
Once an audit record is created and assigned, the designated auditor can perform the audit for the mapped assets. The audit process allows auditors to verify asset location and condition using the configured checklist and record audit results for each asset.
From the IT Asset Audit Record list page, auditors can initiate the audit directly from the Action column.
Navigate to IT Asset → IT Asset Audit Record.
In the Action column, select Audit for the required audit record.
The audit workspace displays the mapped assets and the associated audit checklist.
Auditors can Export asset and checklist data in XLSX format, if required.
Select an asset and click Asset Audit to begin auditing the selected asset.
The Audit details page has three tabs:
The Audit Details screen is used to perform the actual audit for an asset. It captures location verification, condition checks, audit status, and checklist responses based on the selected template.
Audit Details | IT Asset Audit Record
Label
Action
Description / Example
After completing all required fields and checklist entries, click Submit Audit to save the audit results for the selected asset.
This action records the audit outcome and updates the audit progress for the overall audit record.
The Attachments section allows auditors to upload and manage supporting evidence related to the audit. This helps validate audit findings and maintain verifiable records for compliance and future reference.
Auditors can upload files such as asset photos, barcode/QR code images, condition evidence, or audit documents directly from this section.
Add Attachments
To add an attachment:
Navigate to Audit Details.
Open the Attachments section.
Click Add to upload files.
Select the appropriate category and provide an optional description.
Attachments | Fields Description
Label
Action
Description / Example
Uploaded attachments are displayed within the Attachments section and remain linked to the audited asset for reference.
The Recent Activities section displays a chronological log of all actions performed on the audit record. It captures key events, including audit creation, asset mapping, status updates, attachment uploads, and audit completion.
This section provides clear visibility into who performed each action and when, ensuring traceability and accountability throughout the audit lifecycle.
Once all assigned assets have been audited and the required details are recorded, the auditor can select Mark as Completed to finalize the audit. This action confirms that the audit activities are complete and updates the audit status accordingly.
Knowledge Base
A Knowledge Base (KB) is a repository of information about products, services, related topics, etc., intended for self-service. KB makes it easy for users to search for solutions instead of contacting the help desk or experts for repeated/common problems. It is recommended to include articles/guides about all products and services within the organization to enable contactless, round-the-clock self-service.
Infraon's Knowledge Base module enables users to author their articles, curate articles/guides from internal or external sources, and use, share, and manage knowledge across organizations and end-users.
Why Knowledge Base?
Studies conducted by Forrester and Ciboodle state that:
70% of customers prefer to use a company's website to get answers to their questions rather than use phone or email.
An efficient knowledge base can enable customers to manage 85% of their relationship with an enterprise without interacting with humans, allowing organizations to save.
Organizations saw a 50% increase in Customer Satisfaction ratings through social Customer Support (Public Knowledge Base).
An adequate Knowledge Base empowers the end user to quickly find the necessary answers and information without having to go through the hassle of waiting to get hold of an agent on call or waiting for their incident to get assigned to a Techie.
Having said that, to get all the advantages of a Knowledge Base, it is essential to present such complicated and detailed information in a user-friendly format, which Infraon's Knowledge Base offers. Infraon's KB is designed to add quick problem-solving tips, troubleshooting guides, answers to frequently asked questions, sharing best practices through Articles, known errors, and so on in a user-friendly manner.
A study by Coleman Parkes for Amdocs states that 91%of customers would be glad to use the available online database only if it is tailored to their needs. As easy as it may seem to build a knowledge base, it is a constant 'Work in Progress.' Follow the below steps to build an effective KB.
Patch Management
This page provides an asset-centric view of patch status. Once patches are discovered and deployed, administrators can view all patches related to a specific asset directly from the asset details page.
This section represents the Asset-to-Patches relationship, allowing users to see which patches are installed or missing on an individual asset without leaving the asset context.
What You See on the Screen
The Patch Management tab within an asset displays a list of patches associated with the selected asset, categorized by installation status.
Installed – Patches that are already applied to the asset
Missing – Patches that are detected but not yet installed
to view detailed patch information or manage patches across multiple assets.
Allows users to select multiple missing patches for an asset and install them in a single action, reducing manual effort.
Gather
Optimize
Monitor
Re-Organize
Collect only necessary, helpful, and relevant information. Include both internal and external services offered by the organization.
Use Infraon's Incident to KB option or create a KB (article/FAQ etc.) directly.
Keep your content easy to understand and searchable. Ensure that your knowledge base is seamless to navigate through.
Add relevant tags to each KB article/documentation and keep the instructions simple and user-friendly.
Monitor and observe entered keywords, understand the usage of your end customer, and use them to enhance User Experience.
Tune your data and clean up your database regularly. Help customers find the information they are looking for effortlessly.
Delete/archive old articles and keep your KB clutter-free.
How to build an effective Knowledge Base?
Defines the name of the audit record. Use a clear, identifiable title that reflects the audit purpose.
Example: Laptop Physical Verification – Q1
Status
Select from the drop-down
Indicates the current state of the audit. The default status is New (Open) when created.
Other options include: In Progress (Ongoing), On Hold (Pending), and Close (Audit Done)
Audit Objective*
Select from the drop-down
Defines the scope of verification for the audit.
Options include:
Location Check: Verifies the physical location of assets
Asset Condition Check: Verifies the physical condition of assets
Both (Location & Condition Check): Verifies both location and condition
Type*
Select from the drop-down
Specifies how the audit is initiated.
Options include:
Scheduled: Audit runs based on a defined schedule
Random: One-time audit without scheduling
Start Date*
Select date
Specifies the date on which the audit begins. Mandatory for scheduled audits.
End Date*
Select date
Specifies the expected completion date of the audit and helps track audit duration.
Assignment Details
Contact Person*
Select from the drop-down
Identifies the primary point of contact responsible for coordinating the audit. This user is typically responsible for communication and follow-ups related to the audit.
Auditor Type*
Select an option
Defines whether the audit is performed by an internal user or an external entity.
Internal: Audit is conducted by users within the organization
External: Audit is conducted by third-party auditors
Auditor*
Select from the drop-down
Assign the auditor responsible for executing the audit. If External is selected, provide the auditor’s Email and Phone Number.
Notify Audit Scheduling
Click to enable the toggle
Enables audit scheduling and notification configuration. When enabled, scheduling details and email notifications can be configured.
Audit Schedule Details
Schedule Mode
Select an option
Defines how often the audit is triggered.
Options Include: Once, Every, Daily, Weekly, Monthly, and Yearly.
Scheduled At*
Select date and time
Displays the configured audit execution date, time, and time-zone.
Example: 13 January 2026, 12:00 (Asia/Kolkata)
Email Configurations
To*
Enter email address
Specifies the recipients who will receive audit notifications and reminders.
Subject*
Enter text
Defines the subject line of the audit notification email.
Example: Physical Asset Verification
Message Body
Edit content
Configures the audit notification email content. Supports predefined macros that dynamically populate audit information when the notification is triggered.
Filter
Click the filter icon
Apply filters to narrow down assets based on predefined criteria such as asset attributes or categories.
Asset Type
Select from the drop-down
Choose the asset category to display. Options include IT Asset and Fixed Asset.
Asset Category
Select from the drop-down
Filters assets based on categories such as Work Station, Laptop, Desktop, Server, etc., depending on the selected asset type.
Location Check*
Select from the drop-down
Indicates whether the asset is found at the expected location.
Options include:
Yes: Asset is present at the expected location
No: Asset is not found at the expected location
Misplaced: Asset is found, but at a different location
Asset Condition Check*
Select from the drop-down
Records the asset's physical condition.
Options include:
Good: Asset is functional and in acceptable condition.
Damaged: Asset has physical or functional damage.
Unknown: Condition could not be verified.
Audit Status*
Select from the drop-down
Represents the audit classification of the asset.
Options include:
Expected Assets: Asset was expected and successfully verified
Not Expected: Asset was found, but not part of the expected audit list
Expected and Not Found: Asset was expected but could not be located
Audit Comment*
Input field
Add remarks or observations related to the audit, such as location mismatch, damage details, or verification notes.
Example: Asset verified at the assigned location and found to be in good working condition. No physical damage or discrepancies observed during inspection.
Audit By*
Input field
Enter the name of the auditor who conducted the audit for this asset.
Example: Chris Johnson.
Audit Date and Time*
Select date and time
Specify the exact date and time when the audit was performed on the asset.
Checklist Fields
Input as applicable
Displays additional fields defined in the selected (such as Text, Dropdown, Date, DateTime, or Checkbox). These fields capture checklist-specific audit information.
Upload the file to associate it with the audit record.
Topology refers to how various nodes, devices, and connections on your network are physically or logically arranged in relation to each other. Topology View displays the complete topology of all the connected devices in the network. The connections are configured to change colours automatically based on the faults or thresholds.
Node:
Clicking on the node shows the inventory details about the selected node.
Node Devices:
SDH MUX
Routers
SDH EMS Firewall
PDH MUX
On the right click of the node, it shows the Device View, Active Events, and Services.
Below are the details which can be viewed:
Host Name
IP Address
Make
Model
The colours on the Node indicate the status of the device, which depends on the severity of the operation.
Blue -> Grey -> Green -> Yellow -> Orange -> Red -> Dark Red
(Green for Up, Red for Down, and Grey for Disabled devices).
Clicking on the edge shows the connection details and the current performance parameters between the connected nodes, depending on the type.
Below are the details which can be viewed:
Description
Source IP
Source Device
Source Port
Infraon Configuration
The Infraon Configuration module consists of all types of configurations required for the efficient functioning of modules. While there are multiple levels of configurations, few of these configurations are mandatory.
General Settings: Configure business hours, create tags for grouping assets, users, etc., and review the complete audit log.
User Management: Invite requesters and users, assign roles, group them as teams or departments, and view their leave information.
Service Management: Configure technical and service catalogues to offer services and products seamlessly through the self-service portal.
Notifications: Configure and track notifications sent through Infraon.
Infraon Automation: Configure workflows within Infraon to define a flow of process modules like Incident, Request, Etc.
Bots: Install agents to enable discovery and monitoring.
Organization: View and add organization and branch locations.
IT Operations: Add device credentials to initiate the discovery of devices.
Vendor configuration: Customize the multiple tasks in the vendor configuration module, access various details about the vendors, display them in the address book, easily edit or delete them and utilize them on the software license page for efficient management.
Infraon Platform: Check and edit account configuration settings.
A few additional configurations are needed to enable device monitoring. Follow the instructions in the links below to enable protocols as required.
Upgrade Option for Credential-less Organizations! Users can access the management portal to select services. Selected services, with 193 options, are enabled post-payment.
Enabling SNMP is vital to initiating the monitoring of the routers and switches. Follow the steps below to enable SNMP on Cisco routers and switches.
Connect to the router/switch via telnet.
prompt#telnet testrouter
Now, enter the password to enable mode.
Router>enable
What you see on the screen
Basic Details | Home Page
Password:
Router#
The next step is to configure your device:
Router#configure terminal.
Enter one configuration command per line and finish each line with CNTL/Z.
Router(config)#
Add the Read-Only community string using the following command.
Router(config)#snmp-server community public RO ('Public' is the Read-Only community string here)
For a Read-Write community, use the below command.
Router(config)#snmp-server community private RW ('Private' is the Read-Write community string here).
You can now exit the configuration mode and save the settings
Router(config)#exit
Router#write memory
Building configuration...
[OK]
Router#
Additional Configurations
Enabling SNMP in Cisco Routers/Switches
Pro feature in Infraon configuration
Enable SNMP Configurations in Cisco Routers and Switches
Purchase Management
Device Type
EMS Name
Firmware Version
Region
State
City
Location
Destination Ip
Destination Device
Destination Port
Layer Rate
Active Events (Click to redirect to the Active Events page)
Services (Click to redirect to the Services page)
Profile
Locate a Profile from the selected drop-down box.
Vendors
Locate a Vendor from the selected drop-down box.
Stop Auto Reload
Click to Stop (Default is Auto).
It reloads the topology view at every interval of 60 seconds.
Export
Creates a PDF of the current topology view.
Edit
To save a new topology profile or a new topology view. Drag nodes to adjust the view.
Arrows Key
Icons can be used to navigate through the topology diagram.
Zoom Key
Icons can be used to navigate through the topology diagram.
Label
Action
Description/ Example
Filter
Filter can be added based on the City and Condition from the drop-down box below.
Locate Node
Properties
Edge:
What you see on the screen
Note: The thickness of the interface indicates the offered Bandwidth.
Locate a Node from the drop-down. Select the No. of hops, using the drop-down menu. The selected number of neighbors will be displayed.
Click to see the map in full-screen for a wider view.
The following information is shown when the mouse pointer hovers over a Geomap location:
Name
Description
State
Name of the state(territory). Example: Karnataka, Tamil Nadu
District
Name of District. Example: Jalalsar, etc.
Total Sites
The Geomap pins show different colors based on the status of the nodes. The meaning of these colors are:
Color
Description
Green
All the nodes are up and running.
Orange
One or more nodes are in "Disabled" status.
Gray
The maps can be viewed in the following types:
View
OSM
Google Roadmap
Google Terrain
Google Altered Roadmap
Google Satellite
Google Terrain Only
Google Hybrid
Bing Road
Bing Aerial
Bing Aerial with Labels
Bing Road Dark
Offline Map
and can be Sort By:
City
District
State
Country
Label
Action/ Description
Save
Click to save the current map view in the network diagram.
Rescan
Click to rescan the map view.
Working on a Purchase Order
Once a Purchase Order (PO) is created, users with the necessary privileges can manage and process it further. The PO record opens in a pop-up window containing four tabs that provide different views and actions related to the PO.
PO Details
Summary
Displays all information entered during PO creation, including:
Basic Details – Order name, vendor, department, currency, delivery date, etc.
Item & Cost Details – Item name, category, quantity, pricing, discount, tax, and total cost breakdown.
Asset Received
This view shows a detailed summary of assets associated with the PO. It helps track order progress, including the number of items ordered, received, and pending.
Users can classify and organize files for clarity and compliance when uploading attachments to a Purchase Order.
The Shipment Creation feature allows users to create and manage shipments against an approved Purchase Order (PO). Users can create full or partial shipments based on the available quantities in the Purchase Order.
A shipment records the delivery information, shipment items, addresses, contact details, and attachments. Once the shipment is created, the received and available quantities in the Purchase Order are updated accordingly.
The Shipment section is available from the Purchase Order view page. The Add Shipment option is available only when the Purchase Order is Approved and has quantities remaining to be received.
Label
Action
Description / Example
Shipping | Shipment Items
Label
Action
Description / Example
After creation, users can view the shipment and update its status, such as Ready for Dispatch or Dispatched. Once the shipment is delivered, users can use Receive Asset to record the received items.
The received assets are linked to the shipment and added to the IT Asset page. Shipment information is also available from the associated Vendor page.
Shipment | Status Details
Label
Action
Description / Example
The Activity Log provides a detailed history of all actions and updates related to a Purchase Order (PO). It captures every modification authorized users make, including updates to terms and conditions, vendor details, billing/shipping addresses, currency, department, payment terms, and expected delivery dates.
Each log entry is time-stamped and tagged with the user who acted, making monitoring and auditing PO activities easy. The log is organized chronologically, with the most recent changes displayed at the top for quick reference.
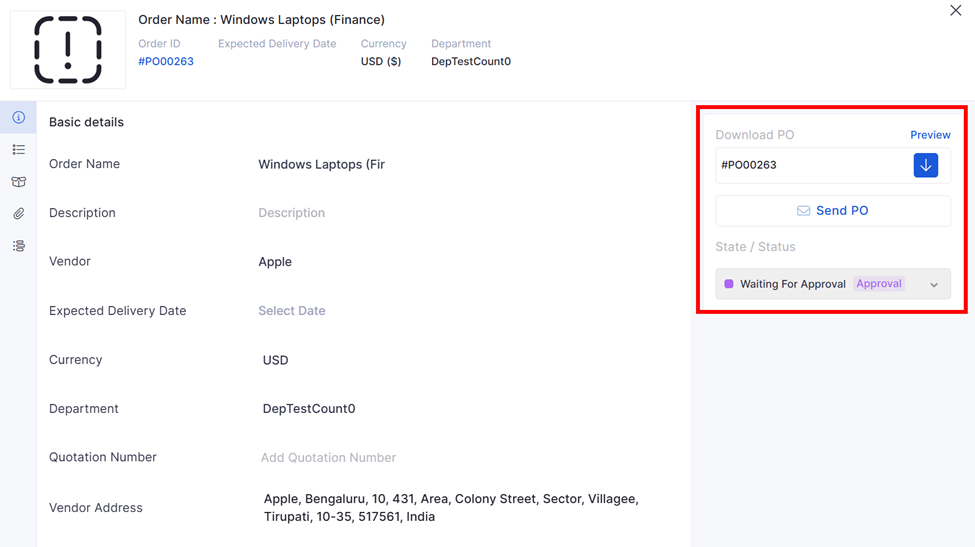
The State / Status indicator reflects the current Purchase Order (PO) stage within its lifecycle. It helps users quickly identify whether a PO is still being drafted or is awaiting approval.
PO Workflow | Basic Details
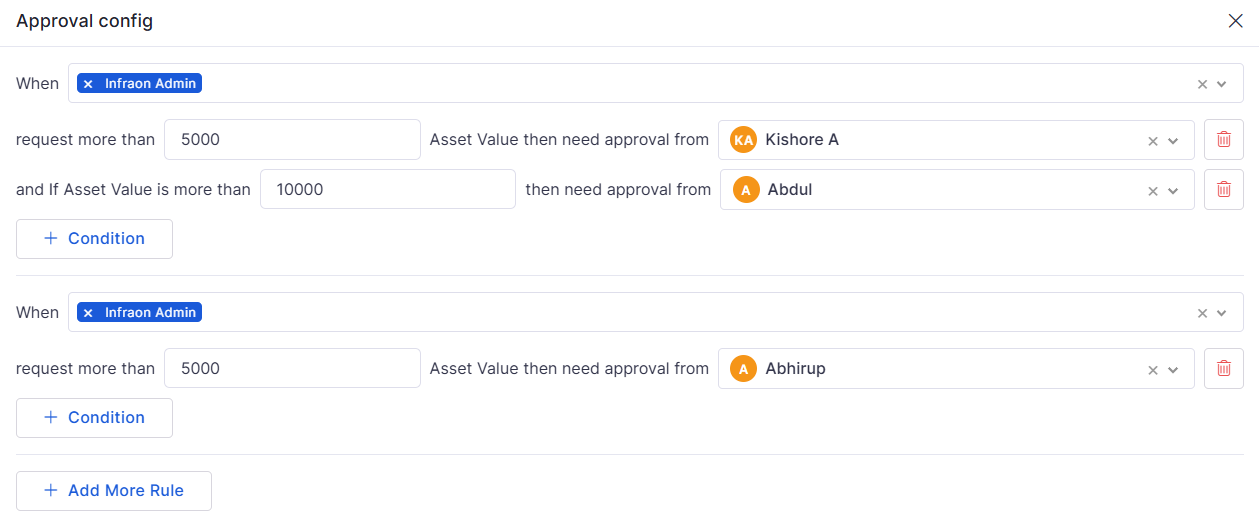
Infraon Infinity supports Purchase Order approval through both the application UI and email-based approval actions. Once the Purchase Order reaches the configured approval stage, authorized approvers can review and approve or reject it according to the configured workflow.
Authorized approvers can directly approve or reject a Purchase Order from the Purchase Order Edit page.
To approve a Purchase Order from the Edit page:
Navigate to Purchase Order.
Open the required Purchase Order that is in Waiting for Approval status.
Click Edit to open the Purchase Order Edit page.
Move to the Terms and Conditions step in the stepper.
Click Approve.
In the approval window:
Enter comments in the Comment section.
Add or select a signature if signature approval is enabled in the workflow.
Click:
After the approval action is completed:
The Purchase Order status is updated automatically.
Approval or rejection comments are recorded in the recent activity/history section.
For multi-level approvals, the next approver in the workflow can continue the approval process.
Infraon Infinity also allows approvers to approve or reject Purchase Orders directly from email approval actions.
When a Purchase Order is submitted for approval, approval emails are automatically sent to the approvers configured in the workflow.
To approve a Purchase Order through email:
Open the approval email received for the Purchase Order.
Click Take Action from the email notification.
Review the Purchase Order details in the approval page.
Enter comments if required.
Software License
The Software License module helps track and manage software licenses across the organization. It allows administrators to record license details, monitor allocation and usage, and maintain compliance by mapping licenses to software, publishers, and vendors.
How does it work
These are added manually or imported using CSV and mapped to the relevant software and publisher. The system tracks purchased and allocated permits in real time and supports scheduled usage checks to monitor thresholds. Licenses can be searched, filtered, edited, or updated in bulk to maintain accurate and compliant license records.
What you see on the screen
The page displays all available licenses in a centralized list. From the left panel, users can view licenses groupedby publisher categories, making it easier to navigate and manage licenses across different software vendors.
Software License | Basic Details
Label
Action
Description / Example
The Actions button in the top panel provides options to manage software licenses in bulk.
This option allows administrators to configure scheduled notifications when software license usage exceeds a defined threshold.
Schedule Usage Alerts | Basic Details
Label
Action
Description / Example
Once configured, the system automatically monitors license usage based on the defined schedule and sends notifications to the selected recipients whenever the usage threshold is exceeded.
This option allows administrators to update existing software licenses in bulk using a CSV file.
Using Bulk Edit, users can modify license attributes, including license count, cost, validity dates, compliance details, notification settings, and allocation information, for licenses already in the system.
Refer to for detailed steps on file preparation, column mapping, and validation rules.
Archived Asset
The page displays assets that have been archived from the active IT Assets and Fixed Assets pages. You can archive assets when they are no longer required for active asset management, such as when an asset is retired, disposed of, or becomes inactive. Archiving removes the asset from active asset views while retaining its asset information for future reference and management.
What You See on the Screen
The Archived Assets page provides separate tabs for IT Assets and Fixed Assets. Each tab displays only the archived assets of the selected asset type.
Archived Assets | Basic Details
Label
Action
Description / Example
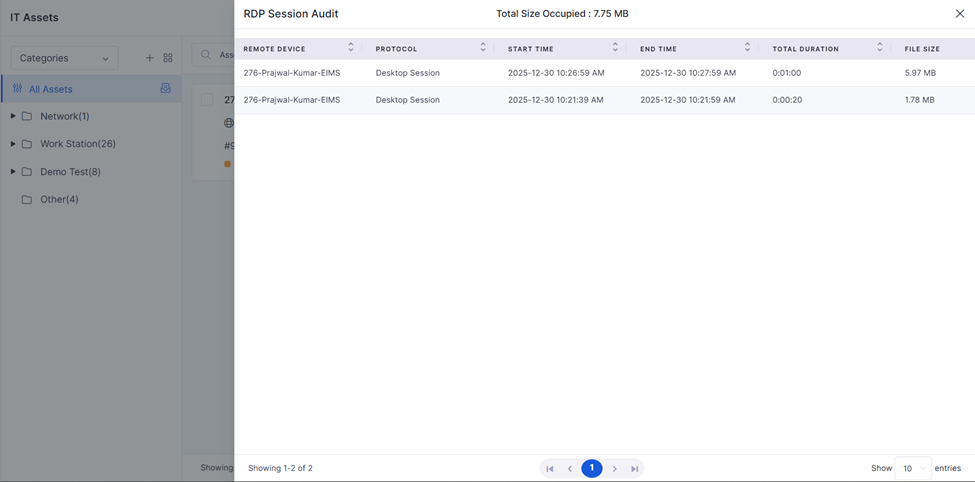
Remote Desktop Protocol
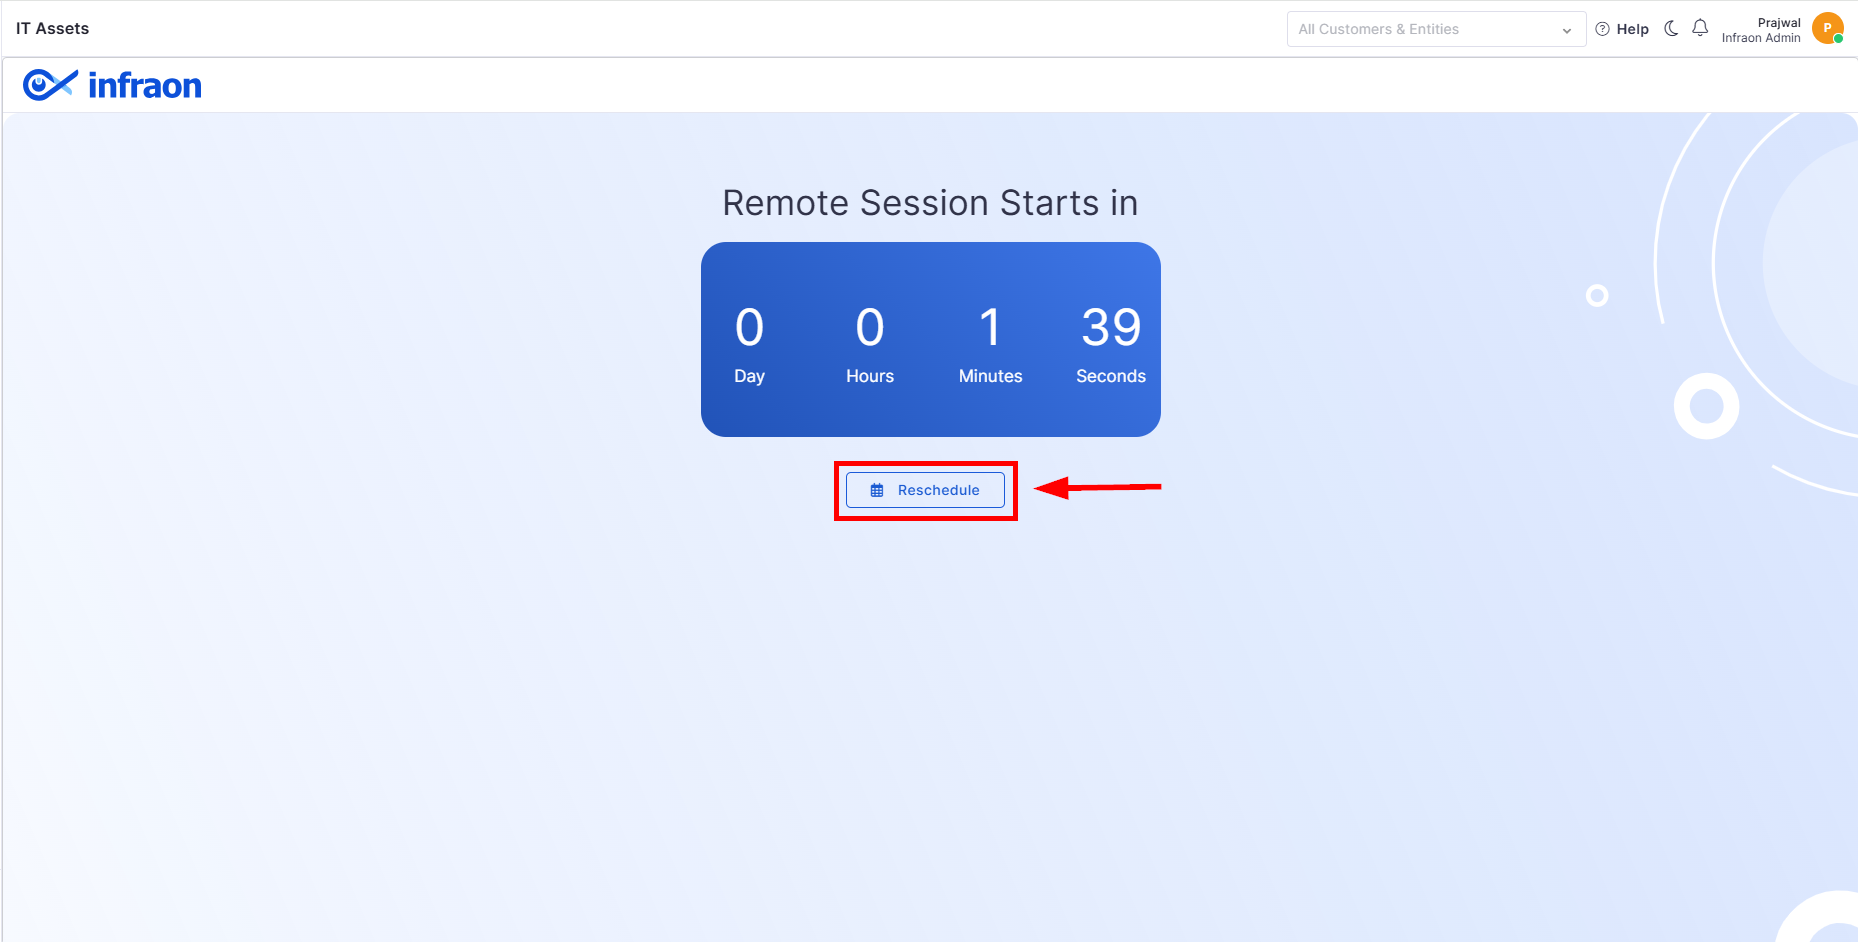
The RDP in the Infraon platform enables administrators and technicians to securely access and manage user systems remotely. It provides flexibility to either request access with user consent or perform unattended sessions for critical operations such as patching, troubleshooting, or configuration changes.
With RDP, IT teams can:
Connect to user devices in real time for support or maintenance.
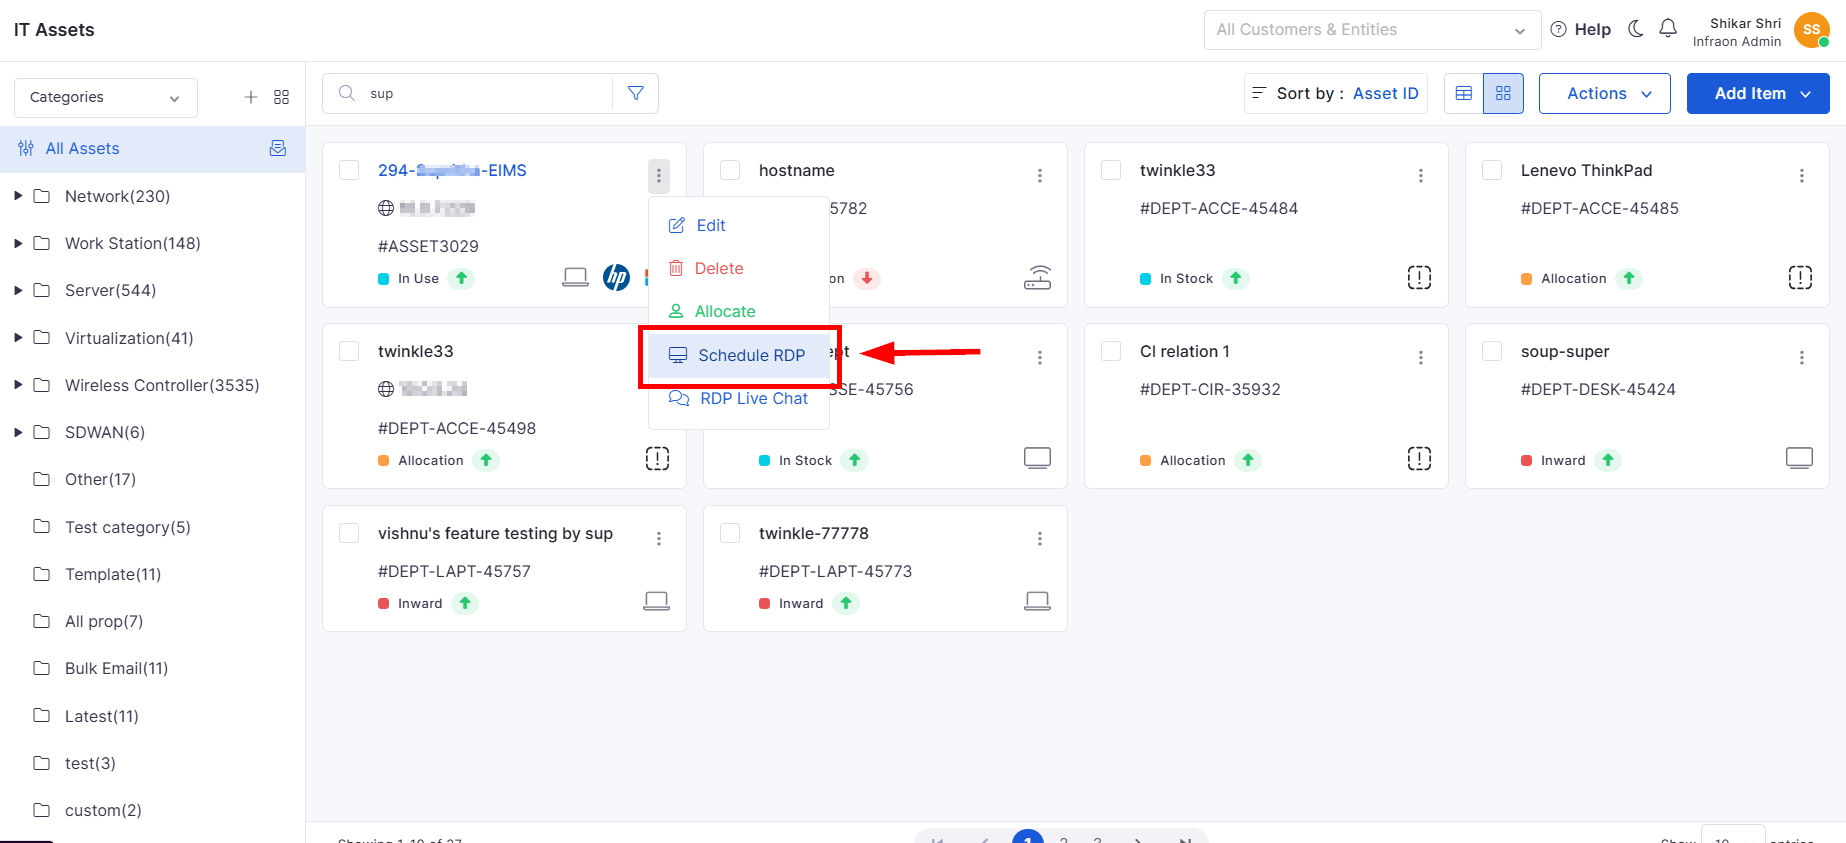
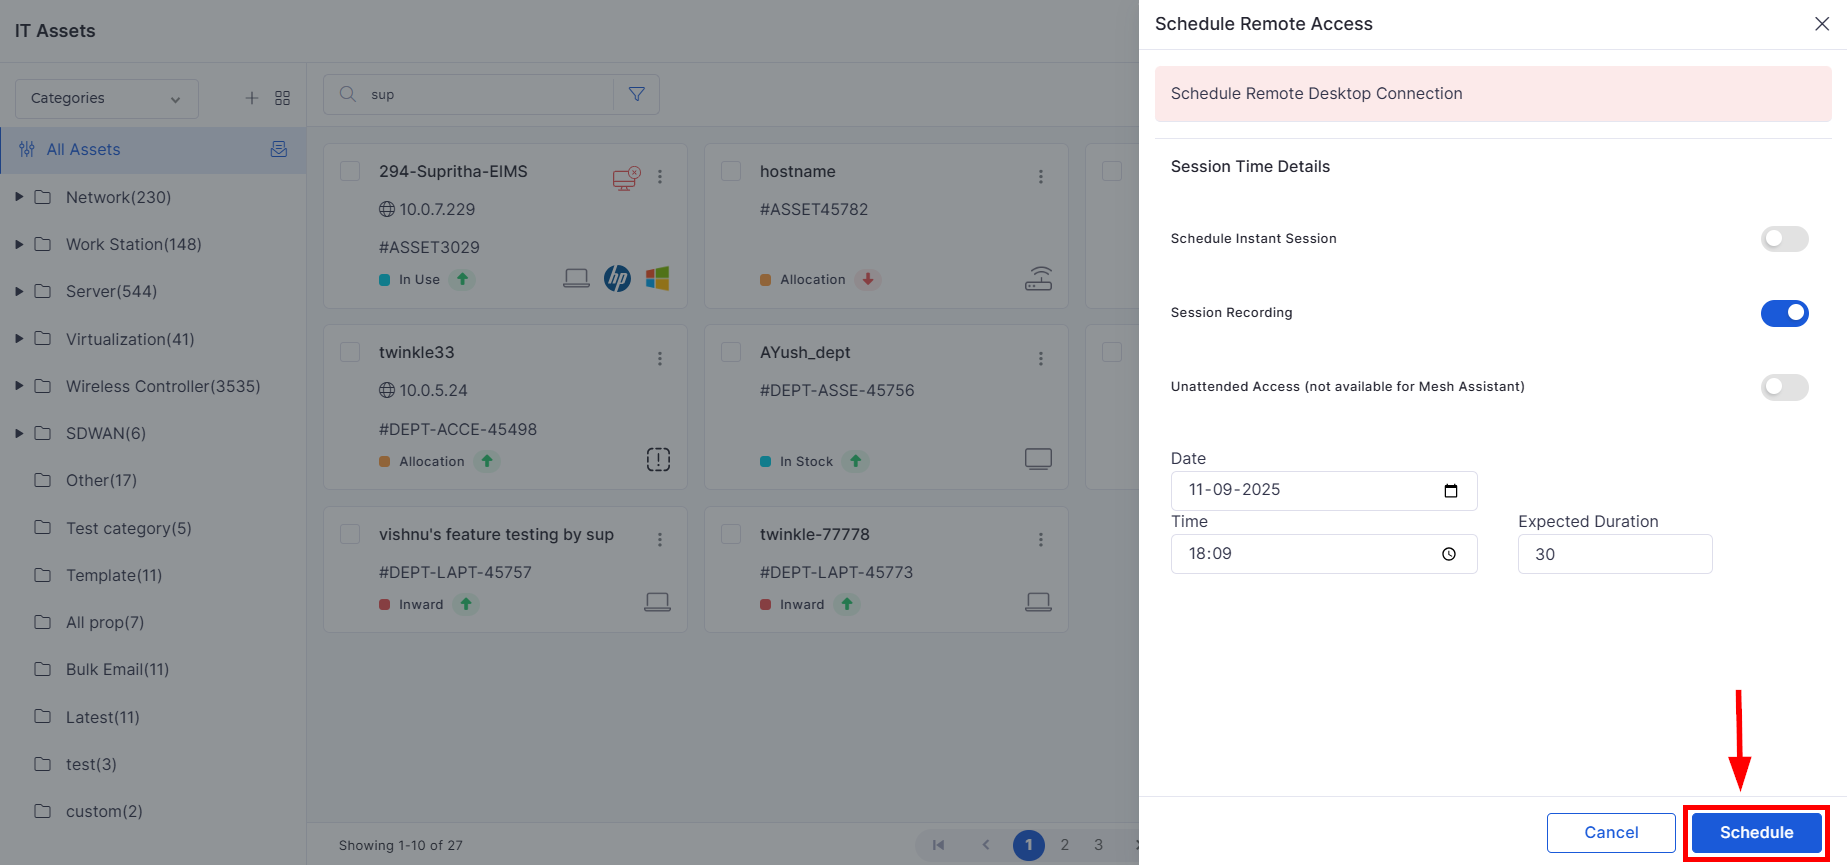
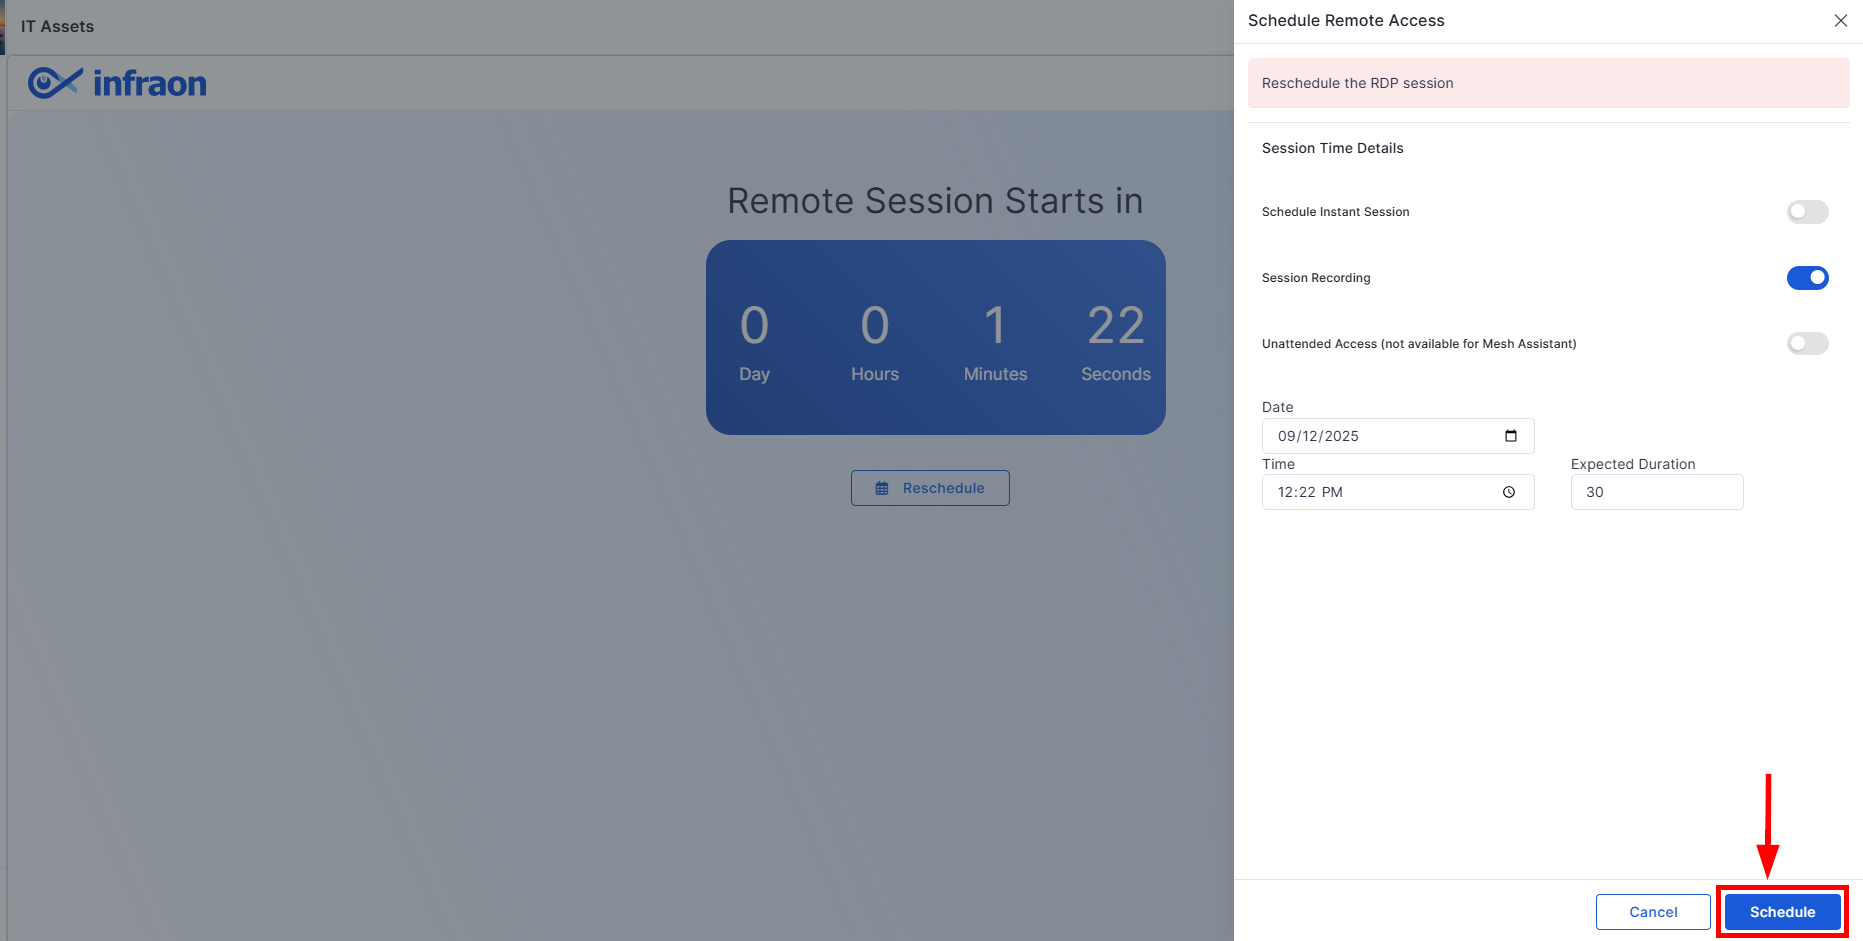
Schedule access sessions for specific time slots with predefined durations.
Asset
The CMDB part of ITSM is incorporated as Assets within Infraon. Infraon Assets allows administrators/asset managers to view and manage all organizational assets, i.e., all IT and non-IT assets, in one place.
Any device with an IP is known as an IT Asset or Node. It can be a Server, Router, Storage Device, Transport Device, Wireless controller, Access point, etc.; as part of an Asset, Infraon collects and maintains the complete inventory details for an asset.
Infraon collects basic yet important inventory information for each device, server, hypervisor, and application. The inventory information includes:
IP Address
Hostname
Device Type
Vendor
Model
Serial Number
Operating System and Version
MAC Address
CPU Information
Memory
HDD Details
Port Level information
Etc.,
For Hypervisors,
CPU Socket
No of Processor
CPU Speed
Hyper-Threading
Memory Size
Etc.,
Total number of sites in the state with the assets.
Total Devices
Total number of locations in the state with the assets.
Maintenance
Number of assets that are in the maintenance condition.
Up Devices
Number of assets that are up and in running condition.
Down Devices
Number of assets that are not reachable.
Disabled Devices
Number of assets that are in "Disabled" status.
Unknown
Number of assets whose status is not known.
If all the nodes are in "Disabled" status.
Red
If all the nodes are down.
Rebrand Infraon
The Rebrand Infraon module within the Infraon Portal allows administrators to customize the platform's appearance to align with the organization's branding. This fosters a more cohesive user experience and strengthens brand recognition.
Here's how it works:
Logo Upload
Upload your organization's logo to display it within the Infraon Infinity platform prominently. The recommended size (170x96 px) and supported file formats (jpeg, png) are provided to ensure optimal display.
Color Theme Selection
Admins can choose from pre-defined color themes (Fixed or Spaced Out) and light, dark, or semi-dark variations to match your organization's branding preferences.
Granular Color Control
Administrators can define specific colors for elements like the logo container, navbar, and user interface text for even greater customization. This allows for a highly tailored look and feel.
Language Selection
Admins can select the preferred language (English or Hindi) for the entire platform interface, ensuring user comfort and efficient interaction with the ITSM system.
Once the changes are satisfactory, click “Save” to proceed.
Select a field, condition, and value, then click Apply Filter.
Filters archived assets based on conditions such as Asset Name contains, Serial Number equal to, or Hostname not equal to.
Select Date Range
Select a relative or custom date range.
Displays assets archived within the selected period.
Example: Last 7 Days or a custom start and end date.
Actions
Restore
Click Restore for an archived asset.
Opens the Restore Asset sidebar, where you provide a Restore Reason and optional Restore Notes before restoring the asset.
IT Assets
Click to view archived IT assets.
Displays only archived IT Assets.
Fixed Assets
Click to view archived fixed assets.
Displays only archived Fixed Assets.
Search
Enter text to search for an asset.
Search using an asset name or other available asset information.
Example: Lenovo ThinkPad.
The Filter option supports multiple field and condition combinations. Available values for conditions such as In and Not In are limited to assets available in the selected archived asset tab.
Filter
Sort By
Select from the drop-down.
Sort asset records in ascending or descending order based on selected criteria. Available criteria include Hostname, Asset Name, Asset ID, Criticality, Operational Status, Status, Device Down, etc. Example: Sorting by “Operational Status” in ascending order will group active devices at the top.
Choose a category to classify the attachment:
Default Category
Quotation
Terms & Conditions
Invoiced and Receipts
Description
Enter text
Provide a brief note or context about the uploaded attachment.
Upload
Click to confirm
Uploads the selected file(s) to the PO record.
Cancel
Click to abort
Closes the pop-up without saving the changes.
Mode of Shipment
Select the shipment method.
Specifies how the items are being transported.
Example: Road Transport.
Challan Number
Enter the challan number.
Records the delivery/challan reference associated with the shipment.
Expected Arrival Date
Select the expected arrival date.
Specifies when the shipment is expected to arrive.
From Address
Select an existing address or add a new address.
Specifies where the shipment is being dispatched from. Addresses can be selected from the Address Book or added from the shipment page.
To Address
Select an existing address or add a new address.
Specifies where the shipment is being delivered.
Contact Details
Enter or select the contact information.
Specifies the person to contact regarding the shipment, typically the vendor contact.
Attachments
Upload supporting documents.
Allows users to attach shipment-related documents such as delivery documents or challans.
Received Quantity
View the quantity already received.
Shows how many units have already been received against the Purchase Order.
Shipment Quantity
Enter the quantity to be shipped.
Specifies how many units are included in the current shipment.
Example: If 100 laptops were ordered and 4 have already been received, the available quantity is 96. The user can create a shipment for any valid quantity up to 96.
Received Product History
View the receiving history.
Displays information about previously received items, including who received them and the quantity received.
Edit
Edit shipment information when permitted.
Shipment information can be edited while the shipment is in Draft status. Once it reaches another status, editing is restricted.
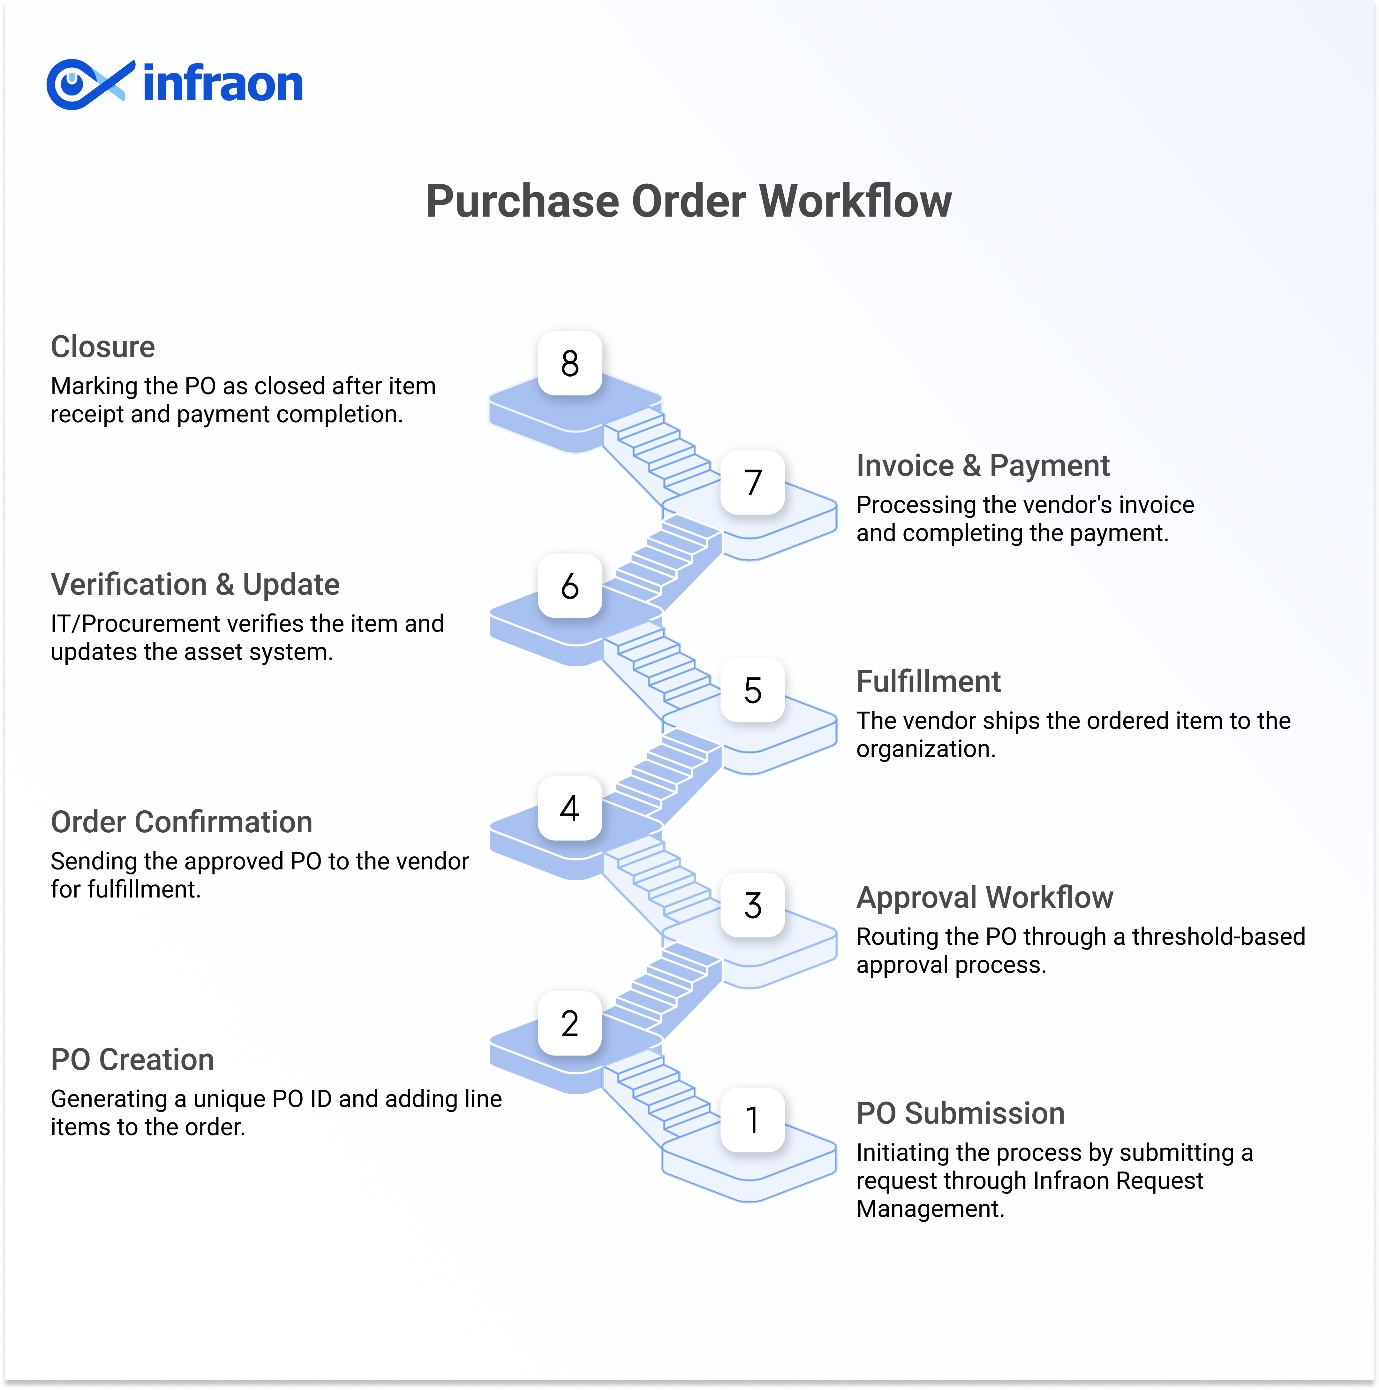
Procurement team records vendor quotes directly in the PO module. Each quote includes price, delivery timelines, and warranty terms and is stored for selection and audit in Infraon.
Negotiation (Execution)
After vendor discussions, procurement or the requesting department updates the PO with revised prices, delivery terms, or SLA changes. All changes are logged in the PO history.
Send to Supplier / Vendor (Execution)
The approved PO is sent to the selected vendor from the PO module. Vendor acknowledgement and expected delivery date are updated in the PO record.
Form Request and Confirmation (Execution)
Confirms final PO details, links any related PR, and performs compliance checks before execution.
Waiting for Quotation Approval (Execution)
PO remains in this stage until all threshold-based approvals are completed within the configured PO workflow in Infraon.
Waiting for Delivery (Execution)
Tracks vendor shipment status. Users can mark items as Received and view the Received Product History in real-time.
Received (Execution)
Items are verified against the PO in the Asset or Fixed Asset module. Received items are linked to asset records in Infraon CMDB.
Waiting for Invoice (Execution)
The vendor invoice is uploaded or linked to the PO. Finance validates invoice details against the PO and received assets.
Waiting for Payment (Execution)
Finance schedules payment according to the PO payment terms. Status is tracked until payment completion.
Payment Done (Execution)
Payment reference details are recorded in the PO record.
PO Close (Close)
PO is closed once all deliveries, invoices, and payments are completed. All related records remain searchable for reporting and audits.
Accept to approve the Purchase Order.
Reject the Purchase Order.
Add or select a signature if signature approval is enabled.
Click:
Accept to approve the Purchase Order.
Reject the Purchase Order.
After the action is completed:
The Purchase Order workflow status is updated automatically.
Approval comments and signature details are recorded in the approval history.
If multi-level approval is configured, the request is forwarded to the next approver in the workflow.
Label
Action
Description / Example
Category
Select from the drop-down.
Choose the asset type linked to the PO. Options include IT Asset or Fixed Asset.
Example: Selecting "IT Asset" will filter the list to only display IT-related items in the PO.
Provides additional information about the shipment.
Example: Laptop shipment - Batch 1.
Purchase Order
View the associated Purchase Order.
Item
Select/view the Purchase Order line item.
Displays the items included in the Purchase Order.
Available Quantity
View the remaining quantity available for shipment.
Status
Update the shipment status.
Tracks the current stage of the shipment.
Example: Ready for Dispatch → Dispatched.
Receive Asset
Click to record received assets.
Status / Stage
Description
Draft (Creation)
When a PO is initially created, it enters the Creation stage and is automatically marked with the status Draft. The PO is still being prepared, and details can be reviewed or edited before proceeding to the next stage.
Waiting for Approval/ Approval
Once the order process is ready to begin, users can advance the PO to the Approval stage. Upon doing so, a pop-up window will appear, prompting the user to define the type of approval and select the appropriate approver(s) — either a team or an individual manager.
Send to Reporting Manager: By default, the approval request is set to be sent to a team. When toggled on, the system switches to manager-based approval, allowing the user to select a specific reporting manager to approve the PO.
Select Team / User: Depending on the approval type, select the team or individual approver from the drop-down list.
An approval email is sent to all designated owners if a team is selected. If a manager is selected, the system sends the approval notification exclusively to that individual.
Example: Selecting Procurement Team will notify all procurement approvers; selecting Finance Manager—John Smith will notify only that manager.
Attachments
Shipping
Shipment Information
The system prevents users from entering a shipment quantity greater than the available Purchase Order quantity. At least one valid line item quantity is required to create a shipment.
Shipment Status and Receiving
Activity Log
State/ Status
Approval of Purchase Orders
Approve from the Edit Page
Approval through Email Action
Allows users to search for specific assets in the PO list.
Example: Enter "Laptop" to quickly locate all laptop assets in the PO.
Select from the drop-down
Identifies the Purchase Order against which the shipment is being created.
Indicates how many units are still available to be shipped.
Records the quantity received against the shipment and links the received assets to the shipment.
Received Quotes (Creation)
Users can switch to Grid View, click the Column Selection icon, and configure the columns displayed in the Software License grid.
Supports drag-and-drop column selection between Available Columns and Selected Columns. Users can rearrange, remove, save, and set preferred columns as the default for the grid view.
New License
Add or import licenses
Provides two options:
– Manually create a new software license.
– Upload licenses in bulk using a CSV file.
View Only Fields
License Name
View license name
Displays the name assigned to the software license.
Publisher
View publisher
Displays the publisher associated with the software. This value is derived automatically from the selected software.
Software
View software
Shows the software to which the license is mapped.
License Type
View license type
Indicates the license type, such as Per User, Per Device, or Subscription.
License Based On
View license metric
Displays the basis for counting the license, such as users, devices, or installations.
Vendor
View vendor details
Shows the vendor from whom the license was purchased.
Purchased
View purchased quantity
Displays the total number of licenses purchased.
Allocated
View allocated quantity
Shows the number of licenses currently allocated to users or assets.
Actions
Edit
Modify license
Allows users to update license details.
Delete
Remove license
Deletes the selected software license from the system.
Bulk Edit
Delete
Click to action
Select multiple software licenses in the grid or card view to update or delete them in a single action.
Auto License Management
Select one or multiple licenses and choose Enable or Disable
Automatically manages license allocation and deallocation based on software inventory scans.
When Enabled:
Automatically allocates licenses for discovered software during inventory scans.
Allocates licenses only for matching software versions.
Automatically deallocates licenses when software is uninstalled, upgraded, or downgraded.
Schedule Mode
Select frequency
Defines how often the system checks license usage.
Available options: Every, Daily, Weekly, Monthly.
At*
Set time(s)
Specifies one or more times at which the alert check should run. Multiple times can be added or removed.
Example: 10:28 AM, 10:30 AM, 10:32 AM.
Add Schedule
Add a time slot
Adds time entry under the selected schedule mode.
Example: Add another daily check at 11:00 AM.
Delete Schedule
Remove time slot
Removes a previously added schedule time.
Start (Optional)
Select start date and time
Defines when the alert schedule should begin.
Example: 2025-01-01 10:00 AM.
Until (Optional)
Select end date and time
Defines when the alert schedule should stop running.
Example: 2025-12-31 06:00 PM.
Schedule Summary
View schedule
Displays a read-only summary of the configured schedule.
Example: Scheduled for every day at 10:28, 10:30, and 10:32.
To*
Select recipients, select from the drop-down column.
Specifies the email recipients who will receive the license usage alerts.
Update Schedule
Save configuration
Saves or updates the scheduled license usage alert configuration.
Search
Search licenses
Allows users to search licenses by license name, software, publisher, or vendor.
Filter
Apply custom filters
Filters licenses using fields such as Software, Publisher, License Type, Vendor, etc. Supported conditions include in, not in, equal to, and not equal to.
Actions
Perform bulk actions
Provides two options:
Schedule License Usage: Allows users to configure scheduled notifications when software license usage exceeds a defined threshold.
Example: Send an alert when license usage crosses 50%, scheduled daily at 10:28 AM, 10:30 AM, and 10:32 AM, to selected email recipients.
Bulk Edit: Enables bulk updates or deletion of multiple software licenses at once by uploading a CSV file.
Threshold (%)*
Enter percentage
Defines the license usage percentage at which alerts should be triggered.
Example: 50 triggers alerts when allocated licenses reach or exceed 50% of the total.
The Schedule RDP allows administrators and technicians to plan remote sessions or initiate instant access sessions.
Before scheduling, ensure that the RDP component is installed on the end user’s device. Click here to view the installation guide.
Navigate to the IT Assets page and switch to Card View.
Select the asset for which you want to schedule an RDP session.
Click the More Options (three dots) icon and choose Schedule RDP.
The Schedule Remote Access sidebar opens. Configure the fields as per the table below.
Schedule Remote Access | Field Details
Label
Action
Description / Example
Schedule Instant Session
Toggle (Enable/Disable)
Allows immediate access instead of scheduling for a future date/time. When enabled, only the Expected Duration field is displayed. Default: Disabled.
Session Recording
After scheduling, session status is indicated with color-coded icons in the Asset Card View:
Orange → Session scheduled, waiting for the scheduled time.
Green → Session is active during the scheduled time.
Red → Session expired; user must reschedule to access again.
A session can be rescheduled only while it is in the scheduled state (indicated by the orange icon).
Click on the session icon to open the session details page.
The page will display the scheduled session details, including the start time and duration.
To make changes, click on the Reschedule icon.
Update the date and time fields as required, then save the changes to confirm the new schedule.
Once an RDP session is successfully scheduled and active, users can access file transfer options from the Remote Access page. Clicking the scheduled session icon navigates the user to the Remote Access page.
The left sidebar displays two options:
Remote Access Page | Basic Details
Label
Purpose
Description
Desktop
Remote desktop access
Opens the remote desktop interface, allowing the user to view and control the remote device screen.
File
File transfer
The File Transfer feature allows users to securely transfer files between their local system and the remote device during an active RDP session. This helps technicians upload required files to the remote system or download files from the remote device for troubleshooting, updates, or verification.
Step 1: After scheduling the RDP session, navigate to the Remote Access page.From the left sidebar, click File, then select Connect to establish the file transfer connection.
Step 2: Once connected, the user can view and access the local drives and directories available on the remote system.
Within the File Transfer interface, users can perform the following actions:
Rename files or folders
Edit files
Delete files or folders
Create new folders
Upload files
Cut, copy, and paste files
Zip files or folders
Refresh the directory view
Search for files using the Find option
Schedule RDP
Instructions to schedule RDP
Session Schedule Status
If no sessions are scheduled for a device, no session icon is displayed in the card view.
Reschedule Session
Remote Access page
File Transfer
File transfer is available only after an RDP session is successfully scheduled and connected.
Clicking any file downloads it to the user’s local system.
Template Configuration
The Template Configuration module allows administrators to manage and customize predefined email templates used across the Infraon Infinity platform. These templates are used for asset allocation, deallocation, hardware and software change notifications, reassignment notifications, and SLA escalation alerts.
Administrators can edit the available templates to modify email content, field mappings, privacy policy text, and notification details based on organizational requirements. The module also supports enabling a comment field in allocation and deallocation templates for end-user acknowledgment workflows.
Available Templates | Basic Details
Template
Purpose
Description/ Example
The Allocation and Deallocation templates include a Privacy Policy option that allows administrators to include organization-specific privacy or compliance information in notification emails.
When the Privacy Policy toggle is enabled:
The configured privacy policy content is displayed in allocation or deallocation emails.
End users can review the privacy terms before acknowledging the request.
Organizations can include terms, disclaimers, usage policies, or compliance-related information.
The Allocation and Deallocation templates also support the Enable Comment Field option.
When enabled:
End users must provide comments while accepting or rejecting allocation and deallocation requests.
The entered comments are captured in allocation reports and activity logs.
This helps administrators track acknowledgment details and user responses more effectively.
Add Asset/Add Item
Assets are referred to as Items in Infraon. Before adding an asset, the category and subcategory must be defined.
Navigate to the respective Asset page (IT, fixed, consumables, etc.). If no categories/subcategories are pre-defined, these can be added when adding the asset (item).
There are three ways to add assets:
Single Asset - You can add a single asset from the drop-down menu in the top right corner
Import from CSV - If you have the asset CSV file, you can import it from the drop-down menu in the top right corner.
SSP Configuration
The SSP (Self-Service Portal) Configuration module, exclusive to Infraon Management Admins, empowers admins to customize their end-users (SSP) experience.
Use the toggle buttons for each module to determine which options appear as menu items on the SSP portal's top panel.
This allows admins to tailor end-user functionality to your organization's needs.
From this central location, admins can control the visibility (by enabling the toggle buttons) of various modules within the SSP (located at the top panel).
The following section breaks down the details:
The Home section allows Infraon Management Admins to customize the appearance and content of the Self-Service Portal (SSP) Home page. Administrators can configure the Home page layout, customize the banner, and control which shortcuts and Quick Access sections are displayed to end users.
To configure the Home page:
Auto Deduplication
Auto Deduplication identifies and consolidates duplicate asset records created through multiple discovery sources, manual entry, imports, or integrations. It helps maintain a single trusted asset record (Golden Record) while preserving historical data and audit traceability.
Navigate to IT Asset/Fixed Asset → Action List →Deduplication to open the Duplicate Cluster page. The system groups potential duplicate asset records into clusters based on duplicate signals and similarity. Users can review the clusters, select the appropriate surviving record, resolve field conflicts, preview the impact, and then merge, split, mark the cluster as not duplicate, or leave it for later.
Asset Deduplication provides capabilities to:
Identify potential duplicate asset records.
Active users
Active users are currently logged in and actively engaging with activities. They represent the real-time presence of people currently using the system, indicating their availability for interaction or collaboration.
From this page:
You can see a list of users who are currently online.
Note: No actions can be performed from this page.
Introduction
Infraon ITAM User Manual
Information in this document is subject to change without prior notice. Companies, names, and data used in examples herein are fictitious and for illustration purposes only unless otherwise stated. No part of this document may be reproduced or transmitted in any form or by any means, electronic or mechanical, for any purpose without the express permission of Infraon Corp.
About this Document
This document aims to outline the features of Infraon products and give detailed information on how to customize & use all the modules available within Infraon products. This document contains sensitive information. Access to this document or the content within should be provided only to authorized users of Infraon products software on a need-to-know basis.
Any unauthorized use or sharing of information in this document will be considered a breach of respective confidentiality/copyright and shall be treated accordingly.
Payment and Financial Documents
Supports bulk enable/disable actions.
Records all allocation and deallocation activities in audit logs.
When Disabled:
Automatic allocation and deallocation will not occur during inventory scans.
Add Assets through Discovery - This only applies to IT assets. Any asset with an IP can be discovered using agent-based discovery. Refer to the 'Discovery' section for details.
Go to Asset -> Asset Type.
Click the 'Add' button -> Single Asset.
There are two tabs on the 'Add Asset' page. Refer to the table for information.
Define Asset | Details
Label
Action
Description/Example
Asset Name*
Add your asset name.
Asset names can be server, host, computer, device, etc.
Category
* Upload images if you have product images.
Click 'Next' to add 'Asset Properties.'
Please refer to the previously mentioned asset properties, which are located in the 'Add asset Categories' section.
Upon clicking on the added assets, icons appear at the top, including the owner, requester, tag, print, and additional options.
Two sections will be displayed on this page when clicking on the asset.
Asset name: This section displays the asset name, IP address, and status. The status can be modified to Trial run, in use, Maintenance, Parts repairs, Accident/failure, Audit, or Lost. To add the requester's location and allocation details, click "more options."
Sections: On the left side of the page, there are seven sections represented by tabs; clicking on these tabs will display specific data on the right side of the page. These sections include:
Details: If an asset picture has been uploaded, the details section will display it. It displays essential details such as hostname, device type, asset status, Asset ID, barcode, IP address, QR code, make, and OS name.
Performance section: System uptime, CPU utilization, memory, and Disk is displayed.
Attachment: Attachments can be added by clicking the 'add' button and uploading a CSV file.
Details: Assets such as Alias, Asset Name, IP Version, and Model are displayed.
Owner: Owner details such as name, e-mail, and phone number are displayed.
Asset Lifecycle: The asset life cycle refers to the stages that an asset goes through, from its acquisition to retirement, encompassing its management, maintenance, and utilization throughout its entire existence.
Hardware: Any hardware components collectively enable the device to function and perform specific tasks.
Following are the sections within the 'Asset properties' tab:
Sections
Show Only Mandatory button.
Back
Submit
Label
Description/Example
Sections
Under sections, you can find various asset properties. If your assets have more than one property, you can select multiple properties and fill in the details in the left section.
Show Only Mandatory Button
When you toggle the show only mandatory button, you will get only the hardware properties, and you need to fill in only those details.
Back Button
Go to Asset -> Asset Type
Click the 'Add' button -> Import from CSV
In the 'Import from CSV,' there are two tabs:
Upload | Details
Label
Action
Description/Example
Category*
Select asset category using the drop-down menu.
Server, Fans, etc. Download the sample CSV file and add details accordingly.
Import Asset List from CSV*
You can either drag and drop the file or browse to upload the CSV file.
Click 'Next' to continue with column matching.
Column Matching | Details
Once the column matching is completed, click 'Import' to import your asset CSV file for asset management.
Asset information is imported from the CSV to the respective category on Infraon. Asset information can be viewed, edited, or deleted using the respective action icon.
Note: The Next button will work only when you have filled out all the information correctly, viz., the correct asset name, category, owner/technician, requesters, user tags, and location.
Asset Properties | Details
Instructions to 'Import from CSV'
Note: The 'Next' button is enabled only when you have uploaded a relevant CSV file.
Navigate to Infraon Platform > SSP Configuration.
Enable the Home toggle.
Configure the required settings.
Save the changes.
Select the preferred Home page layout for the Self-Service Portal.
The available designs are:
Old Design
New Design
The selected design determines which Quick Help and Services options are displayed on the Home page.
Option
Description
Old Design
Displays the classic SSP Home page layout.
New Design
Displays the redesigned SSP Home page with additional configuration options, including the Banner Sub-title and updated Quick Help options.
The Banner Title defines the title displayed at the top of the SSP Home page.
Field
Description
Banner Title
Enter the title to display on the SSP Home page banner.
The Banner Subtitle is available only when New Design is selected.
Field
Description
Banner Sub-title
Enter the subtitle to display below the Banner Title on the SSP Home page. Available only for the New Design layout.
The Quick Help and Services section allows administrators to choose which shortcuts are displayed on the SSP Home page.
Only the selected shortcuts are shown to end users.
If all options are removed, the Quick Help and Services section is hidden from the SSP Home page.
The following shortcuts are available for the Old Design layout.
Option
Description
Browse Articles
Displays the Browse Articles shortcut.
View Tickets
Displays the View Tickets shortcut.
View Requests
The following shortcuts are available for the New Design layout.
Option
Description
View Tickets
Displays the View Tickets shortcut.
Submit Ticket
Displays the Submit Ticket shortcut.
Assets
The Quick Access section allows administrators to configure which expandable sections are displayed on the SSP Home page.
Users can quickly access frequently used information directly from the Home page.
The available options are listed below.
Option
Description
Active Tickets
Displays the Active Tickets section.
Active Requests
Displays the Active Requests section.
Assets
After configuration, the selected sections are displayed on the SSP Home page.
Review previous merge activities and undo eligible merges.
Asset Deduplication | Sidebar
Label
Action
Description / Example
Duplicate Clusters
Click
Opens the queue containing identified duplicate asset clusters for review and resolution.
Dedup Rules
Click
How it works
Toggle (Enable/Disable)
Enables automatic recording of the RDP session. Recorded sessions are stored securely and can be accessed only by authorized users. Default: Disabled.
Unattended Access (not available for Mesh Assistant)
Toggle (Enable/Disable)
Allows sessions to start instantly without requiring user approval. Available only when the Mesh Agent is used. Default: Disabled.
Date
Select from the calendar
Choose the date on which the RDP session should start.
Example: 11-09-2025.
Time
Select from the time picker
Define the exact start time of the RDP session.
Example: 18:09 (6:09 PM).
Expected Duration
Enter time in minutes.
Set how long the session should remain active. Default: 30 minutes.
Example: 60 minutes.
Cancel Button
Click to cancel scheduling
Closes the Schedule Remote Access window without saving changes.
Schedule Button
Click to confirm scheduling
Confirms the entered details and creates the scheduled session.
Opens the file transfer interface, enabling users to upload or download files to or from the remote device.
Allocation
Asset allocation notification
Used to send allocation details to end users when an asset is assigned. Includes asset details, requester details, allocation time, privacy policy, and optional comment field configuration.
Deallocation
Asset deallocation notification
Used to notify users when an allocated asset is deallocated or returned. Supports privacy policy and optional acknowledgment comments.
Hardware Changes
Hardware change notification
Sends notifications about hardware modifications or asset updates.
Software Changes
Software change notification
Used to notify users about software installation, updates, removal, or license-related changes.
Privacy Policy
Comment Field
Click the Edit icon under the Action column to modify a template.
Additional rows and fields can be added using the Add Row option available in the configuration panel.
Changes made to templates are reflected in the corresponding notification emails sent to end users.
View Contract Details
After creating a contract, click the required contract in the Contract Management list to open its details page. The page provides an overview of the contract, its basic information, item and cost details, related contracts, purchase orders, approvals, attachments, and activity history.
View Contract Details | Basic Details
Label
Action
Description
The Summary section displays key information about the selected contract, including its name, ID, type, contact person, and email address.
View Contract | Summary
This section displays the contract's validity period, renewal settings, expiry notifications, and applicable terms and conditions.
View Contract Details | Term of Contract
The Item and Cost Details section displays the items associated with the contract and their pricing information.
View Contract Details | Item and Cost Details
The Related Contracts section allows users to view contracts associated with the current contract and establish new contract relationships.
View Contract Details | Related Contracts
The Purchase Orders section allows users to view purchase orders associated with the contract, link existing purchase orders, and create new purchase orders.
View Contract Details | Purchase Orders
The Approval section displays the approval information associated with the contract.
View Contract Details | Approval
The Attachments section allows users to view existing files associated with the contract and add new attachments.
View Contract Details | Attachments
The Activity section maintains a history of events and changes associated with the contract. It helps users track updates made to contract information and related records.
Each activity entry may display the action performed, the user or system responsible, and the date and time of the event.
View Contract Details | Activity
Add Purchase Order
that displays key financial information based on the entered item detailsTo create a new Purchase Order (PO) in the Infraon platform, navigate to the top panel and click “+ Add Purchase Order.”
You can add a PO in two ways:
Manually – Enter each PO detail individually.
Bulk Upload – Upload a CSV file to add multiple POs simultaneously.
Instructions to Add a Purchase Order
Purchase Order | Basic Details
Add Address | Add PO
Item Details | Add PO
The Add Item section is used to add line items to the Purchase Order along with their cost details. It supports both hardware and software items, with fields dynamically changing based on the selected category type.
This section captures:
Item details (type, name, category)
Quantity and pricing information
Discount and tax calculations
There are two types:
Add Hardware Asset Items
Used to add physical asset items, such as IT or Fixed Assets, to the Purchase Order.
Displays fields like Item Name, Category Type, Category, Part Number, and Quantity
Suitable for the procurement of hardware devices and asset-based inventory
Terms of Order | Add PO
Once added, click on Save to confirm and add the PO to the inventory.
To import a purchase order using a CSV file, select the Import from CSV option from the list of available creation methods.
Follow these steps to complete the import successfully:
Download the sample CSV template to ensure the correct data structure.
Enter the required information into the CSV file accurately.
Upload the completed CSV file and click Next.
Review the system’s column mapping, adjust if needed, and click Import.
Uploaded SBOM
Uploaded SBOM allows users to upload an SBOM JSON file generated from a server and view the software inventory and vulnerability information contained in the file. This provides visibility into the server's applications, components, libraries, and associated vulnerabilities without requiring the user to manually enter the software information.
How does Uploaded SBOM work?
An SBOM JSON file can be generated from a server using the supported SBOM generation process and downloaded to the local system. The user can then upload the generated JSON file in the application. Once uploaded, the SBOM information contained in the file is displayed for review.
Use case
For example, an administrator generates an SBOM JSON file for a server and downloads it locally. The administrator uploads the JSON file to the application, after which the system displays the information available in the file, such as the number of components, applications, libraries, and vulnerabilities identified for that server.
What do you see on the screen?
When an SBOM JSON file is uploaded, the system displays the SBOM information contained in the file. Users can review the software and vulnerability information associated with the uploaded server data.
Upload SBOM
The upload section allows users to provide an SBOM JSON file generated from a server for viewing.
Label
Action
Description/Example
After an SBOM JSON file is uploaded, the Uploaded SBOM page displays the applications and their associated component and vulnerability information. Users can review the uploaded data and use the available actions to inspect or download component information.
The Uploaded SBOM table provides application, component, vulnerability, scanner, and upload information for the SBOM data.
Label
Action
Description/Example
The Actions column allows users to inspect the components associated with an uploaded application or download the component information.
Label
Action
Description/Example
Component Details
The top panel allows users to select the type of components they want to view. The component details provide information about the selected component, including its version, type, supplier, origin, and licensing information. Users can switch between two display modes to examine the components and their relationships.
Action Icon | Component Details
Label
Action
Description/Example
Agent Control Policy
The Agent Control Policy allows administrators to define rules and actions to manage agent behaviorin the system. A policy can be configured to specify the conditions under which actions should be performed on agents, including performance monitoring, event-based controls, and license-based event controls.
This helps automate agent management based on defined criteria and supports consistent agent performance and reliability.
The Agent Control Policy page displays the existing policies configured in the system.
Agent Control Policy | Basic Details
Label
Action
Description / Example
User Asset Lifecycle
The User Asset Lifecycle module provides complete visibility into all assets allocated to individual users throughout their lifecycle. It enables asset administrators, IT operations teams, and compliance teams to track current and historical asset assignments, monitor critical events, and enhance decision-making during offboarding, transfers, or audits.
This module consolidates every stage of the asset lifecycle — from onboarding to deallocation and end-of-life — capturing key events such as allocation, deallocation, transfers, hardware/software changes, new service requests, patch or security updates, warranty expiry, and AMC expiry.
User Asset Lifecycle | Basic Details
Add Request for Quotation
To create a new RFQ, click + Add Request for Quotation from the RFQ listing page. The system opens a multi-step wizard that guides you through creating the RFQ.
Complete the following tabs in sequence:
Quotation Request Properties – Enter the general information and quotation details.
Item Details – Add the products or services for which quotations are requested.
Feature Configuration
The Feature Configuration module enables administrators to manage and control system features and AI capabilities across the Infraon Platform through a centralized interface.
It allows configuration of feature behavior without requiring backend changes, ensuring consistency across modules and services. Administrators can track, discover, and enable all AI-related capabilities and privileges available within the organization.
The module provides granular control over how AI-driven functionalities operate, including knowledge base generation, search behavior, automation intelligence, and user experience settings.
The Meeting section allows administrators to configure the visibility and behavior of Meeting features in the Infraon Platform. Administrators can control Meeting field visibility, legacy Agenda functionality, the Meeting navbar shortcut, VC location booking conflicts, and the action buttons available in the Meeting view.
Meeting | Configuration
Category Template
The Category Template allows IT admins to predefine metadata fields, default behaviours, and automation logic for various asset categories. It acts as a blueprint that ensures asset records are consistent, enriched with required fields, and easily mapped during asset onboarding or discovery.
It is used to:
Apply default settings like location, ownership, and asset ID.
Choose which field groups (like Procurement or OS details) should appear when creating assets.
Add asset category.
Select an asset category that suits your requirement. Refer to the asset categories section for more details.
Asset ID
Customize the asset ID
Customize the asset ID for the assets as required by changing the prefix, number, type, and custom format of the asset ID from the Infraon Configuration.
You can opt for alphanumeric, random or auto-increment and a custom format. This allows overwriting of existing assets IDs that update all previously assigned IDs to the new format.
Asset Workflow (Beta)
Edit and customize the stages and statues of the IT Assets.
Flexible to edit and customize the stages and statuses of IT assets and change the flow based on the requirements. Easily modify the default workflow, add new statuses, and control transitions.
Asset Allocation Mail
Approve or reject the mail by identifying the owner of the email.
Acceptance and rejection are identified through the email sent to the asset's owner. Allowance of resending the email by eliminating the previous restriction.
Calculation
Depreciation calculation
Calculate the depreciation based on the two methods provided for the assets. These methods gradually reduce the asset's value to provide more accurate and comprehensive reports. Enhances the accuracy and efficiency of asset management, providing a more comprehensive view of asset performance.
Maintenance
Maintenance Configuration
Configure the assets for maintenance, schedule maintenance periods and easily track progress and history.
Self-service portal
Asset details in self-service portal
With the new portal, you can easily view the complete details of the assets, which allows for a self-service portal and a more convenient and user-friendly experience.
Owner/Technician
Select the owner or technician using the drop-down menu.
Requesters
Select the requester using the drop-down menu.
User Tag
Select user tags from the drop-down.
Assets may be grouped using these using tags.
Location
Add the asset location.
The location where you are working or performing business activities.
If you feel you have entered the incorrect information, you can click the back button and fill in the correct information.
Submit
After filling in all the asset property details, click on the submit button to import the single asset.
Ensure to add asset details to the default file before uploading.
Displays the View Requests shortcut.
View Change
Displays the View Change shortcut.
Submit Ticket
Displays the Submit Ticket shortcut.
Assets
Displays the Assets shortcut.
Service Catalogue
Displays the Service Catalog shortcut.
Displays the Assets shortcut.
View Requests
Displays the View Requests shortcut.
Workspace
Displays the Workspace shortcut.
Browse Articles
Displays the Browse Articles shortcut.
View Change
Displays the View Change shortcut.
Hardware & Devices
Displays the Hardware & Devices shortcut.
Displays the Assets section.
Trending Articles
Displays the Trending Articles section.
Service Catalogues
Displays the Service Catalogues section.
Opens the page where deduplication rules can be created and managed.
Merge History
Click
Opens the history of previous merge and keep-apart actions.
Duplicate Signals Summary
View
Displays a summary of the signals used to identify potential duplicate asset records.
Displays the name of the contract.
Vendor
Display
Displays the vendor associated with the contract.
Contract Admin
Display
Displays the user responsible for administering the contract.
Business Owners
Display
Displays the business owners associated with the contract.
Manufacturer
Display
Displays the manufacturer associated with the contract, if applicable.
Visibility Type
Display
Displays the configured visibility category for the contract.
Visibility to
Display
Displays the users, departments, or other entities permitted to access the contract.
Approver
Display
Displays the assigned approver or approval team.
Version
Display
Displays the contract version.
Currency
Display
Displays the currency used for the contract.
Description
Display
Displays the contract description.
Displays the contract's expiry or end date.
Auto Renew
Display
Displays the configured automatic renewal setting.
Notify Expiry
Display
Displays whether expiry notifications are enabled.
Notify Before
Display
Displays the number of days before expiry when a notification should be sent.
Notify To
Display
Displays the configured notification recipient.
Terms and Conditions
Display
Displays the terms and conditions associated with the contract. Multiple entries may be shown.
Additional Terms and Conditions
Display
Displays any additional terms and conditions entered for the contract.
Displays the name of the software associated with the contract item.
Quantity Type
Display
Displays the unit used to measure the quantity, such as User.
Price Unit
Display
Displays the price per unit for the item.
Total
Display
Displays the total amount for the item before any applicable adjustments.
Final Total
Display
Displays the final amount for the item after applicable calculations or adjustments.
Create Contract
Click
Create a new contract from the related contracts section, if the option is available.
Create Purchase Order
Click
Create a new purchase order from the contract details page, if the option is available.
Approval Status and History
View
View the available approval outcomes, approver details, and related information.
Attachment Details
View
Displays the available information about an attachment, such as its file name and category.
Version Added
Records the addition of a contract version.
Approver Added / Approver Removed
Records changes to the assigned approvers or approval team.
Attachment Added
Records when a file is attached to the contract.
Attachment Deleted
Records when an attachment is removed.
Added Related Contract(s)
Records when one or more related contracts are linked to the contract.
Added Related Purchase Order(s)
Records when one or more purchase orders are linked to the contract.
Contract Expiry Reminder Sent
Records when a contract expiry reminder is sent.
Contract Name
Display
Displays the name of the contract. For example, Dell Latitude 7450 Laptop.
Contract ID
Display
Displays the unique identifier assigned to the contract.
Contract Type
Display
Displays the type of contract selected during creation.
Contact Person
Display
Displays the contact person associated with the contract.
Email ID
Display
Displays the email address of the associated contact person.
Label
Action
Description
Contract ID
Display
Displays the unique identifier of the contract.
Contract Name *
Label
Action
Description
Start Date
Display
Displays the date on which the contract becomes effective.
End Date
Label
Action
Description
License Type
Display
Displays the type of software license, such as Perpetual or Subscription.
Software Name
Label
Action
Description
Related Contracts
View
Displays the contracts linked to the current contract.
Link Contract
Click
Label
Action
Description
Purchase Orders
View
Displays the purchase orders linked to the contract.
Link Purchase Order
Click
Label
Action
Description
Approval Details
View
View the available information about the contract approval process.
Approver
Display
Label
Action
Description
Attachments
View
Displays the files attached to the contract.
Add
Click
Activity
Description
Created
Records the initial creation of the contract.
Multiple Changes
Records multiple contract field updates made during an operation.
Description Added / Description Changed
Summary
Terms of Contract
Item and Cost Details
Note: The fields displayed in this section may vary depending on the selected contract type and the items associated with the contract.
Related Contracts
Purchase Orders
Approval
Attachments
Activity
Display
Display
Display
Link an existing contract to the current contract.
Link an existing purchase order to the contract.
Displays the assigned approver or approval team.
Add a new attachment related to the contract.
Records when a contract description is added or modified.
Components
View
Displays the number of components associated with the application.
Example: 312
Critical
View
Displays the number of Critical vulnerabilities identified for the application.
High
View
Displays the number of High vulnerabilities identified for the application.
Scanner
View
Displays the scanner or tool used to generate the SBOM data.
Uploaded On
View
Displays the date and time when the SBOM JSON file was uploaded.
Actions
Perform action
Provides actions to View Components and Download Components for the selected application.
Displays components categorized as files.
Library
Select
Displays library components associated with the application.
Application
Select
Displays components categorized as applications.
Operating System
Select
Displays components related to the operating system.
Name
View
Displays the name of the component.
Example: OpenSSL
Version
View
Displays the version of the component.
Example: 1.1.1
Type
View
Displays the type or category of the component.
Supplier
View
Displays the supplier associated with the component.
Origin
View
Displays the origin or source of the component.
License
View
Displays the license associated with the component.
Grid View
Select
Displays the component information in a structured grid with details such as Name, Version, Type, Supplier, Origin, and License.
Graph View
Select
Displays the components in a graphical representation, allowing users to visually understand the relationships between the components.
Upload SBOM
Click the Upload SBOM button
Allows users to upload the SBOM JSON file generated from a server.
SBOM JSON File
Select/Upload
Allows users to select the downloaded SBOM JSON file from the local system.
Uploaded SBOM Data
View
Displays the information contained in the uploaded SBOM file.
Application
View
Displays the name of the application identified in the uploaded SBOM.
Example: Google Chrome
Version
View
View Components
View
Opens the component details for the selected application. Users can filter the displayed components by category and switch between Grid View and Graph View.
Download Components
Download
All
Select
Displays all available components associated with the selected application.
Files
Column Details
Action Icons
Displays the version of the application.
Example: 124.0.6367.91
Downloads the component information associated with the selected application.
Select
Audits
Infraon records all automated and manual activities that occur within the tool and saves them as Audits.
Audit records information of the user, the action performed, the IP address, and the time stamp when the action was performed.
No actions can be performed from this page.
Account Signup
This module is designed for initial user registration within the Infraon Infinity platform. Administrators can verify their accounts by providing essential details like their email address, company name, and mobile number. This information is stored securely within the Infinity data, allowing registered administrators to access and utilize the various functionalities.
Department*
Select from the drop-down.
Specify the department raising the PO. Configure Departments by .
Example: IT Department
Expected Delivery Date
Select from the calendar drop-down
Define the date the goods or services are expected to be delivered.
Example: 15-Oct-2025
Vendor*
Select from the list or add new
Clicking on Vendor opens a list of all registered vendors. If the required vendor is not listed, click Add Vendor to register a new one.
Example: HP India Sales Pvt. Ltd.
Requested By*
Select from the drop-down
Select the user or requester who initiated the Purchase Order. The drop-down displays both Users and Requesters in a single list.
Use the search option to quickly locate a record. Additional records load automatically as you scroll through the list.
Example: John Mathews (User), David Kumar (Requester)
Payment Terms
Select from the drop-down
Specify the payment terms agreed upon with the vendor.
Example: 30 Days, 60 Days, 90 Days
Status
Select from the drop-down.
Indicates the current stage of the PO. Only two statuses are available at creation: Draft (Creation) and Waiting for Approval (Approval).
Quotation Number
Enter the quotation number and click Add
Specify the quotation reference received from the vendor. Multiple quotation numbers can be added to record revised or updated quotations for the same Purchase Order.
Example: QTN-10045, QTN-10045-REV1
Description
Click to add
Provide additional details or context about the PO.
Example: Procurement of high-performance laptops for newly hired software developers, each with 32GB RAM and 1TB SSD storage.
Repetitive PO Creation
Click to select the configuration
Opens a pop-up where users can schedule recurring PO creation:
Once – Create the PO at a specific date and time.
Daily – Repeat every day at the set time.
Weekly – Select specific weekdays.
Same as Shipping Address
Click to tick the check box
Copies the shipping address into the billing address field automatically.
Cost details are calculated based on quantity, unit price, discount, and tax
Add Software Asset Items
Used to add software licenses and subscriptions to the Purchase Order.
Enabled when Category Type = Software
Displays fields like Publisher, License Type, Software Name, License Based On, and Count
Removes hardware-specific fields such as Category and Part Number
Supports license-based procurement and tracking
Add Attachment
Click Add and upload file(s)
Upload quotation documents or supporting files related to the Purchase Order. You can attach one or more files and assign a category before submitting.
Example: Vendor Quotation.pdf, Revised Pricing Sheet.xlsx
Validate the data, correct any errors, and click Proceed with the valid records to finish the process.
Label
Action
Description / Example
Order Name*
Click to add
Enter a unique name for the PO to identify it easily.
Example: Purchase of 15 Dell Latitude 5440 Laptops – Q4
Currency*
Select from the drop-down
Label
Action
Description/ Example
Shipping Address*
Input text
Enter the complete shipping address where the goods or services will be delivered.
Example: 101, Tech Park, Bangalore – 560001
Billing Address
Input text
Label
Action
Description/ Example
Terms and Conditions
Input Text
Specify the contractual obligations, guidelines, or special instructions that govern the purchase. This may include delivery timelines, payment terms, warranty details, or return policies.
Example: “Delivery by 15-Oct-2025. 1-year manufacturer warranty applies.”
Remarks
Input Text
Infraon automatically generates a purchase order summary displaying key financial information based on the details of the entered item. This summary consolidates all cost-related data, including the total quantity of items, the aggregated cost before and after discounts, applicable tax values, and any shipping charges.
The following fields are available for review:
Total Order Quantity – Total number of items in the purchase order.
Subtotal (₹) – Combined cost of all items before applying discounts and taxes.
Discount (%) – Percentage discount applied to the subtotal.
Discount Amount (₹) – Monetary value of the discount.
For subcategories, use the format Category/Subcategory (e.g., Network/Router). Specify only the category if no subcategory is provided (e.g., Network).
The Expected Delivery Date must be in either mm/dd/yyyy or dd/mm/yyyy format and must not be a past date.
Tax Rate and Discount Rate must be numeric values between 0 and 100.
Choose the currency in which the PO will be processed.
Example: INR, USD, etc.
Enter the complete billing address associated with the PO.
Example: Corporate Office, MG Road, Bangalore – 560001
Add any additional notes or comments relevant to the purchase order that are not covered under the terms and conditions.
Example: “Please deliver the laptops to the IT storage room in Building B.”
Filter by Policy Name
Enter a policy name or keyword.
Filters the policy list based on the policy name.
Example: Enter Enterprise Agent Policy to locate the policy.
Name
View the policy name.
Displays the name assigned to the Agent Control Policy.
Agents
View the agent count.
Displays the number of agents associated with the policy.
To create a new Agent Control Policy, select Add Policy from the Agent Control Policy page.
The policy is configured through the following steps:
1
Agent Details
The Agent Details step is used to provide the basic information for the policy and select the agents to which the policy will apply.
Agent Details
Label
Action
Description / Example
Once added, click Next to continue.
2
The Configuration step defines the configuration details and rules for the selected agents. After completing Agent Details, click Next to proceed to Configuration. The configuration defined in this step determines the agent behaviour governed by the policy.
The Configuration section allows administrators to define how the agent communicates with the system, what performance information it collects, and which events and software-related information it manages.
Configuration | Basic Details
Label
Action
3
The Schedule step is used to define when the configured Agent Control Policy should be applied. After completing the configuration, proceed to Schedule to specify the required schedule options.
The Schedule section allows you to define when the agent inventory should be synchronized with the system. Select a schedule mode and specify the required date and time.
Label
Action
Description / Example
Only one policy can be applied to an agent at a time. If multiple policies are enabled for the same agent, the system overrides the existing policy with the latest policy.
What you see on the screen
Add Agent Control Policy
Action
Description / Example
Search
Click to input text.
Allows you to search for users in the lifecycle grid. You can search by Username, Email ID, or other identifiers.
Filter
Click to input text.
Provides advanced filtering options for refining results.
Fields: Username, Email, Role, Department. Conditions: in, not in, equal to, not equal to, contains, not contains.
Username
View only
Displays the user’s login ID in the system. Often shown with an associated email ID.
Example: 10034 / 10034@mail.com
Assigned Assets
View only
Shows the total assets currently allocated to the user. If multiple assets are assigned, only a few are listed, with the remainder summarized.
Example: 461005193, +2 More
Department Name
View only
Displays the department to which the user belongs.
Example: HR, Finance, IT, etc.
Role
View only
Shows the user’s role in the system (e.g., Requester, Admin, IT Manager).
Example: Requester, Infraon Admin, Vendor Admin, etc.
Is Active
View only
Displays whether the user account is active or inactive. Represented with a toggle and status label.
Example: Active (blue toggle ON), Inactive (grey toggle OFF)
Last Login Time
View only
Shows the most recent login timestamp of the user in the system.
Example: Sep 10, 2025 11:56 AM.
User Preferences also provide ownership-based filters that allow different personas to see assets depending on their relationship to the user.
User Asset Lifecycle | View Filters
Label
Description / Example
All Users
Displays the complete list of users in the system along with their currently assigned and historical assets.
Example: An administrator selects All Users to audit asset allocations across the entire organization.
Owned By Me
Shows only the assets that are currently allocated to the logged-in user.
Example: A requester chooses Owned By Me to review their assigned laptop and software history.
Owned By Requesters
This option in the User Asset Lifecycle module allows organizations to define filters that tailor the visibility of asset lifecycle events for different teams and user roles.
These preferences serve as organization-level filters, enabling teams to focus on the most relevant activities, such as assignments, transfers, security checks, or end-of-life events.
User Asset Preferences | Basic Details
Label
Description / Example
Assignment & Allocation
Track when an asset is assigned, acknowledged, transferred, or returned by a user.
Example: A laptop is assigned to an employee during onboarding and later returned during exit.
Usage & Operations
Monitor user activity on assets, including software installations, policy violations, and maintenance requests.
Example: Track when unauthorized software is installed or when a patch request is raised.
Movement & Transfer
When you select a user in the User Asset Lifecycle page, the system displays detailed asset information and activity timelines. The following table explains each element:
Vendor Details – Select one or more vendors to whom the RFQ will be sent.
Terms and Conditions – Specify the commercial terms, conditions, and other applicable notes.
After completing all the required information, submit the RFQ to initiate the procurement workflow.
The Quotation Request Properties tab is the first step in creating an RFQ. Use this tab to capture the basic request information, requester details, scheduling information, shipping details, and communication preferences.
Quotation Request Properties | Basic Details
Label
Action
Description / Example
Title
Enter the RFQ title.
Provide a meaningful title to identify the RFQ.
Example: Laptop Procurement - Q3 2026.
Currency
Once added, click on Next to save the current information and navigate to the Item Details tab.
The Item Details tab is used to add the products or services for which quotations are requested. You can manually add one or more line items, or use the CSV upload option to add multiple items in bulk. Each line item captures the required procurement details, such as item information, quantity, category, pricing, and other configured fields.
The page also provides options to download a sample CSV based on the configured line item fields and upload a completed CSV to create multiple line items at once. The uploaded file is validated against mandatory fields, configured columns, and user permissions before the items are added to the RFQ.
After adding all the required line items, review the calculated Subtotal, Tax, and Grand Total, and then click Next to proceed to the Vendor Details tab.
The Vendor Details tab is used to select the vendors who will receive the Request for Quotation (RFQ). You can add one or more vendors from the existing vendor repository and associate them with the RFQ. The selected vendors are used for RFQ communication, quotation submission, quotation comparison, and vendor evaluation during the procurement process.
Click + Add Vendor to open the Select Vendor window. Search for the required vendor (s), select one or more, then click Select Vendor to add them to the RFQ.
After the vendors are added, they appear in the Vendors Contacted section and become available for RFQ communication and quotation tracking.
The Terms and Conditions tab is the final step in creating an RFQ. Use this tab to specify the shipping address, reply-to contact details, and the applicable terms and conditions for the quotation. This information is shared with the selected vendors and forms part of the RFQ communication.
Terms & Conditions | Basic Details
Label
Action
Description / Example
Shipping Address
Enter the shipping address.
Specify the complete delivery address where the requested items are to be shipped.
Example: Warehouse A, Plot No. 45, Whitefield, Bengaluru - 560066.
Reply To Location
Select a reply-to location.
Once added, click Submit to validate the entered information and create the Request for Quotation (RFQ).
Quotation Request Properties
Item Details
Vendor Details
The vendors selected in this step are used throughout the RFQ lifecycle, including sending RFQs, receiving vendor quotations, comparing quotations, evaluating vendors, and creating Purchase Orders after vendor approval.
Terms and Conditions
Label
Action
Description / Example
Show "Associate With" field
Enable or disable the toggle.
Controls the visibility of the Associate With and Associated Items fields in the Add Meeting form.
When enabled, both fields are displayed. When disabled, both fields are removed from the Add Meeting form.
Show legacy multi-item Agenda list
Enable or disable the toggle.
Controls the legacy multi-item Agenda functionality.
When enabled, the detailed multi-item Agenda list, including the Add Agenda button and grid, is available in the Add Meeting form.
When disabled, the detailed Agenda list and its separate in-progress and completed views in Meeting Details are hidden. The single Agenda field remains available regardless of this setting.
Show Meeting navbar shortcut
Enable or disable the toggle.
Controls the Meeting shortcut displayed in the top navigation bar.
When enabled, the shortcut appears for users with the required Meeting permission.
When disabled, the shortcut is hidden even if the user has Meeting permissions. Clicking the shortcut opens the Meeting calendar in Workspace.
Meeting | Actions
Label
Action
Description / Example
Save Settings
Click to save the configuration.
Saves the configured Meeting settings and applies them to the Meeting module.
Reset to Default
Click to restore the default configuration.
Meeting
Configuration
Simplify asset management through structured, pre-configured templates.
The template configuration is split into two tabs:
Basic Details
Fields
This section allows administrators to configure behavior-based options for the asset category.
Label
Action
Description / Example
Notify End Users on Asset Allocation
Click the toggle to enable
Sends a notification to the end user when an asset is allocated. User can Accept/Deny the asset.
Notify End Users on Asset De-allocation
This tab allows you to define which metadata sections should appear when assets of this category are created or imported.
OS Properties (e.g., OS Name, Product Key, Version)
Admins can:
Select or deselect which sections to include in the template.
View or modify the fields inside each group by clicking Show Fields.
Create Custom Fields to accommodate organization-specific needs.
Basic Details
Once added, click on Next.
Fields
Once a template is configured, it automatically applies when creating assets under that category.
Multiple templates can be created to match the structure of workstations, servers, SaaS tools, or custom asset types.
Custom fields are fully supported for CSV imports and asset discovery.
Patch Management
Patch Management is the process of continuously identifying, tracking, and applying software updates across IT assets to ensure systems remain secure, stable, and compliant.
In Infraon platform, the Patch Management module provides a centralized view of all detected patches across the organization and their installation status on assets. It helps IT teams understand which patches are available, which are missing, and where action is required, enabling informed, controlled patch-deployment decisions.
Patch Management is currently supported only for Windows-based assets.
What Is a Patch?
A Patch is a software update released by a vendor to address known issues in an application or operating system. These issues may include security vulnerabilities, functional bugs, performance limitations, or compatibility problems.
Patches can apply to operating systems, third-party applications, utilities, or security components.
Installation Steps
Follow these steps to enable Patch Management in Infraon platform.
Step 1: Prerequisites
Ensure:
PATCH_MANAGEMENT is enabled
InfraonPatch feature flag is enabled
Infraon is installed on assets
Step 2: Install Infraon Patch App
Navigate to Marketplace
Locate
Click Install
The configuration page is displayed after installation.
Step 3: Configure and Verify
Enter the required configuration details
Click Verify
Click Submit
Step 4: Patch Agent Installation (Bulk)
After successful configuration, the Patch Agent is installed in bulk on all eligible inventory assets.
Step 5: Patch Agent Installation (Single Asset)
Navigate to Bots → Inventory Agent
Select the required asset
Click
Step 6: View All Patches
Navigate to Assets →
View all discovered patches in the organization
Step 11: Install Patch from Asset List
From the install the patch on assets where it is marked as Missing
Troubleshooting
If an older Patch Agent exists:
Navigate to C:\Program Files
Delete the infraon folder
Reinstall the Patch Agent
The Patch Management page provides a consolidated view of all patches detected across the organization, along with their associations with assets.
On the left panel, patches are categorized based on their installation status:
All displays every patch detected in the environment
Missing displays patches that are not yet installed on one or more assets
Installed display patches that have already been applied
This page primarily represents the Patches-to-Assets relationship, enabling users to identify which assets are impacted by a specific patch. to view the Assets-to-Patches relationship.
Patch | Basic Details
Label
Action
Description / Example
Patch details can be viewed by selecting a patch from the Patch Management list.The Patch Details page provides a comprehensive view of the selected patch, including its metadata, affected assets, and associated files.
The Summary tab provides high-level information about the selected patch. This view helps users quickly understand what the patch is, its importance, and its current approval and testing status.
In this section, users can view:
Patch title and description
Patch category and severity
Patch size
Release date
The Assets tab displays all assets associated with the selected patch, along with their current patch and operational status. This view helps users identify where the patch is already applied and which assets still require action.
The left panel allows users to filter assets based on patch status:
Missing: Displays assets where the selected patch has not yet been installed
Installed: Displays assets where the patch is already applied
In this section, users can:
Label
Action
Description / Example
The Files tab lists the files associated with the selected patch. This view provides visibility into the actual installation packages used during patch deployment.
In this section, users can view:
File name
Download URL
Release date of the file
File size
Add License
To add a new software license, navigate to the top panel and select New License.
Software licenses can be added using two methods:
Manually
Import from CSV
Manually
Fill in the basic license information as described below, then click Next.
License Information | Basic Details
Label
Action
Description / Example
Additional Details | Add Additional Information
Label
Action
Description / Example
Once all required details are entered, click Submit to add the software license to the platform.
It allows administrators to bulk add or update software licenses using a predefined CSV template.
Step 1: Go to Software License Management and click New License → Import from CSV from the top panel.
Step 2: Click Download CSV File to download the empty CSV template. Use this template to prepare software license data in the required format.
Step 3: Open the downloaded CSV file and fill in the required license details.
Step 4: Upload the prepared CSV file. On the Column Matching screen, map each CSV column to the corresponding software license field in the system, then proceed.
Step 5: The system validates all uploaded records. If issues are detected—such as missing mandatory fields, invalid values, incorrect date formats, duplicate licenses, or unsupported file types—appropriate error messages are displayed.
Step 6: If validation errors exist, download the invalid records for review and correction.
Only valid records will be processed. Click Proceed with Valid Records to continue.
Once the import is successful, the system displays a confirmation message. The imported software licenses are added to the Software License Management page and are available for review and further updates.
Vulnerability
SBOM Vulnerabilities provides a centralized view of vulnerabilities identified across the software components and applications discovered in scanned assets. It helps users review vulnerability severity, CVSS scores, fix states, affected packages, and scan information to support vulnerability assessment and remediation.
Vulnerabilities are identified from the software components recorded in the SBOM data of scanned assets. The identified CVEs are consolidated in the Vulnerabilities page, where users can review the vulnerability details and prioritize them based on severity and fix state.
The SBOM Vulnerability table is documented with the columns CVE ID, Application Name, Package, Version, Severity, CVSS Score, Fix State, Scan Time, and Actions.
When you open SBOM > Vulnerabilities, the SBOM Vulnerabilities page is displayed. The page provides an overview of the identified vulnerabilities followed by the vulnerability inventory table. Users can review vulnerability information and select the available action to view detailed information about a specific vulnerability.
The vulnerability table provides detailed information about each identified CVE, including the affected application and package, vulnerability severity, CVSS score, fix state, and scan information.
Software Metering
This module is used to monitor and analyze application usage across devices. It provides visibility into application usage frequency, duration, and activity at the process level, helping organizations understand actual software consumption.
This feature is primarily used for:
Tracking how often an application is used
Measuring time spent on each application
Identifying underutilized or unused software
View Purchase Requisition
The View Purchase Requisition page provides complete visibility into the Purchase Requisition details, workflow progress, line items, approvals, related records, attachments, and activity history.
Users can navigate between sections in the left panel and track the current PR status in the workflow stage panel.
Purchase Requisition View | Overview
The header section displays summarized information about the selected Purchase Requisition, including:
Purchase Requisition ID
Currency
Workspace
Workspace is a centralized collaboration and productivity hub within the Infraon platform that enables users to communicate, collaborate, manage operational activities, and interact with AI-powered assistants from a unified interface.
Workspace contains the following modules:
Calendar helps users manage schedules, events, meetings, shifts, and video conferences. It provides centralized visibility into planned activities and supports coordination across teams.
Workspace Settings is used to configure live chat behavior,technician allocation, session handling, and chat response settings within the Workspace module. It helps administrators manage live chat operations between requesters and support technicians.
Show Teams calendar sync
Enable or disable the toggle.
Controls the visibility of the Connect Teams option in the Meeting calendar.
When enabled, the Connect Teams option is displayed.
When disabled, the option is hidden. Teams calendar integration availability depends on the applicable product release and deployment.
Block VC location double-booking
Enable or disable the toggle.
Controls whether overlapping meetings can be scheduled for the same Participating VC Location.
When enabled, the system prevents the meeting from being saved if the selected VC location is already booked during an overlapping time slot and displays a conflict warning.
When disabled, you can schedule overlapping meetings without a conflict block.
Meeting action buttons
Select or clear the required options.
Controls the action buttons displayed in the Meeting view. Available options are Meeting Minutes, Meeting Notes, and Attendees. Deselecting an option removes the corresponding button from the Meeting view after the settings are saved.
Note: End Meeting is not controlled by this setting. Meeting permissions and RBAC control its visibility.
Resets the Meeting settings to their predefined default values.
Displays assets owned by requesters.
Owned By Technicians
Displays assets assigned to technicians or IT staff members responsible for managing and supporting assets.
Example: An IT Manager uses Owned By Technicians to check which assets are currently managed by their support team.
Log when users move assets to different locations, transfer them to others, or return them.
Example: An employee shifts from the Bangalore office to the Delhi office, and their allocated device is updated accordingly.
Support & Tickets
Capture user-raised tickets, repair status updates, and issue resolutions.
Example: A requester raises a ticket for a faulty monitor, and the lifecycle view shows the repair and resolution history.
Security & Compliance
Track user adherence to security policies, monitor encryption status, flag unauthorized access attempts, and log compliance audit results.
Example: Record antivirus scans, detect policy violations, or log failed login attempts.
End-of-Life & Recovery
Track asset returns from users, reassignment after exit, and data wipe confirmations.
Example: An employee’s laptop is collected, data-wiped, and reassigned to a new hire.
Click to select from the dropdown
Allows filtering lifecycle events by time range.
Options: Current Hour, Last 60 minutes, Today, Last 7 Days, Custom Range, etc.
User Preferences
Click to select a preference.
Filters lifecycle events by organizational categories (Assignment & Allocation, Usage & Operations, Movement & Transfer, Support & Tickets, Security & Compliance, End-of-Life & Recovery).
Example: Selecting Security & Compliance displays only encryption, antivirus, or compliance-related events.
Allocated Assets
View only
Displays assets currently allocated to the selected user. Includes details such as Asset Name, Serial Number, IP Address, Location/Entity, Allocation status, and deployment state.
Example: APPLE IMAC PRO INF-190
Owned Assets
View only
Shows assets owned by the selected user. These are linked through ownership relationships (not just allocation). Includes details like Asset ID, Serial Number, IP, and current status.
Example: Alex - INF-189
Previously Allocated Assets
View only
Displays assets that were previously assigned to the user but have since been deallocated or reassigned.
Example: DESKTOP-H14QMPB
Show Activity / Hide Activity
Click to expand/collapse.
Expands or collapses the lifecycle activity timeline for a specific asset. Shows historical changes and actions performed.
Example: State Changed from Manage to Deploy, Status Changed from In Use to Allocation – Performed by Shikar, Sep 10, 2025 05:58 PM.
Status
View only
Displays whether the user is active or inactive.
Example: Status: Is Active
User Information (Name & Email)
View only
Displays basic details of the selected user, including display name and email ID.
Example: Shikar Srivastava
Select the transaction currency.
Determines the currency used for quotation amounts.
Example: USD, EUR, INR.
Status
View or select the current RFQ status.
Displays the current workflow status. New RFQs are created in the Draft state by default.
Priority
Select the priority level.
Specifies the urgency of the RFQ.
Example: Low, Medium, High.
Location
Select the delivery or business location.
Associates the RFQ with the applicable location or branch.
Requested By
Select the requester.
Specifies the user raising the RFQ.
Buyer
Select the buyer responsible for the procurement.
Identifies the procurement owner responsible for processing the RFQ.
Requested Date
Select the request date.
Indicates when the RFQ was created or requested.
Required Date
Select the required delivery date.
Specifies the expected date by which the requested items are required.
Reporting Manager
Select the reporting manager.
Associates the RFQ with the requester's reporting manager, if applicable.
Payment Terms
Select the payment terms.
Defines the agreed payment conditions.
Example: NET-30.
Ship Via
Select the shipping method.
Specifies the preferred shipping or carrier method.
Example: DHL.
FOB Point
Enter the FOB point.
Specifies the shipping ownership transfer point.
Example: Warehouse A.
Freight Terms
Select the freight terms.
Defines the freight responsibility for the shipment.
Example: FOB Destination.
Quote Due Date
Select the quotation submission deadline.
Specifies the last date by which vendors must submit their quotations.
Print Date
Select the print date.
Specifies the date to be printed on the RFQ document, if required.
Description
Enter additional information.
Provide supporting details or instructions related to the RFQ.
Notify Vendor Before Quotation Due Date
Enable or disable the toggle.
Sends a reminder notification to vendors before the quotation submission deadline.
Specify the location from which vendor communications will be managed.
Contact Person
Select a contact person.
Choose the primary contact for vendor communication.
Terms and Conditions
Select the applicable terms and conditions.
Select a predefined terms and conditions template that will be included in the RFQ.
Click the toggle to enable
Sends a notification to the end user when the asset is de-allocated.
Customize Asset ID
Click the toggle to enable
Allows customization of asset IDs as per customer-defined formats. Helps ensure traceability and compliance with internal tagging rules.
Example: #ESOL-D-0038.
Note: Common categories must include the "Customized Asset Id" field for this to work.
Select default asset location
Select from the dropdown list
Automatically assigns a default location when an asset of this category is created or discovered.
Example: Head Office – Bengaluru.
Select default asset Owner/Technician
Select user(s) from dropdown
Assigns a default owner or technician to assets created under this category.
Workspace Settings
Calendar:
Description / Example
Agent Heartbeat Interval
Enter the interval in seconds.
Defines how frequently the agent sends a heartbeat to the system to indicate that it is active and connected.
Example: Enter 60 to send a heartbeat every 60 seconds.
Collect Performance Metrics
Enable or disable the option.
Enables the agent to collect performance-related metrics from the associated asset. When enabled, the agent collects the configured performance information.
Performance Metrics Sync Interval
Enter the interval in seconds.
Defines how frequently the collected performance metrics are synchronized with the system.
Example: Enter 300 to synchronize the metrics every 300 seconds.
Once added, click Next to continue.
Schedule Mode
Select the required schedule frequency: Once, Every, Daily, Weekly, or Monthly.
Determines how often the inventory synchronization is performed.
Once
Select Once and specify the date and time.
Runs the inventory synchronization only once at the specified date and time.
Every
Select Every and configure the required interval.
Runs the inventory synchronization repeatedly at the configured interval.
Daily
Select Daily and specify the time.
Runs the inventory synchronization every day at the specified time.
Example: Daily at 11:30 AM.
Weekly
Select Weekly and configure the required day and time.
Runs the inventory synchronization every week according to the configured schedule.
Monthly
Select Monthly and configure the required date and time.
Runs the inventory synchronization every month according to the configured schedule.
At
Select the date and enter the time.
Specifies when the inventory synchronization should run.
Example: 14 August 2026 at 11:30 AM.
After entering the scheduling details, click Submit to finalize the policy.
Profile Name*
Enter a name for the policy.
Defines the name used to identify the Agent Control Policy.
Example: Enterprise Agent Policy.
Select Agent*
Search for and select the required agents.
Determines which agents the policy will be applied to.
Search
Enter a keyword.
Searches the available agents to help locate the required agent.
Filter
Apply filter conditions.
Filters the available agents based on selected criteria.
Filter Condition
Define the required filtering criteria.
Allows administrators to narrow down the agent list based on specific agent/asset attributes.
Field
Select an attribute.
Defines the attribute on which the filter is applied.
Example: Asset Name.
Operator
Select the required operator.
Defines how the selected attribute should be evaluated.
Example: not in.
Value
Select or enter the required value.
Specifies the value against which the condition is evaluated.
Example: Select one or more asset names.
Add Control Policy
Add the selected control policy
Adds the selected control policy to the list of policies assigned to the asset.
Example: Select a control policy and click Add Control Policy to assign it to the asset.
Remove Control Policy
Remove the selected control policy
Removes the selected control policy from the asset's assigned policy list.
Example: Select an assigned control policy and click Remove Control Policy to unassign it.
Select All
Select all the listed control policies
Selects all control policies displayed in the list, allowing you to add or remove multiple policies at once.
Example: Click Select All to select every policy currently displayed.
The enhanced search functionality allows administrators to use both generic search and filter conditions when selecting agents. This is particularly useful when managing a large number of agents.
Configuration
Schedule
Severity
View only
Indicates the risk or importance level of the patch to help with prioritization.
Example: Critical, Unspecified, etc.
Release Date
View only
Shows when the vendor released the patch.
Example: Sep 09, 2025.
Category
View only
Indicates the type of patch.
Example: Security updates, Definition updates, Updates, etc.
KBID
View only
Displays the related Knowledge Base reference, if available.
Example: KB5065426.
Knowledge Base (KB) ID, if available
Support URL for reference
Test status and approval status
Asset Name
View only
Displays the name of the asset associated with the patch.
Example: 140-Sam-EIMS.
Asset ID
View only
Displays the asset's unique identifier.Example: ASSET0001.
Operational Status
View only
Indicates whether the asset is currently reachable or active.
Example: Up, Down.
Type
View only
Displays the asset type.Example: Laptop.
Status
View only
Indicates the asset usage or allocation status along with patch applicability.Example: In Use, Allocation.
Make
View only
Displays the manufacturer of the asset.Example: Lenovo, Dell.
Serial Number
View only
Displays the asset's hardware serial number.
Example: PF4R241T.
Bulk Actions
Select and apply
Allows users to select multiple assets using checkboxes and install the patch across all assets chosen at once. Select multiple missing assets and deploy the patch in a single action.
ID
Click to view more details.
Unique identifier for each patch. Clicking it opens the Patch Details page.Example: ZPH-W-0008.
Title
View only
Search
Click to search
Allow users to locate assets using keywords quickly. Search by asset name or asset ID to find a specific device.
Displays the name or description of the patch. No actions can be performed.
Example: 2025-09 Cumulative Update for Windows 11.
Enables advanced filtering using multiple fields and conditions.
Fields: CI ID, Asset Name, Asset ID, etc. Conditions: in, not in, contains, not contains, equal to, and not equal to.
Optional notes to describe the purpose or scope of the license.
Example: License for finance team users.
Publisher*
Select from the drop-down column
Software publisher associated with the license. This is derived from the selected software.
Example: Adobe.
Total number of licenses purchased or available.
Example: 300.
License Based On*
Select allocation basis
Defines how the license is allocated.
Example: User (license assigned per user).
License Key
Enter license key
Vendor-provided license key, if applicable.
Example: XXXX-YYYY-ZZZZ-AAAA.
Effective From*
Select start date
Date from which the license becomes active.
Example: 01-Jan-2025.
End Date / Trial End Date
Select end date
Applicable for Subscription or Trial licenses.
Example: 31-Dec-2025.
Payment Frequency*
Select frequency
Billing cycle for subscription licenses.
Example: Monthly.
Vendor
Select vendor
Vendor from whom the license was purchased.
Example: Adobe Authorized Reseller.
AMC Cost
Enter AMC amount
Annual Maintenance Contract cost, if applicable.
Example: ₹15,000.
AMC Start Date
Select date
Start date of AMC coverage.
Example: 01-Jan-2025.
AMC Expiry Date
Select date
End date of AMC coverage.
Example: 31-Dec-2025.
Notify user on license and AMC expiry
Enable / Disable
Sends alerts before license or AMC expiry.
Example: Enabled to notify 30 days before expiry.
Currency
Select currency
Currency used for the license cost.
Example: INR.
PO Number
Enter PO reference
Purchase Order number for procurement tracking.
Example: PO-2025-0041.
Invoice Number
Enter invoice reference
Invoice number received from the vendor.
Example: INV-ADBE-88901.
Invoice Date
Select invoice date
Date on which the invoice was issued.
Example: 05-Jan-2025.
Is Maintenance Included
Select from the drop-down column.
Indicates whether maintenance support is included with the license.
Example: Yes.
Compliance Status
Select from the drop-down column
Indicates license compliance status.
Option Includes: Compliance and Non-Compliance.
License Name*
Enter license name
Name used to identify the license in the system.
Example: Adobe Acrobat – User License.
Description
Department
Select from the drop-down column.
Department responsible for the license ownership.
Example: General Management.
Cost*
Enter total cost
Import From CSV
Important guidelines:
Mandatory fields such as License Name, Software, License Type, License Count, and License Based On must be provided.
Values for License Type must match the supported types (Perpetual, Subscription, Trial, Free License, Volume).
Dates must follow the YYYY-MM-DD format.
Numeric fields such as License Count, Cost, and AMC Cost must contain valid numbers.
Dropdown-based values (Publisher, Software, Vendor, Department, Compliance Status) must match existing values in the system.
Save the completed file in .csv format.
Enter description
Total cost of the license purchase.
Example: 1200.
Monthly – Choose a day of the month.
Quarterly – Schedule every three months.
Yearly – Schedule annually.
Once selections are made, a confirmation message will display the schedule details.
Example: Schedule every quarter on the 1st, 10:00 AM, to order IT consumables such as keyboards, mice, and docking stations.
Displays the unique identifier of the vulnerability.
Example: CVE-2024-1234
Application Name
View
The Actions column allows users to open the detailed information of a selected vulnerability for further investigation.
Label
Action
Description/Example
Overview
View
Displays the overview of the selected vulnerability.
The detailed specification confirms the CVE hero information, affected software, package information, description, data source, and references shown in the sidebar.
How does Vulnerability work?
Use case:
For example, if OpenSSL 1.1.1 is installed on an asset and a vulnerability such as CVE-2024-1234 is identified, the Vulnerabilities page displays the CVE, affected application and package, severity, CVSS score, fix state, and scan time. Users can select View to open the detailed vulnerability information.
What do you see on the screen?
Column Details
Action Icons
Supporting license optimization and cost control
Software metering uses agent-based tracking, in which installed agents continuously monitor application activity on devices. The data collected is processed and displayed in both summary and detailed views.
Metering is configured through rules, where one or more applications are grouped and tracked across selected devices or environments.
Software Metering works through agent-based tracking combined with rule configuration. Once a metering rule is created, it is pushed to the Inventory Agents installed on devices. These agents continuously monitor application usage (based on process activity) and send the collected data to the platform, where it is aggregated and displayed in summary and detailed views for analysis.
Key Points:
Rule-Based Tracking: Applications are monitored based on configured Software Metering rules.
Agent Dependency: Tracking is performed by Inventory Agents installed on devices.
Continuous Monitoring: Usage is captured when the application process is running, even if it is not actively used.
Sync Functionality: The Sync option ensures newly added or updated rules are applied to all agents and devices.
New Application Handling: Newly installed applications are tracked only if they are part of an existing rule.
New Device Handling: New devices start tracking only after receiving the configured rules (via sync or default push).
No Scheduling Required: Once configured, tracking runs automatically without manual intervention.
The Software Metering screen displays all configured Software Metering Rules along with their associated applications. It provides options for searching, filtering, creating, and managing rules, as well as synchronizing configurations with agents to ensure accurate tracking.
Software Metering | Basic Details
Label
Action
Description / Example
Search
Enter keyword
Allows you to search Software Metering rules using Rule Name or Application details.
Filter
Apply filter conditions
To create a new Software Metering rule, click on + Create Rule located at the top right corner of the page. A configuration panel opens, where you can define which applications to track and the rule's scope.
A rule is typically created per application or specific use case, making it easier to identify and analyze usage.
Create Rule | Basic Details
Label
Action
Description / Example
Rule Name
Enter value
Specify a unique and meaningful name for the rule, ideally based on the application being tracked.
Example: Microsoft Edge Usage Tracking
Software
Select from the list
How Does it Work
What you see on the screen
Create Rule
Once all details are entered, click Save to create and activate the rule.
Priority
Required Date
Requested By
PR Title and Description
Details Section
The Details section is loaded by default when the View page opens.
This section displays:
PR Information
Contract Reference details
Address Details
Additional requisition information configured during PR creation
Users can expand or collapse sections using the expand/collapse icon available on each section header.
The Item and Cost Details section displays all configured PR line items and procurement cost details.
This section includes:
Line item information added during PR creation
Quantity, tax, conversion factor, and order details
Cost summary including:
Subtotal
Tax
Grand Total
The line item grid supports pagination for viewing multiple records.
The Approval section displays the configured approval workflow for the Purchase Requisition. This section helps users track:
Current approver
Approval progress
Parallel approval configuration
Approval percentage requirements
Approval status
The workflow view updates dynamically based on the configured approval stages and actions performed by approvers.
The Vendor section displays the vendor-related information configured for the Purchase Requisition.
This section includes:
Vendor type
Vendor name
Payment terms
Shipping method
Tax and inspection-related configurations
The Terms and Conditions section displays the configured procurement terms associated with the Purchase Requisition.
This includes:
Terms and Conditions template
Additional procurement conditions
Procurement instructions configured during PR creation
The Related Records section displays associated records linked with the Purchase Requisition.
This section displays the record count for:
Purchase Orders
RFQs
Contract References
Users can quickly identify related procurement records from this section.
The Activity Log section maintains the complete audit trail of Purchase Requisition activities.
This section displays:
PR creation activities
Status changes
Approval actions
Contract updates
System-generated activities
Additional capabilities include:
Timeline view
Grid view
Activity search
Chronological tracking of updates and workflow actions
Details
Item and Cost Details
Approval Workflow
Vendor Details
Terms and Conditions
Related Records
Activity Log
Asset Lifecycle
Endpoint Assets
The Endpoint Assets Lifecycle represents the systematic stages that endpoint devices, such as laptops, desktops, and mobile devices, go through within an organization.
Infraon platform ensures that each stage is managed efficiently, from request to retirement, to maintain operational consistency and accountability.
Below is an overview of each stage, its significance, and key actions within the Infraon platform.
Lifecycle Stages
1. Request
The lifecycle begins when a user or department requests a new asset. This stage involves capturing detailed information about the required asset, such as type, quantity, and purpose.
Purpose: To initiate the procurement or allocation process.
Action in Infraon platform: Create a request ticket and record the details of the asset requirements.
Once the request is approved, the required asset is procured or leased. This stage ensures the requested assets are obtained and ready for quality checks.
Mandatory QA Check: Every asset undergoes a quality assurance (QA) process to verify its compliance with standards.
Failed QA: Assets are marked for return to the vendor.
Passed QA: Assets are marked as ready for the next stage.
Assets that pass the QA process are added to inventory. They are categorized based on type, location, and availability for better tracking and management.
Purpose: To ensure assets are available and ready for deployment.
Action in Infraon platform: Record and track the asset’s status in the IT asset module.
The asset is configured and prepared for use. This includes installing required software, updating licenses, and ensuring compliance with security protocols.
Purpose: To make the asset operational and ready for allocation.
The prepared asset is assigned to a specific user or department.
Actions in Infraon platform:
Update the asset’s status to "Allocated."
Assign ownership details in the system.
The assigned user evaluates the asset and decides whether to accept it.
If Accepted: The lifecycle continues to the Operation stage.
If Rejected: The asset is returned to In-stock for reassessment or reallocation.
The assigned user actively uses the asset. During this stage, audits are conducted periodically to verify the asset’s compliance, functionality, and condition.
Purpose: To monitor the asset's performance during its active use.
Actions in Infraon platform:
Conduct regular audits and record results.
Move non-compliant or faulty assets back to In-stock for resolution.
The asset is sent for maintenance if an issue arises during the operation stage. This includes resolving technical issues, replacing parts, or updating software.
Purpose: To restore the asset to a functional state.
Actions in Infraon platform:
Create a maintenance ticket.
Log actions taken during the repair process.
After maintenance, the asset returns to operational status with repairs completed and parts replaced.
Purpose: Ensures the asset is functional and ready for continued use until new issues arise or it reaches EOL.
When an asset reaches its end of life (EOL) or becomes irreparable, it is decommissioned. This involves securely wiping data and marking the asset for disposal.
Purpose: To ensure safe and compliant asset removal from active inventory.
The final stage of the lifecycle involves officially retiring the asset. It is removed from the active inventory, and disposal records are archived for reference.
Purpose: To close the lifecycle and maintain audit records.
The Network Devices Lifecycle tracks the stages that network devices, such as routers, switches, firewalls, and other networking hardware, go through within an organization.
Below is an overview of each stage, its significance, and key actions within Infraon platform.
The lifecycle begins when a user or department requests a new network device. This stage captures detailed information about the required asset, such as type, quantity, and purpose.
Purpose: To initiate the procurement or allocation process for the required network device.
Action on the Infraon platform: Create a request ticket and record the asset details.
Once the request is approved, the required network device is procured or leased. This stage ensures that the requested devices are obtained and ready for quality checks.
Mandatory QA Check: Every device undergoes a quality assurance (QA) process to verify its compliance with standards.
Failed QA: Devices are marked for return to the vendor.
Passed QA: Devices are marked as ready for the next stage.
Devices that pass the QA process are added to inventory and categorized based on type, location, and availability. This enables better tracking and management of devices.
Purpose: To ensure network devices are available and ready for deployment.
Action in Infraon platform: Record and track device status in the IT Asset module.
The asset is configured and prepared for integration into the network. This includes setting up hardware, performing initial network configurations, and ensuring the device is operational.
Purpose: To make the network device operational and ready for integration into the network.
The network device is integrated into the organization's network infrastructure. This includes connecting the device to other network components, applying configurations, and testing connectivity.
Purpose: To ensure the device is fully integrated and functional within the network.
Action in Infraon platform: Track integration progress and update device status.
The network device enters active use, supporting the network's operation. During this stage, regular audits are conducted to verify compliance, functionality, and security.
Purpose: To monitor the device’s performance and ensure it continues to meet network requirements.
Actions in Infraon platform:
Conduct regular audits and record results.
Move non-compliant or faulty devices back to In-stock for resolution.
If an issue arises during operation, the device is sent for maintenance. This includes resolving technical issues, replacing components, or updating firmware/software.
Purpose: To restore the device to a functional state and ensure network stability.
Actions in Infraon platform:
Create a maintenance ticket.
Log actions taken during the maintenance process.
After maintenance, the device is reinstalled and reconfigured as necessary. Any replacement parts are replaced, and the device is returned to active use.
Purpose: To ensure the device is fully functional and restored to its operational state.
Action in Infraon platform: Track reinstallation actions and update device status to "In-use."
When the network device reaches its end of life (EOL) or is no longer functioning as intended, it is decommissioned. This stage involves securely wiping data and removing the device from the network.
Purpose: To ensure safe and compliant device removal from the network.
Action in Infraon platform: Mark the device as decommissioned and initiate disposal procedures.
The final stage of the lifecycle involves officially retiring the device. It has been removed from the active inventory, and disposal records have been archived for future reference.
Purpose: To close the lifecycle and maintain proper audit records.
Action in Infraon platform: Remove the device from the active inventory and store all related documentation for compliance and reporting.
Tag Management
Tags are simplified identification keywords used to group items or users within Infraon. Tags can be applied to users, assets, articles, etc.
Tag Types
Tagging enables quick grouping of items/users. At this point in time, tags are added for:
Assets - Tag assets by brand, vendor, location technician, etc.
Users - Tag users by the team, skills, location, service catered, etc.
Expertise - Tag teams (team creation) with Hardware, Python, Django, or product expertise like washing machines, TV, etc.
Services - Tag services by team, location, category, classification, etc.
In a business where the end-users call from multiple locations for support on laptops and desktops, asset tags such as Laptop, Desktop, NY, AU, and IND can be used to assign these technicians tagged as Laptop, Desktop, NY, AU, and IND.
Go to Infraon Configuration -> General Setting ->Tag Management
Click the '"Add Tag button'
Once both the parameters are added, click 'Submit' to save the tag.
Repeat the process to add multiple tags. Tags can be edited or deleted using the respective icons.
Here are the 7 methods you can assign the asset tag.
Method 1: Single Asset
Go to Infraon Asset Card page -> Select the asset-> ( ⋮ ) More -> Edit
Enter the required details, add the tag in Asset Tag, and click Next.
Check the details in Asset Properties and click Submit.
Method 2: Bulk- Card/ Grid View
Go to the Infraon Asset Card page -> Select multiple Assets.
Click on Tag at the center of the top panel. Click on “Yes, Edit it.”
Name your Tag and click Submit.
Method 3: Bulk Edit
Go to the Infraon Asset Card page -> Actions -> Bulk Edit.
Select the Category.
Download the CSV file (Excel sheet) and enter the tag name on the sheet.
Upload the same edited CSV file.
Method 4: Tags can be assigned directly while adding an asset.
Go to the Infraon Asset Card page -> Add Item -> Single Asset
Add the required details to add the asset.
Select the Tag in the Asset Tag section.
Click Next -> Asset Properties -> Submit.
Method 5: Manually from CSV file (excel sheet)
Go to the Infraon Asset Card page -> Add Items -> Import from CSV
Select the required Category and download the CSV file.
Enter the Tag name in the sheet, use a semicolon (;) to add multiple tags at a time Eg: SHQ; BHQ
Upload the same edited CSV file.
Method 6: Asset details page
Go to the Infraon Asset Card page -> Select the Asset Name and redirect to the Details page.
Locate the Tags button in the center of the page, near the left panel.
Click to proceed to Add the required tags.
Method 7: Import from CSV
Go to Infraon configuration page -> IT Operations -> Discovery -> Automatic Discovery.
Click the "Import from CSV" button at the bottom center of the page.
Download the CSV file (Excel sheet) and enter the tag name on the sheet.
Upload the same edited CSV file.
Method 1: Bulk
Go to the Infraon Asset Card page -> Select the Asset Name and redirect to the Resource page.
Check the boxes next to the resources you need to tag.
Click on the Add Tag option, add the required tag, and click Submit.
Method 2:
Go to Infraon configuration page -> IT Operations -> Advance Resource Configuration.
Click Configure.
Navigate to the top right corner and click Actions -> Tag.
Add the required Tag.
Method 3: Advance configuration (CSV file)
Go to Infraon configuration page -> IT Operations -> Advance Resource Configuration.
Click Configure.
Click the "Export" button in the top right corner.
Clicking the button downloads the CSV file immediately (a pop-up may appear).
Method 1: Single
Go to Infraon Asset Card page -> Select the asset-> ( ⋮ ) More -> Edit
Enter the required details, add the tag in Owner Tag, and click Next.
Check the details in Asset Properties and click Submit.
Method 2: Bulk Edit
Go to the Infraon Asset Card page -> Actions -> Bulk Edit.
Select the Category.
Download the CSV file (excel sheet) and Enter the Tag name in the sheet.
Upload the same edited CSV file.
Method 3: Bulk- Card/ Grid View
Go to the Infraon Asset Card page -> Select multiple Assets.
Click on Tag at the center of the top panel. Click on “Yes, Edit it.”
Name your Tag and click Submit.
Method 4: Import from CSV
Go to Infraon configuration page -> IT Operations -> Discovery -> Automatic Discovery.
Click the "Import from CSV" button at the bottom center of the page.
Download the CSV file (Excel sheet) and enter the tag name on the sheet.
Upload the same edited CSV file.
My Profile
When you click the Profile icon (top-right corner of the platform), a dropdown menu appears. This menu provides quick access to personal settings, status control, log history, shortcuts, and session actions.
Profile Menu | Basic Details
Label
Description
Example / Notes
System Configuration
Customize your language and time zone settings on Infraon.
The module offers a centralized location for administrators to manage various user experiences and formatting settings for different modules within the Infraon Infinity platform.
Here's a breakdown of the key functionalities:
System Configuration | Basic Details
Label
Action
Description / Example
Enable Event Collection
Enable or disable the option.
Controls whether the agent collects events generated by the associated asset.
When enabled, relevant events are collected and synchronized with the system.
Device Uptime Tracking
Enable or disable the option.
Enables tracking of the device's uptime information through the agent.
Enable Software Metering
Enable or disable the option.
Enables software metering for the associated assets, allowing software usage information to be collected through the agent.
Enable Software Metering Rule Sync
Enable or disable the option.
Enables synchronization of software metering rules with the agent so that the configured metering rules can be applied to the associated assets.
Displays the application associated with the vulnerability.
Example: Google Chrome
Package
View
Displays the software package affected by the vulnerability.
Example: openssl
Version
View
Displays the version of the affected package.
Example: 1.1.1
Severity
View
Displays the severity level of the vulnerability.
Example: Critical, High, Medium, or Low
CVSS Score
View
Displays the Common Vulnerability Scoring System (CVSS) score assigned to the vulnerability.
Example: 8.1
Fix State
View
Displays the current fix status of the vulnerability.
Example: Fixed / Unfixed
Scan Time
View
Displays the date and time when the vulnerability was identified during the scan.
Actions
Perform action
Provides actions available for the selected vulnerability, such as viewing its detailed information.
CVS Breakdown
Affected Software
View
Displays the applications and software packages affected by the vulnerability.
Endpoints
View
Displays the number of endpoints affected by the vulnerability.
CVSS Breakdown
View
Displays the CVSS vector and individual metrics used to calculate the vulnerability's CVSS score.
Displays the potential impact on the confidentiality of information.
Example: High
Integrity
View
Displays the potential impact on the integrity of information.
Example: High
Availability
View
Displays the potential impact on the availability of the affected system or resource.
Example: High
Affected Software
Application Name
View
Displays the name of the application affected by the vulnerability.
Example: Antigravity IDE (User)
Hostname
View
Displays the hostname of the endpoint where the affected application is identified.
Example: 317-Ayush-EIMS
Package
View
Displays the software package affected by the vulnerability.
Example: Scintilla
Version
View
Displays the version of the affected package.
Example: 5.5.4
CVE Lifecycle
Published
View
Displays the date when the CVE was originally published.
Example: Sep 14, 2019
NVD Updated
View
Displays the date when the CVE information was last updated in the NVD.
Patch Released
View
Displays whether a patch has been released for the vulnerability.
Example: Pending
Remediated
View
Displays whether the vulnerability has been remediated.
Example: Pending
Description
View
Displays the description of the vulnerability.
Example: SciLexer.dll in Scintilla in Notepad++ (x64) before 7.7 allows remote code execution or denial of service via Unicode characters in a crafted .ml file.
Reference(s)
View
Displays the available reference links associated with the CVE.
Example: Packet Storm, GitHub, Notepad++ download page, and Scintilla history.
Affected Software / Affected Product
Product
View
Displays the affected product.
Example: notepad++
Vendor
View
Displays the vendor associated with the affected product.
Example: notepad-plus-plus
Version Range
View
Displays the affected version range.
Example: * – 7.7
Platform
View
Displays the platform associated with the affected product, when available.
Product
View
Displays additional affected products or components.
Example: scintilla
Endpoint
Hostname
View
Displays the hostname of an endpoint associated with the affected software.
Example: 317-Ayush-EIMS
IP Address
View
Displays the IP address associated with the affected endpoint.
Example: 172.31.0.1, 10.0.7.240
Application
View
Displays the application identified on the affected endpoint.
Example: TortoiseGit 2.17.0.2 (64 bit)
Hostname
View
Displays the hostname of the affected endpoint.
Example: 317-Ayush-EIMS
IP Address
View
Displays the IP address associated with the endpoint.
Example: 172.31.0.1, 10.0.7.240
Application
View
Displays the application associated with the vulnerability on the endpoint.
Example: Antigravity IDE (User)
Click Next -> Import -> Proceed with Valid Records.
Click Next -> Import -> Proceed with Valid Records.
Click Next -> Import -> Proceed with Valid Records.
Enter the Tag name in the sheet.
Now navigate to the Infraon configuration page -> IT Operations -> Advance Resource Configuration.
On the top right corner, click Bulk Resource Update.
Upload the same edited CSV file.
Click Next -> Import -> Proceed with Valid Records.
Click Next -> Import -> Proceed with Valid Records.
Click Next -> Import -> Proceed with Valid Records.
Label
Action
Description/Example
Tag Name*
Give a name to the tag
Laptops, Desktops, IT, HR, India, NY, etc.
Type*
Select tag type using the drop-down menu.
How to use a tag effectively?
Instructions to 'Add a Tag'
Note: Assigned tags cannot be deleted.
Instructions to ‘Assign a Tag’
Asset Tag
Resource Tag
Owner/ User Tag
Refer 'Tag Types' section above for detailed information
Displays the logged-in user’s basic profile details.
Shikar – shikar.srivastav@infraon.io
Clock In / Clock Out
Used to log working hours for attendance tracking. Switching to Clock Out ends the current active session.
Shows the timestamp of the last action.
View Logs
Opens attendance/activity logs to review login history and time entries.
View daily login/logout logs.
Status
Shows the current availability status. Users can switch between statuses such as Active, Away, and Busy, depending on configuration.
Current Status: Active
Account Settings
Navigates to the Account Settings page, where users can update profile details, security settings, preferences, and attendance config.
Click here to know more.
Keyboard Shortcuts
Opens a pop-up showing available keyboard shortcuts for quick navigation.
User: g+u, Requester: g+r, etc.
Logout
Logs the user out of the platform.
Redirects to the login page.
Privacy Policy / Terms of Service
Links to compliance and platform usage policies.
External redirect.
This page lets users manage their personal profile settings, including basic details, password, preferences, signature, attendance options, approvals, and security settings like 2FA. All changes apply only to the logged-in user.
Users can update basic profile details, including full name, gender, contact number, time zone, and email address. This section also supports changing the profile picture and enabling Two-Factor Authentication (2FA) for secure login.
General | Account Settings
Label
Action
Description / Example
Profile Picture
Upload / Change
Upload or modify your avatar displayed across the platform.
Full Name
View / Edit
Users can update their login password by entering their current password and setting a new one. This is used to maintain account security and should be updated periodically or when credentials are compromised.
Change Password | Account Settings
Label
Action
Description / Example
Current Password*
Enter existing password
Required to verify identity before applying changes
New Password*
Enter new password
Adjust personal viewing and language settings. Users can set how many records appear per page, select their preferred interface language, and adjust the font size using the slider.
These preferences apply only to the logged-in user and do not affect global system settings.
Use this section to create and manage email signatures that automatically append to communications sent from the platform. Multiple signatures can be added and stored for different use cases (e.g., support, escalation, internal).
Add Signature | Account Settings
Label
Action
Description / Example
New Signature
Click
Opens a pop-up window to create a new signature.
Title
Enter text
This section stores the user's professional details and organizational mapping. It helps in defining the user’s role, department, experience, skills, business entity, and notification contact details within the platform.
Field Details| Account Details
Label
Action
Description / Example
Designation
Enter text
Stores the job title used internally.
Example: Frontdesk Engineer
Organization Role
After entering details, click Submit to save changes.
Updated details will reflect across dashboards, workflows, and reporting modules.
This section displays your attendance logs for selected date ranges. Users can view clock-in/clock-out times, total working hours, remarks, and reasons for leave. You can filter records, review daily entries, and verify time logs based on system-recorded data.
Label
Action
Description / Example
Date
View
Shows the specific date of attendance entry.
Example: 19 Wed, Nov 2025
In
The Pending Approvals section displays requests that require the user’s action—typically approval or rejection of workflow items such as attendance logs, requests, or task submissions.
This page only shows items assigned to the logged-in user as an approver. If no items require action, the page remains empty.
This page displays the attendance records of users who report to you. It includes login/logout times, total and effective working hours, remarks (Worked/Absent), and location-based fields such as latitude, longitude, and distance from the base. You can search by username, apply date-range filters, and review daily logs to monitor team activity and ensure compliance.
User Info (Name & Email)
Account Settings
General
Change Password
User Preferences
Signature
Information
Attendance
Pending Approvals
Sub-ordinates Attendance
Language
Select the required language from the drop-down.
Defines the language used in the system interface.
Example: Select English to display the interface in English.
Country
Select the required country from the drop-down.
Defines the country configured for the system.
Example: Select Albania as the country.
Timezone
Select the required time zone from the drop-down.
Defines the time zone used by the system for displaying and processing date and time values.
Example: Select (GMT-11:00) Pacific/Midway [SST].
Idle Session Timeout
Enter the timeout duration in minutes.
Defines how long a user session can remain inactive before it times out.
Example: If set to 15, the session times out after 15 minutes of inactivity.
Account Unlock Wait (in Mins)
Enter the waiting period in minutes.
Defines the time a user must wait before attempting to unlock or access an account after it has been locked.
Example: If set to 15, the user must wait 15 minutes.
Page reload interval (Sec)
Enter the interval in seconds.
Defines how frequently the page automatically reloads or refreshes.
Example: If set to 23, the page reloads every 23 seconds.
Location
Select the required location from the drop-down.
Defines the location associated with the system configuration.
Example: Select Aaronfort Robert Throughway as the configured location.
Currency
Select the required currency from the drop-down.
Defines the default currency used for financial information across supported modules.
Example: If INR is selected, financial amounts are displayed using the INR currency format.
Disable SSP 2FA
Enable or disable the toggle.
Controls whether Two-Factor Authentication (2FA) is disabled for users accessing the Self-Service Portal (SSP).
When enabled, SSP 2FA is disabled. When disabled, users can use SSP 2FA where applicable.
This powerful feature allows for customization of how specific data is formatted within various Infraon modules. For example, admins can define prefixes for modules like Assets, etc. These prefixes will be displayed instead of the actual names within the portal, potentially improving organization and clarity for users.
Additionally, formatting options for these modules can be configured, providing granular control over how information is presented.
The following section breaks down the details:
Asset
Prefix
Knowledge Base
Prefix
Once the changes are made to satisfaction, click “Save” to proceed.
Two-Factor Authentication (2FA) adds an extra layer of security to requester accounts in the Self-Service Portal (SSP) by requiring a time-based one-time passcode (TOTP) from an authenticator app.
The availability of the 2FA option in the requester’s Account Settings depends on the organization-level configuration set by the administrator.
Behavior Based on Org Settings
Org Setting
Result in SSP
Example
Disable Requester 2FA = Enabled
The 2FA toggle in the requester’s account settings is disabled. Requesters cannot activate two-factor authentication (2FA) on their accounts.
Admin has disabled requester 2FA for the organization → requesters see the toggle as disabled.
Disable Requester 2FA = Disabled
The 2FA toggle in the requester’s account settings is enabled, allowing requesters to set up and use two-factor authentication (2FA).
The 2FA toggle is dynamically enabled/disabled based on org-level configuration.
Admins maintain centralized control to enforce or relax requester 2FA usage.
The API User & Token configuration allows administrators to manage the validity period of API User tokens and control encryption for API responses at the organization level.
API User & Token | Configuration
Label
Action
Description / Example
API User Token Expiry (Years)
Enter the required number of years.
Defines the validity period for newly generated API User tokens. The allowed range is 1 to 10 years. If no organization-specific value is configured, the default validity period is 5 years.
Example: Enter 2 to set newly generated API User tokens to expire after 2 years.
Encrypt API Response
Enable or disable the toggle.
1
Open System Configuration
Go to Infraon Platform > System Configuration.
2
Enter the expiry period
In the API User & Token section, enter the required value in API User Token Expiry (Years).
3
Verify the value
Ensure that the value is between 1 and 10.
4
Save the configuration
Click Save.
1
Open System Configuration
Go to Infraon Platform > System Configuration.
2
Enable response encryption
In the API User & Token section, enable Encrypt API Response.
3
Generate an encryption key
Generate a Response Encryption Key if one does not already exist.
4
Save the configuration
Click Save.
When response encryption is enabled, the setting takes effect on the next API call. Token regeneration is not required.
The Response Encryption Key is organization-specific and is used for API Users whose API response encryption is enabled.
When no key exists, the button displays Generate Key.
After you generate a key, the button changes to Rotate Now.
Key generation and rotation are available to the Management Admin.
Rotating the key does not require regenerating the API User token.
New encrypted API responses use the latest key.
Previously generated encrypted responses remain decryptable using their respective key version.
The organization-level Encrypt API Response setting can be overridden for individual API Users. The available response encryption behavior is:
Response Encryption
Description
Always encrypt
Encrypts API responses for the API User regardless of the organization-level setting.
Never encrypt
Returns API responses in plain JSON regardless of the organization-level setting.
Inherit organization default
Important Notes
API User Token Expiry (Years) applies to newly generated API User tokens.
Existing tokens are not affected when you change the token expiry configuration.
Encrypt API Response applies only to API User API traffic. Regular user sessions and standard portal traffic are not affected.
If encryption is required but no encryption key is available, the system does not return the API response as unencrypted business data.
Response encryption settings take effect without regenerating the API User token.
Response encryption keys are scoped to the organization.
Module Formatting
Disable SSP 2FA
API User & Token
Changes to API User Token Expiry (Years) apply to newly generated tokens. Existing API User tokens continue to use their original expiry date.
Configure API User Token Expiry
If you enter an invalid value, the system displays the message: Allowed range is between 1 and 10 years.
Configure API Response Encryption
If response encryption is required but you have not generated a Response Encryption Key, the API request fails safely and does not return the requested business data in plain text.
Generate or Rotate the Response Encryption Key
Disabling Encrypt API Response does not affect API User tokens. It only changes how subsequent API responses are returned.
API User Response Encryption
Changes to response encryption take effect on the next API call and do not require token regeneration.
Refines the list based on conditions.
Fields: Software
Conditions: in, not in, equal to, not equal to, contains, not contains
Sync
Click to sync
Updates and pushes the latest Software Metering rules to all agents. Ensures newly added or updated rules are applied to devices and tracking starts accordingly.
+ Create Rule
Click to create
Opens the Create Rule configuration to define a new Software Metering rule with selected applications.
Column Details
Rule Name
View / Sort
Displays the name of the Software Metering rule. Helps identify the tracking configuration.
Application List
View
Shows the list of applications included in the rule. Multiple applications can be grouped under a single rule.
Comment
View
Displays additional notes or descriptions provided during rule creation.
Actions
Edit
Click to modify
Allows you to update the selected rule, such as modifying applications or comments.
Delete
Click to remove
Deletes the selected Software Metering rule from the system.
Select one or more applications to be tracked under this rule. The list is populated from agent-discovered software.
Example: Microsoft Edge
Comment
Enter value
Add optional notes describing the purpose of the rule.
Example: Monitor browser usage for analysis
Applicable For
Select from the dropdown
Defines the scope of the rule.
Options:
All – Applies to all devices with agents
Selected Device – Applies only to chosen devices
2. Acquisition
Assets cannot move directly from Acquisition to In-stock without passing the QA check.
3. In-stock
4. Installation
5. Allocation
6. User Acceptance
7. Operation
8. Maintenance
9. In-Used
10. Decommission
11. Retire
Network Assets
Lifecycle Stages
1. Request
2. Acquisition
Devices cannot move directly from Acquisition to In-stock without passing the QA check.
3. In-stock
4. Implementation
5. Integration
6. Operation / In-Use
7. Maintenance
8. Re-Install
9. Decommission
10. Retire
IT Asset Audit Record
The IT Asset Audit Record is used to conduct physical verification of IT and Fixed Assets to validate asset condition, location, and compliance. It maintains an audit history for each asset for each audit execution.
Audits can be created as random or scheduled and configured as internal or external. Each audit is performed using predefined templates (checklists) that define the verification criteria for auditors. The module tracks audit progress, completion status, and audit results across selected asset categories.
What You See on the Screen
The IT Asset Audit Record page displays all created audit records, including their current status, progress, and assigned auditors. Users can search, filter, schedule, and manage audits, and create and apply audit templates.
Audit Records | Basic Details
Label
Action
Description / Example
Templates define the checklist used during an IT Asset Audit. They specify what an auditor must verify for each asset, including condition, serial number, location, compliance details, and custom verification points.
Templates ensure audits are performed in a structured and consistent manner and can be reused across multiple audit records. Assigning a template is mandatory to execute an audit.
To create a new template:
Navigate to IT Asset Audit Record.
From the top panel, select Template.
Click Add Template to configure a new checklist.
Templates are built by selecting relevant asset attributes and adding custom input fields that auditors will complete during the audit.
Add Template | Basic Details
Label
Action
Description / Example
After selecting the required asset columns, add verification fields to build the checklist. These fields define what the auditor must review or capture during the audit.
Available field types include:
Email – Capture an email address for confirmation or contact
Text – Record short text inputs such as serial numbers or remarks
Number – Capture numeric values like counts or measurements
Dropdown – Provide predefined options for selection
Once all required columns and checklist fields are configured:
Click Submit to save the template.
The template becomes available for selection while creating or editing an IT Asset Audit Record.
Saved templates can be reused across multiple audits to maintain uniform verification standards.
How does it work
Multiple pre-configured reports are available on Infraon. These can be customized, and new custom reports can also be added.
What you see on the screen
The Report Grid page displays all created reports, including their category, description, scheduling details, and available actions. Users can search, filter, create, schedule, and export reports directly from this page.
It also provides visibility into scheduled reports and allows quick operations without opening individual reports.
Report Grid | Basic Details
Label
Action
Description/ Example
Column Details | Report Grid
Label
Action
Description/ Example
Admins can enable hiding the requester’s info in reports to comply with data privacy regulations.
Admin allows requester 2FA → requesters can enable 2FA for their accounts.
Controls whether API responses for API Users are returned in encrypted format.
When enabled, API responses for API Users with encryption enabled are encrypted before being returned.
Generate Key / Rotate Now
Click the button to generate or rotate the response encryption key.
Allows a Management Admin to generate the organization's response encryption key or replace the existing key.
The button displays Generate Key when no key exists and Rotate Now after a key has been generated.
Uses the current Encrypt API Response setting configured for the organization.
Select from the drop-down
Used to manage audit templates (checklists).
Options include:
View Template (review existing checklists)
Add Template (create a new checklist for audits).
to view the steps to add templates.
Add New Audit
Click to create
Create a new audit record by defining audit details, category, audit type (internal/external), auditors, schedule, and assigning a template.
Audit ID
Click ID
Unique system-generated identifier (for example, AUD0106) used to track the audit record.
Audit Title
View text
Displays the audit name, such as "Quarterly Laptop Audit."
Contact Person
View avatar/name
Primary point of contact responsible for the audit.
Status
View state
Indicates the audit lifecycle state:
Open-New
In progress- Ongoing
on hold- pending
Close -Audit Done
Audit Type
View value
Specifies whether the audit is performed for IT Assets or Fixed Assets.
Category
View value
Shows the asset categories included in the audit, for example, Laptop, Desktop, Workstation, and Windows Server.
Audit Status
View progress
Displays completion progress such as 0 of 10 Completed or 10 of 10 Completed, with a visual progress indicator.
Creation Time
View timestamp
Shows when the audit record was created in the system.
Internal Auditors
View icons/count
Displays the assigned internal auditors responsible for performing the audit.
External Auditors
View icons/count
Displays assigned external auditors if the audit is marked as external.
Schedule Details
View schedule
Shows whether the audit is scheduled or run immediately, along with planned execution details.
Audit Completion Time
View timestamp
Displays the date and time when the audit was completed.
Actions Icons
Edit
Click icon
Modify audit details such as title, auditors, schedule, or assigned template before completion.
Audit
Click to perform
Launch the audit execution screen where auditors perform checks based on the assigned template.
Permanently remove the audit record from the system.
Specific Asset Columns
Select from the drop-down
Select asset-type–specific attributes for verification.
Option Includes: Status, Installation Date, State Change Reason, etc.
Text Area – Capture detailed comments or observations
Check Box – Confirm yes/no or compliance-based checks
Date – Record a specific date
Date and Time – Record a precise date and time of verification
Search
Type keywords
Search audit records by Audit ID or Audit Title. Minimum three characters are required to trigger a search.
Filter
Select criteria
Filter audits using fields such as Audit ID, Audit Name, Contact Person, State, Status, Audit Type, Category, Auditor, and Creation Time.
Conditions include in, not in, equal to, not equal to, contains, and not contains.
Select Date Range
Choose a time window
Filter audit records based on creation time.
Examples: Current Hour, Last 60 mins, Today, Last 7 Days, etc.
Template Name
Enter a value
Provide a meaningful name to identify the checklist.
Example: Laptop Physical Verification
Common Asset Columns
Select from the drop-down
Templates
Add Template
Checklist Fields
Template
Select standard asset attributes that apply across asset types.
Option Includes: Criticality, Service Status, Business Function, etc.
Dropdown
Used to generate on-demand (one-time) reports without saving or scheduling them. These reports are executed instantly based on selected parameters and are not stored in the report grid unless explicitly saved.
Available Report:
MRTG Report: Generates real-time graphical reports for network traffic and bandwidth utilization using MRTG data.
Example: View a device's bandwidth usage over time.
Statistics Report: Provides aggregated statistical data based on selected metrics (e.g., count, average, min, max).
Example: Average CPU usage across devices for the last 7 days.
Forecast Report: Predicts future trends based on historical data using predefined thresholds and patterns.
Example: Forecast storage utilization for the next 30 days.
Prediction Report: Uses analytical models to estimate future outcomes or behaviors based on existing data.
Add Report
Button
Click to create a new report with configuration, filters, and scheduling options.
Displays the report category (e.g., Asset Report, Audit Report).
Description
View only
Displays a brief summary of what the report contains or represents.
Example: “Asset report for update changes like hardware/software details.”
Schedule Description
View only
Displays scheduling details if configured.
Example: “Scheduled for every Sunday at 11:30 (Asia/Kolkata)”. If no schedule is set, this field remains empty or shows “-”.
Actions
Edit
Click
Opens the report configuration page to modify columns, filters, timescale, sorting, and other settings.
Clone
Click
Creates a duplicate of the selected report with the same configuration. Users can modify and save it as a new report.
Send Now
Click
Generates and sends the report immediately via configured channels (e.g., Email). Does not affect existing schedules.
Schedule
Click
Opens the schedule configuration window to define report frequency (Once, Daily, Weekly, Monthly), time, and delivery method.
Delete
Click
Permanently deletes the selected report from the system. This action cannot be undone.
Export as CSV
Click
Downloads the report as a CSV file for external analysis or sharing.
Export as PDF
Click
Downloads the report in PDF format with a structured layout and optional graphical representation.
Export as XLSX
Click
Downloads the report as an Excel (XLSX) file for advanced data manipulation.
Bulk Actions
Delete
Select + Click
Select multiple reports using checkboxes and delete them in bulk. Useful for removing unused or duplicate reports.
Email
Enabling this toggle will obfuscate the requester’s email ID in reports to comply with data privacy regulations.
Use the designated toggle switch to restore the requester's email display in the report interface for authorization.
Search
Input field
Click to search for a report from the available reports. Minimum 3 characters required.
Filter
Click to apply filters
Filter reports based on fields such as Name, Category, Description, and Schedule.Supported conditions: in, not in, equal to, not equal to, contains, and not contains.
Show Scheduled Reports
Toggle
Enable the display of only reports that have an active schedule configured. The disabled state shows all reports.
Name
Click to open the report
Displays the report name. Clicking opens the report configuration page, where users can modify settings or preview the report.
Example: Clicking the Asset Allocation Report opens its configuration.
Category
Label
Mask
Unmask
Name
Enabling this toggle will obfuscate the requester’s name in reports to comply with data privacy regulations.
Use the designated toggle switch to restore the requester's name display in the report interface for authorization.
Contact
Enabling this toggle will obfuscate the requester’s contact information in reports to comply with data privacy regulations.
Data Privacy
Mask/ Unmask Requester Info
Adhoc Report
View only
Use the designated toggle switch to restore the requester's contact information in the report interface for authorization.
Update the display name associated with your account.
Example: Shikar.
Email
View Only
Shows the registered email address used for login and notifications.
Gender
Select Option
Choose the gender preference from Male, Female, or Other.
Phone Number
Add / Edit
Enter your primary mobile number with the country code.Example: +974 4412 3456.
Timezone
Select Dropdown
Set your local timezone for accurate timestamps.Example: (GMT+05:30) Asia/Kolkata [IST].
Landline
Add / Edit
Enter the official landline contact number (optional).
Contact Extension
Add / Edit
Add an internal extension number if applicable (optional).
Two-Factor Authentication (2FA)
Enable / Disable
Enable enhanced security using TOTP via an authenticator app.
Submit
Save Changes
Applies and saves profile updates.
Define a new secure password for login
Submit
Save changes
Applies the password update after validation
Name of the signature template.Example: "Support Team Signature"
Editor (Text area)
Type / Format
Add and format signature content. Supports text styling, hyperlinks, and images.Example: Name, role, contact details, company logo.
Apply styling and insert media for professional formatting.
Save / Close
Save or Exit
Save changes or close the editor without saving.
Enter text
Defines the functional role assigned within the system hierarchy.
Example: Service Engineer
Department
Select from the dropdown
Associates the user with a specific department. Used for routing & reporting.
Example: Support / Operations / Engineering
Experience Months
Enter value (number)
Total months of professional experience. Helpful for skill-mapping.
Example: 24
Experience Years
Enter value (number)
Total years of professional experience.
Example: 3
Skills
Select from the dropdown
Define skillsets for resource assignment & workload mapping.
Example: Networking / Troubleshooting / Linux
Notify Email
Enter email
Email address used for task/ticket notifications.
Example: john.doe@infraon.com
Notify Phone No(s)
Enter phone
Phone number used for SMS/voice alerts.
Example: +91 987XXXX210
Business Entity
Enter or select
Indicates the business unit to which the user belongs.
Example: Global Support
Business Segment
Enter text
Categorizes the user under a business division.
Example: IT Operations
Partner Name
Enter text
Used when the user belongs to a partner organization.
Example: TechSolutions Pvt Ltd
Subsidiary
Enter or select
Maps the user to a subsidiary entity in multi-org setups.
Example: Infraon India Pvt Ltd
View
System-recorded clock-in time.
Example: 03:52 PM
Out
View
System-recorded clock-out time.Example: 06:41 PM
Effective Hours
View
Actual productive time calculated from first clock-in to last clock-out after break deductions.
Example: 1 hr, 39 min
Total Hours
View
Gross working hours, including all logged sessions.
Example: 2 hr, 48 min
Remarks
View
Work status based on attendance.
Example: Worked / Absent
Latitude / Longitude
View
Shows captured geo-coordinates (if location tracking is enabled).
Login Type
View
Indicates login source. Example: Remote / Base / Mobile
Distance from Base
View
Distance from the assigned base location at login time.
Approval Status
View
Shows if attendance adjustments are pending approval.
Example: Approved / Pending
Reason
View
Shows remarks for absence or manual edits. Example: No Reason Provided
Filter (Last 30 Days)
Select Filter
Filters attendance records based on date range.
Example: Today / This Month / Custom Range
Dedup Rules
The Dedup Rules page allows administrators to define the conditions used to identify duplicate asset records and determine how those records should be handled.
What you see on the screen
The rule list displays information such as:
Label
Action
Description / Example
Order
Click New Dedup Rule to open the Rule Builder. Users can configure condition groups, similarity thresholds, perform a dry run, and publish the rule.
Label
Action
Description / Example
The Two Records Are Duplicates When section allows users to define the conditions used to determine whether two asset records should be considered duplicates. Users can add one or more conditions and combine them using AND or OR operators.
AND requires all specified conditions to match before two records are identified as duplicates.
OR requires at least one of the specified conditions to match.
Users can also organize conditions into groups to create more flexible duplicate-matching rules.
Example
Consider two asset records with the following details:
Asset 1: Dell Laptop, Serial Number SN12345, MAC Address AA:BB:CC
Asset 2: Dell Laptop, Serial Number SN12345, MAC Address XX:YY:ZZ
If the rule is configured as:
both the Serial Number and Asset Name must match for the records to be identified as duplicates.
If the rule is configured as:
the records can be identified as duplicates when either the Serial Number or MAC Address matches. This is useful when one identifier may not be available for every asset.
Label
Action
Description / Example
Label
Action
Description / Example
IMACD
IMACD stands for Install, Move, Add, Change, and Dispose, which provides a structured way to manage organizational changes smoothly. It combines system installation, coherent movement, planned inclusions, adaptation, and organized disposal, forming a strong guide for transformation.
It’s a well-organized path for handling any shift, from setting up new systems to retiring outdated resources. This approach ensures smoother transitions, minimizes disruptions, and streamlines changes within the ever-evolving business landscape.
From setting up new systems to responsibly recycling old ones, the IMACD process breaks down into five distinct stages, each tackling a core element of IT management and resource handling:
Installation
The Installation phase focuses on deploying and configuring new IT assets within the target infrastructure. This encompasses provisioning compute nodes, client devices, applications, and network fabric. Meticulous installation guarantees the functional integrity and optimal performance of these components.
It is the foundational layer for a highly available and resilient IT ecosystem, where adherence to best practices ensures optimal system operation and efficient resource utilization.
Move
The IMACD Move phase addresses the physical and logical relocation of IT resources. This encompasses the migration of hardware assets to a new site (e.g., office relocation or reconfiguration) and the transfer of data and software between servers or cloud environments.
The "Add" phase of IMACD focuses on the planned integrations of new IT components into the existing infrastructure. This involves the strategic onboarding and configuration of various elements, including:
Software applications: Deploy and integrate new software tools with existing systems, ensuring compatibility and data interoperability.
Hardware upgrades: Incorporation of enhanced hardware components to augment performance, functionality, or capacity, adhering to technical specifications and compatibility standards.
Network expansions: Extension of the network infrastructure to accommodate additional devices, locations, or increased bandwidth requirements, following network design principles and security best practices.
The configuration management workflow within IT operations hinges on controlled deployments to modify or update hardware or software configurations. This Change Management phase addresses evolving business needs and issues through controlled modifications. Examples include:
The Disposal stage of the IMACD encompasses the planned and secure retirement or removal of hardware and software assets at the end of their useful life. This stage is crucial for asset optimization by effectively reallocating resources and minimizing security vulnerabilities inherent to outdated systems. Additionally, it ensures compliant data disposal and prioritizes the secure handling of sensitive information.
Clicking the IMACD process will display the following information:
Asset Categories/Sub-Categories
See it in action!
Defining the asset category and sub-category is the first step in adding the asset. Categories can also be called Parent categories. It is recommended that an asset category be added before an asset. The process of adding a category and a sub-category is the same.
Hovering the mouse over the category:
Business Hours
The daily working hours of teams/departments within an organization are called business hours. This, in turn, aids in assigning work based on users' working hours and setting and meeting SLAs.
When creating a profile, you could choose between specific working days/hours and 24/7 availability.
Use the Exclude Hours option to add a break in the business hours. This can be the weekend, an official lunch hour/break time, or a change in the Technician's shift. SLAs are adjusted as needed.
To view the complete list of holidays applicable to your region, add 'Holiday' or click on import holidays. 'Exclude hours and Holidays' are excluded.
Go to Infraon Configuration -> General Settings -> Business Hours.
Asset Scope
Select All Assets or Filtered Assets
Defines the assets to which the deduplication rule applies. All Assets evaluates the complete asset inventory, while Filtered Assets evaluates only the assets matching the selected criteria.
Asset Scope
Select Filtered Assets
Applies the deduplication rule only to assets that match the defined filter conditions.
Field
Select an asset field
Specifies the asset field used to filter the records, such as Asset Name, Asset Type, or Manufacturer.
Contains
Enter the matching value
Defines the text or value that the selected field must contain.
Value
Enter a value
Specifies the value used with the selected field and condition to determine which assets are included in the deduplication scope.
OR
Combine conditions using OR
Requires at least one condition to match. Example: Serial Number matches OR MAC Address matches.
Condition Group
Add or group conditions
Allows users to organize multiple conditions into groups for creating more precise duplicate rules.
Field
Select a field
Specifies the asset field to compare, such as Serial Number, Asset Name, IP Address, or MAC Address.
Condition
Select a matching condition
Defines how the selected field is evaluated between the records.
Value
Specify the comparison value
Defines the value used by the condition when evaluating the duplicate criteria.
One-click Merge Threshold
Set the merge threshold
Defines the confidence level above which a duplicate cluster can be merged automatically without manual review, provided there are no conflicts. For example, 0.95 automatically merges qualifying matches.
Cancel
Select Cancel
Discards the changes made while creating or editing the deduplication rule and returns without publishing the rule.
Publish Ruleset
Select Publish Ruleset
Saves and activates the configured deduplication ruleset so that it can be used to identify and process duplicate asset records.
View
Displays the order in which the deduplication rule is evaluated.
Rule Name
View/Edit
Displays the name assigned to the deduplication rule.
Match Condition
View
Displays the conditions used to identify matching asset records.
Survivor Strategy
View
Displays the strategy used to determine which record survives the merge.
Clusters
View
Displays the clusters associated with the rule.
Precision
View
Displays the rule precision using a progress bar.
Status
Toggle
Enables or disables the rule directly using the toggle switch.
Updated
View
Displays when the rule was last updated.
Actions
Click
Allows users to edit or delete the rule.
Rule Name
Enter a rule name
Defines a unique name for the deduplication rule to identify its purpose.
Schedule
Select from Manual, Hourly, Daily, and Weekly
Two Records Are Duplicates When
Define duplicate conditions
Specifies the criteria used to determine when two asset records are considered duplicates.
AND
Combine conditions using AND
Dry Run — No Writes
Enable Dry Run
Evaluates the current asset snapshot and identifies potential duplicate clusters without making any changes to the asset records.
Confidence Threshold
Set the confidence percentage
Create Dedup Rule
Define Duplicate Conditions
Serial Number → Equals → AND → Asset Name → Equals
Serial Number → Equals → OR → MAC Address → Equals
Deduplication Rule Controls
Determines when the deduplication rule runs. Manual Only requires the user to trigger the rule manually.
Requires all conditions to match. Example: Serial Number matches AND Asset Name matches.
Defines the confidence level used to classify potential duplicate matches. For example, matches above 0.85 are considered confident, while lower-confidence matches are flagged as Ambiguous.
Click to view in a tabular format.
Panel View
Click to view the details in the form of a Summary Card.
New Process
Click to add an IMACD process
IMACD
Displays the IMACD ID associated.
Process name
Indicates the process name associated with the IMACD process.
Assignee
Displays the name of the assignee assigned to the respective process.
Process Type
Denotes the type of process instance associated with a particular IMACD.
Status
Displays the current status of the process.
Priority
Indicates the priority of the process; the priority can be low, medium, high, or critical.
Asset Count
Displays the asset count involved in the process.
Actions
Delete
Click to delete the process.
Description
Displays a brief description of the IMACD process.
Status
Indicates the current state of the process. (Ex. New or Waiting for Approval)
Process Type
Shows the type of IMACD process. (Move, Add, etc.)
Priority
Low, Medium, High, and Critical.
Workflow
Indicates the name for the Visual flowchart of processes.
Shipment Details
Shipping Address
The designated address at which the package is to be retrieved. (Example Branch Office)
Destination Address
The physical address where the physical package should be delivered. (Example Head Office)
Asset Details
Asset Type
Defined the type of asset whether to be IT or fixed asset.
Asset Category
Category is the first division of assets within the selected asset type. For example, within IT assets, there can be categories like laptops, desktops, etc.
Asset Details
Displays the name of the asset selected.
Comment
Any comment associated with the asset.
Left Panel
Assignee
Displays the name of the assignee assigned to the respective process.
Gate Pass
Shows the selected gate pass processed by the admin.
Communication
All
Displays all the communication that happened in between the process.
Email
Displays the email communication.
SMS
Displays the SMS communication.
Comment
Displays the comment made during the process or shipment of the asset.
Mail
Click to add or send a mail during the process.
Add Notes
Click to add notes for better communication.
Attachments
Default Page
Displays all the attachments (documents) aligned to the process.
Add
Click to add new attachments.
Recent Activities
Default Page
Provides a real-time overview of all activities, both in progress and completed, within the corresponding IMACD stage.
Search
Click to search for the required communication within the process.
Label
Action/ Description
Search
Search for the required IMACD process.
Filter
Filter can be added based on the field (Name, Status, State, Creation Time, Assignee, IMACD ID, Priority, and Process Type) and select the condition from the drop-down box below.
Label
Description/ Example
IMACD Details
Basic Details
Add
Change
Decommissioning
What you see on the screen
About IMACD process:
IMACD Details| Fields
Grid View
Example: Predict potential device failures based on past alerts.
Statistics Pattern Report: Identifies recurring patterns and trends in statistical data over time.
Example: Detect recurring spikes in network usage during specific hours.
Edit
Click to make changes to the category.
Delete
Click to delete the category.
Before adding an asset category/sub-category
The ‘Add Category’ field tab is where you can define or configure asset properties. Asset properties may include basic details like make, model, size, dimensions, etc., and critical information like EOL, EOS, end of support, etc. Some properties are mandatory for all asset categories.
The properties within Infraon are categorized into sections. Some sections are optional, whereas some are mandatory. The optional sections are available for selection based on the type or category of assets.
The sections are listed below the title ‘Available Section’. Once selected, they are added to the ‘Selected Section’ part and are available for defining permissions and field-level customizations. Please note that selecting fields makes them mandatory for the selected asset category. Field selection is also possible for mandatory sections.
In addition, Infraon allows you to create custom fields and select unique identifiers.
Few asset properties are mandatory across all asset categories. The mandatory properties and the fields are as follows:
Label
Fields
Common Properties
Status, Criticality, Service Status, Operational Status, Business Function, Description, Installation Date, Usage Type, State Change, Reason, Retire Reason, Vendor, Uninstall Date
Procurement Properties
Warranty In Year & Month, Warranty Expiry Date, Expiry Date, Purchase Vendor, AMC Vendor, AMC Cost, AMC Expiry Date, Lease End Date, Disposal Date, Reason, End Of Life, End Of Sale, End Of Support, End Of Extended Support, Last Renewal Cost, Next Support Renewal Cost, Effective Date, Effective Cost, Estimated Cost, Book Value, Tax Credit,
Cost Properties
The asset properties below are optional and available for selection.
Label
Examples
Hardware Properties
Serial Number, Hostname, Alias, Make, Model, UUID, Manufacturer, Domain, IP Address, Series, Tag No, QR Code, Barcode
OS Properties
OS Name, OS Version, OS Service Pack, OS Install Date, OS Installed By, Build Number, Product ID, Product Key, Virtual Memory
CPU Properties
Additional customizations are enabled within the 'Selected Sections.' You can define role-based view and edit permissions. These can be defined at the property level as well as the field level. You can enable or disable a specific field and make it mandatory using the relevant action icons.
Unique fields are unique identifiers for assets. Use the unique field drop-down to select as per requirement.
In addition to the default asset property fields, Infraon allows you to add custom fields.
Check the ‘Add Custom Field’ section below for more information.
Add pound currency in the asset management from UI symbols verification
Expanded Currency Options! Now offering 163 currencies, with INR as the default. Detailed asset currency view, cost estimates, and currency display in asset life cycle and depreciation graphs.
Select Assets -> Asset Type (IT Asset or Fixed Asset, etc.) from the left menu panel to view the asset grid page. The category panel is displayed on the left, and the assets are listed in a card view on the right.
Click on the + icon in the category panel.
The 'Add asset category' window appears.
Choose whether you are adding the category or the sub-category using the option button.
There are two tabs to add a category/sub-category.
Basic Details | Fields
Label
Action
Description/Example
Category Name
Add the asset category name.
Define the asset category name you want to categorize for asset management.
For example, the IT asset defines the category as laptop, desktop, etc.
Associate Item Types
Use the dropdown menu to associate asset items to this category.
Other Details | Fields
Label
Action
Description
Mark as CI
Select the toggle button to mark it as CI
CIs (Configuration Items) enable better tracking, management, and understanding of the asset's relationships and dependencies with other CIs.
Notify End Users on Asset Allocation (End Users can Accept/Deny assets)
After this step, click ‘Next’ to define fields for the selected asset category.
To add a sub-category within the selected category, proceed as below:
Label
Action
Description/Example
Sub-Category
Click on the sub-category.
Select this option to define an asset sub-category. A sub-category can be defined for an existing category too.
Parent Category
Select the parent category name using the drop-down menu.
Click 'Next' to define 'Fields' for the sub-category.
Basic Details | Fields
The mandatory sections are added by default. There are multiple levels of customization available here.
Level 1: From the list of mandatory fields, select fields to make them mandatory.
Level 2: Scroll down to select additional sections to add them to the selected section.
Level 3: Select fields from the additional sections to make them mandatory.
Level 4: Define role-based privileges, enable/disable fields or make them mandatory.
Level 5: Create a custom field to suit your specific needs.
Level 6: Select fields from the list of unique identifiers to add them.
Once the customization is complete, click ‘Submit’ to save. The ‘Add Item’ section provides details and instructions on adding an asset.
Label
Action
(+)
To add a sub-category.
How does it work?
Mandatory Asset Properties
Unique Fields
Create a Custom Field
Instructions to add the Asset Category
Click the 'Add Profile' button
Label
Action
Description/Example
Profile Name*
Give a name to the Business Hour Profile.
Support Team, Main Branch, Tech Support
Description
Once all the parameters are added, click 'Submit' to save the profile. Business Hour Profiles can be linked to SLA, Reports, and Discovery. Please refer to the module below for more details.
Repeat the process to add multiple profiles. Business Profiles can be edited or deleted using the respective icons.
The Software License View page provides a detailed overview of a selected software license, including license availability, allocation details, compliance status, lifecycle information, and license usage insights.
This page helps users monitor license consumption, track allocation status, manage license distribution, and review software license utilization from a centralized view.
What you see on the screen
License View | Basic Details
Label
Action
Description/ Example
The Allocate option allows users to distribute software licenses to different distribution types, such as Individuals, Assets, Departments, Locations, Entities, or Tags. Users can allocate licenses based on availability and track allocation details directly from the Software License View page.
The allocation process updates software usage details, allocation counts, insights, and distributed license records automatically after successful distribution.
Navigate to the required Software License View page.
Click Allocate.
The Distribute License sidebar opens.
Select the required Distribution Type.
Select the target value in the Distributed To field.
Enter allocation details such as owner or quantity, based on the selected distribution type.
Click Distribute to allocate the license.
After successful allocation:
License allocation counts are updated.
Available and allocated license values are refreshed.
Distribution details are recorded.
The allocation activity is updated in the audit records.
Distribute License | Allocation
The Distribute License sidebar is used to allocate software licenses to supported distribution targets.
Label
Action
Description/ Example
Once added, click Distribute to allocate licenses. This allocates the selected software license to the configured distribution target.
Merge History
The Merge History page provides a record of previous deduplication actions and allows users to review what happened to duplicate clusters.
Merge History | Top Panel
Label
Action
Description / Example
Add a brief description of the profile.
Tech support team from the Head Office.
Timezone
Select Timezone applicable for the profile.
Select 'Timezone' based on the team's work location. Multiple business profiles can be created to align to SLAs of multiple teams supporting multiple locations.
Work Hours
Use the option to select if the team works 24*7 or selected working days/hours.
24*7 - Select exclude hours for your team.
Select Working Days/Hours - Select weekdays, start and end times. The selected days and hours are taken as official working hours for the organization/team.
For the 'Select Working Days/ Hours' option, there is an option to add multiple Business Hour profiles. This can define business hours on weekends (Saturday/Sunday) or other holidays.
Exclude Hours
Add a reason and select weekdays, start, and end times to add exclude hours.
This can be the weekend, an official lunch hour/break time, or a change in the technician's shift.
Use the 'Add Exclude Hours'option to add multiple instances. 'Exclude Hours'are excluded while calculating SLAs.
Yearly Holiday List
Add Date and Holiday Name to add a specific day as a holiday.
To view the complete list of holidays applicable to your region, add 'Holiday' or click on import holidays.
Owner
Select the required owner.
Allows users to associate the allocated license with a specific owner or requester.
Quantity
Enter the required quantity.
Specifies the number of licenses to distribute. The entered value should not exceed the available license count.
Software Details
View-only field; no action can be taken
Displays complete information related to the selected software license, including software name, publisher, license type, compliance status, license count, and allocation details.
Allocate
Click Allocate to distribute licenses.
Opens the Distribute License sidebar, allowing users to allocate software licenses to individuals, assets, departments, locations, or other supported distribution types.
Software Logo
View-only field; no action can be taken
Displays the logo associated with the selected software or publisher.
Total License(s)
View-only field; no action can be taken
Displays the total number of purchased or available licenses configured for the software.
Available License(s)
View-only field; no action can be taken
Displays the number of licenses currently available for allocation.
Allocated License(s)
View-only field; no action can be taken
Displays the number of licenses already distributed to users, assets, departments, or locations.
Under-Licensed
View-only field; no action can be taken
Displays the number of allocations exceeding the available license count.
Compliance Status
View-only field; no action can be taken
Displays the compliance condition of the software license, such as Compliance or Non-Compliance.
License Based On
View-only field; no action can be taken
Displays the allocation type configured for the license, such as User or Asset.
License Count
View-only field; no action can be taken
Displays the configured license quantity for the software.
License Type
View-only field; no action can be taken
Displays the license category, such as Perpetual or Subscription.
Publisher
View-only field; no action can be taken
Displays the publisher associated with the software license.
License Life Cycle
View-only field; no action can be taken
Displays the software license lifecycle timeline from the effective date to the current or expiry date.
Effective From
View-only field; no action can be taken
Displays the start date from which the license becomes active.
License Usage (Last Year)
View-only field; no action can be taken
Displays a graphical representation of software license usage trends for the last year.
Distribution Type
Select the required distribution type.
Allows users to choose how the license should be distributed. Supported options include Individual, Department, Location, Asset, Entity, and Tags.
Distributed To
Select the required value.
Allocate
How does it work
Allocation is allowed only when licenses are available.
Expired licenses cannot be allocated.
Allocation details are reflected in usage insights and distributed license records.
Multiple license keys can be maintained under a single software license and selected during allocation.
Users can later deallocate licenses individually or in bulk based on allocation requirements.
Displays values based on the selected distribution type. Example: If Location is selected, the location list is displayed.
Displays all recorded deduplication actions.
Merged
Select
Displays clusters that were merged.
Kept Apart
Select
Displays clusters that were kept separate.
Undone
Select
Displays actions that were undone.
History Details
Label
Action
Description / Example
Timestamp
View
Displays when the deduplication action was performed.
Action
View
All
Select
Duplicate asset records can originate from discovery, manual entry, imports, or integrations.
The objective is to maintain one Golden Record while preserving historical and audit information.
Automatic merging requires zero conflicts + similarity at or above the one-click merge threshold
Invoice No., Part No., Cost, Purchase Date, Depreciation Type, Salvage Value, Currency, PO Number
Location Properties
Location Hierarchy, Country, State, City, Pin Code, Landmark, Flat House No Building Company, Area Colony Street Sector Village, Zone, Region, Division, Location Code, Latitude, Longitude
Select the toggle button and correspondingly add the trigger notification timer.
Unified notification system for handling large-scale allocations/ deallocations across various asset categories.
The allocation/ deallocation email process begins when an asset is assigned to a user for the first time. A single email containing all allocated asset information from that specific period will be sent to the De-allocation or vice versa.
Notify End Users on Asset De-allocation
Select the toggle button to enable the functionality
Enabling the toggle button will trigger a notification for the end user to accept/deny the deallocation of the asset.
Notify Owner on Warranty and AMC expiry
Select the toggle button and correspondingly add the trigger notification timer.
Turn on the toggle and set the alert date. This will automatically notify asset owners when their warranties and AMCs are about to expire.
Notify owner on discovery of blacklisted Application
Select the toggle button to enable the functionality
The owner of the IT asset will be notified via email upon discovery of a blacklisted application.
Notify Owner on Hardware Changes
Click to turn on/off the toggle button
When enabled, the system notifies the asset owner whenever there are hardware changes detected in the asset.
In addition, administrators can configure notifications to also include a requester along with the owner. Filter allows you to specify which hardware components should trigger notifications (e.g., CPU, memory).
Note: USB component changes are excluded by default, preventing unnecessary alerts for minor modifications.
Example: If memory is upgraded in a server, both the owner and the selected requester will receive a notification. However, if only a USB device is added/removed, no notification will be sent.
CI Notification fields
Dropdown / Multi-select
Allows users to select the hardware components or CI components that should trigger notifications when changes occur.
Owner (Default)
Recipient Option
Sets the asset owner as a notification recipient by default.
Notify Asset Department
Toggle
Enables notifications to the configured email group(s) associated with the asset's department.
Department
Dropdown / Multi-select
Select one or more departments whose configured email group(s) should receive hardware change notifications for the associated assets.
This field is available only when Notify Asset Department is enabled.
Notify Asset Location
Toggle
Enables notifications to the configured email group(s) associated with the asset's base location.
Location
Dropdown / Multi-select
Select one or more locations whose configured email group(s) should receive hardware change notifications for the associated assets. This field is available only when Notify Asset Location is enabled.
Notification Email(s)
Email Configuration
Allows administrators to configure or specify the email addresses or email groups that should receive notifications, where supported by the configuration. Allows administrators to select one or more requesters as additional notification recipients.
Notify Owner on Software Change
Select the toggle button to enable the functionality and choose users to notify
When enabled, the system notifies the asset owner (and selected users) via email whenever software is installed or uninstalled on the asset.
Notification content is based on the configured Software Changes template.
Notify on Inactive Inventory Agent
Select the toggle button to enable the functionality, set the inactivity duration (in days), and choose users to notify
When enabled, the system sends an email notification to the selected users if the asset’s inventory agent remains inactive for the specified number of days.
Down Since
Number and Time Unit
Specifies the duration for which an inventory agent must remain inactive before a notification is triggered.
Example: Configure 5 Days to identify agents that have been inactive for five days.
Notify To
Recipient Configuration
Specifies the user or recipient who should receive notifications about inactive inventory agents.
Define the parent category of your asset sub-category.
Purchase Order
The Purchase Order (PO) module streamlines and manages asset and service procurement within the organization. It helps eliminate manual errors, ensures compliance, and provides visibility across procurement workflows.
Adhering to ITIL v4 principles, the PO module ensures that procurement activities support value co-creation, optimize risk and cost, and maintain compliance through standardized workflows and clearly defined responsibilities.
Users with assigned roles can manually create purchase orders. The system supports customizable PO numbering, threshold-based approval workflows, vendor quote attachment, and order tracking.
The PO module supports core workflows depending on whether the item is available in inventory or needs to be procured from a vendor.
Used when specific roles (based on RBAC) are permitted to add a Purchase Order from the PO module directly.
Consumable Asset (Beta)
Consumable assets are resources gradually used or consumed over time, such as printer ink, paper, cleaning supplies, or markers. While essential to daily operations, these items require careful management to ensure continuous availability and cost control.
Infraon platform's Consumable Assets module offers a robust solution for tracking and managing these resources. This module allows users to monitor asset availability and associated costs, ensuring comprehensive oversight of all consumable assets.
The Consumable Asset management interface shares a consistent layout with other asset management sections, including IT Assets, Fixed Assets, Software Inventory, and Software Licenses. Asset categories are displayed in the screen's left navigation panel.
To help you get started:
Browse categories by using the intuitive left sidebar
.
Active dependencies prevent automatic merging and send the cluster for manual review.
Undo is available only within 30 days.
A wrongly grouped cluster can be split into two or more groups, with every existing record assigned exactly once.
Displays the action performed on the cluster.
Actor
View
Displays the user or process that performed the action.
Survivor
View
Displays the record selected as the surviving asset.
Retired Records
View
Displays the records retired as part of the merge.
Overridden Fields
View
Displays fields whose values were overridden during the merge.
Undo
Click
Reverses an eligible deduplication action within the available 30-day window.
Key Behavior
Step
Description
Create PO
A department user submits a request for an item (e.g., a laptop) via Infraon Request Management.
Users with privileges will create a PO using the "Add" option in the PO module.
PO Creation
The PO is generated manually based on request data. A unique PO identifier (customizable format) is assigned. Line items such as model, quantity, price, and delivery terms are added.
Approval Workflow
The PO follows an approval process based on threshold values (1-level and 2-level).
After approval, the PO is shared with the vendor. The vendor acknowledges the order and provides delivery timelines.
Fulfilment
The vendor ships the item. IT/Procurement receives and verifies the asset and updates the asset system.
Invoice & Payment
Vendor sends invoice → Finance team processes payment → Linked with PO record.
Closure
Once the item is received and payment is made, the PO is marked as Closed in the system.
The PO Download option allows users to download the Purchase Order as a document for review and verification. The downloaded file includes complete PO details, including vendor information, line items, pricing, taxes, and terms.
When can you download the PO:
During Approval: If the {{PO download link}} macro is configured in the Approval Email Template, approvers can download the PO directly from the approval email when the status is Waiting for Approval.
After Approval: The PO can be downloaded from the PO view once it is approved (existing behavior).
This page displays the complete list of configured Purchase Orders (POs) categorized by vendor and allows users to perform essential procurement-related operations. You can filter records, view order statuses, configure approval rules, and manage vendor-wise orders with relevant actions like add, edit, or delete.
Basic Details | Purchase Order
Label
Action
Description / Example
Search
Type search query
Use this to find a purchase order quickly.
Note: Type at least three characters to initiate the search.
Filter
When this setting is enabled, the system allows users to define a custom purchase order ID structure. The format can be configured using prefixes, numeric values, and selected fields to align with business-specific naming conventions.
This format is applied automatically during purchase order creation, ensuring each PO is uniquely and consistently identified.
Example Formats:
#PO-00001
#PO-PURCHASE-00002
#PO-2026-IT-0100
You can configure this from: Purchase Order → Actions → Customize PurchaseOrder ID
or
System Configuration → Formatting → Purchase Order
Customize Purchase Order ID Format | Field Reference
Label
Action
Description / Example
Preview Section
View-only
Displays a live preview of the generated PO ID based on the selected format.
Prefix
Enter text manually
This option allows you to define dynamic approval workflows for POs based on predefined conditions such as role-based submission and amount thresholds. Approval rules are essential for ensuring proper financial governance aligned with organizational policies.
Click Configure Approval.
Select a User Role (e.g., NOC Operator).
Enter the Request Threshold value (e.g., ₹5,000).
Add a condition for Asset Value (optional).
Assign the Approver for each rule.
Click + Condition to add layered conditions (optional).
Click + Add More Rule to create additional approval scenarios.
Save the configuration.
This rule engine allows multiple tiers of approval, ensuring purchases are validated based on business-critical thresholds.
Click the + icon in the Vendor option on the top right corner.
The vendor creation form includes three tabs: Organization Details, Address, and Representatives. Refer to the table below for guidance on filling in each field.
Use Template Configuration to customize the Purchase Order preview, print, and PDF layout. It allows you to control how sections and fields are arranged in the final Purchase Order document.
The configuration includes two options:
Layout – Used to arrange template sections and reorder fields.
Field Manager – Used to add or remove sections and fields.
The Purchase Order template includes the following sections:
Header
Vendor Details
Order Details
Shipping Details
Item Details
Summary
Terms and Conditions
Signatures
Footer
Step
Action
1
Navigate to Purchase Order Template Configuration.
2
Use the Layout tab to rearrange sections and reorder fields.
3
Option
Description
Layout
Displays the current template structure for reordering sections and fields.
Field Manager
Displays available sections and fields that can be added to the template.
Undo
How It Works
Direct PO Creation by Authorized Users
PO Creation Workflow
This is a configurable workflow within the Infraon platform for Purchase Order creation and processing. Users with the necessary permissions can later modify the PO workflow from the module. The workflow can be customized to include multiple approval levels, threshold-based approvals, and additional process elements as required.
PO Download
Downloading the PO does not impact the approval workflow or status.
What Do You See on the Screen?
Customize Purchase Order ID
Configure Approval
Add an Approval Rule
Add Vendor
Template Configuration
How to Configure Purchase Order Template
Actions
Saved changes apply to Purchase Order preview and downloaded PDF files.
Order Details is a default section and remains part of the template.
added in Purchase Order can also be used in the template layout.
Click any category to view its associated assets
Use filters and sorting options to find specific items quickly
Like the IT Assets and Fixed Assets modules, consumable assets can be organized into categories for easier management and tracking. This allows organizations to classify and manage resources based on type, usage, or department needs.
The following table provides detailed information about consumable asset management:
Consumable Assets | Basic Details |
Label
Action
Description/ Example
Search
Allows searching for specific consumable assets
Search by asset ID, asset name, owner, etc., to quickly find the required consumable asset
Filter
There are two ways to add consumable assets:
1. Single Asset - You can add a single asset from the drop-down menu in the top right corner
2. Import from CSV - If you have the asset CSV file, you can import it from the drop-down menu in the top right corner.
In the Asset module, go to the Consumable Asset submodule page.
Click Add Item and choose Single Asset.
There are two tabs on the 'Add Asset' page. Refer to the table for information.
Define Asset | Add Asset info
Label
Action
Description/ Example
Product Image
Add an image or icon representing the asset
Use the drag-and-drop feature or upload files in PNG, JPG, or JPEG formats (Max size: 20 MB)
Asset Name
Once all the parameters are added, click 'Next' to add consumable details.
Consumable Details | Common Properties
Label
Action
Description/ Example
Quantity
Enter a whole number or decimal value
Specify the available quantity of the asset in the inventory
Re-Order Quantity
Once all the parameters are added, click 'Submit.' The Asset is added under the selected category within Infraon platform.
Upload a CSV file containing the asset details to add multiple assets simultaneously. This process works similarly to importing a CSV file to add multiple IT or Fixed Assets. Click hereto learn more.
The Asset Details page provides a comprehensive overview of each asset, displaying essential information on the top panel, such as:
Product Image
Asset Name
Asset ID
Asset Type
Model
Vendor
On the left panel of the page:
Cost Properties
Users can track the financial aspects of consumable assets, with each asset listing key cost-related information, such as:
Total Inventory Cost
Average Buying Price
Selling Price
This feature allows organizations to effectively monitor costs and profitability, providing better control over financial resources.
Managed By
Under the " Managed By " section, administrators can assign specific users to oversee individual assets, ensuring clear accountability and efficient management.
Tags
This section displays a list of tags associated with each asset, enabling easier navigation and quick filtering for faster access to relevant asset information.
Refer to the following table for detailed information:
Action Icons | Basic Details
Label
Action
Description/ Example
Add Stock
Click to modify inventory details
Use this option to add more items to the inventory. In the pop-up window, provide details such as Location, Quantity, Price, Expiry Date, and Vendor, then click Add to confirm.
Distribute
The Asset Details page is organized into three distinct sections located on the left panel of the page.
The module offers comprehensive tracking of inventory status across various periods—weekly, monthly, and yearly.
Users can monitor asset availability by location, gaining insights into the number of assets in Instock, newly Added items, and those that have been consumed. This functionality ensures optimal inventory management and aids in predicting future asset needs.
The Inventory History section provides a comprehensive overview of stock movements, allowing users to view inventory levels by location, quantity, available quantity, action type, vendor, status, added date, and expiration date. This makes it easy to track changes in stock over time, helping teams plan for restocking or asset replenishment based on consumption trends.
The Recent Activities section captures the complete history of each asset, including:
When the asset ID was created, modified, or updated.
Any changes in asset status, location, or ownership.
This audit trail ensures that users have full visibility into each asset's lifecycle, making it easier to trace any changes for reporting or troubleshooting purposes.
Label
Action/ Description
Search
Search for the required asset’s history by adding its name or ID or filtering by the user who made changes to it.
Date Range
Apply a filter to view the asset history within a specified time frame. From the drop-down menu, select options such as Current Hour, Last 30 minutes, Last Hour, etc.
Export
What do you see on the screen
Note: Refer to the '' section for more information.
Add Consumable Asset
Instructions to 'Add Single Asset'
Note: Fields marked with asterisk (*) are mandatory.
Note: Clicking “Show Mandatory Icon” will display only the mandatory fields within the tab.
Instructions to 'Import from CSV’
Asset Details
Action Icons
Summary
Inventory History
Recent Activities
Action Icons
Request for Quotation
A Request for Quotation (RFQ) is a procurement document that invites one or more vendors to submit quotations for products or services required by an organization. It enables procurement teams to compare vendor responses, evaluate pricing and commercial terms, obtain the necessary approvals, and select the most suitable vendor before generating a (PO).
Within Purchase Management, the RFQ module serves as the bridge between procurement requests and purchase execution. After identifying procurement requirements, users create an RFQ, invite vendors to participate, collect quotations, compare vendor responses, complete the approval process, and generate Purchase Orders for the selected vendors. Throughout the lifecycle, the module maintains communication history, attachments, approvals, and activity logs to provide complete traceability and auditability.
The Request for Quotation process begins by creating an RFQ and defining the required products or services, vendors, and commercial details. The RFQ is then shared with the selected vendors, who submit their quotations before the specified due date. Procurement teams review the received quotations, compare vendor pricing and terms, evaluate technical and commercial requirements, and select the appropriate vendor or vendors.
Once the quotation is approved, the system generates one or more Purchase Orders based on the awarded vendors. Throughout the process, the RFQ workflow tracks each stage of the procurement lifecycle while maintaining communication history, approvals, attachments, and activity records.
The RFQ module integrates with the following Purchase Management modules:
Apply filters based on specific fields and conditions
Fields: Asset Name, ID, Owner, Location, Requester, and Type. Conditions: "in," "not in, "equal to, "and "not equal to" from the drop-down options.
Add Item
Click to add a new consumable asset to the inventory
Choose between adding an asset manually or importing a CSV file for bulk upload.
Asset Name
Click on the asset name to view more details in a pop-up window
Displays the asset name (e.g., Markers, Printer Ink). Clicking will open a pop-up showing Summary, Inventory Details, and Recent Activities.
Asset ID
View-only field: no actions can be taken
Displays the unique asset ID associated with the consumable asset (e.g., INFRAON0448).
Vendor
View-only field: no actions can be taken
Shows the vendor name associated with the consumable asset (e.g., Microsoft, Camlin).
Type
View-only field: no actions can be taken
Indicates the asset type, such as whether the asset is degradable or non-degradable (e.g., Degradable, Non-Degradable).
Total Quantity
Modify the asset’s quantity
It displays the total stock available. Click on the plus or minus to adjust the quantity and add the respective details: Location, Quantity, Price, Total Price, Expiry By, and Vendor in the pop-up window.
Enter a specific name for the asset
Assigning a unique name makes it easier to locate and identify the asset
Category
Select the appropriate category from the dropdown
Placing an asset in a specific category streamlines navigation and organization
Owner/Technician
Choose from the dropdown list
Designate an owner or technician responsible for the asset
End User/Requester
Choose from the dropdown list
Identify the end user or requester who will be utilizing the asset
Owner Tags
Select tags from the dropdown
Assign tags to the owner for simplified identification and filtering
Asset Tags
Select tags from the dropdown
Tag the asset for enhanced searchability and filtering
Location
Choose the asset’s storage location from the dropdown
Specify where the asset will be stored to assist in inventory tracking and management
Enter a whole number or decimal value
Define the minimum quantity level that will trigger a reorder to maintain stock availability
Buying Price
Enter a whole number or decimal value
Specify the purchase price per unit of the asset
Selling Price
Enter a whole number or decimal value
Set the selling price of the asset if it’s available for resale
Low Stock Threshold
Enter a whole number or decimal value
The minimum quantity level set for inventory items triggers a reorder alert to prevent stockouts.
Threshold User Type
Select from the dropdown
Select whether the threshold is based on a Department or User level
Threshold To
Choose from the dropdown
Based on the selected user type, choose the specific user or department responsible for managing the threshold
Type
Select from the dropdown
Specify whether the asset is Degradable or Non-Degradable
Expiry Date
Click to open a calendar to select a date
Enter the expiration date of the consumable asset
Model
Input the model number
Provide the model number associated with the asset for better tracking and identification
Description
Input descriptive details
Include relevant details about the asset to enhance clarity and understanding
Currency
Select from the dropdown
Choose the currency in which the asset was purchased to maintain accurate cost records
Click to allocate inventory assets
Distribute the asset to specific users or departments. In the pop-up window, enter details such as Location, Quantity, and Distribution Type (User/Department), then click Distribute to finalize.
Edit
Click to open a pop-up window for updates
It allows users to modify asset details, including the Name, Image, Owner, Requester, and other relevant fields.
Delete
Click to remove the asset from the inventory
Permanently deletes the consumable asset from the inventory. Confirm the action by selecting Yes, Delete It.
Click to download the asset history details in CSV format. This format enables easier analysis of asset history for tracking and financial purposes.
Timeline View
View the asset history in a timeline format. This provides a visual representation of changes made over time, allowing users to assess the sequence of events and modifications quickly.
Grid View
Switch to a grid view for a more structured and tabular representation of the asset history. This view is ideal for comparing and analyzing multiple data points at once.
Purchase Requisition (PR): Procurement requirements captured in Purchase Requisitions can be used to initiate the RFQ process.
Vendor Management: Vendors selected in the RFQ are retrieved from the configured vendor records.
Workflow Management: Controls RFQ statuses, transitions, approvals, and publishing of the RFQ workflow.
Field Configuration (RBAC): Determines field visibility, edit permissions, mandatory fields, and access based on user roles.
Custom Fields: Allows organizations to extend RFQ forms with business-specific information.
Purchase Order (PO): Approved vendor quotations are converted into one or more Purchase Orders for procurement execution.
The following table describes the default lifecycle of a Request for Quotation.
Lifecycle | Workflow Stages
State / Status
Workflow Stage
Description / Example
Draft
Creation
The RFQ is created and saved with the required procurement details. Users can modify the RFQ before communicating it to vendors.
Example: An RFQ for purchasing office laptops is created and saved as a draft.
Sent to Vendor
The Request for Quotation page displays all RFQs created in the organization. From this page, you can search, filter, create, view, edit, and manage RFQs. It also provides access to line-item column configuration and displays key information, including the RFQ ID, title, requester, required date, priority, total amount, location, and current status.
Label
Action
Description / Example
Search
Enter a keyword to locate an RFQ.
Searches RFQs using values such as the RFQ ID, title, requester, or other searchable fields.
Example: Enter RFQ0097 or Laptop Procurement to locate a specific RFQ.
Filter
Click the Filter icon to apply one or more filters.
Use advanced filter logic for PO records.
Fields: Purchase Order Name, ID, Vendor, Department, Description.
Conditions: in, not in, equal to, not equal to, contains, not contains.
Filter by Date
Select from the dropdown
Narrow down POs based on time ranges.
Options include: Last 30 Days, Last 60 Days, Last 90 Days, Custom, etc.
The Meeting module allows users to create, schedule, and manage meetings directly from the Workspace Calendar. It supports one-time, instant, and recurring meetings with attendee management, location selection, meeting associations, calendar views, filters, and meeting lifecycle operations such as starting, joining, canceling, and ending meetings.
The module also supports multiple meeting types, including video conferences and conference room meetings, while allowing meetings to be associated with operational entities such as Tickets, Requests, Changes, and Assets.
What you see on the screen
This page displays a calendar-based meeting management interface that lets users schedule and track meetings across the Month, Week, Day, and List calendar views.
Users can create meetings, refresh calendar data, and apply status and meeting-specific filters. The calendar also lets users navigate between dates and view meetings by status, attendee email, VC location, region, meeting type, and associated records.
Meeting | Basic Details
Label
Action
Description / Example
Meeting | Filters
Label
Action
Description / Example
Meeting | Calendar Legend
The calendar uses color coding to indicate meeting status and type.
Color
Meeting Status / Type
Use this option to create and schedule a new meeting from the Meeting calendar.
The meeting creation process is organized into the following four sections:
Meeting Details
Location & Invitees
Host & Contact Person
Agenda & Attachments
Add Meeting | Field Descriptions
Label
Action
Description / Example
Add Meeting | Locations & Invitees
Label
Action
Description / Example
Add Meeting | Host & Contact Person
Label
Action
Description / Example
Add Meeting | Agenda & Attachments
Label
Action
Description / Example
Once all required details are added, click Schedule Meeting to create and schedule the meeting.
Customer Registration
The Customer Registration module enables organizations operating in MSP (Management Service Provider) mode to create and manage customer accounts within the Infraon platform.
This module is required when a single organization manages multiple customers (tenants) and needs:
Logical segregation of customer data
Customer-wise asset mapping
Customer-specific user access
License allocation and tracking per customer
Entity-level structuring under a customer
Customer Registration ensures that assets, users, licenses, reports, dashboards, and monitoring configurations are mapped and isolated based on the selected Customer or Entity.
When MSP is disabled, this module is not available, and the organization operates in a single-tenant model.
Customer Registration | Basic Details
Label
Action
Description / Example
To create a new customer, click Add Customer on the top panel.
In the Add Customer sidebar, provide the required information across the following sections:
Customer Details
Entity Details
Settings
Customer Details | Add Customer
Label
Action
Description / Example
After entering the required details, click Next to proceed to the Entity Details section.
Entity Details | Customer Details
The Entity Details tab allows you to create and associate one or more entities under a customer. An entity represents a logical or operational subdivision of a customer, such as a branch, department, region, or business unit. Each entity can maintain its own contact and location information while remaining mapped to the parent customer.
Entities help segregate assets, users, reports, and configurations within a customer scope when MSP is enabled.
Click Save to create the entity and associate it with the customer. After the entity is added, click Next to proceed to the Settings configuration.
Settings | Customer Details
Label
Action
Description / Example
Click Next to proceed to the License configuration.
License | Add Customer
The License tab is used to allocate license counts to the customer for users and assets. This section defines how many resources the customer is permitted to use within the organization.
The configured values determine the operational limits for that customer and are validated against the organization’s available license pool. This tab includes:
User License Count
User Count
Technician User Count
Asset License Count
Each value entered here controls how many corresponding users or assets the customer can manage within the platform.
After entering all required details, click Submit to create the customer.
Duplicate Clusters
Clusters with no field conflicts that meet the configured one-click merge threshold can be merged automatically during a pipeline run. However, clusters with active dependencies such as open Incidents/Changes, License Allocations, or Contract relations are kept for manual review.
What you see on the screen
The Duplicate Clusters page provides a consolidated view of asset records identified as potential duplicates. It allows users to review duplicate clusters, compare candidate records, select a survivor, resolve field-level conflicts, and perform the required deduplication action.
The page includes:
Summary cards
Duplicate cluster filters
Duplicate cluster list
Cluster review options
Duplicate Clusters | Summary Cards
Label
Action
Description / Example
Filter Duplicate Clusters
You can filter the duplicate cluster queue based on its current state.
Label
Action
Description / Example
Cluster Details
The duplicate cluster list displays key information about each identified cluster.
Label
Action
Description / Example
Clicking a Cluster opens the Cluster Review page, where users can examine the records in detail before resolving the cluster. Use the Cluster Review page to examine candidate asset records within a duplicate cluster before deciding whether to merge them.
Review Details
Label
Action
Description / Example
The candidate records section displays the asset records identified as potential duplicates.
For each candidate record, you can review information such as:
Asset record
Source
Created date
Completeness score
Use this information to compare the candidate records and determine which record should be retained.
The Survivor is the asset record that will be retained when the duplicate records are merged.
To select a survivor
Open the duplicate cluster.
Review the candidate records.
Select the record that should remain after the merge.
The selected record is marked as Survivor.
When a survivor is selected, the field conflict table uses the survivor's values as the default values for the merged record.
Use Case
An asset may have been discovered from multiple sources and therefore exist as several records. One record may contain more complete or reliable information than the others.
In this situation, select the most appropriate record as the Survivor so that it becomes the trusted asset record after the merge.
The field conflict table allows you to compare values from the candidate records before merging them.
Fields with different values across candidate records are identified as conflicts.
Fields with matching values are not marked as conflicts.
The table provides:
Values from the different candidate records.
A result column showing the value that will be used in the merged record.
Visual identification of conflicting fields.
Review the conflicts carefully before completing the merge to ensure that the resulting asset record contains the appropriate information.
When duplicate asset records contain different values for the same field, the Field Conflict table highlights the conflicting values.
Review the values provided by each source and determine which value to retain in the final asset record.
Steps
Review the conflicting field.
Compare the values provided by the different sources.
Select the value that should be retained in the final asset record.
Continue reviewing the remaining conflicting fields.
The selected values are applied when the duplicate records are merged.
Use Case
An asset may have a different hostname or location in two discovery sources. The reviewer can compare the source values and select the correct value before merging the records.
If field-level values have been manually overridden during conflict resolution, the reviewer can reset the selections to the values associated with the proposed survivor.
Steps
Review the current field selections.
Select Reset to Survivor.
Verify that the field values have been restored to the proposed survivor's values.
Make any required changes before proceeding with the merge.
This helps quickly revert manual field selections and return to the survivor-based values.
Before merging duplicate records, review the Merge Impact Preview to understand what will happen when the merge is completed.
The preview provides information such as:
Records that will be retired.
Tickets that will be re-pointed.
Licenses that will be released.
Steps
Review the merge impact information.
Verify the records that will be retired.
Review any tickets that will be re-pointed.
Review licenses that will be released.
Label
Action
Description / Example
Cluster Review | Split Cluster
Label
Action
Description / Example
Instructions to add a process
In the Infraon platform, navigate to the IMACD module.
Click on the Add process -> Install, located at the top right corner of the page.
Enter the respective call-out boxes.
Install IMACD| Fields
CI relationship in CMDB Upstream
Add Purchase Requisition
To add a new Purchase Requisition, click + Add Purchase Requisition available at the top-right corner of the Purchase Requisition page.
In Purchase Requisition, there are three tabs available for configuration:
Purchase Requisition Properties
Item Details
Terms and Conditions
Execution
The RFQ is sent to one or more selected vendors, inviting them to submit quotations before the due date.
Example: The RFQ is emailed to three approved hardware vendors.
Pending Vendor Response
Execution
The system is waiting for vendors to respond with their quotations. Procurement users can monitor pending vendor responses during this stage.
Example: Two invited vendors have not yet submitted their quotations.
Quotation Received
Execution
One or more vendors have submitted their quotations successfully. The quotations are available for review and comparison.
Example: Three vendors submit pricing, delivery schedules, and commercial terms.
Under Evaluation
Execution
Procurement teams evaluate the received quotations based on pricing, technical specifications, delivery timelines, and commercial conditions.
Example: Vendor quotations are compared to identify the most suitable supplier.
Negotiation in Progress
Execution
Procurement users negotiate pricing, payment terms, delivery schedules, or other commercial conditions with vendors before finalizing the quotation.
Example: The procurement team requests a revised quotation with a discounted unit price.
Waiting for Quotation Approval
Approval
The selected quotation is submitted for approval according to the configured RFQ workflow.
Example: The Procurement Manager reviews the recommended vendor before approving the quotation.
Approved
Approval
The quotation has been approved and is ready for Purchase Order creation.
Example: The selected vendor quotation is approved for procurement.
PO Created
Closure
One or more Purchase Orders are generated for the approved vendor(s), completing the procurement selection process.
Example: Separate Purchase Orders are generated for two vendors supplying different line items.
Closed
Closure
The RFQ lifecycle is complete, and all procurement activities associated with the RFQ have been finalized.
Example: The RFQ is automatically closed after successful Purchase Order generation.
Rejected
Approval
The quotation or RFQ is rejected during the approval process, preventing Purchase Order creation until corrective action is taken.
Example: The quotation is rejected because it exceeds the approved procurement budget.
Cancelled
Closure
The RFQ is canceled before completion due to changes in procurement requirements or business decisions.
Example: The procurement request is withdrawn because the requested items are no longer required.
Filters the RFQ list based on configured criteria such as Status, Requested By, Supplier, Priority, Location, or custom fields. Multiple filters can be applied simultaneously and cleared when no longer required.
Date Filter
Select a predefined date range from the drop-down list.
Displays RFQs created within the selected time period. Available options include Last 60 Days, Last 90 Days, Last 180 Days, and Last 365 Days.
Actions
Click Actions to access additional page-level options.
Select Line Item Column Selection to configure the columns displayed for RFQ line items in the Add, Edit, and View pages.
Add Request for Quotation
Click + Add Request for Quotation.
Opens the New Request for Quotation wizard, allowing you to create a new RFQ by entering the quotation details, adding line items, selecting vendors, and configuring terms and conditions.
Action Icons
Edit
Edit an existing RFQ.
Opens the selected RFQ in edit mode, allowing authorized users to update the RFQ details based on the current workflow stage and assigned permissions.
Delete
Delete an existing RFQ.
Removes the selected RFQ from the system after confirmation. This action is available only to users with the required permissions and for RFQs that satisfy the configured workflow rules.
Merged This Month
View
Displays the number of duplicate records merged this month.
Pending
Select
Displays clusters that are pending review or resolution.
Ambiguous
Select
Displays clusters where the duplicate relationship requires further review.
Resolved
Select
Displays clusters that have already been resolved.
Rule
Select
Displays the deduplication rule associated with the cluster.
%
Enter percentage
Displays the percentage or similarity-related value associated with the cluster.
Record
View
Displays the number of asset records included in the cluster.
Sources
View
Displays the sources from which the records originated.
Similarity
View
Displays the similarity score between the records using a progress bar.
Conflicts
View
Displays the number or presence of conflicting field values between records.
Proposed Survivor
View
Displays the asset record proposed to remain as the surviving record after merging.
State
View
Displays the current state of the duplicate cluster.
Action
Click
Provides the Review option.
Choose Survivor
Choose the Survivor
Displays multiple asset lists for selection of the survivor; it has details of the asset. Allows the reviewer to select or override the record that should remain as the surviving asset record.
Resolve field conflicts
Select the required field for the survivor
In the Resolve field conflict, it displays all details of the asset that is under the matched field like IP address, asset name. Displays field values from each source and highlights fields where conflicting values are identified. You can select from different source and make it as one cluster.
What happens on merge
View
Displays the selected result value that will be retained after the merge.
Verify that the selected values represent the most accurate asset information.
If the impact is acceptable, proceed with the merge.
Split Cluster
Assign each record to a group
Allows users to divide records into separate groups. Records assigned to the same group remain together; the split does not merge or retire any records.
+ Add Group
Select + Add Group
Allows users to create an additional group when the records need to be divided into more than two groups.
Assign to Group
Select Cluster A, Cluster B, or another added group
Assigns each record to the selected group. Every record must be assigned to a group before the split can be confirmed.
Confirm Split
Select Confirm Split
Splits the original cluster into the configured groups based on the record assignments.
Duplicate Clusters
View
Displays the total number of identified duplicate clusters, along with a percentage badge, subtitle, and progress bar.
Redundant Records
View
Search
Enter keyword
Search for the required data.
All
Select
Cluster
Click
Displays the unique identifier of the duplicate cluster. Click to open the Cluster Review page.
Rule
View
Cluster name
View
Displays the name of the Cluster
Cluster Similarity
View
Merge
Select Merge
Consolidates duplicate asset records into a single record. The selected Survivor is retained, while the other records are retired.
Not Duplicate
Select Not Duplicate
Splitting this Cluster
Select a group (Cluster A or Cluster B) for each record
Allows users to divide the records in the cluster into separate groups. Records assigned to the same group stay together, and splitting does not merge or retire any records.
Cluster A / Cluster B
Assign records to Cluster A or Cluster B
Cluster Review
Choose Survivor
Resolve Field Conflicts
Reset to Survivor
What Happens on Merge
Review the impact before confirming the merge to ensure that dependent records and relationships are handled as expected.
Displays the number of asset records identified as redundant.
Displays all duplicate clusters in the queue.
Displays the Rule name of the cluster.
Displays the similarity score between the records using a progress bar.
Keeps the records separate when they represent different assets, even if they have similar names or identifiers.
Provides two groups within the cluster to organize the records. For example, records can be assigned to Cluster A or Cluster B based on whether they belong to the same asset.
Selected CI is written by this CI
Author of the selected CI
The attribute pertains to the authorship of a selected CI
Backed up by
Is backed up by the Selected CI
Back up of the selected CI
This feature refers to the backup status of a chosen CI
Cluster
Belongs to the cluster of the selected CI
Belongs to the cluster of the selected CI
This signifies the membership of a chosen CI within a specific cluster.
Connects
Connects to the selected CI
Selected CI is connected by this CI
Indication of the selcted CI is linked to or communicates with the specified CI. For Example: if a router (selected CI) is connected to a switch (connecting CI), the "Connects" attribute for the router would show the switch's name, indicating the network link.
Connected to
Connected to the selected CI
Selected CI is connected to this CI
Showcases a connection or relationship between the two components. For example: IoT, the connected to field for the bulb would display the hub’s name.
Are part of
Is a part of the selected CI
Selected CI is part of this CI
Signifies that the chosen CI is a component or element within another CI, illustrating a hierarchical relationship.
Consumes
Consumes the selected CI
Selected CI is consumed by this CI
The chosen CI utilizes or relies on another CI for its operation or functionality, representing a dependency where the selected CI consumes the specifies CI.
Attached to
Is attached to the selected CI
Selected CI contains this CI
Denotes that the selected CI is connected to or contained within the specified CI. For example: In email clients, files attached to an email are indicated through the "Attached to" field. The files are linked to the email they are attached to.
Contained By
Is contained by the selected CI
Selected CI contains this CI
Signifies that the chosen CI is encompassed or hosted within another CI, indicating that the selected CI is a part of or nested within the specified CI. For example: In web development, widgets or elements contained by a web page are represented by the Contained By field. The elements are part of the web page's content.
Cooled By
Is cooled by the selected CI
Selected CI cools this CI
This attribute signifies that the chosen CI is responsible for cooling another CI, indicating a relationship where the selected CI is the source of cooling for the specified CI. Example:
Gets Resources from
Gets resources from the selected CI
Selected CI defines resources for this CI
The chosen CI receives resources from another CI, signifying a dependency where the selected CI relies on the specified CI to provide necessary resources. Network devices like routers get resources such as bandwidth and routing information from core switches. The Gets resources from field for the router would list the core switch’s name.
Used by
Is used by the selected user
Selected CI depends on this CI
The attribute signifies that the chosen CI is utilized by a specific user, indicating a relationship where the selected CI plays a role in providing functionality or value to the user. For example: Software applications, this is used by a certain user, the attribute for the application would display the user’s name. This indicates that the user relies on the application for their tasks.
Distributes
Is used to distribute the selected CI
Selected CI is distributed
Indication that the chosen CI serves the purpose of distributing another CI, highlighting a relationship, selected CI is responsible for disseminating or sharing the specified CI. Example: Data sharing point, where a file service distributes files and documents to authorized users. The distributes field for the service would indicate its role in distributing files.
Provides DR for
Provides DR (Disaster Recovery) for the selected CI
Selected CI's DR (Disaster Recovery) is provided by this CI
The attributes signifies that the chosen CI is responsible for offering disaster recovery services for another CI, indicating a relationship where the selected CI is a source of recovery in case of a disaster affecting specified CI. Example: High availability cluster, provides disaster recovery by ensuring seamless failover in case of components failures
Is Edited by
Is edited by the selected user
Editor of the selected CI
This attribute indicates that the chosen CI is modified or edited by a specific user, highlighting the relationship where the selected CI is subject to changes made by the specified user. Example: Configuration Files: A configuration file is edited by an administrator to adjust settings or parameters for a software application or system.
Is enabled by
Is enabled by the selected CI
Enables the selected CI
This signifies that the chosen CI is made functional or operational by another CI, highlighting a relationship where the selected CI relies on the specified CI to enable its functionality. Example: Network Services, like remote desktop access is enabled by a service daemon that runs in the background to facilitate the service.
Exchanges
Exchanges information with the selected CI
Selected CI exchanges information with the selected CI
Indication that the chosen CI shares or transfers information with another CI, showcasing a relationship where both Cis interact to exchange data or communication. Example: IoT Devices, in a smart home can exchange data with a central hub to provide real-time status updates and receive commands.
Exchanges data with
Exchanges data with the selected CI
Selected CI exchanges data with this CI
The attribute indicates that the chosen CI shares or transfers data with another CI, highlighting a relationship where both Cis interact to exchange specific data or information. Example: API Communication A web application can exchange data with a third-party API to retrieve external information or perform specific actions.
Fed By
Is fed by the selected CI
Selected CI feeds this CI
The chosen CI receives inputs or resources from another CI, emphasizing a relationship where the selected CI is supplied with essential inputs or support by the specified CI. Example: Workflow automation, an automated process can be fed by data inputs that trigger different stages of the workflow.
Template for
Is a template for selected CI
Selected CI has this CI
This attribute indicates that the chosen CI serves as a template for another CI, highlighting a relationship where the selected CI provides a blueprint or predefined structure that the specified CI follows. Example: Email Template, provides a standardized format for creating consistent emails. The “Template for” field for the template would indicate its role in email communication.
Is Attached To
Is attached to the selected CI
Selected CI has this CI
This attribute signifies that the chosen CI is physically or logically connected to another CI, highlighting a relationship where the selected CI is part of or connected to the specified CI. Example: Documents in Email, an attachment is attached to an email indicating that the attachment is sent along with the email.
Is Registered On
Is registered on the selected user
Selected CI has been registered to this CI
Indicates that the chosen CI is registered or associated with a specific user, highlighting a relationship where the selected CI is linked to the specified user for identification or ownership purposes. Example: Software Licenses is registered on user’s account, indicating that the user has ownership rights to use the software.
Hosts
Hosts the selected CI
Selected CI has been hosted on to this CI
The attribute indicates that the chosen CI provides hosting or support for another CI, highlighting a relationship where the selected CI is being hosted or managed by the specified CI. The attribute indicates that the chosen CI provides hosting or support for another CI, highlighting a relationship where the selected CI is being hosted or managed by the specified CI.
Example: Cloud Infrastructure a virtual machine instance hosts a software application in a cloud environment, providing the necessary resources for the application to run.
Impacts
Impacts the selected CI
Selected CI is impacted by this CI
The attribute indicates that the chosen CI has an effect or influence on another CI, highlighting a relationship where the selected CI directly or indirectly affects the specified CI. Example: Software Updates can impact the stability and functionality of an application, potentially introducing new features or causing compatibility issues.
Implement End Point From
Implement the endpoint from the selected CI
Selected CI is implemented the endpoint from this CI
The chosen CI is used to create or establish an endpoint based on another CI, highlighting a relationship where the selected CI is implemented to provide a specific endpoint using the features or capabilities of the specified CI. Example: Network Endpoint is implemented by configuring a network device, allowing data to be sent or received through the endpoint.
Rack contains
Rack contains the selected CI
Selected CI contains this CI
This indicates that the chosen CI is physically located within a rack, emphasizing a relationship where the selected CI is housed or positioned inside the specified rack. Example: Server Rack Configuration is contained within a server rack, highlighting that the server is physically installed and mounted in the rack.
Member of
Is a member of the selected CI
Selected CI contains this CI
The chosen CI is a part of or belongs to a larger entity or group represented by the selected CI. This relationship highlights that the selected CI contains or encompasses the specified CI as a constituent element. Example: Software modules, can be a member of a larger suite, indicating that the application is part of the suite offering various functionalities.
Instantiated by
Is instantiated by the selected CI
Selected CI initiates this CI
The indication that the chosen CI is initiated, created or brought into existence by another CI, highlighting a relationship where the selected CI is the result of an instantiation process initiated by the specified CI. Example: Virtual machine can be instantiated by a hypervisor, indicating that the hypervisor creates and manages the VM.
IP Connection
IP connection of the selected CI
Selected CI has IP Connection to this CI
This CI has an IP connection to another CI, highlighting a relationship where the selected CI is connected to the specified CI through an IP-based network connection. Example: Web services can have an IP connection to a load balancer distributing incoming traffic among multiple instances of the service.
Contains Room
Contains room for selected user
Selected CI has room
Provides a room intended for a specific user, highlighting a relationship where the selected CI encompasses a physical space designated as a room for the specifies user.
Zone contains
Zone contains for selected CI
Selected zone contains the selected CI
A specific zone or area, highlighting a relationship where the selected zone encompasses or contains the specified CI.
Managed by
Is managed by the selected user
Selected CI depends on this CI
The management or oversight of a specific user, highlighting a relationship where the selected CI relies on the specified user for administration, control or maintenance. Example: Network device management is managed by a network engineer, indicating that the engineer is responsible for its configuration and operation.
Stack Member of
Stack member of the selected CI
Selected Stack member of the selected CI
The chosen CI is a member or component of a larger stack or assembly represented by the selected CI. This relationship highlights that the selected CI is part of the specified stack or grouping. Example: Automation frameworks can be stack member within an automation framework, highlighting that the module is part of the framework’s functionality.
Owned by
Is owned by the selected CI
Selected CI is owned by this CI
This attribute indicates that the chosen CI is owned or possessed by a specific entity, user, or group represented by the selected CI. This relationship highlights that the selected CI is under the ownership or responsibility of the specified owner. Example: Digital Assets ownership is ow
Powered by
Is powered by the selected CI
Selected CI is powered by this CI
The chosen configuration is powered or energized by another CI, highlighting a relationship where the selected CI relies on the specified CI for the necessary power source or energy supply. Example: Data centers servers are powered by uninterruptible power supplies to ensure continuous operation during power outages.
Provides
Provides the Selected CI
Selected CI has been provided on to this CI
The attribute indicates that the chosen CI offers a specific service, capability or resource to another CI, highlighting a relationship where the selected CI serves as a source of provision for the specified CI. Example: API Provider, provides access to certain functionalities for a software application, allowing the application to interact with those functionalities.
Stored on
Is stored on for the selected CI
Selected CI has been stored on to this CI
Logically stored on another CI, highlighting a relationship where the selected CI is located, hosted or saved on the specified CI. Example: Data storage is stored on a hard drive indicating that the file's data is physically stored on the drive.
Provisioned
Provisioned to the selected user
Selected CI depends on this CI
Allocated or prepared for a specific user, system or entity, highlighting a relationship where the selected CI relies on the provisioning CI for its availability and operation. Example: Resources in cloud, Cloud resources like storage volumes are provisioned by a cloud service provider, allowing users to allocate and manage resources.
Sends data to
Sends data to the selected user
Selected CI sends data to the CI
The chosen CI sends data, information or communication to another CI, highlighting a relationship where the selected CI transmits data to the specified CI. Example: Machine-to-Machine Communication in a production line send production data to a control system, facilitating process monitoring.
Has registered
Has Registered for the selected CI
Selected CI has been registered on this CI
The chosen Configuration Item has been registered or recorded on another CI, highlighting a relationship where the selected CI is associated with or documented on the registering CI. Example: Software License has been registered with a licensing server, enabling the authorized use of the software.
Receives Traffic
Receives traffic for the selected CI
Selected CI received traffic on this CI
This attribute receives incoming data, communication, or activity, usually in the form of network traffic or interactions, from another source or CI. This relationship highlights that the selected CI is a target for incoming traffic. Example: Email Server receives incoming emails from other email servers or clients for distribution to recipients.
Runs On
Runs on by the selected user
Selected CI depends on this CI
The chosen Configuration Item is executed or operated on another CI, highlighting a relationship where the selected CI relies on the specified CI for its functioning or operation. Example: Automation script runs on an automation platform, executing the scripted tasks and workflows.
Receives Data From
Receives from the selected user
Selected CI depends in this CI
This attribute indicates that the chosen Configuration Item receives data, information, or communication from another source or CI, highlighting a relationship where the selected CI depends on the specified CI to provide data or input. Example: IoT Data exchange is a central data hub receives data from multiple IoT devices for storage and analysis.
Submitted by
Is submitted by the selected user
Selected CI depends on this CI
This attribute indicates that the chosen Configuration Item has been submitted or provided by a specific user or entity, highlighting a relationship where the selected CI relies on the submitting CI for its creation, input, or initiation. Example: Change Requests is submitted by a stakeholder initiating a formal request for changes to a system or process.
Subscribed by
Is subscribed by the selected user
Selected CI depends on this CI
This attribute indicates that the chosen Configuration Item is subscribed to or followed by a specific user, entity, or system, highlighting a relationship where the selected CI depends on the subscribing CI for updates, notifications, or interactions. Example: Email Subscriptions, an email newsletter is subscribed to by a user, receiving regular updates and content.
Supported by
Is supported by the selected user
Selected CI depends on this CI
The chosen Configuration Item is supported, maintained, or provided assistance by a specific user, team, or entity, highlighting a relationship where the selected CI relies on the supporting CI for its maintenance, troubleshooting, or operational assistance. Example: Helpdesk Services, an IT helpdesk is supported by IT support agents, providing technical assistance to users.
Use End Point From
Use End Point from the selected CI ,
Selected CI depends on this CI
Indication that the chosen Configuration Item utilizes or accesses an endpoint provided by another CI, highlighting a relationship where the selected CI relies on the specified CI's endpoint for its functionality or data exchange. Example: Data Source, a dashboard application uses a data endpoint from a database server to fetch and display real-time data.
Uses
Uses the selected CI
Selected CI has been Used on to this CI
The chosen Configuration Item is utilized, employed, or incorporated by another CI for its functionality, operation, or capabilities. This relationship highlights that the selected CI is a component or resource used by the using CI. Example: Network device, a network switch uses network cables to establish connections.
Virtualizes
Virtualizes the selected CI
Selected CI has been virtualized on to this CI
Indication that the chosen Configuration Item is subjected to virtualization, transforming it into a virtual representation that operates within a virtual environment. This relationship highlights that the selected CI has been virtualized on the specified virtualization platform. Example: Cloud Computing, a cloud provider’s infrastructure) virtualizes resources like compute, storage, and networking (selected CI) for cloud services.
Name
Parent
Child
Description
Written By
Switch calendar view
Displays meetings in a month-wise calendar format.
Week
Switch calendar view
Displays meetings in a week-wise calendar format.
Day
Switch calendar view
Displays meetings in a day-wise calendar format.
List
Switch calendar view
Displays meetings in list format.
Microsoft Teams
Access Teams options
Provides access to Microsoft Teams-related options when enabled.
Meeting Started
Apply filter
Displays meetings that are currently in progress.
Meeting Completed
Apply filter
Displays meetings that have ended.
Meeting Title
Filter meetings
Filters meetings based on the meeting title.
Attendee Email
Filter meetings
Filters meetings based on the attendee email address.
VC Location
Filter meetings
Filters meetings based on the selected VC location.
Location / Regions
Filter meetings
Filters meetings based on the selected location or region.
Meeting Type
Filter meetings
Filters meetings based on the configured meeting type.
Associate With
Filter meetings
Filters meetings based on the module or record associated with the meeting.
Gray
Completed
Red
Cancelled
Schedule Type*
Select schedule type
Defines how the meeting is scheduled. This field is mandatory.
Available Options: One Time and Recurring.
Start Time*
Select start date and time
Specifies when the meeting starts. This field is mandatory.
End Time*
Select end date and time
Specifies when the meeting ends. This field is mandatory.
Meeting Type
Select meeting mode
Defines the type of meeting session.
Example: Web-Based Video Conference.
Meeting Link*
Enter meeting URL
Specifies the URL used to join the meeting. This field is mandatory.
Associate With
Select module or record
Associates the meeting with a supported module or operational record.
Participating VC Locations*
Select participating locations
Specifies the VC locations that will participate in the meeting. This field is mandatory.
Select all guest locations
Enable/disable toggle
Selects all available guest VC locations that match the selected regions.
Add a VC location manually...
Select VC location
Allows users to manually add a VC location.
Attendees Email
Manage attendee emails
Displays the number of selected attendee email addresses and lets attendees add from the available options.
Invite everyone from the selected VC locations
Enable/disable toggle
Invites everyone associated with the selected VC locations.
Add from EMS Directory
Select an email ID
Allows users to add an attendee by selecting an email ID from the EMS Directory.
Add an email ID manually
Enter email ID
Allows users to manually enter an attendee email address and add it to the meeting. Example:
Host Email
View host email
Displays the email address of the meeting host.
Host Phone
View host phone
Displays the meeting host's phone number, when available.
Meeting Contact Person
Enter contact details
Specifies the person invitees can contact on the day of the meeting.
Contact Person Name*
Enter contact name
Specifies the meeting contact person's name. This field is mandatory.
Contact Person Phone Number*
Enter contact phone number
Specifies the meeting contact person's phone number. This field is mandatory.
Schedule Meeting
Schedule meeting
Creates and schedules the meeting after you configure the required details.
Previous / Next
Navigate calendar
Moves to the previous or next month, week, or day based on the selected calendar view.
Add Meeting (+)
Create a new meeting
Opens the Add Meeting panel to schedule a new meeting.
Refresh
Refresh calendar data
Reloads the calendar and displays the latest meeting information.
View All
Apply filter
Displays all meetings.
Upcoming
Apply filter
Blue
Upcoming — web-based VC
Green
Upcoming — network-based VC
Amber
Title / Subject Line*
Enter meeting title
Specifies the name or subject of the meeting. This field is mandatory.
Example: Monthly review
Type
Select meeting type
Location / Regions*
Select regions
Selects the required regions. The selected regions filter the available participating VC locations and attendees.
Host VC Location*
Select host location
Meeting Host
View host details
Displays the meeting host details from the user's EMS profile.
Host Name
View host name
Agenda
Enter meeting agenda
Allows users to enter the meeting agenda or discussion details.
Attachment
Upload attachment
Hover over or focus on a meeting time to read the meeting subject.
Add Meeting
Meeting Details
Locations & Invitees
Selecting a region filters the available participating VC locations and attendees; it does not automatically select every matching location.
To select all matching guest locations, enable Select all guest locations. You can also select VC locations manually.
Attendees can be added from the EMS Directory or by entering an email ID manually.
Host & Contact Person
Invitation and reminder emails include the host and contact person details with their respective labels.
Agenda & Attachments
Mandatory fields are marked with an asterisk (*).
The meeting start time must be later than the current system time.
Month
Displays scheduled meetings that have not yet started.
In-Progress
Defines the meeting's purpose or category.
Specifies the VC location the meeting host uses.
Displays the meeting host's name.
Allows users to attach supporting documents or files related to the meeting.
Add Customer
Click to add
Opens the Add Customer sidebar to create a new customer with customer details, entities, roles, dashboards, and license allocation.
Customer Card
Click on card
Displays customer summary including:
Customer Name
Customer Code
Assets Count
Users Count
Edit
Click edit icon
Opens the selected customer in edit mode to update customer details, entities, or license allocation.
Delete
Click delete icon
Deletes the selected customer after confirmation.
Customer License
Click icon
Opens the Customer License Sidebar displaying allocated and used license counts per license type.
License Allocation
Unique reference code used for mapping and identification.
Example: AIR001
Domain
Enter domain name
Specifies the customer’s primary domain.
Example: airtel.com
Business Email
Enter official email
Used as the primary communication email for the customer.
Example:
Phone Number
Select country code and enter number
Contact number associated with the customer.
Example: +1 25********8
Website
Enter website URL
Official website of the customer.
Example:
Subscription ID
Enter subscription reference
Identifier for subscription or contract tracking.
Example: SUBAIR2026001
Is Active
Toggle On/Off
Enables or disables the customer in the system.
Location Name
Enter location name
Primary operational or registered location name.
Example: Airtel Corporate HQ
Country
Enter country
Country where the customer operates.
Example: United States
Region
Enter region
Regional classification within the country.
Example: North America
State
Enter state
State of the customer location.
Example: New York
District
Enter district/county
County within the state (if applicable).
Example: New York County
City
Enter city
City of the customer location.
Pin Code
Enter postal code
ZIP code of the location.
Example: 10036
Landmark
Enter nearby landmark
Reference point near the customer location.
Example: Near Bryant Park
Flat, House No., Building, Company
Enter address line 1
Primary address details.
Example: 1095 Avenue of the Americas
Allows you to search customers by Customer Name or Customer Code.
Filter
Click to apply filters
Customer Name *
Enter customer name
Defines the customer identifier within the organization.
Example: Airtel
Code *
Full Logo
Upload image file (Drag & Drop or Browse)
Upload the complete company logo displayed on the top-left of the application (expanded menu) and in exported documents.
Recommended Size: 320 × 80 pxFormats: png, jpeg, jpg (Max 20 MB)
Logomark / Icon
Upload image file (Drag & Drop or Browse)
What you see on the screen
Add Customer
Fields marked with an asterisk (*) are mandatory and must be completed before proceeding.
Filters customers using:
Fields: Customer Name and Customer Code
Conditions: in, not in, equal to, not equal to, contains, and not contains.
Enter unique customer code
Upload the compact logo icon displayed when the side menu is collapsed.
Define the process by adding a suitable name. For example, “Adding asset.”
Description
Provide a brief description of the add process.
Once all the details are filled correctly, click Save.
The following IMACD process will be created successfully.
In the Infraon platform, navigate to the IMACD module.
Click on the Add process -> Move, located at the top right corner of the page.
Enter the respective call-out boxes.
Move IMACD | Fields
Label
Action
Description/Example
Process Name
Add a necessary name to the process.
Define the process by adding a suitable name. For example, “Moving IT team’s systems.”
Description
Once all the details are filled correctly, click Save.
The following IMACD process will be created successfully.
When the Move process reaches the "Waiting for Approval" state, users are restricted from selecting or printing the Gate Pass template.
The Gate Pass can only be printed once the process is approved. After approval, the Gate Pass will display the approver’s name for validation.
A Verification button is available directly within the grid. Approvers or reviewers can use this button to verify and approve the Move process without navigating to a separate page.
When a move request is approved, the asset status is automatically updated as per the configured lifecycle.
Once the asset is delivered, the issuing user can acknowledge receipt from the system.
After a successful move or IMACD installation, the asset’s location field is automatically updated to the new location.
For gate passes, the Infraon logo is shown by default; if the organization has uploaded a custom logo, that logo is used on the printed gate pass.
In the Infraon platform, navigate to the IMACD module.
Click on the Add process -> Add, located at the top right corner of the page.
Enter the respective call-out boxes.
Install IMACD| Fields
Label
Action
Description/Example
Name
Add a necessary name to the process.
Define the process by adding a suitable name. For example, “Adding asset.”
Description
Once all the details are filled correctly, click Save.
The following IMACD process will be created successfully.
In the Infraon platform, navigate to the IMACD module.
Click on the Add process -> Change, located at the top right corner of the page.
Enter the respective call-out boxes.
Change IMACD| Fields
Label
Action
Description/Example
Process Name
Add a necessary name to the process.
Define the process by adding a suitable name. For example, “Moving IT team’s systems.”
Description
Once all the details are filled correctly, click Save.
The following IMACD process will be created successfully.
In the Infraon platform, navigate to the IMACD module.
Click on the Add process -> Destroy, located at the top right corner of the page.
Enter the respective call-out boxes.
Change IMACD| Fields
Label
Action
Description/Example
Process Name
Add a necessary name to the process.
Define the process by adding a suitable name. For example, “Moving IT team’s systems.”
Description
Once all the details are filled correctly, click Save.
The following IMACD process will be created successfully.
Installation
Move
Workflow Configuration
Approval State Restriction
Verification
Asset Status
Addition
Change
Destroy
Purchase Requisition Properties | Basic Details
The Purchase Requisition Properties tab is used to configure PR information, contract references, vendor details, requester information, and procurement-related configurations before adding line items and submitting the PR.
Label
Action
Description / Example
PR Information
Title
Click Next to proceed to the Item Details tab for configuring line items, procurement costs, and related item information.
Item Details | Basic Details
The Item Details tab is used to add and manage line items associated with the Purchase Requisition. Users can configure procurement-related item information required for the procurement process.
The Item Details section allows users to configure:
Item Name
Item Type
Category and Sub-Category
Quantity
Unit Cost
Tax Rate and Tax Amount
Loaded Cost
Conversion Factor
Consignment Details
Order Unit
Model Details
Commodity Code
Vendor-related Item Details
based on field configuration and RBAC permissions
Users can:
Add line items manually using the + Add Item option
Upload multiple line items using the Upload as CSV option
Download a predefined CSV template using the Download Sample CSV option
Configure visible line item columns based on permissions and field configurations
View calculated values such as Subtotal, Tax, and Grand Total
After configuring the required line item details, click Next to proceed to the Terms and Conditions tab.
Terms and Conditions | Basic Details
The Terms and Conditions tab is used to configure shipping details, billing information, and procurement terms associated with the Purchase Requisition. Users can define delivery addresses and apply predefined terms and conditions required for procurement processing.
Label
Action
Description/ Example
Shipping Address
Enter the shipping address details
Specify the delivery address for the requested items.
Example: Infraon Technologies, Bangalore Office, 5th Floor, MG Road, Bengaluru – 560001
Billing Address
Enter the billing address details
Once all required details are configured, click Submit to complete the Purchase Requisition.
Fields marked with an asterisk (*) are mandatory and must be completed before proceeding.
To create and configure custom fields for Purchase Requisition,
Fields marked with an asterisk (*) are mandatory and must be completed before submitting the Purchase Requisition.
How does it work?
Assets must be added to Infraon to enable management. There are multiple ways to add assets.
Assets can be added directly from the Infraon asset module. Within the asset module, there are options to manually add an asset or add bulk assets using a .csv file.
Agent-based discovery initiated from the Infraon configuration module.
Assets can be viewed in Grid and card views. Clicking on the corresponding action icons in the assets allows you to scan and search for assets, export them, and perform maintenance actions.
Asset Details | Actions
The Actions menu lets you manage the selected asset. The available actions depend on the asset type, configuration, and user permissions.
Label
Action
Description / Example
You can archive an asset from the IT Assets or Fixed Assets page using the Archive Asset action. Archiving removes the asset from the active asset view and moves it to Archived Assets.
1
Open the asset page
Navigate to Assets and open IT Assets or Fixed Assets.
2
Locate the asset
Locate the asset that you want to archive.
3
Enter the required details in the Archive Asset sidebar.
Click Archive Asset to complete the process.
Archive Asset | Basic Details
Label
Action
Description / Example
Once the required details are entered, click Archive Asset. The asset is archived and moved from the active asset view to
When this setting is enabled, the system allows admins to define a custom asset ID structure for each asset category. The format can be tailored using prefixes, numeric values, and custom fields to meet organizational standards.
This format is applied automatically during asset creation, bulk upload, or discovery, ensuring each asset is uniquely and consistently identified.
Example Formats
#IT-LPT-0001
#ASSET00023
#ESOL-D-0038
You can configure this from the Category Template > tab.
Customize Asset ID Format | Field Reference
Multi-selection of assets is facilitated by clicking the checkboxes adjacent to each desired asset.
Add the required level of priority aligned to the process.
Priority can be chosen from Low, Medium, High, and Critical.
Assignee
Select from the drop-down box.
Name of the user to whom the task is assigned.
Location
Select the location from the drop-down box.
Note: If the desired location isn't listed in the dropdown, click "Add" to create a new entry.
Displays the location of the asset.
Add Asset
Add
Click to add the asset that needs the installation process.
Asset Type
Defined the type of asset whether to be IT or fixed asset.
Asset Category
Category is the first division of assets within the selected asset type. For example, within IT assets, there can be categories like laptops, desktops, etc.
Asset Details
Displays the asset name of the asset selected.
Comment
Click to add a comment about the asset.
Example: Handle with care.
Save
Click to save the process.
The following details will get saved once clicked.
Provide a brief description of the movement process.
Relocation of the user’s workstation from the Head Office to the Branch Office.
Priority
Add the required level of priority aligned to the process.
Priority can be chosen from Low, Medium, High, and Critical.
Assignee
Select from the drop-down box.
Name of the user to whom the task is assigned.
Address Details
Source Address
Select the required address from the drop-down menu below or click 'Add' to enter a specific address manually.
The designated address at which the package is to be retrieved.
Add Location
Click Add (+) next to the Source Address field and enter the required location details.
Allows users to manually add a new location to be used as the Source Address for the IMACD Movement. Enter details such as Location Name, Country, Region, State, District, City, Pin Code, Landmark, Address, Description, Latitude, and Longitude.
The newly added location can then be selected as the Source Address.
Filter by Default for Asset of Source Location
Select the required asset from the list.
Automatically filters and displays assets associated with the selected Source Address.
Example: When Bangalore Office is selected as the Source Address, only the assets associated with that location are displayed for selection.
Add Asset
Add
Click to add the asset that needs the installation process.
Choose or attach the asset(s) involved in the move from the asset inventory.
Example: Dell Latitude 5530 – Asset ID: AS10045
Comment
Click to add a comment about the asset.
Add additional notes or special handling instructions for the move.
Example: Handle with care – includes sensitive hardware components.
Returnable
Checkbox
Enable this checkbox if the asset is intended for temporary relocation and will be returned later.
Once checked, a Return Date field appears, specifying the date by which the asset is expected to be returned.
Example: Checked for temporary laptop loan, return date: October 15, 2025.
Save
Click to save the process.
The following details will be saved once clicked.
Provide a brief description of the add process.
Number of Assets
Specify the number of assets to be added (numeric value).
Example: 4,5, etc.
Priority
Add the required level of priority aligned to the process.
Priority can be chosen from Low, Medium, High, and Critical.
Assignee
Select from the drop-down box.
Name of the user to whom the task is assigned.
Location
Select the location from the drop-down box.
Note: If the desired location isn't listed in the dropdown, click "Add" to create a new entry.
Displays the location of the asset.
Save
Click to save the process.
The following details will get saved once clicked.
Provide a brief description of the movement process.
Priority
Add the required level of priority aligned to the process.
Priority can be chosen from Low, Medium, High, and Critical.
Assignee
Select from the drop-down box.
Name of the user to whom the task is assigned.
Location
Select the location from the drop-down box.
Note: If the desired location isn't listed in the dropdown, click "Add" to create a new entry.
Displays the location of the asset.
Add Asset
Add
Click to add the asset that needs the installation process.
Asset Type
Defined the type of asset whether to be IT or fixed asset.
Asset Category
Category is the first division of assets within the selected asset type. For example, within IT assets, there can be categories like laptops, desktops, etc.
Asset Details
Displays the asset name of the asset selected.
Comment
Click to add a comment about the asset.
Example: Handle with care.
Save
Click to save the process.
The following details will get saved once clicked.
Provide a brief description of the movement process.
Priority
Add the required level of priority aligned to the process.
Priority can be chosen from Low, Medium, High, and Critical.
Assignee
Select from the drop-down box.
Name of the user to whom the task is assigned.
Location
Select the location from the drop-down box.
Note: If the desired location isn't listed in the dropdown, click "Add" to create a new entry.
Displays the location of the asset.
Add Asset
Add
Click to add the asset that needs the installation process.
Asset Type
Defined the type of asset whether to be IT or fixed asset.
Asset Category
Category is the first division of assets within the selected asset type. For example, within IT assets, there can be categories like laptops, desktops, etc.
Asset Details
Displays the asset name of the asset selected.
Comment
Click to add a comment about the asset.
Example: Handle with care.
Save
Click to save the process.
The following details will get saved once clicked.
Select Archive Asset
In Grid View or Card View, open the Actions menu for the asset.
Select Archive Asset.
4
Enter archive details
Enter the required details in the Archive Asset sidebar.
5
Archive the asset
Click Archive Asset to complete the process.
Change the Status of the assets.
Edit the Location
Enable/ Disable
Delete multiple assets at once.
Diagnose
Mask Alarms
Unmask Alarms
Maintenance
Change category
Label
Action
Description/ Example
Search
Search for the required asset.
Filter
Filter can be added based on the field (Card name, card type, device IP, part number, and serial number) and condition from the drop-down box below.
Edit
Click Edit to modify the asset.
Opens the asset details in edit mode.
Delete
Click Delete to remove the asset.
Archive Reason*
Select from the drop-down.
Select the reason for archiving the asset.
Available options: Disposed, Retired, Inactive Asset, Etc.
Archive Notes
Enter additional information, if required.
Label
Action
Description / Example
Preview Section
View-only
Shows a live preview of how the Asset ID will look once generated.
Example: #ASSET-0001
Prefix
The actions available in the menu may vary based on the asset type and the permissions assigned to the user.
Archive an Asset
To archive multiple assets, select the required assets using the selection checkbox. Once one or more assets are selected, click Archive Asset from the selection toolbar.
Archive Reason is mandatory. You cannot archive the asset until you select a reason.
Customize Asset ID
Ensure that the "Customized Asset Id" field is selected in the Fields tab of the category template.
Once saved, the format is automatically applied to all assets created under the configured category.
Used to provide the title or summary for the Purchase Requisition.
Example: Laptop Procurement for the IT Team.
Currency
Select a currency from the dropdown
Used to define the transaction currency for the Purchase Requisition.
Example: USD, INR, or EUR.
Status
Select a workflow status from the dropdown
Displays and manages the Purchase Requisition's current workflow state.
Example: Draft, Waiting for Approval, or Approved.
Status Date
Select the date
Displays the current workflow status date associated with the Purchase Requisition.
Example: 21 May 2026.
Priority
Select the priority from the dropdown
Used to define the priority level of the Purchase Requisition.
Example: Low, Medium, High, or Critical.
Location
Select a location from the dropdown
Used to associate the Purchase Requisition with a specific branch or operational location.
Requested By
Select a requester from the dropdown
Used to define the user requesting the Purchase Requisition.
Requested Date
Select the requested date
Used to define the date on which the Purchase Requisition was requested.
Example: 20 Mar 2026.
Required Date
Select the required date
Used to define the expected procurement or delivery date for the requested items or services.
Example: 28 Mar 2026.
Reporting Manager
Select the reporting manager from the dropdown
Used to associate the requester’s reporting manager for approval or tracking purposes.
Description
Enter the description
Used to provide detailed information about the Purchase Requisition requirement.
Example: Procurement request for employee onboarding laptops and accessories.
Contract Reference
Contract Type
Select the contract type from the dropdown
Used to associate a contract category with the Purchase Requisition.
Example: AMC, Service Contract, or Procurement Contract.
Contract Reference
Select the contract reference from the dropdown
Used to map an existing contract reference associated with the Purchase Requisition.
Example: AMC-2026-001.
Contract Revision
Enter the contract revision
Used to define the revision version of the associated contract.
Example: Revision 2 or v1.1.
Vendor Details
Vendor
Select a vendor from the dropdown
Used to associate the vendor with the Purchase Requisition.
Example: Dell Suppliers, Cisco Distributor, or HP Vendor.
Payment Terms
Select payment terms from the dropdown
Used to define payment conditions associated with the Purchase Requisition.
Example: Net 30, Advance Payment, or Quarterly Payment.
Ship Via
Select the shipping method from the dropdown
Used to define the shipment or delivery method for the requested items.
Example: Courier, Air Freight, or Direct Delivery.
FOB Point
Enter the FOB point
Used to define the Freight On Board location or shipment transfer point.
Example: Bangalore Warehouse or Chennai Port.
Type
Select the requisition type
Used to define whether the Purchase Requisition is for internal or external procurement.
Example: Internal or External.
Pay Tax To Vendor
Enable or disable the toggle
Used to define whether applicable tax payments should be made directly to the vendor.
Pay On Receipt
Enable or disable the toggle
Used to define whether payment should be processed upon receiving the requested items or services.
Inspection Required
Enable or disable the toggle
Used to define whether the requested items require inspection before approval or acceptance.
Next
Click Next
Cancel
Click Cancel
Cancels the Purchase Requisition creation process without saving changes.
Specify the billing or invoice address associated with the Purchase Requisition.
Same as Shipping Address
Check to copy the shipping address into the billing address field
Automatically copies the Shipping Address details into the Billing Address field.
Terms and Conditions
Select the required terms and conditions from the drop-down
Used to apply predefined procurement terms for the Purchase Requisition. to configure Terms and Conditions.
To scan and search for an asset, click on the 'Scan and search asset' option, then use your phone to scan the QR code, which will initiate the asset search process.
Export
Click to choose the category.
To export the data, click the 'Export' button, then choose the desired category, and finally download the CSV file containing the selected data.
Maintenance
Click to redirect to the Maintenance page.
When an asset is designated for maintenance, its status is changed to the "maintenance" stage. After scheduling the maintenance time, the asset is set to run automatically during that scheduled period. Once the maintenance is completed, the asset reverts back to its previous state, resuming normal operations or the state it was in prior to the maintenance activity.
Bulk Edit
Go to the Infraon Asset Card page -> Actions -> Bulk Edit.
Select the Category.
Download the CSV file (excel sheet) and Enter the Asset details in the sheet.
Upload the same edited CSV file.
Click Next -> Import -> Proceed with Valid Records.
To Edit Multiple Assets information or details at once.
Download Agent
Click to download the Infraon agent available on Windows, MAC, and Linux.
Customize Asset ID
To customize the Asset ID configuration.
RDP Session Audit
View RDP session details.
Opens the RDP Session Audit window for the selected asset. Users can view a list of RDP sessions, including the remote device name, protocol used, session start and end times, total duration, and the recorded session file size.
The page also shows the total storage size occupied by the recorded sessions.
Deletes the selected asset after confirmation.
Add Owner
Click Add Owner to assign an owner.
Allows you to assign an owner to the selected asset.
Archive Asset
Click Archive Asset to archive the asset.
Moves the asset from active asset management to Archived Assets.
CLI Session
Click CLI Session to start a CLI session.
Opens a CLI session for supported assets.
Add any additional information or context related to the archival.
Example: The asset was replaced with a new laptop and is no longer in use.
Enter text manually
Define a static prefix that appears before the numeric or alphanumeric value.
Example: ASSET, ESOL, IT-LPT
Add Field (Custom Format)
Click to add fields
(Optional) Add dynamic components like location code or department manually.
Number Type
Select from the dropdown
Choose how the numeric part of the ID should be generated.
Options:
· Auto Increment: Sequential numbers (e.g., 0001, 0002)
· Alpha Numeric: Mix of letters and numbers (e.g., IT01A)
· Random: Generates a randomized unique value (e.g., X23B)
No of values
Select from the dropdown (1–10 digits)
Define the length of the numeric part.
Example: 4 creates IDs like 0001, 0002, etc.
Starting From
Enter a numeric value
Sets the starting number for the ID sequence.
Example: 1 generates 0001, 0002...
A Purchase Requisition (PR) is used to formally request the procurement of items or services required for business operations before a Purchase Order is created. It helps organizations track, review, approve, and manage procurement requests through a structured workflow.
For example, an employee can submit a Purchase Requisition to request laptops, software licenses, networking devices, office equipment, or vendor services. Once submitted, the PR moves through the configured approval workflow before proceeding to the procurement or Purchase Order stage.
It is commonly used for:
Hardware procurement requests
Software or license requests
Vendor service requests
Office and operational purchases
Internal approval-based procurement processes
Unlike a which is issued to a vendor to confirm procurement, a Purchase Requisition is an internal request used for approval and procurement planning before the actual purchase process begins.
A Purchase Requisition follows a workflow-driven process in which each PR moves through predefined stages based on the configured and approval conditions. Users can create PRs, add line items, configure vendor and address details, submit the PR for approval, and track the approval status from the PR view page.
Workflow Stages | Purchase Requisition
Label
Description / Example
The Purchase Requisition page displays all created PR records in a grid view. Users can search, filter, create, edit, delete, and manage Purchase Requisitions. The page also provides quick access to PR details, including priority, requested date, total amount, workflow status, and vendor information.
Purchase Requisition | Basic Details
Label
Action
Description/ Example
Custom Field
Custom Fields allow IT admins to create and manage asset-specific metadata fields that go beyond the default system-defined attributes. These fields enable teams to tailor asset records to suit organizational, compliance, or operational needs.
It is designed to support:
Organization-specific field tracking (e.g., Warranty Location, Department Tag, Device Owner Remarks)
Flexibility in defining Text, Date, Dropdown, or Numeric fields
CI relationship in CMDB Downstream
Rejected
Indicates that the PR has been rejected during the approval process. Users can review and modify the PR if required.
Closed
Final stage of the Purchase Requisition lifecycle, indicating that the PR process is completed successfully.
Used to apply advanced filter conditions based on PR fields such as Status, Priority, Vendor, Workflow State, or custom fields.
Date Range
Select a date range
Used to filter Purchase Requisitions based on selected date ranges such as Today, Last 7 Days, Last Month, or custom date ranges.
Line Item Column Selection
Click Actions and configure columns
Used to configure and manage visible line item columns such as Item Name, Quantity, Unit Cost, Tax Amount, and custom fields based on RBAC permissions.
Add Purchase Requisition
Click + Add Purchase Requisition
Opens the Purchase Requisition creation page to add a new PR, including vendor, line items, addresses, and terms and conditions.
Column Details
Purchase Requisition ID
Click to open in the view page
Displays the unique Purchase Requisition ID.Example: PR0002. Clicking the ID opens the detailed PR view page.
Title
View only field, no actions can be taken
Displays the configured title or summary of the Purchase RequisitionExample: "Laptop Procurement Request" or "Networking Device Purchase".
Requested By
View only field, no actions can be taken
Displays the name of the user who created or submitted the Purchase Requisition.
Requested Date
View only field, no actions can be taken
Displays the date on which the Purchase Requisition was created or submitted.
Required Date
View only field, no actions can be taken
Displays the expected procurement or delivery date configured for the Purchase Requisition.
Priority
View only field, no actions can be taken
Displays the configured priority level of the Purchase Requisition.Available Options: Low, Medium, High, or Critical.
Total Amount
View only field, no actions can be taken
Displays the total calculated amount of all configured line items in the Purchase Requisition.
Status
View only field, no actions can be taken
Displays the current workflow status of the Purchase Requisition
Available Options: Draft, Waiting for Approval, Approved, Rejected, or Closed.
Vendor
View only field, no actions can be taken
Displays the mapped vendor associated with the Purchase Requisition.
Locations
View only field, no actions can be taken
Displays the configured branch, office, or operational location associated with the Purchase Requisition.
Edit
Click the edit icon
Opens the selected Purchase Requisition in edit mode to modify details, such as line items, vendor details, addresses, or workflow-related information, subject to permissions.
Delete
Click the delete icon
Deletes the selected Purchase Requisition from the system, subject to delete permissions and workflow restrictions.
Draft
The initial stage is when the Purchase Requisition is created and saved, including PR details, vendor details, line items, and terms and conditions.
Waiting for Approval
Indicates that the PR has been submitted for approval and is awaiting action from the configured approver or approval team.
Approved
Search
Enter keywords to search PR records
Used to search Purchase Requisitions using keywords such as PR0002, vendor name, requester name, or PR title.
Indicates that the PR has been approved successfully based on the configured workflow and approval conditions.
Click the filter icon to apply conditions
Author of the selected CI
Selected CI is written by this CI
The attribute pertains to the authorship of a selected CI
Backed up by
Back up of the selected CI
Is backed up by the Selected CI
This feature refers to the backup status of a chosen CI
Cluster of
Belongs to the cluster of the selected CI
Belongs to the cluster of the selected CI
This signifies the membership of a chosen CI within a specific cluster.
Connected by
Selected CI is connected by this CI
Connected by the selected user
Indication that the chosen CI is connected by another CI or user, highlighting a relationship where the selected CI is linked or associated with the connecting CI or user. Example: Internet Connection, a smartphone is connected by a cellular network, providing access to the internet.
Connected to
Selected CI is connected to this CI
Connected to the selected CI
Showcases a connection or relationship between the two components. For example: IoT, the connected to field for the bulb would display the hub’s name.
Consists of
Selected CI consists of this CI
Consists of selected CI
This indicates that the chosen Configuration Item is composed of or includes another CI as its component or part, highlighting a relationship where the selected CI is made up of the specified component CI. Example: Data model, a database schema consists of tables, relationships, and attributes that define the data structure.
Consumed by
Selected CI is consumed by this CI
Consumed by the selected CI
This attribute indicates that the chosen Configuration Item is consumed or utilized by another CI or process, highlighting a relationship where the selected CI is a resource, input, or service used by the consuming CI. Example: Service Dependency, a micro service is consumed by another micro service in a micro services architecture.
Attached by
Selected CI contains this CI
Is attached by the selected CI
This attribute indicates that the chosen Configuration Items attached, linked, or associated with another CI, highlighting a relationship where the selected CI is connected or added as a component or part to the attaching CI.Collaborative Document contains an attached comment thread for discussions.
Contains
Selected CI contains this CI
Contains the selected CI
Indication that the chosen Configuration Item includes, encompasses, or holds another CI as a part, component, or element, highlighting a relationship where the selected CI acts as a container for the contained CI. Example: Database Table contains multiple tables that store structured data.
Cools
Selected CI cools this CI
Cools the selected CI
The attribute indicates that the chosen Configuration Item functions to cool, dissipate heat, or regulate temperature for another CI, highlighting a relationship where the selected CI plays a role in maintaining the temperature of the cooled CI.
Defines Resources for
Selected CI defines resources for this CI
Define Resources for the selected CI
The chosen Configuration Item establishes, specifies, or sets resources, capabilities, or allocations for another CI, highlighting a relationship where the selected CI provides resource definitions or guidelines to the CI it defines resources for. Example: Cloud Resource Configuration defines resources like virtual machines and storage for a cloud deployment.
Depends on
Selected CI depends on this CI
Depends the selected user
This attribute indicates that the chosen Configuration Item relies on or has a dependency on another CI or user, highlighting a relationship where the selected CI requires the support, functionality, or input of the depending CI or user to operate effectively. Example: Network Connectivity, a printer depends on network connectivity to receive print jobs from users.
Distributed by
Selected CI is distributed
Is distributed by the selected CI
The chosen Configuration Item is distributed or made available to others by another CI, entity, or user, highlighting a relationship where the distributing CI facilitates the dissemination or availability of the selected CI. Example: Newsletter Dissemination. An email newsletter is distributed by a company to its subscribers.
DR provided by
Selected CI's DR (Disaster Recovery) is provided by this CI
DR provided by the selected CI
The chosen Configuration Item serves as the source or provider of Disaster Recovery capabilities for another CI, highlighting a relationship where the providing CI ensures the availability of recovery mechanisms in the event of a disaster affecting the selected CI. Example: Data archival system ensures disaster recovery by storing historical data for compliance and recovery purposes.
Editor
Editor of the selected CI
Edited by the selected user
Indication that the chosen Configuration Item is associated with an entity or user who is responsible for making edits, modifications, or updates to the content, settings, or configuration of the selected CI. This relationship highlights the role of the editor in managing changes to the selected CI. Document Editor: An editor is responsible for editing and revising a document (selected CI) to improve its content.
Enables
Enables the selected CI
Is enabled by the selected CI
This attribute indicates that the chosen Configuration Item empowers or allows the functionality, operation, or capabilities of another selected CI. This relationship highlights the role of the enabling CI in providing necessary support or resources for the enabled CI. Example: An API enables developers to interact with software components programmatically.
Exchanges
Selected CI exchanges information with the selected CI
Exchanges information with the selected CI
Indication that the chosen Configuration Item is involved in a two-way exchange of information, data, or communication with another selected CI. This relationship highlights the active communication and interaction between the two CIs. Data Synchronization: Two databases exchange data updates to ensure consistency between them.
Exchanges data with
Selected CI exchanges data with this CI
Exchanges data with the selected CI
The attribute indicates that the chosen CI shares or transfers data with another CI, highlighting a relationship where both Cis interact to exchange specific data or information. Example: API Communication A web application can exchange data with a third-party API to retrieve external information or perform specific actions.
Feeds
Selected CI feeds this CI
Is fed by the selected CI
The chosen Configuration Item provides data, information, resources, or inputs to another CI, highlighting a relationship where the selected CI serves as a source or supplier of essential elements to the fed CI. Example: Sensor Data in a smart home feed data on temperature, humidity, and occupancy to a central control system.
From template
Selected CI has this CI
From template for selected CI
The indicates that the chosen Configuration Item is derived, created, or instantiated from a specific template CI, highlighting a relationship where the selected CI is based on or follows the structure, configuration, or guidelines provided by the template CI. Example: Software codebase is developed following a coding template for coding standards and best practices.
Has Registered
Selected CI has been registered to this CI
Has registered on the selected user
The chosen Configuration Item has been registered or recorded on another CI, highlighting a relationship where the selected CI is associated with or documented on the registering CI. Example: Software License has been registered with a licensing server, enabling the authorized use of the software.
Hosted on
Selected CI has been hosted on to this CI
Hosted on the selected CI
This attribute indicates that the chosen Configuration Item is hosted, deployed, or run on another CI, typically a server or computing environment. This relationship highlights that the selected CI relies on the hosting CI for execution and resources. Example: Cloud Service Hosting is hosted on a cloud provider’s infrastructure for scalability and availability.
Impacted By
Selected CI is impacted by this CI
Impacted by the selected CI
The chosen Configuration Item is affected, influenced, or impacted by another CI, event, or factor, highlighting a relationship where the selected CI's functioning, state, or performance is influenced by the impacting CI or event. Example: Network Outage, a server is impacted by a network outage causing loss of connectivity.
Implement End Point To
Selected CI is implemented the endpoint from this CI
Implement the endpoint from the selected CI
Indication that the chosen Configuration Item has implemented an endpoint from another CI, implying that the selected CI has established a connection, interface, or access point to the endpoint CI. Example: IoT Device Interaction, a smart home controller implements endpoints from various IoT devices to control and monitor them.
In Rack
Selected CI has been in rack to this CI
In Rack contains the selected CI
The chosen Configuration Item is physically located within or housed in a specific rack or rack unit. This relationship highlights the physical placement of the selected CI within the specified rack. Example: Storage system are installed in storage racks for data storage and retrieval.
Includes
Selected CI has been included on to this CI
Includes the selected CI
The chosen Configuration Item encompasses or contains another CI as a component, feature, or part, highlighting a relationship where the including CI has the selected CI as an integral element. Example: Software Module, an application suite includes individual software modules that provide specific functionalities.
Instantiates
Selected CI has been instantiated on this CI
Instantiates the selected CI
This attribute indicates that the chosen Configuration Item has been created, initialized, or instantiated on another CI, typically a computing environment or platform. This relationship highlights the process of setting up and initiating the selected CI within the context of the instantiating CI. Example: Software execution, an application is instantiated on a user's device or computer to run and perform tasks.
IP Connection
Selected CI has IP Connection to this CI
IP connection of the selected CI
This attribute indicates that the chosen Configuration Item is linked or connected to another CI through an Internet Protocol connection, facilitating data transmission and communication between the two CIs. Example: Remote Access, a remote desktop application, uses IP connections to allow remote access to a host computer.
Located In
Selected CI located in this CI
Located In for the selected CI
The chosen Configuration Item is physically situated within or positioned inside another CI, typically a larger or encompassing physical entity. This relationship highlights the spatial location of the selected CI. Example: Storage room, files are located in a storage room for safekeeping.
Located in Zone
Selected CI located in zone to this CI
Located In zone for the selected CI
This attribute indicates that the chosen Configuration Item is positioned within a specific zone or area, usually with defined boundaries or characteristics. This relationship highlights the spatial location of the selected CI within the context of the zone CI. Example: Medical zone, the Medical devices are located in a medical zone within a hospital.
Manages
Selected CI has been managed on to this CI
Manages the selected CI
The chosen Configuration Item is under the management, control, or supervision of another CI or entity. This relationship highlights the overseeing and administrative role of the managing CI over the selected CI. Example: Asset Management, an IT asset management system manages computers and devices by tracking their usage and status.
Master of
Selected CI has master of the selected CI
Master of the selected CI
This attribute indicates that the chosen Configuration Item serves as a master or primary entity in relation to another CI. This relationship highlights that the selected CI is governed, controlled, or derived from the master CI. Example: Master Configuration, a master configuration file, defines standard settings for software applications.
Owns
Selected CI has been owned on to this CI
Owns the selected CI
The chosen Configuration Item is owned, possessed, or controlled by another CI or entity. This relationship highlights the ownership and responsibility that the owning CI has over the selected CI. Example: Resource Ownership, a team owns a shared server and manages its access and usage.
Powers
Selected CI has been Powered on to this CI
Powers the selected CI
Indication that the chosen Configuration Item is a source of power that enables the operation or functionality of another CI. This relationship highlights the role of the powering CI in supplying the necessary energy for the selected CI. Example: Power adapter, powers a printer by converting electrical current.
Provided By
Selected CI depends on this CI
Provides by the selected user
This Configuration Item relies on or is supported by another CI or entity for specific resources, services, or functionalities. This relationship highlights the provider's role in offering what the dependent CI needs. Example: Network connection, an application depends on a network router to establish internet connectivity.
Provides storage for
Selected CI's storage is provided by this CI
Provides storage for the selected CI
This attribute serves as a source or provider of storage resources for another CI. This relationship highlights the role of the providing CI in supplying the storage capacity required by the dependent CI. Example: Storage Array provides high-performance storage for databases in an enterprise environment.
Provisioned From
Selected CI depends on this CI
Provisioned from the selected CI
The chosen Configuration Item is provisioned, set up, or derived from another CI or entity. This relationship highlights the source from which the selected CI is created or obtained. Example: Server blueprint, a physical server is provisioned from a server blueprint that defines hardware and software settings.
Receives data from
Selected CI depends in this CI
Receives data from the selected CI
This attribute indicates that the chosen Configuration Item receives data, information, or communication from another source or CI, highlighting a relationship where the selected CI depends on the specified CI to provide data or input. Example: IoT Data exchange is a central data hub receives data from multiple IoT devices for storage and analysis.
Registered on
Selected CI has been registered on this CI
Registered on the selected CI
Indicates that the chosen CI is registered or associated with a specific user, highlighting a relationship where the selected CI is linked to the specified user for identification or ownership purposes. Example: Software Licenses is registered on user’s account, indicating that the user has ownership rights to use the software.
Routes Traffic
Selected routes traffic depends on this CI
Routes Traffic for the selected CI
This attribute plays a role in directing or routing network traffic for another CI. This relationship highlights the routing capabilities of the routing CI and its influence on the path of traffic for the selected CI. Example: Router, routes network traffic between subnets and directs data packets for servers.
Runs
Initiated running for selected CI
Runs the selected CI
Configuration Item initiates or is responsible for the execution and operation of another CI. This relationship highlights the role of the running CI in starting and managing the functionality of the selected CI. Example: Web Server, a web server runs websites and serves web content to users.
Sends Data To
Selected CI sends data to selected CI
Sends data to selected CI
The attribute indicates that the chosen Configuration Item is capable of transmitting or forwarding data to another selected CI. This relationship highlights the ability of the sending CI to deliver information or data to the receiving CI. Example: Network device, a computer sends data to a printer for printing.
Submits
Selected CI has been submitted to this CI
Submits the Selected CI
This attribute indicates that the chosen Configuration Item is presented or provided to another CI or entity for a specific purpose, often involving approval, review, or processing. This relationship highlights the action of submitting the selected CI to the receiving CI. Example: Document Submission, an employee submits an expense report to the finance department for reimbursement.
Subscribes to
Selected CI depends on this CI
Subscribes to by selected user
The attribute indicates that the chosen Configuration Item is linked to or relies on another CI or entity for receiving updates, notifications, or information. This relationship highlights the act of subscribing to the source CI for relevant updates. Example: Software Updates, a system administrator subscribes to software updates for security patches.
Supports
Selected CI has been supporting to this CI
Supports the selected CI
The chosen Configuration Item provides assistance, help, or resources to another CI or entity. This relationship highlights the role of the supporting CI in aiding and assisting the supported CI. Example: Technical Support, a help desk provides technical support to resolve issues with software applications.
Use End Point To
Selected CI uses end point to this CI
Use End Point to the selected CI
The chosen Configuration Item leverages or interacts with another CI or entity as an endpoint to achieve a specific purpose. This relationship highlights the utilization of the endpoint CI to fulfill a particular function for the using CI. Example: Messaging Platform, a chatbot uses a messaging platform's endpoint to interact with users.
Used by
Selected CI is used by the this CI
Used by the selected user
This attribute indicates that the chosen Configuration Item is actively utilized, operated, or relied upon by another CI or entity. This relationship highlights the role of the using CI in utilizing the functionalities or resources of the selected CI. Example: Application Usage, a software application is used by end-users to perform tasks.
Virtualized by
Selected CI is virtualized by this CI
Virtualized by the selected CI
The chosen Configuration Item has been transformed into a virtualized instance by another CI or entity. This relationship highlights the role of the virtualizing CI in creating and managing virtual instances of the selected CI. Example: Desktop virtualization, virtualizes desktop environments for remote access.
Name
Parent
Child
Description
Author of
Reusability across different asset categories
Uniform data collection and visibility across modules like IT Assets, Fixed Assets, and CMDB
Custom Fields ensure that asset data models are scalable and relevant to different business environments.
Below is a detailed breakdown of the elements shown on the Custom Field listing screen:
Label
Action
Description / Example
Search
Type at least three characters to perform a search
Performs a free-text keyword search on custom field labels.
Example: Asset ID, Owner Group
Filter
Custom fields allow you to extend the default asset metadata by creating organization-specific attributes. These fields can be added to both Assets and Resources, with field type options and properties varying depending on the selection.
Begin by selecting the type of entity the custom field will be associated with:
Asset
Resource
Label
Action
Description / Example
Property
Select from the dropdown
Choose the property group the custom field belongs to.
Options: Common, Procurement, OS, CPU, BIOS, Disk, Monitor, Keyboard, Mouse, Cost, Assignment, etc.
Field Type
Select from the dropdown
Based on the selected Field Type, different configurations appear on the screen. See below for type-specific settings.
Label
Action
Description / Example
Field Type
Select from dropdown
Available options: Text, Phone Number, Email, and Number.
Label
Enter custom field label
Each field type triggers a specific form layout. Below is a detailed breakdown.
Based on the selected Field Type, additional configuration fields appear. Each type serves a unique purpose. The details below explain the labels and their usage in a clear format for end users.
Email / Phone Number / Text | Configuration
Field
Purpose
Placeholder
This is the default hint text displayed in the field before the user inputs any value. It auto-fills based on the field type (e.g., “Enter your email”) but can be edited to provide more specific guidance.
Validation Rules
This allows you to add descriptive text that instructs users on what type of input is expected. For example: “Must be a valid company email address.”
Regex
Number | Configuration
Field
Purpose
Min
Sets the minimum allowable value for the number field. This prevents users from entering values below the defined threshold.
Max
Sets the maximum allowable value. Useful for setting limits like asset quantity, license count, etc.
Validation Rule
Drop-down | Configuration
Field
Purpose
Label
Visible name for each dropdown option. Should be human-readable (e.g., “HR Department”).
Value
Backend reference for that label (e.g., HR01), used for automation, filters, and rules.
Action
Text Area | Configuration
Designed for long-form input (e.g., notes, remarks).
Uses the same configuration layout as Email/Text fields.
Best used for optional descriptions or unstructured inputs.
Checkbox / Radio | Basic Details
Field
Purpose
Label
The name shown to users for the option. Use clear wording like “Yes”, “No”, “Internal Use Only”, etc.
Value
This is the stored backend value for the label (e.g., “Y” for Yes, “N” for No). Used in reports and rule automation.
Date / Date & Time | Configuration
These types do not have field-specific validations like Min/Max or Regex.
A placeholder auto-fills with a default hint (e.g., "Select a date").
All common options (like category mapping, toggles for mandatory/unique) are applicable.
Custom fields can be linked to categories or sub-categories to determine their visibility and usage.
Option
Purpose
Common Custom Field
When enabled, this makes the field available across multiple selected categories. Best for generic fields like “Department” or “Asset Tag.”
Category/Sub-Category
Select the target group where the field should be active. Fields in a Category propagate to all sub-categories. Fields added only to a Sub-Category are restricted there.
Mandatory
What Do You See on the Screen?
All created custom fields will appear as selectable options in the Category Template > Fields tab.
Deleted fields cannot be recovered.
Fields are global and can be reused across multiple modules or templates.
Add a Custom Field
Duplicate field labels or property-field combinations are not allowed. Each custom field must be unique.
Steps to Add a Custom Field
If Asset is Selected
If Resource is Selected
Field Type-Based Configuration
Add Related Categories
Avoid using duplicate labels or field names across categories to maintain clarity and avoid conflicts.
Fields are global once created but are only active in the categories they are mapped to.
Select a field → choose a condition → enter value
Filter options include:
Fields: Label, Type
Conditions: equal to, not equal to, contains, not contain, in, not in
Example: Filter where Type = Text
Label
View only
Displays the name of the custom field.
Example: Customize Asset ID, Branch Code
Property
View only
Category this field belongs to (e.g., Custom Property, Procurement Property)
Field Type
View only
Data type assigned to the field.
Example: Text, Date, Dropdown, Email, etc.
Type
View only
Denotes the module or entity this field applies to.
Example: Asset, Contract, Software
All Related Categories
View only
Lists the number of asset categories using this custom field.
Example: 2, 3, etc.
Action Icons
Edit
Click pencil icon
Opens the custom field in edit mode to change label, field type, or related categories
Delete
Click trash icon
Deletes the custom field. This action is only allowed if the field is not in active use.
Choose the type of input expected for this field.
Options: Text, Phone Number, Email, Date, Date & Time, Checkbox, Radio, Text Area, Drop Down, Number.
Label
Enter custom field label
Example: Asset Location Code, Internal User Email, Device Category, etc.
Example: Resource Owner, Vendor Email
Enables admins to define pattern-based validation using regular expressions. This ensures that input strictly matches defined criteria (e.g., emails must follow abc@domain.com).
Error Text
This is the message shown to the user when the input fails validation. It should clearly explain what went wrong.
Example: “Please enter a valid email format.”
Optional message or description that informs the user what the number field is intended for or how to fill it.
Add multiple entries using "+" and remove using delete icon. Avoid duplicating labels/values.
Toggle this ON to enforce field entry during asset/resource creation.
Unique
Prevents duplicate values. Useful for fields like Serial Number, Asset ID, or Employee ID.
Disable
Temporarily hides the field from being used without deleting it.
Action Icons
Add
Confirms and applies the field-to-category association. You can add multiple mappings.
Delete
Removes the field from a specific category. Does not delete the field entirely.
Login Settings
Login Settings allows administrators to configure authentication methods, Single Sign-On (SSO), two-factor authentication (2FA), CAPTCHA validity, and login page customization. These settings help organizations manage user access and apply security requirements across the Infraon platform.
Standard Authentication
Standard Authentication provides three methods for users to sign in to Infraon: Username & Password Default, Mobile Number & SMS, and Email-Based 2FA. Administrators can configure the required authentication method and its settings based on the organization's security requirements.
Login Settings | Standard Authentication Methods
Label
Action
Allows users to sign in to Infraon using their registered email address and password. This is the default authentication method and is enabled by default. Users enter their credentials on the login page to access the application.
Configure an SMS gateway to send OTPs to users' registered mobile numbers. A primary SMS gateway is required, and a secondary gateway can be configured as an additional option.
Standard Authentication | Mobile Number & SMS Configuration
Email-based 2FA requires users to verify their identity using an OTP sent to their registered email address. When enabled, the system displays the email OTP verification screen after successful primary authentication.
To configure Email-Based 2FA, enable the option and open the configuration using the edit option. Configure the OTP settings and email template, then save the changes.
Standard Authentication | Email-Based 2FA Configuration
Single Sign-On (SSO) allows users to access the Infraon portal using an external identity provider instead of managing separate login credentials. Infraon supports Microsoft SSO, Google SSO, OpenID Connect (OIDC), Security Assertion Markup Language (SAML) SSO, Secure Pass SSO, and SSO Configuration.
Microsoft Single Sign-On (SSO) allows users to sign in to Infraon using their Microsoft accounts without entering separate Infraon credentials.
To configure Microsoft SSO, enable the option and configure the SSO Allowed Domains field to specify which email domains are permitted to sign in. Submit the changes to apply the configuration.
Google Single Sign-On (SSO) allows users to sign in to Infraon using their Google accounts without entering separate Infraon credentials.
To configure Google SSO, enable the option and configure the SSO Allowed Domains field to specify which email domains are permitted to sign in. Submit the changes to apply the configuration.
OpenID Connect (OIDC) is an authentication protocol that allows users to sign in to Infraon using an external identity provider. It verifies the user's identity and enables single sign-on (SSO).
To configure OIDC, enable the option and click the Edit icon to open the configuration settings. Enter the required identity provider details, such as Client ID, Client Secret, Issuer, Auth Scope, authorization and logout endpoints, and configure role mapping. Save the settings to apply the configuration. You can click the Edit icon again to modify the settings when required.
Single Sign-On| OIDC Configuration
SAML SSO configuration includes service provider settings, identity provider settings, identity provider claims, role mapping, and additional user configuration.
Enable the SAML SSO option to open the configuration sidebar. Complete the mandatory fields and submit the configuration. Once saved, the SAML option remains enabled, and the Edit option is displayed on the SAML card.
Single Sign-On| SAML SSO Configuration
Secure Pass SSO allows users to sign in to Infraon through the configured Secure Pass authentication mechanism without entering their Infraon credentials separately.
To configure Secure Pass SSO, enable the option and click the Edit icon to open the configuration settings. Update the required details and submit the changes. You can use the Edit icon again to modify the configuration when required.
Single Sign-On| Secure Pass SSO Configuration
Select the allowed email domains for Single Sign-On (SSO) to specify which domains can be used by users to sign in to Infraon through Microsoft or Google authentication. This restricts SSO access to users whose email addresses belong to the selected domains.
The Security & Customization settings allow administrators to control login access, configure CAPTCHA validity, and customize the login page.
Configure the IP addresses, IP ranges, or subnets permitted to access Infraon. You can enter the IP details manually or import them using a CSV file. A maximum of 1,000 rows is allowed for CSV uploads. If both the IP list and CSV data are provided, the CSV data takes priority. Click Submit to apply the configuration.
After submitting, click the Edit icon to modify the allowed client IP addresses or update the configuration when required.
Security & Customization | Configure Allowed Client IP Address
Configure the CAPTCHA validity duration to control how long a successful CAPTCHA verification remains valid. Users are prompted to complete CAPTCHA verification again after the configured duration expires.
To configure CAPTCHA, enable the option and click the Edit icon to modify the validity duration. Set the required duration within the allowed range and submit the changes to save the configuration. You can use the Edit icon again to update the settings when required.
Login Page Configuration allows administrators to customize the login page's text, images, colors, links, and supporting resources.
Enable the Login Page Configuration option and click Edit to modify the available settings. After completing the changes, click Submit to save them.
Allows users to sign in using their registered email address and password.
This is the default authentication method in Infraon.
Mobile Number & SMS
Enable or disable the authentication option and configure the SMS gateway.
Allows users to sign in using their registered mobile number and an SMS OTP.
Configure the primary SMS gateway and, optionally, a secondary gateway to send OTP messages.
Email-Based 2FA
Enable the option and configure OTP settings and the email template.
Allows users to verify their identity using an OTP sent to their registered email address.
Administrators can configure OTP verification limits, validity, user-level 2FA overrides, and the email template.
Label
Action
Description/Example
Primary – SMS Config Type
Select the configuration type.
Select an SMS Gateway to configure the gateway used to send OTP messages.
Title *
Label
Action
Description/Example
Max OTP Login Attempts *
Enter a number.
Specify the maximum number of OTP verification attempts allowed during a login session.
Example: Entering 5 allows up to five verification attempts.
OTP Validity (Minutes) *
Label
Action
Description/Example
Microsoft SSO
Enable or disable the option.
This option leverages the power of Single Sign-On (SSO) for a more convenient and potentially more secure login experience.
Users can log in to the Infraon Infinity portal using their existing Microsoft credentials, eliminating the need to manage separate passwords for the platform.
Relying on Microsoft's robust authentication infrastructure improves user experience and potentially enhances security.
Google SSO
Label
Action
Description/Example
Client ID *
Enter text.
Enter the client identifier provided by the OIDC identity provider.
Client Secret *
Label
Action
Description/Example
Service Provider URL *
Enter the service provider URL.
Specifies the base URL used by Infraon for SAML authentication. The related service endpoints are populated using this URL.
Label
Action
Description/Example
Client ID *
Enter text.
Enter the client identifier provided by Secure Pass.
Client Secret *
Label
Action
Description/Example
Configure Allowed Client IP Address
Enter the IP address range or subnet.
Specify the IP address range or subnet authorized to log in to Infraon.
CAPTCHA Configuration
Set the Expiry Duration in hours.
Label
Action
Description/Example
IP Address
Enter the allowed IP address, IP range, or subnet.
Specifies the client IP addresses permitted to log in.
Example: 10.0.5.24 or 192.168.1.0/24.
Import from CSV
Label
Action
Description / Example
Username Field Label
Enter the required label
Displays “E-Mail ID” instead of “Username/E-mail ID” on the login page.
Username & Password Default
Mobile Number & SMS
Note: After configuring and submitting the settings, click the Edit icon to modify the SMS gateway configuration.
Email-Based 2FA
Note: You can use the Edit icon again to modify the configuration when required.
Single Sign-On (SSO)
Microsoft SSO
Google SSO
OIDC
SAML SSO
Secure Pass SSO
Note: Users must be registered by an administrator before they can sign in through Secure Pass. After authentication, registered technicians are redirected to the main portal, while registered requesters are redirected to the self-service portal. If a user is registered as both a technician and a requester, the technician portal takes priority.
SSO Configuration
Security & Customization
Configure Allowed Client IP Address
CAPTCHA Configuration
Login Page Configuration
Enter text.
Enter a name to identify the SMS gateway configuration.
Add Country Code
Enable or disable the option.
Configure whether the country code should be added to the recipient's mobile number, based on the gateway requirements.
Use GET Request
Enable or disable the option.
Configure whether the SMS gateway request uses the GET method.
Use HTTPS
Enable or disable the option.
Enable this option to use HTTPS for the SMS gateway request.
URL *
Enter the gateway URL.
Enter the SMS gateway endpoint URL, such as https://. Use the URL provided by the SMS gateway provider.
Status Code
Enter the required status code.
Specify the HTTP status code used to identify a successful gateway response, according to the provider's configuration.
Send SMS Individually
Enable or disable the option.
Configure whether SMS messages are sent individually to recipients.
Request Parameters
Click Add to add a parameter and the delete icon to remove an added parameter. Enter the key and value, and configure the parameter options.
Add the parameters required by the SMS gateway API.
Enter the parameter name in Key and its corresponding value in Value.
Enable Pass to Header to include the parameter in the request header, or Pass to Query to include it in the query string, as required by the gateway API.
Secondary – Enable Secondary SMS Gateway
Enable or disable the toggle.
Enable this option to configure a secondary SMS gateway.
When enabled, the secondary gateway configuration fields are available.
Submit
Click Submit after completing the configuration.
Saves the SMS gateway settings. Review the primary and secondary configurations, if applicable, before submitting.
Enter a number.
Specify how long the generated OTP remains valid.
Example: Entering 3 means the OTP is valid for three minutes.
Override User-Based 2FA (User Account Settings)
Enable or disable the option.
Configure whether the standard Email-Based 2FA settings override the 2FA configuration defined in individual user account settings.
Subject *
Enter text.
Specify the subject line of the email containing the login OTP.
Email Body *
Enter or edit the email content.
Customize the email message sent to users. Include the supported macros {{User}}, {{OTP}}, and {{Expiry Timeout}} to insert the user's name, generated OTP, and OTP expiry timeout, respectively.
Save
Click Save after configuring the settings and email template.
Saves the Email-Based 2FA configuration and template.
Enable or disable the option.
This login method prioritizes both convenience and security.
Users can access the Infraon portal with their existing Google credentials, eliminating the need for separate login details.
OIDC
Enable the option and configure the required settings.
Enables authentication through an OpenID Connect identity provider using the configured client credentials, issuer, endpoints, and role mapping.
SAML SSO
Enable the option and configure the service provider and identity provider details.
Enables authentication through a SAML-compatible identity provider. Administrators can configure endpoints, bindings, identity provider claims, and role mapping.
Secure Pass SSO
Select Secure Pass SSO and configure the required settings.
Enables authentication through Secure Pass digital identity, with access determined by the user's registration and role.
SSO Configuration (Microsoft, Google)
Select the SSO Allowed Domains
Configure single sign-on (SSO) using Microsoft or Google as the identity provider.
Specify the email domains permitted to sign in through SSO.
Users with email addresses matching the configured domains are allowed to authenticate.
Example: company.com allows users with email addresses such as user@company.com to sign in.
Enter text.
Enter the client secret associated with the registered application.
Issuer *
Enter a URL or issuer value.
Specify the issuer URL of the OIDC identity provider.
Auth Scope *
Enter the required scopes.
Specify the scopes requested during authentication, based on the identity provider's configuration.
Auth *
Enter the authentication endpoint.
Specify the endpoint used to initiate authentication with the identity provider.
Logout *
Enter the logout endpoint.
Specify the endpoint used to log users out of the identity provider, where supported.
Enter Role *
Enter a role value.
Enter the external role name to be mapped to an Infraon role.
Select Role *
Select a role.
Select the corresponding Infraon role for the specified external role.
Default Role
Select a role.
Select the role assigned by default when no specific role mapping applies, according to the system's configuration.
Create User If Not Exist
Enable or disable the option.
Configure whether a user account is created automatically when the authenticated user does not already exist in Infraon.
Generate Email If Email Not Found
Enable or disable the option.
Configure whether Infraon generates an email address when the identity provider does not supply one.
Submit
Click the Submit option
Click the Submit option to save the OIDC configuration.
Client ID *
Enter the client identifier.
Enter the identifier used to identify the registered application or service provider, as required by the configuration.
Assertion Consumer Service URL *
View the generated URL.
Displays the service provider endpoint that receives the SAML authentication response. The URL contains the service provider URL and the fixed path /ux/saml/ssocallback.
The path section is read-only.
Assertion Consumer Service Binding *
Select a binding.
Select the binding used to transmit the SAML response to the assertion consumer service.
Single SignOn Service URL *
View the generated URL.
Displays the service provider's SSO endpoint using the service provider URL and the fixed path /ux/saml/ssocallback.
The path section is read-only.
Single SignOn Service Binding *
Select a binding.
Select the binding used for the single sign-on service.
Single SignOut Service URL *
View the generated URL.
Displays the service provider's single sign-out endpoint using the service provider URL and the fixed path /ux/saml/sls.
The path section is read-only.
Single SignOut Service Binding *
Select a binding.
Specifies the binding used for the service provider's single sign-out service.
The default value is urn:oasis:names:tc:SAML:2.0:bindings:HTTP-Redirect.
Identity Provider URL *
Enter the identity provider URL.
Enter the identity provider URL used for SAML authentication.
The identity provider's service endpoints are populated using the configured URL where applicable.
Entity ID *
Enter the entity identifier.
Enter the entity identifier provided by the identity provider.
x509cert
Enter or provide the certificate.
Configure the identity provider's X.509 certificate used to validate SAML responses or assertions, as supported by the configuration.
Single SignOn Service URL *
Enter a URL.
Specifies the endpoint that processes SAML authentication requests.
The URL configuration supports the identity provider URL and an additional endpoint path.
Single SignOn Service Binding *
Select a binding.
Select the binding supported by the identity provider's SSO service.
Single SignOut Service URL *
Enter a URL.
Specifies the endpoint used for logout through the identity provider.
The URL configuration supports the identity provider URL and an additional endpoint path.
Single SignOut Service Binding *
Select a binding.
Select the binding supported by the identity provider's single sign-out service.
Email Key *
Enter the claim name.
Specify the claim containing the user's email address.
Role Key *
Enter the claim name.
Specify the claim containing the user's role information.
First Name Key *
Enter the claim name.
Specify the claim containing the user's first name.
Last Name Key *
Enter the claim name.
Specify the claim containing the user's last name.
User Name Key
Enter the claim name.
Specify the claim containing the user's username, if provided by the identity provider.
Enter Role *
Enter a role value.
Enter the role name received from the identity provider.
Select Role *
Select a role.
Map the external role to the corresponding Infraon role.
Default Role
Select a role.
Select the default Infraon role to assign when no specific role mapping applies, according to the system's configuration.
Create User If Not Exists
Enable or disable the option.
Configure whether Infraon creates a user account when an authenticated user does not already exist.
Generate Email If Email Not Found
Enable or disable the option.
Configure whether Infraon generates an email address if the identity provider does not provide one.
When enabled, the Email Suffix option will display.
Email Suffix *
Enter a suffix.
Specify the email suffix used when generating an email address for a user whose email is not provided by the identity provider.
Submit
Click Submit
Click the Submit button to save the SAML SSO
Enter text.
Enter the client secret associated with the Secure Pass application.
Environment *
Select an environment.
Select the environment in which Secure Pass authentication will operate, such as Staging.
Assurance Level (ACR) *
Select an assurance level.
Select the required authentication assurance level: SOP1 – Low (email/mobile verified), SOP2 – Medium (advanced signature), or SOP3 – High (biometric).
Scope
Enter or retain the default value.
Specifies the scope for Secure Pass profile data. Retain the default scope unless Secure Pass support advises otherwise.
Callback URL
View and register the URL.
Register this URL in the Secure Pass developer portal as the redirect URI for the application.
Redirect URI Override
Enter a URL, if required.
Use this field only for sandbox or testing when the registered redirect URI differs from the Callback URL. Leave it blank in production unless otherwise required.
Submit
Click Submit
Click Submit to save the Secure Pass
Specify how long CAPTCHA remains valid after a successful login.
Once the configured duration expires, users must complete CAPTCHA validation again.
The default expiry duration is 1 hour.
Login Page Configuration
Customize the login page settings.
Customize the login page settings by enabling the login page configuration feature.
After enabling it, click Edit to modify the login page settings, including field labels, header and footer, content, colors, font size, and links/
Select Import from CSV, then upload a CSV file using Browse or drag and drop the file.
Allows multiple client IP addresses or ranges to be imported from a CSV file.
A maximum of 1,000 rows is allowed.
Download Sample CSV
Click Download sample CSV file here.
Downloads a sample CSV file to help you prepare the import file in the required format.
Submit
Upload the CSV file or enter the IP details, then click Submit to apply the configuration.
Saves the allowed client IP address configuration. When both the IP list and CSV data are provided, the CSV data takes priority.
Password Field Label
Configure the password field label
Defines the label displayed for the password field.
Sign-in Button Text
Configure the button text
Defines the text displayed on the sign-in button.
Self Service Link Text
Configure the link text
Defines the text displayed for the self-service link.
Header Text
Enter the header text
Displays the configured text in the login page header.
Header Description
Enter the header description
Displays supporting information below the header text.
Header Image
Upload or configure the header image
Displays the configured image in the login page header.
Footer Text
Enter the footer text
Displays the configured text in the footer section.
Footer Description
Enter the footer description
Displays supporting information in the footer.
Footer Image
Upload or configure the footer image
Displays the configured image in the login page footer.
Text Color
Choose a text color
Select a color that contrasts with the login page background image to ensure readability.
Font Size
Select Small, Medium, or Large
Sets the font size for the applicable login page text.
Links
Configure the required links
Provides access to relevant pages or resources from the login page.
Documents
Upload supporting documents
Supports PDF, DOC, DOCX, XLS, XLSX, PPT, PPTX, TXT, CSV, JPG, PNG, GIF, BMP, and WEBP files, with a maximum size of 12 MB per file.
Registration Link Text
Configure the registration link
Defines the text displayed for requester registration.
Restrict to Specific Domains
Configure domain restrictions
Restricts requester registration to approved domains when enabled.
Approved Domains
Specify permitted domains
Lists the domains allowed for requester registration.
Live Clock
Configure the live clock section
Provides the live clock feature on the login page, if enabled.
User Guide
Configure the user guide resource
Makes the configured user guide available from the login page.
Get the Mobile App
Configure mobile app links
Provides links to the app on the App Store and Google Play.
Announcement
Display eligible announcements
Displays announcements without a Visibility Config restriction. Each announcement remains visible until its publish end date.
Submit
Click
Click the submit button to save the changes made on the login page.
Contract Management
Contract Management is a dedicated module in Infraon platform designed to handle and track all essential contractual agreements. It ensures streamlined organization and visibility into each contract’s lifecycle. This module allows users to efficiently store and monitor important details such as start and end dates, renewal terms, obligations, compliance requirements, and associated costs.
With the Contract Management module, organizations can manage various contract types, including:
Procurement Contracts: Manage purchase and acquisition of IT hardware, software, fixed assets, and consumable items, including pricing, quantity, and tax details.
Support & Maintenance Contracts: Track support agreements, maintenance schedules, and service coverage for assets and systems.
Service Contracts: Manage contracts related to outsourced or third-party services and operational support.
System Integration & Project Contracts: Handle contracts for system implementation, integration activities, and project-based engagements.
Lease Contracts: Manage lease agreements for assets, equipment, or infrastructure with defined terms and durations.
Other Contracts: Capture and manage additional contract types that do not fall under standard categories.
The Contract Management page provides an organized view of all the contracts stored in the inventory and their associated details. Users can access a pre-configured list of contract categories on the left panel, including Software, Hardware, Lease, and Service.
These categories are dynamically displayed based on the types of contracts added to the system.
The following table outlines the available action icons and their functionality:
Basic Details | Contract Management |
The main page also displays essential fields for each contract, ensuring users have quick access to critical information at a glance. These fields include:
Contract Name
Contract ID
Type
Vendor
Clicking on a specific contract opens a detailed pop-up window for privileged users. This window provides a comprehensive view of the contract's key information and associated details. Refer to the table below for more information:
Contract Details | Contract Management |
When this setting is enabled, the system allows users to define a custom contract ID structure. The format can be configured using prefixes, numeric values, and custom fields to align with organizational standards.
This format is applied automatically during contract creation, ensuring each contract is uniquely and consistently identified.
Example Formats:
#CONT-0001
#PROC-2026-0001
#AMC-IND-0100
You can configure this from: Contract Management → Actions → Customize Contract ID.
Customize Contract ID Format | Field Reference
Label
Action
Description / Example
The fields include Contract Name, Type, ID, Vendor, Status, Managed By, Approver, Description, Start Date, and End Date.
Note: Contract-level custom fields are also available for filtering. Unsupported types, such as checkbox and radio button fields, are excluded.
Grid View
Display the contract data in a grid format.
Provides a structured, row-column view of all contracts for easy comparison.
Card View
Display the contract data in a card-based layout.
Allows users to view contracts as individual cards for a concise summary of key details.
New Contract
Add a new contract to the inventory.
Create new contracts in any predefined categories: Software, Hardware, Lease, or Service.
Edit
Modify details of an existing contract.
Enables users to make changes to already added contracts.
Delete
Remove a contract from the inventory.
Permanently delete the selected contract and its associated details.
Manufacturer
Status
Renewal Status
Expiry Date
Showcases detailed contract information, including basic details, software license properties, terms of the contract, and itemized cost details.
License Info
View-only field, no actions can be performed here.
Provides a summary of the license information linked to the contract, ensuring clear visibility of license-specific attributes.
Attachment
Privileged users can upload attachments
It enables privileged users to add files by dragging and dropping or browsing to upload (accepted formats: png, jpeg, jpg, txt, doc, docx, CSV, xls, xlsx, pdf; max size: 20 MB). Attachments are categorized under Default Category, Contract Agreement, Insurance and Bonding, Legal Notices, Payment Terms, and Terms and Conditions.
Activity Log
Can be viewed in grid or card view; includes search functionality
Displays the complete history of all activities performed on the contract since its creation, with advanced search capabilities for ease of navigation.
Recent Activities
View-only field, no actions can be performed here.
Highlights only the most recent actions taken on the contract, providing a quick overview of recent updates.
Custom Format
Click to add fields
Add dynamic components such as Vendor, Contract Template, Location, or Year.
Field Type
Select from the dropdown
Choose the type of field to include. Options include Text, Alpha Numeric, Random, Year, Contract Model, Contract Template, Vendor, Manufacturer, and Location.
No of values
Select from the dropdown
Define the length of the selected field.
Add Field
Click to add
Add multiple fields to build a structured contract ID format.
Number Type
Select from the dropdown
Define how the numeric sequence is generated (e.g., Auto Increment, Random).
Starting From
Enter a numeric value
Set the starting number for the sequence. Example: 1 → 0001.
Label
Action
Description
Search
Search for specific contracts by name, type, etc.
Use this feature to locate contracts in the inventory quickly based on specific details.
Filter
Label
Action
Description
Top Panel
View-only field, no actions can be performed here.
Displays fundamental contract details such as the contract ID, name, and associated information.
Summary
Preview Section
View-only
Displays a live preview of the generated Contract ID based on the selected format.
Prefix
Enter text manually
What do you see on the screen
Note: Users cannot create new contract categories. Only the predefined categories—software, Hardware, Lease, and Service—are available for selection.
View Contract Details
Customize Contract ID
Apply filters based on fields and conditions.
View-only field, no actions can be performed here.
Define a static prefix for the contract ID. Example: CONT, PROC, AMC.
API Registration
APIs or Application Programming Interfaces are added to enable data exchange between Infraon and computers/programs/applications. API integrations are possible with other third-party applications and web services supporting HTTP protocol.
Infraon supports REST API. REST stands for Representational State Transfer that adheres to REST architectural constraints. REST serves as a bridge between the client and the server, allowing communication over HTTP. It enables servers to cache responses, resulting in improved application performance.
The REST-API serves as a single point of entry into the system. Before granting access to the application's resources, it encapsulates the business logic and processes all client requests, including authorization, authentication, data sanitization, and other necessary tasks. Infraon supports the below content types:
application/json
application/x-www-form-urlencoded
txt/plain
APIs use authorization to secure client requests accessing data. While integrating third-party APIs, these credentials are provided by the respective API provider. Based on the API, you can select one of the below Auth Types:
API Key - Uses a key-value pair in the API's request headers or query parameters.
Basic Auth - Uses a verified username and password with the request.
Custom Auth - Uses token-based authorization that requires CSRF URL, token, key, username, and password with the request.
No Auth - Uses when there is no authorization to request data.
Requests
Sites
Technicians
Assets
It enables external applications or systems to receive real-time updates when specific events occur in Infraon workflows. It facilitates unified automation and communication between Infraon and third-party tools by invoking a registered API when triggered by workflow conditions.
It allows users to:
Register external APIs to be invoked during a workflow transition
Enable or disable webhook responses for specific workflow actions.
Automate actions like sending notifications, updating external systems, or triggering remote scripts without manual intervention.
Go to Infraon Configuration -> General Settings -> API Registration
Click the 'Add API' button and refer to the table below for more details:
API Key - Auth Key, Auth Value, and Add Key to (Header/Query)
Basic Auth - Username and Password
Custom Auth - Token details, Key, Request Type (GET, POST), Username, and Password
No Auth - No credentials required.
Once all the parameters are added, click 'Submit' to add the API. APIs can be edited or deleted using the respective icons.
Worklog
Label
Action
Description / Example
Name
Enter a name
It helps identify the integration's purpose, especially when managing multiple APIs in Infraon. This will display the name for the API integration you're configuring.
Example: JIRA, ServiceNow, etc.
Content Type
API Supported Operations
Webhook Handler for Workflow
Instructions to 'Add API'
Auth-Type Fields
Choose from the dropdown
This defines the format of data being sent to the API.
Options: application/JSON, text/plain, multipart/form-data, and application/xml.
Authentication Type
Choose from the dropdown
This defines the method by which the API call is authenticated. The correct type must be selected based on the API provider’s documentation.
Options: API Key, Basic Auth, Custom Auth, and No Auth.
Username
Enter your username
The username is used to authenticate API calls using authentication methods like Basic Auth. This typically refers to your registered email address or username in the third-party platform.
Example: When integrating Jira, this would be your Atlassian email ID, username@example.com.
Password
Enter your password
This field is used along with the username to authenticate the API. If you're using Basic Auth, this is often your account password, or an App Password generated from the external platform’s security settings—especially in platforms like Jira or GitHub, where regular passwords are restricted.
Is Base64 Encode
Toggle ON/OFF
When enabled, Infraon will automatically convert the username and password into a Base64-encoded string for APIs requiring that format (standard with Basic Auth).
Secret Key
Enter the token/key.
The secret key refers to an API token or access key required for secure authentication. It replaces or supplements the password in many modern APIs. You can generate this token from the API/Developer settings section of platforms like Jira, Freshdesk, or Salesforce.
Example:
cJXbGJI2y1oIh3IsnTI5jR6VCJ9....
Client ID
Enter the client ID.
The Client ID is a unique identifier assigned when registering your application in an OAuth2-compliant platform (e.g., Azure, Google, Atlassian).
Example: 11853234773……...
Base URL
Enter API base URL
This is the root URL of the third-party API to which Infraon will send requests. It forms the foundation of all endpoint calls.
For Jira, it might look like: https://yourdomain.atlassian.net/rest/api.
Enable Webhook Response
Toggle ON/OFF
This option allows Infraon to receive real-time call-back responses from external platforms via webhooks. It ensures Infraon can process workflow actions or status updates triggered externally when enabled.
Description
Optional input
You can provide an internal description to explain the purpose of this integration. This is not used for functional purposes but is helpful for clarity and documentation.
Header Parameter
Enter key-value pairs
Some APIs require additional headers for authentication or custom handling. Here you can define header keys (e.g., Authorization) and assign static values or macros.
Add to Query Parameter
Toggle ON if needed
When enabled, the header parameter is attached to the URL as a query string instead of being sent in the header.
Add a Dashboard
Instructions to 'Add Dashboard'
To add a new dashboard:
Navigate to the Dashboard module.
Expand the left panel by clicking the right arrow key.
Click the plus (+) icon to create a new dashboard.
Provide a name (this name will represent and help identify the dashboard) for the dashboard and click Create.
Once created, the next step is configuring Widgets, which dynamically display data from various modules in graphical or tabular formats.
Infraon widgets are pre-built components designed to pull key insights from your infrastructure, ITSM modules, and network data, and display them in clear, interactive formats such as:
Widgets are grouped into multiple categories, such as Assets, Statistics, Views, ITSM, Contract Management, IMACD, and Purchase Orders ensuring complete coverage across IT operations and business service management.
The Assets category provides insights into IT and Fixed Assets, including inventory distribution, purchases, license usage, consumables, and vendor information. IT teams can track asset lifecycles, utilization, and financial impact.
Summary Widget
The Summary widgets offer high-level aggregation and drill-down capabilities for the ITAM modules. These widgets support flexible data grouping and multiple drill-down levels, empowering users to visualize and analyze operational metrics with greater depth.
The Views category provides device-level status and network visualizations, enabling topology-based monitoring and drill-downs.
The Contract Management category enables organizations to track vendor/manufacturer contracts, including their types and status, for compliance and renewal purposes.
The IMACD category captures Install, Move, Add, Change, and Dispose activities, providing visibility into asset and service lifecycle changes.
The Purchase Order category tracks all purchase orders, providing summaries of order counts and detailed records.
Select the widget you want to configure, then set up its parameters.
While each widget serves a predefined purpose (e.g., asset tracking), they can be fully customized by applying filters, selecting specific time ranges, or adjusting visual elements such as color schemes.
The Configuration tab allows you to define how a widget should display information. Different configuration fields will appear depending on the widget category and chart type selected. The table below combines all available fields across different widget types for reference.
The Filter tab allows you to refine and narrow widget data by applying specific filters. Instead of displaying all available information, you can limit the results to focus on relevant data points .
Click on Add to finalize your configuration and add the widget to the dashboard.
You can perform the following actions while editing a dashboard:
Edit Dashboard | Add Dashboard
Click on Submit to save and apply the changes to your dashboard.
The Global Filters section in the Edit Dashboard page is used to configure dashboard-level filters that dynamically apply across all configured widgets. These filters help users narrow down dashboard data by selected criteria, such as infrastructure, assets, locations, and ITSM-specific parameters.
Users can configure:
Standard Global Filters
Date Filters
Configurations | Global Filters
Label
Action
Description / Example
The Location Hierarchy Filter allows administrators to configure location-based hierarchy levels for dashboard filtering. Users can then select values through cascading dropdowns to filter ticket and asset/CMDB widgets based on the selected hierarchy.
How does it work?
An administrator can configure a hierarchy such as Country → State → City. When a user selects a country, the State dropdown displays only states under that country, and selecting a state further scopes the city options. After clicking Apply, the dashboard widgets display data matching the selected hierarchy.
Location Hierarchy Filter Configuration
The configuration sidebar allows administrators to enable the filter, add hierarchy levels, reorder them, and save or cancel the configuration.
Label
Action
Description / Example
The dashboard displays cascading dropdowns for the configured hierarchy levels.
Label
Action
Description / Example
The Infraon platform dashboard widgets support custom field-based filtering and grouping, enabling users to analyze data using workflow-specific attributes. Supported custom fields of type Dropdown, Checkbox, and Radio Button can be used in both Filter and Group By configurations for supported summary widgets.
While configuring a supported widget, users can navigate to the Filter section to apply custom field-based filters and use the Group By option to group widget data based on selected custom field values.
The Group By dropdown displays both default fields and supported custom fields (Dropdown, Checkbox, and Radio Button) for the selected module.
For the Count Summary widget, Group By values update dynamically based on the selected module. When users switch between modules such as Incident and Request, the available custom fields are refreshed, and users must reselect the required Group By field.
If multiple workflows contain custom fields with the same name, the workflow name is automatically appended to the field name to avoid duplication and help users identify the correct field when selecting a filter or Group By.
Nested Grouping allows users to analyze Summary widgets data across multiple hierarchical levels within a dashboard widget. It helps organize asset data in a structured, expandable format for deeper visibility into asset distribution and categorization.
This feature is available in the Summary widgets and supports up to 4 levels of grouping.
Navigate to Dashboard → Edit Dashboard.
Select the Asset Summary widget.
Go to the Configuration tab.
Enable the Nested Grouping toggle.
Nested Grouping | Configuration
Label
Action
Description / Example
Grouping Structures | Example
Purpose
Example
After saving the widget configuration, the Asset Summary widget displays data in a hierarchical tabular structure within the dashboard.
Users can expand grouped levels, view grouped asset counts, open sidebar asset details, export data, and edit the existing widget configuration.
Custom Column allows users to create custom KPI-based calculations for supported dashboard count widgets using a formula builder. This feature helps users define calculated metrics directly within the widget configuration using mathematical operations, following BODMAS precedence rules.
Navigate to the Dashboard and select Add New Widget.
Select a supported Count Widget such as Total Incident Count.
Enable the Enable Formula toggle to activate Formula Mode.
Open the Formula tab to create custom KPI columns.
Add a custom column name and configure the formula expression using supported operators.
Apply the changes to preview the calculated widget data.
Save the widget configuration and dashboard.
The formula builder supports standard mathematical operations following BODMAS precedence rules:
Addition (+)
Subtraction (-)
Multiplication (*)
Division (/)
Formula Configuration
Label
Description / Example
To learn more about configuring Custom Columns using the Formula Builder,
Example KPI Formulas
KPI Name
Formula
Bar Chart
Shows comparative metrics in horizontal/vertical bar form.
Example: License Usage.
Area Chart
Highlights cumulative growth or changes over time with shaded areas.
Gauge Chart
Displays progress against a target or threshold (like a speedometer).
Example: SLA Compliance Rate.
Sunburst Chart
Provides hierarchical data in concentric circles for drill-down insights.
Example: Business Service Summary.
Data Panel
License Usage
Bar Chart, Data Table
True-up Cost
Data Panel
Top Publishers
Bar Chart, Data Table
Consumable Summary
Data Panel
Location-Wise Asset Summary
Bar Chart, Data Table
Agent Status
Data Panel
Asset Location Drilldown Table
Data Table
Asset Location Drilldown Summary
Data Panel
Asset Aging Summary
Bar Chart, Data Panel
Agent Count
Displays agent counts in a panel view with Total, Active, and Inactive agents. When the Creation Time filter is applied, all counts are shown.
When the Down Since filter is applied, only the inactive agent count for the selected time range is displayed.
View: Data Panel
Agent Summary
Displays a summary of Inventory Agent or Data Collector Agent instances grouped by version and build number, with Total, Active, and Inactive agent counts. Users can configure the title, grouping, display style, background color, auto-reload interval, time scale, and custom filters. Clicking a count opens a list of the corresponding agents for the selected version, build, and status.
View: Data Table
Patch Agent Count
Displays the total number of inventory agents, the number with the Patch Agent installed, and the number without it. Clicking a count opens a panel listing the corresponding agents. The widget is available only to organizations with the Patch Management license and the InfraonPatch feature flag enabled.
View: Data Panel
Enables filtering and grouping data by the chosen attribute for focused monitoring.
Drill-Down Level 1
Select an option from the group by fields and the widget view
First-level drill-down using the chosen field, showing a quick breakdown (e.g., open/closed status).
Drill-Down Level 2
Add secondary grouping and view option.
Allows further segmentation of data (e.g., breakdown by priority within status) and supports multiple levels for deep analysis.
Timescale
Choose time period (e.g., current week)
Filters widget data by the selected timescale, aiding trend analysis.
Auto Reload
Set refresh interval
Ensures summary data is updated automatically at specified intervals.
Chart Type
Select a data panel, a pie chart, a bar chart, or a data table
Provides various visualization options for presenting summary and drill-down data.
Show Unassigned
Enable toggle
The Show Unassigned option displays data that are not assigned to you.
Show Total Count
Enable toggle
The Show Total Count option displays the total number of records along with the existing status-wise counts in the summary widget. Enables or disables the display of the total number of records in the ITSM Summary Widget. It is disabled by default.
Geo Map Drilldown Summary
Data Panel
Device Status
Data Panel
Choose how data is grouped (e.g., Device Type, Day, Assignee, Requester). Determines the primary categorization for the widget.
Type*
Dropdown
Select the data type relevant to the widget.
Example: Active Events
Top*
Dropdown
Define how many top results to display.
Example: Top 10 Assets by Value.
Drill-Down (Add Level)
Add additional field levels
Let's users add hierarchical drill-downs for deeper analysis.
Example: Group by Device Type → Location → Vendor.
Timescale*
Dropdown
Select the time range for data visualization.
Options: Last Hour, Current Day, Current Week, Current Month, etc.
Auto Reload*
Dropdown
Set automatic refresh intervals for the widget.
Example: 5 mins, 15 mins, 30 mins, 1 hour, etc.
Chart Type
Icon selector
Choose the display format. The available types are Panel View, Data Table, Line Chart, Bar Chart, Area Chart, Gauge Chart, Sunburst Chart, and Pie Chart.
Cross Launch URL
Input field
Provide a URL that can be cross-linked for detailed analysis or drill-through.
Color Palette
Selector
Choose a predefined color scheme for graphs and charts. Helpful in aligning with brand or theme.
Show All
Toggle (On/Off)
Option to display all available results instead of a limited set.
Example: Show all services in Business Service Summary.
Filter resources (users, services, or configurations) by tags.
Example: Cloud Resource, Database Server, API Service, etc.
Assignee
Select from the dropdown
Restrict data to a particular assignee. Helpful in tracking workload distribution.
Custom Filters
Add field-value pair
Filters are visible based on selected preferences. Different filters are available on the Infraon platform, which can be applied to a widget to filter data displayed in the Dashboard.
Here is the list of custom filters depending on the field :
Asset ID
IP Address
Device Type
Field
Select field type
Choose the attribute to filter on.
Example: Location, Department, Priority, etc.
Value
Select the corresponding value
Define the actual filter criteria.
Example: Critical, High, Medium, Low.
Add Filter
Click to add a new row.
Add multiple filters for complex queries.
Add new widgets using the same configuration and filter process described earlier.
Assignee
Click Assignee on the top bar.
Assign the dashboard to a specific User or a Team. Select from the pop-up list (e.g., Approval Team, Change Team).
Global Filter
Click Global Filter on the top bar
Apply overall filters to the dashboard:
Global Filter: Toggle on/off. Add filters such as Location, Department, and Make to refine dashboard and widget data.
Date Filter: Enable/disable to view data within a selected time range.
Resize Widgets
Click and drag the widget’s edges
Increase or decrease widget size to fit the dashboard layout.
Reposition Widgets
Double-click and drag a widget
Move the widget’s position anywhere on the dashboard canvas.
Disable Date Filter
Enable or disable the date filter option.
Displays the date range filter on the dashboard view page to filter widget data by the selected time duration.
Add Level
Select a level
Adds a location or asset custom field as a hierarchy level.
Example: Country, State, City.
Hierarchy Level
Configure
Defines the order in which hierarchy values are displayed and selected.
Reorder
Drag and drop
Changes the order of configured hierarchy levels.
Example: Move City above State.
Cancel
Click
Closes the configuration sidebar without saving the changes.
Submit
Click
Saves the configured hierarchy levels and applies the configuration to the dashboard.
Disable Location hierarchy filter
Disable toggle
Disable the Location Hierarchy Filter for the dashboard.
Apply
Click
Applies the selected hierarchy values to the dashboard widgets.
Select required fields under Levels.
Add additional levels if required.
Click Apply Changes to preview.
Click Add and then Submit to save the dashboard.
Add Level
Click to add a grouping level
Adds additional grouping levels for deeper asset categorization. Supports up to 4 levels.
Delete Level
Click the delete icon
Removes the selected grouping level from the hierarchy configuration.
Level Sequence
Arrange selected fields
Determines how asset data is grouped in the widget. The first field becomes the parent level, followed by child levels.
Apply changes to preview
Click to generate preview
Displays widget data in a hierarchical structure based on the selected grouping levels before saving.
Auto Reload
Select refresh interval
Automatically refreshes widget data based on the selected interval without changing the grouping configuration.
Department Asset Analysis
Department → User → Status
Brackets / Parentheses ()
Add Column
Adds additional custom KPI columns within the same widget configuration.
Apply Changes to Preview
Validates the configured formula and refreshes the widget preview with calculated KPI values.
Chart Type
Description / Example
Data Panel
Displays high-level KPIs or summary metrics in a compact panel format.
Example: Total Active Assets.
Data Table
Presents detailed data in a structured table with sorting, filtering, and drill-down options.
Example: Asset Location Drilldown Table.
Line Chart
Widget
View
New Purchases
Data Panel
AMC Expiry
Data Panel
Label
Action
Description
Widget Name
Select module
Displays the summary based on the chosen ITAM category, auto-refreshes for a real-time view.
Group By
Widget
View
Text/URL Panel
Data Panel
Network Diagram
Data Panel
Topology View
Widget
View
Contract Summary
Data Panel
Contract Count Panel
Data Panel
Widget
View
IMACD Summary
Displays a summary of IMACD data based on the logged-in user's data visibility and access permissions. The widget ensures that users see only the IMACD records they are authorized to view in the IMACD module grid.
For non-admin users, the widget applies the same visibility rules as the IMACD grid, including access based on created-by, assignee, team routing, approval/review profile membership, and asset ownership/tag linkage.
The widget ensures that no record is displayed if the user does not have access to that record in the IMACD module grid. Infraon Management Admin, Infraon Admin, and Read Only Admin users continue to have unrestricted access to IMACD data.
This widget helps users view IMACD information consistently while ensuring that restricted records are not exposed through the dashboard.
View: Summary Widget.
IMACD Count
Data Panel
Widget
View
PO Summary
Data Table
PO Count
Data Panel
Label
Action
Description / Example
Title*
Enter text
A mandatory field is needed to provide a unique name for the widget.
Example: Asset Summary
Group By*
Label
Action
Description / Example
Asset Tags
Select from the dropdown or search.
Filter assets by pre-defined tags.
Example: Critical Devices, Production Servers, etc.
Supported options include: Location, State, City, Device Type, Make, Model, Branch, Branch Code, Asset Tags, Asset Custom Fields, Resource Tags, Resource Custom Fields, Link Name, Link Mode, ISP Name, Region, and PO Number.
Enables the Location Hierarchy Filter for the dashboard.
Displays values scoped according to the selected parent level.
Example: After selecting India, the State dropdown displays states under India.
Used to define the hierarchy of asset grouping. Each selected field becomes a grouping level in the widget.Example: Location → Department → Device Type.
Vendor → Model → Asset Type
Configures the COUNT-based calculation logic using supported fields within the Formula Builder.Example: COUNT(State - Resolved), COUNT(Reopened), or COUNT
(COUNT(State - Resolved) / COUNT) * 100
Asset Type
IT Asset Status
Fixed Asset Status
Group By
Location Name
Installed Location
Organization Name
Is Active
Designation
Floor
Building
SAP ID
Location
OLD Associated Assets
Colour
Service Catalogue
Organization Name
Department
Team
And more.
Asset Grid Page
There is no single home page for Assets. Assets are added based on the asset type, each with a grid page. Click on the respective asset type from the left panel to view the list of assets in the selected category. This page is referred to as the 'Asset Grid Page'.
Assets can be viewed as a card or a grid view. Asset details include the following information.
Asset Name
IP Address
Asset Category
Asset ID
Asset Status
Device Type
Make
There are three ways to search for an asset.
Barcode Search - Click the Scan & Search Asset icon and scan the barcode using a barcode scanner. The corresponding asset information is displayed automatically.
QR Code: Users can generate, print, and scan QR codes for assets to quickly access asset-related information.
Asset Search - Click the 'Scan & Search Asset' icon and type the asset ID to search.
Users can customize the information displayed when a QR code is scanned by selecting which asset fields to include in the QR data.
To customize QR code fields:
Navigate to the required Asset module page.
Click Actions.
Select Customize QR Columns.
Choose the fields to be displayed in the QR scan result.
Click:
Submit – Applies the configuration for newly generated QR codes.
Submit & Overwrite – Regenerates QR codes for existing assets with the updated configuration.
The customization supports:
Standard asset fields
Custom fields such as:
Text
Number
Additionally:
A maximum of 6 fields can be selected for QR display.
Updated asset values are automatically reflected in QR scan results after regeneration.
Printed and bulk-generated QR codes maintain the configured field information.
Asset ID changes are reflected in QR data when Asset ID customization is enabled.
Users can scan the generated QR codes using:
Mobile device camera scanners
Third-party QR scanner applications
QR scanning applications available on Google Play Store
When scanned, the QR code displays the configured asset information based on the selected QR columns.
Customize columns based on unique preferences. Arrange columns effortlessly with a simple drag-and-drop action, streamlining the experience for optimal efficiency and organization.
Select one or more assets to view the asset actions below:
Owner - Click to add/change asset owner.
Requester - Click to update the requester and/or owner.
Tag - Click to update the asset tag.
Print - Click to print the asset label(s).
Enhanced Software Management! Now, easily sort asset ID, name, operational status, and overall status in ascending or descending order while adding software.
Asset Label Templates allow you to create and manage reusable QR code and barcode label templates for IT assets. Instead of using a single fixed label format, you can create multiple templates for different asset categories and printing requirements.
Each template supports configurable branding, asset fields, QR/barcode settings, label styling, and paper dimensions, enabling the system to generate print-ready PDF labels based on the saved template configuration.
The Asset Label Templates page displays all available label templates and provides options to search for, create, preview, edit, and delete them. From this page, you can manage reusable templates used when printing QR code or barcode labels for assets.
Asset Label Templates | Basic Details
To create a new asset label template, navigate to IT Assets → Asset Label Templates, and click Add Template.
The New Template page allows you to configure the layout, branding, visible asset fields, styling, and paper settings for the label. As you update the configuration, the preview panel displays the label layout in real time.
Complete the following sections before saving the template.
Specify the basic information for the template.
Select the label layout that defines the structure and supported configuration options.
Configure the branding elements that appear on the printed label.
Select the asset information to display on the printed label.
Configure the appearance of the label and QR/barcode.
Configure the paper and label size for printing.
After completing the required configuration, click Save Template. The template is saved and becomes available for preview, editing, and selection while printing QR code or barcode labels for assets.
The Print Jobs feature allows Infraon Platform users to generate QR/Barcode labels for multiple assets in a single print job. Users can select an existing label template, filter assets based on their requirements, choose all or specific filtered assets, and submit them for printing.
Large print jobs are processed in batches in the background, and users can track progress, download completed labels, or retry failed jobs. The Print Jobs tab provides an overview of all submitted print jobs and their current processing status.
Batch Processing[
Large print jobs are automatically divided into batches so that they can be processed in the background.
The system calculates the number of batches based on the number of selected assets. The default batch size can be 250 assets per batch. For example, a print job containing approximately 5,000 assets can be processed across multiple batches.
The progress shown on the Print Jobs page is based on the number of completed batches.
If a batch fails:
The entire job is not incorrectly marked as completed.
The failed or pending batch can be retried.
Successfully completed batches are not processed again during retry.
The system supports up to 10,000 assets per print job, subject to the configured behavior when the limit is exceeded.
After successful batch processing, the system generates the asset labels as PDF files.
If the generated output exceeds the configured PDF threshold, the output is divided into multiple PDF files. When multiple PDFs are generated, the completed print job provides a ZIP download containing the generated files.
If a batch or worker fails during processing, the print job is marked as Failed, and the failure reason is displayed in the job details.
Click Retry to resume processing the failed or pending batches.
During retry:
Completed batches are not processed again.
Already printed assets are not duplicated.
A successful retry changes the job status to Completed.
If the retry fails again, the job remains Failed with the latest failure reason.
The Print Jobs page opens with the list of existing print jobs.
The top panel displays a quick overview of the Print Jobs page, which includes:
The Print Jobs page provides an overview of print jobs and their current processing status. You can search and filter print jobs, monitor processing progress, and perform actions such as downloading completed output or retrying failed jobs.
Print Jobs | Basic Details
Click New Print Job to create a bulk asset label print job. The New Print Job panel allows you to configure the job, select a label template, filter assets, and choose the assets to be printed.
Print Job | Job Details
The selected asset count is displayed before the job is submitted.
Review the job details, selected template, and asset count.
Click Preview to review the print-job configuration.
Click Submit Job to create the print job.
Once submitted, the print job is created with Pending status and is processed in the background.
After creating a Print Job, click the Job ID from the Print Jobs list to open the Print Job details page. The details page contains the Assets and Details tabs.
The Assets tab displays the assets included in the Print Job along with their printing status. It also provides options to download the generated print files.
Print Jobs | Assets List
Details
The Details tab provides an overview of the Print Job, its completion progress, generated files, and batch processing information.
Print Jobs | Details List
Print Jobs | Details List
The Asset Status tab provides an asset-level view of the printing status. It allows users to view assets and generate a print label for a specific asset. By selecting an asset, users can open a new Print Job, provide a job name, and send the label for printing directly.
It categorizes assets into:
All
Not Printed
Printed
Reprinted
You can search assets by Asset Name or Asset ID, and filter them by Job ID or Asset Type.
Asset Status |Basic Details
The asset list displays details such as Asset ID, Name, Type, Department, Print Status, Last Printed Date, and Last Job.
For example, an asset with status Printed can show its last printed date and the ID of the print job that generated the label.
Asset Reconciliation allows administrators to create reconciliation campaigns for selected assets and request users to verify and acknowledge the assets assigned to them.
Administrators can track the acknowledgment status, manage pending or overdue requests, send reminders, and optionally use a Maker-Checker process to verify the user's acknowledgment.
The Asset Reconciliation page provides an overview of reconciliation activities and allows administrators to manage campaigns and active acknowledgment requests.
Asset Reconciliation | Basic Details
Click New Campaign to create a reconciliation campaign.
A campaign defines which assets need to be reconciled, when the acknowledgment is due, how frequently the campaign should run, and whether Maker-Checker verification is required.
Asset Reconciliation | Campaign Details
The Active Request tab displays all currently active asset reconciliation requests and provides the information required to track and complete each request.
Active Request | Basic Details
Filter - Click on the 'Search Filter' field and type the name, asset ID, hostname, IP address, or category/sub-category to search.
Email
Phone fields
QR regeneration activities are recorded in audit logs and asset history.
More - Click to update asset status and location, enable, disable, or delete the asset.
The asset(s) must be in an 'enabled' state for editing.
Filter templates by template type.
Column Details
Add Template
Click Add Template
Opens the New Template page to create a new asset label template.
Name
View
Displays the template name.
Label Type
View
Displays the selected base layout of the template.
Example: Default Tag
Template Type
View
Displays the selected code type used by the template.
Example: QR Code
Label Size
View
Displays the configured label dimensions.
Example: 2.5" × 1.5"
Last Used
View
Displays the date when the template was last used for printing.
Created By
View
Displays the user who created the template.
Action Icons
Preview
Click the Preview icon
Opens a preview of the saved label template.
Edit
Click the Edit icon
Opens the selected template in edit mode. All previously saved settings are preloaded.
Delete
Click the Delete icon
Deletes the selected template after confirmation.
Logo
Upload, replace, or remove
Upload a company logo.
Supported formats: PNG, JPG, JPEG, SVG.
QR Size
Drag the slider
Adjust the size of the QR code or barcode displayed on the label.
Specify the paper orientation.
Options: Portrait, Landscape
Margin
Select or enter a value
Specify the page margin.
Example: 0 mm
Label Size
Select from the dropdown
Select the predefined label size.
Example: Small
Label Height
Enter a value
Specify the label height.
Example: 1.5 in
Label Width
Enter a value
Specify the label width.
Example: 2.5 in
Spacing L→R
Enter a value
Specify the horizontal spacing between labels.
Example: 0.1 in
Spacing T→B
Enter a value
Specify the vertical spacing between labels.
Example: 0.1 in
View the count.
Displays the total number of print jobs created.
Pending
View the count.
Displays the number of print jobs waiting to be processed.
Running
View the count.
Displays the number of print jobs currently being processed.
Completed
View the count.
Displays the number of print jobs that have finished successfully.
Failed
View the count.
Displays the number of print jobs that could not be completed successfully.
Search and Filters
Search
Enter a keyword in the search field.
Searches print jobs using information such as Job ID, Job Name, Template, or Submitted User.
Status
Select a status from the dropdown.
Filters print jobs by processing status, such as Running, Completed, Pending, or Failed.
Template
Select a template from the dropdown.
Filters the list to display only print jobs created using the selected label template.
Refresh
Click the Refresh icon.
Refreshes the print-job list and retrieves the latest job status and progress.
Column Details
Job ID
Click the Job ID.
Opens the details of the selected print job.
Example: PJ0119
Job Name
View the job name.
Displays the name provided when creating the print job.
Template
View the template name.
Displays the label template selected for generating the asset labels.
Assets
View the asset count.
Displays the number of assets included in the print job.
Status
View the current status.
Displays the current processing status of the print job.
Example: Completed
Progress
View the progress indicator.
Displays the percentage of the print job that has been completed.
Example: 100%
Batches
View the batch count.
Displays the number of completed batches against the total number of batches.
Example: 25 / 25
Submitted
View the submission date.
Displays the date on which the print job was submitted.
Example: Aug 05, 2026
Actions
Delete
Click the Delete icon.
Deletes the selected print job from the print-job list. Use this action to remove a print job that is no longer required.
ZIP
Click the ZIP icon.
Downloads the generated labels for the selected print job. The label package may be downloaded as a ZIP file containing the generated label files.
Determines the layout and information that will be printed on the asset label.
Field
Select an asset field.
Selects the asset attribute on which the filter should be applied.
Example: Asset Name
Condition
Select the required condition.
Defines how the selected field should match the specified value. Available conditions include In, Not In, Equal To, Not Equal To, Contains, Not Contains, and Is Empty.
Value
Enter or select the value according to the selected condition.
Specifies the value against which the selected field is filtered.
Example: If Field = Site and Condition = Equal To, select or enter Bangalore as the value. For Is Empty, no value is required.
Add
Add another filter condition.
Allows multiple conditions to be applied to further refine the list of assets.
Apply Filter
Click Apply Filter.
Applies the configured conditions and updates the matching asset count.
Delete Filter
Click the delete icon.
Removes an individual filter condition.
All Filtered
Select All Filtered.
Includes all assets matching the applied filters in the print job.
Example: If 28,749 assets match the filters, all 28,749 assets are included.
Custom Selection
Select Custom Selection.
Allows you to manually select specific assets instead of including every filtered asset.
Asset ID
View the Asset ID
Displays the asset's unique identifier.
Example: ASSET_01-2026-5CD7-5943-LAPT-9758
Name
View the Name
Displays the name of the asset to be included in the print job.
Type
View the Type of the asset
Displays the type or category of the asset.
Displays the number of assets for which the print file was generated successfully.
Failed
View the count.
Displays the number of assets for which the print operation failed.
Total Selected
View the count.
Displays the total number of assets selected for the Print Job.
Asset ID
View the asset ID.
Displays the unique identifier of the asset included in the Print Job.
Name
View the asset name.
Displays the name of the asset for which the label was generated.
Department
View the department.
Displays the department associated with the asset.
Print Status
View the status.
Displays the current printing status of the asset, such as Printed, Failed, or Reprinted.
ZIP
Click ZIP.
Downloads the generated print files for the Print Job as a ZIP file.
Download all as ZIP
Click Download all as ZIP.
Downloads all generated print files included in the Print Job as a single ZIP file.
Displays the label template used to generate the print files.
Total Assets
View the count.
Displays the total number of assets included in the Print Job.
Submitted Date
View the date and time.
Displays when the Print Job was submitted.
Submitted By
View the user name.
Displays the user who created or submitted the Print Job.
Output Size
View the size.
Displays the total size of the generated print output.
Example: 23.3 KB.
Progress
View the progress.
Displays the percentage of the Print Job completed and the number of completed batches.
Example: 100% – 1 of 1 batches complete.
Downloads
View the generated files.
Displays the files generated for the Print Job and provides options to download them individually or as a ZIP file.
Download
Click Download.
Downloads an individual generated print file.
Example: A generated PDF file for an asset.
Download all as ZIP
Click Download all as ZIP.
Downloads all generated print files as a single ZIP archive.
Batch Log
View the batch information.
Displays the batches processed for the Print Job along with the assets included in each batch and its processing status.
Selects an individual asset for which the print label needs to be generated.
Print Label
Select the print option for the asset.
Opens a New Print Job tab with the selected asset and its label details.
Job Name
Enter the Print Job name.
Enter a name to identify the Print Job.
Example: Laptop Asset Label.
Send to Print
Submit the Print Job.
Creates the Print Job for the selected asset and sends the generated label for printing.
Displays requests that are awaiting user acknowledgment.
Overdue
View the count.
Displays requests that have passed their due date without being completed.
Accepted
View the count.
Displays assets that users have acknowledged.
Rejected
View the count.
Displays assets that users have rejected.
Verified
View the count.
Displays acknowledgments that have been verified through the Maker-Checker process.
Campaigns
Select the Campaigns tab.
Displays the reconciliation campaigns created in the system.
Active Requests
Select the Active Requests tab.
Displays the currently active reconciliation requests.
Search
Enter a keyword.
Searches for the required campaign or reconciliation request.
Status
Select a status.
Filters reconciliation records according to their current status.
Date Range
Select a date range.
Filters records based on the selected period.
New Campaign
Click New Campaign.
Opens the campaign configuration page to create a new reconciliation campaign.
Provides additional information about the purpose or scope of the campaign.
Select Asset
Select Assets from the list
Determines which assets are included in the reconciliation campaign.
All Assets
Select All Assets.
Includes all applicable assets in the campaign.
Filtered Assets
Select Filtered Assets.
Includes assets that match the configured filter criteria.
Field
Select the required asset field.
Specifies the asset attribute on which the filter is applied.
Example: Asset Name, Asset Type, Site, or Department.
Condition
Select a condition from the dropdown: in, not in, equal, not equal, contains, not contains, or is Empty.
Defines how the selected field should be matched against the specified value.
Example: Contains returns assets where the selected field includes the entered value.
Value
Enter or select the required value.
Specifies the value used to filter the assets.
Example: Enter Laptop to find assets where the selected field contains “Laptop.”
Manually Selected
Select Manually Selected.
Allows specific assets to be selected manually.
Due Date
Select the due date.
Defines the date by which users should complete the acknowledgment.
Schedule Interval
Configure the required interval.
Determines how frequently the reconciliation campaign should run when recurring reconciliation is required.
Enable Maker-Checker
Enable or disable the toggle.
Enables a verification step in which a checker reviews the user's acknowledgment before it is considered verified.
Save Draft
Click Save Draft.
Saves the campaign without launching it.
Launch Campaign
Click Launch Campaign.
Launches the campaign and generates reconciliation requests for the selected assets.
Displays the asset's name and unique ID included in the reconciliation request.
User
View the assigned user.
Displays the user to whom the asset is currently assigned.
Latest Campaign
View the campaign name.
Displays the most recent reconciliation campaign associated with the request.Example: Quarterly Asset Reconciliation.
Triggered
View the triggered date.
Displays the date on which the reconciliation request was initiated or sent to the user.
Due Date
View the due date.
Displays the deadline by which the user must complete the reconciliation request.
Status
View the request status.
Displays the current status of the reconciliation request, indicating whether it is still pending or has been completed.
Last ACK
View the latest acknowledgment.
Displays the date and details of the user's most recent acknowledgment for the asset.
Actions
Perform the available action on the request.
Provides actions to manage or process the selected reconciliation request.
Label
Action
Description / Example
Search
Enter keyword
Search templates by template name.
Filter
Label
Action
Description / Example
Name
Enter a value
Specify a unique name for the template.
Example: Laptop QR Label
Type
Select from the dropdown
Label
Action
Description / Example
Layout Type
Select from the dropdown
Choose the base template layout.
Available Options:
Default Tag
IT Property Label
Cable Tag
Rack Strip
Standard Tag
Detail Tag
Label
Action
Description / Example
Company Name
Enter text
Specify the company or organization name to display on the label.
Example: Infraon Technologies
Brand Color
Select a color
Label
Action
Description / Example
Select fields to print on label
Select one or more fields
Select the asset fields to display on the label.
Example: Asset ID, Asset Name, Serial Number,Location, Owner, Department, or Custom Fields.
Label
Action
Description / Example
Label Border
Select a border style
Choose how the label border is displayed.
Options: Solid, Dashed, None
Corners
Select a corner style
Label
Action
Description / Example
Paper Size
Select from the dropdown
Select the paper size used for printing.
Example: A4 – 8.27 × 11.69 inches
Orientation
Label
Action
Description / Example
Top Panel Details
Label
Action
Description / Example
Job Name*
Enter a unique name for the print job.
Identifies the print job.
Example: Q2 Audit Labels. The job name is mandatory and must be unique.
Label Template
Label
Action
Description / Example
Assets
Select the Assets tab.
Displays all assets included in the Print Job and their current print status.
Printed
Label
Action
Description / Example
Status
View the status.
Displays the current status of the Print Job.
Example: Completed.
Template
Label
Action
Description / Example
Asset Status
Select the Asset Status tab.
Displays the assets available for label printing along with their current print status.
Select Asset
Label
Action
Description / Example
Total Sent
View the count.
Displays the total number of reconciliation requests sent.
Pending
Label
Action
Description / Example
Campaign Name
Enter a name for the campaign.
Identifies the reconciliation campaign.
Example: Quarterly Asset Reconciliation.
Description
Label
Action
Description / Example
ACK #
View the acknowledgment number.
Displays the unique identifier assigned to the asset reconciliation request.
Asset Name / ID
Asset Search/Scan
QR Code Customization
Assets column selection
Asset Actions
Sorting drop-down feature for Asset card view page
Asset Label Templates
What You See on the Screen
Add Templates
Template Name
Base Layout
Each layout supports a predefined number of visible fields and specific branding and formatting options.
Branding
Visible Fields
The maximum number of fields that can be selected depends on the selected layout type.
Style
Label Dimensions
The system validates the configured label dimensions against the selected paper size. If the label configuration exceeds the available paper area, the template cannot be saved until the values are corrected.
Print Jobs
How it works
A print job is processed independently in the background. You can monitor its status from the Print Jobs page without waiting for the entire printing operation to finish.
What you see on the screen
For a Completed job, the download option is available.
A Failed job provides an option to retry the processing.
A Running job displays its current progress, while a Pending job remains at 0% until processing begins.
Label Designer allows users to create and customize asset labels by defining the label layout, QR code, and required asset information.
Add a New Print Job
View Print Job
Assets
Asset Status
Asset Reconciliation
How it Works
Add Reconciliation Campaign
Active Request
Click the Filter icon
Select the code type to print.
Options: QR Code, Barcode, or both (depending on the configuration).
Select the accent color used for the label design and preview.
Configure the appearance of label corners.
Options: Rounded, Sharp
Select from the dropdown
Total Jobs
Select a template from the dropdown.
View the count.
View the template name.
Select the required asset.
View the count.
Enter a description.
View the asset details.
Invoice and Billing
Invoice and Billing enables users to manage vendor invoices and validate them against the corresponding Purchase Order (PO) and Goods Receipt Note (GRN) before approving the invoice for payment. The feature uses 3-Way Matching to compare the quantities and related information from the PO, GRN, and invoice, helping users identify mismatches before processing the invoice.
Invoice and Billing is used to create, view, search, filter, and manage vendor invoices throughout their lifecycle. It also provides visibility into invoice matching, approval, payment, and audit information.
How It Works
The invoice processing flow follows these steps:
1
Create or record a vendor invoice
2
Select the vendor
The relevant PO number is available for selection.
3
Select the Purchase Order
The related GRN number is available after selecting the PO.
4
Compare line-item quantities
The system compares the PO quantity, GRN quantity, and Invoice quantity for each line item.
5
Review the 3-Way Match status
The system displays the status as Matched, Pending, or Override Required.
6
Submit an override when required
If a mismatch is identified, an authorized user can submit an override with a reason and justification.
7
Approve the invoice
The invoice can be approved after the 3-Way Match is successful or the required override has been approved.
8
Proceed with payment and completion
For example, if a PO contains 100 units, the GRN confirms receipt of 100 units, and the invoice is for 100 units, the line item can be considered Matched. If the invoice quantity differs from the PO or GRN quantity, the system identifies the mismatch and may require an override.
When you open Invoice and Billing, the invoice listing displays the invoices available for the selected period. It provides options to create a new invoice and view or manage existing invoices.
Invoice and Billing | Basic Options
The 3-Way Matching column helps users identify whether the invoice information matches the corresponding Purchase Order and Goods Receipt Note.
Action | Line Item Column Selection
Example: If a user wants to focus on Item Name, Quantity, Unit Cost, Tax, and Line Cost, they can move these columns to Selected Columns, arrange them in the required order, and click Submit. The Line Item view will then display the selected columns according to the configured arrangement.
To create a new invoice, click Create from the Invoice and Billing screen. The Add Invoice screen is divided into three sections: Invoice Information, Line Items, and Terms and Conditions.
The Invoice Information section is used to enter the basic details required to create and process an invoice.
Add Invoice | Invoice Information
* Mandatory fields must be completed before the invoice can be created.
Click Next to move to the Line Items section.
The Line Items section is used to add and manage the individual items included in the invoice. Users can enter the item details in Form View or Grid View. The section also provides options to add new line items and import or export line-item information using CSV files.
Add Invoice | Line Item
Invoice Total
After adding the line items and applicable taxes, the invoice displays the calculated totals. Example: If the Subtotal is 24 and the applicable Tax is 3, the Grand Total is 27.
Click Next to Saves/proceeds from the Line Items section and move the user to the Terms and Conditions section.
The Terms and Conditions section allows you to select and associate the required terms and conditions with the invoice.
Add Invoice | Terms and Conditions
Click the Invoice ID from the Invoice and Billing list to open the invoice's View page. The page displays the invoice information along with its current workflow status and attachment details.
The Details section displays the details entered while creating the invoice.
View Invoice | Details
The Item and Cost Details section displays the line-item information associated with the selected invoice. It provides details about the item, quantity, cost, tax, units, and related assets.
View Invoice | Item and Cost Details
At the bottom of the Item and Cost Details section, the invoice displays the cost summary.
The Terms and Conditions section allows you to select and review the applicable terms and conditions for the invoice. The selected terms are displayed in a table with their title and available actions.
View Invoice | Terms and Conditions
The 3-Way Match validates the invoice by comparing the corresponding information from the Purchase Order(PO), Goods Receipt Note(GRN), and Invoice.
If the quantities do not correspond, the system identifies the mismatch and displays the appropriate match status. Authorized users can submit an override with a reason and justification when required.
The Related Records section displays the records associated with the invoice. The count shown for each record type indicates the number of related records available.
View Invoice | Related Records
The Approval section displays the approval progress of the invoice, including who has approved it and whether parallel approvals are configured. This helps users track the invoice approval status and identify the approvers involved in the process.
The Activity Log records the activities and changes made to an invoice, including the activity description, the user who performed the action, the date and time, and the associated field values. This helps users track invoice creation and subsequent modifications.
View Invoice | Activity Log
Label
Action
Description / Example
Filter by duration
Select / Filter
Displays invoices created or available within the selected time period.
Example: Selecting Last 60 Days displays invoices from the previous 60 days.
Search
Label
Action
Description
Line Item Column Selection
Click
When you click the Action drop-down for an invoice, Line Item Column Selection is displayed, and the Column Selection window opens.
It allows you to choose which Line Item columns should be displayed and arrange them according to your requirements.
Available Columns
Label
Action
Description
Invoice Information
Enter / Select
Enter the general information required to create the invoice, such as invoice type, vendor, Purchase Order, GRN, invoice details, and other applicable invoice information.
The available POs are based on the selected vendor, and the available GRNs are based on the selected PO.
Line Items
Add / Enter
Label
Action
Description / Example
Type*
Select
Select the type of invoice to be created. The available types include Invoice, Consignment, Credit, and Debit.
Example: Select Invoice for a standard vendor invoice.
Label
Action
Description / Example
Form View
Click
Displays the line-item information in a form-based layout, allowing users to enter or review the details of an individual item.
Label
Action
Description / Example
Terms and Conditions
Select
Select the required terms and conditions from the dropdown.
Example: Terms for Contract.
Title
Label
Action
Description / Example
Type
View
Displays the type of invoice.
Example: Invoice.
Location
Label
Action
Description / Example
Loaded Cost
View
Displays the loaded cost associated with the item.
Example: 1.
Label
Action
Description / Example
Terms and Conditions
Select
Select the required terms and conditions from the available options.
Example: Terms for Contract.
Title
View
Label
Action
Description / Example
Item
View
Displays the item being compared between the PO and invoice.
Ordered PO Qty
Label
Action
Description / Example
Purchase Requisition
View
Displays the number of Purchase Requisitions related to the invoice.
RFQs
Label
Action
Description / Example
Activity Description
View
Displays the activity performed on the invoice.
User
What You See on the Screen
Add Invoice
Invoice Information
Note: The PO and GRN relationship is particularly important for the 3-Way Matching process: the document specifies that the PO number is listed based on the selected vendor, while the GRN number is based on the selected PO.
Line Items
Terms and Conditions
View Invoice
Details
Item and Cost Details
Terms and Conditions
3-Way Match
Related Records
Approval
Activity Log
Enter
Search for the required invoice details using the search tab.
Invoice ID
View
Displays the unique identifier of the invoice.
Example: INV0012.
Type
View
Displays the type of invoice.
Example: Invoice. The available types include Invoice, Consignment, Credit, and Debit.
Vendor
View
Displays the vendor associated with the invoice.
Example: HCL.
Purchase Order
View
Displays the Purchase Order associated with the invoice.
Amount
View
Displays the total amount associated with the invoice.
Due Date
View
Displays the date by which the invoice is due.
Example: Aug 27, 2026.
3-Way Matching
View
Displays the matching result between the Purchase Order, Goods Receipt Note, and Invoice.
Example: The screen can display Mismatch or Pending.
Status
View
Displays the current status of the invoice.
Example: An invoice may be in Draft status.
Action
Edit or delete
Displays the edit and delete icon.
Select / Drag and Drop
Displays the available columns under Invoice and Billing and Invoice and Billing Custom Fields. Drag and drop the required columns from Available Columns to Selected Columns.
Selected Columns
Rearrange / Freeze
Displays the columns selected for the Line Item view. Rearrange the columns or freeze a column as needed.
Cancel
Click
Closes the Column Selection window without applying the changes.
Submit
Click
Applies the selected columns, arrangement, and column settings.
Add the items included in the invoice and provide the required item-level information, such as item name, item type, quantity, unit cost, tax, units, commodity information, remarks, and other applicable details. It uses line-item information for 3-way matching between the PO, GRN, and Invoice.
Terms and Conditions
View / Enter
Displays the terms and conditions associated with the invoice. Users can review the applicable terms and conditions while creating the invoice.
Status
View
Displays the current status of the invoice. A newly created invoice can be displayed as Draft.
Status Date
View
Displays the date associated with the current invoice status.
Location
Select
Select the location associated with the invoice.
Vendor Invoice Ref*
Enter
Enter the reference number provided on the vendor's invoice.
Example: VEN-INV-2026-0012.
Vendor*
Select
Select the vendor associated with the invoice.
Example: HCL.
PO Number
Select
Select the Purchase Order associated with the selected vendor. The available POs are based on the selected vendor.
GRN Number
Select
Select the Goods Receipt Note(GRN) associated with the selected Purchase Order. The available GRN is based on the selected PO.
Invoice Date*
Select / Enter
Specify the date on which the vendor invoice was issued.
Example: 27-Aug-2026.
GL Posting Date
Select
Specify the date on which the invoice is posted to the General Ledger.
Due Date*
Select / Enter
Specify the date by which the invoice payment is due.
Example: 27-Sep-2026.
Summary
Enter
Enter a brief summary or description of the invoice.
Example: Invoice for laptop supplies received against PO-10045.
Attachments – Vendor Invoice
Upload
Upload the vendor invoice document as an attachment. You can drag and drop the file or select Browse to upload it. Supported formats are PDF, DOC, DOCX, XLS, and XLSX, with a maximum file size of 20 MB.
Extract and Validate
Click
After uploading the vendor invoice document, click Extract and Validate to extract invoice information and validate it against the selected Purchase Order (PO).
The validation identifies matched and mismatched fields and displays warnings or errors that may require correction.
Validation Result
View
Displays the overall validation outcome.
Example: Mismatch.
Matched Fields
View
Displays the number of fields that successfully match the PO.
Example: 2 matched fields.
Warnings
View
Displays the number of validation warnings identified.
Example: 1 warning.
Errors
View
Displays the number of validation errors identified.
Example: 3 errors.
3-Way Matching — PO vs Invoice
View
Compares the PO and invoice details, including item, ordered PO quantity, GRN quantity, invoice quantity, PO amount, and invoice amount.
Match
View
Indicates whether the compared information matches.
Example: Mismatch when the item or amount does not match the PO.
Budget Validation
View
Displays the budget validation result.
Example: Not Available – No budget is linked to this PO.
Total Amount
View
Displays the PO total, invoice total, and difference.
Example: PO Total: 10, Invoice Total: 5000, Difference: 4990.
View Validation Details
Click
Opens detailed Invoice Extraction and Comparison information for reviewing the validation results.
Grid View
Click
Displays multiple line items in a tabular format, allowing users to view and manage the item information in a grid.
Add Item
Click
Adds a new line-item row to the list. Enter the required information for the newly added item.
Download Sample CSV
Click
Downloads a sample CSV file that can be used as a template for preparing line-item information for upload.
Upload as CSV
Click
Allows users to upload line-item information using a CSV file instead of entering each item manually.
Loaded Cost
Enter / View
Displays or specifies the loaded cost associated with the line item.
Order Unit
Select
Specifies the unit in which the item was ordered.
Example: Each.
Tax
Enter / Select
Specifies the applicable tax for the line item.
Conversion Factor
Enter
Specifies the conversion factor used between the order and issue units.
Prorated Cost
View / Enter
Displays or specifies the prorated cost associated with the line item.
Issue Unit
Select
Specifies the unit in which the item is issued. Example: Each.
Tax Exempt
Select
Indicates whether the line item is exempt from tax.
Model
Enter / Select
Specifies the model associated with the item.
Tax Code
Select / Enter
Specifies the tax code applicable to the line item.
Tax Exempted
View / Select
Displays or specifies the tax-exempted information for the line item.
Prorate Service
Select
Specifies whether prorating is applicable to the service or line item.
Prorated
View / Enter
Displays or specifies the prorated information for the line item.
Distributed
View / Enter
Displays the distribution information associated with the line item.
Change To Store
Select
Specifies the store-related change associated with the line item.
Item Type
Select
Specifies the type of item.
Example: Material.
Item Name
Select / Enter
Specifies the name of the item being included in the invoice.
Receipt Required
Select
Indicates whether a receipt is required for the item.
Commodity Group
Select
Specifies the commodity group associated with the item.
Quantity
Enter
Specifies the quantity being invoiced.
Example: 10.
Unit Cost
Enter
Specifies the cost of one unit of the item.
Remarks
Enter
Allows users to enter additional information or comments about the line item.
Line Cost
View / Calculate
Displays the total cost associated with the line item.
Commodity Code
Enter / Select
Specifies the commodity code associated with the item.
Related Assets
Select/Click
Click Related Assets to open the Related Asset window. The window displays the available asset list. Select the required asset from the list to associate it with the invoice line item.
Action
Delete
The delete option is available; if needed, you can delete the line item.
View
Displays the title of the selected terms and conditions.
Example: Terms for Contract.
Action
Select
Provides actions for managing the selected terms and conditions, such as Delete and View Terms and Conditions.
Delete
Click
Removes the selected terms and conditions from the invoice.
View Terms and Conditions
Click
When you click View Terms and Conditions from the Action column, a Terms And Conditions window opens. The window displays the detailed content of the selected terms and conditions.
If the terms and conditions include an attachment, the attachment is also displayed with its file name, size, and date.
The attachment can be downloaded from the Terms and Conditions window.
View
Displays the location associated with the invoice.
Summary*
View
Displays the summary or description provided for the invoice.
Vendor Invoice Ref
View
Displays the reference number provided for the vendor invoice.
Vendor
View
Displays the vendor associated with the invoice.
PO Number
View
Displays the Purchase Order associated with the invoice.
GRN Number
View
Displays the Goods Receipt Note associated with the invoice.
Invoice Date
View
Displays the date of the vendor invoice.
Example: 10 Aug 2026.
GL Posting Date
View
Displays the General Ledger posting date associated with the invoice.
Due Date*
View
Displays the date by which the invoice is due for payment.
Upload Invoice
View / Download
Displays the uploaded vendor invoice document.
Attachments – Vendor Invoice
View / Download
Displays the vendor invoice attachment associated with the invoice.
Order Unit
View
Displays the unit in which the item was ordered.
Example: Each.
Tax
View
Displays the tax value associated with the line item.
Example: 3.
Conversion Factor
View
Displays the conversion factor configured for the item.
Example: 3.
Prorated Cost
View
Displays the prorated cost associated with the item.
Example: 3.
Issue Unit
View
Displays the unit in which the item is issued.
Example: Each.
Tax Exempt
View
Displays the tax-exempt information configured for the item.
Model
View
Displays the model associated with the item.
Tax Code
View
Displays the tax code associated with the item.
Tax Exempted
View
Displays whether the item has been exempted from tax.
Example: false.
Prorate Service
View
Displays the prorate service information associated with the item.
Prorated
View
Displays the prorated information for the line item.
Distributed
View
Displays the distribution information associated with the item.
Change To Store
View
Displays the store-related information associated with the item.
Item Type
View
Displays the type of item.
Example: Material.
Item Name
View
Displays the name of the item.
Example: Dell.
Receipt Required
View
Displays whether a receipt is required for the item.
Commodity Group
View
Displays the commodity group associated with the item.
Quantity
View
Displays the quantity included in the invoice.
Example: 12.
Unit Cost
View
Displays the cost per unit of the item.
Example: 2.
Remarks
View
Displays any remarks entered for the line item.
Line Cost
View
Displays the total cost for the line item.
Example: 24.
Commodity Code
View
Displays the commodity code associated with the item.
Related Assets
View
Displays the assets associated with the line item.
Example: Related Assets (0/12) indicates the related asset information for the item.
Displays the title of the selected terms and conditions.
Example: terms for contract - terms and conditions.
Action
Click
Provides actions for managing the selected terms and conditions, such as Delete and View Terms and Conditions.
View
Displays the quantity ordered in the Purchase Order.
GRN Qty
View
Displays the quantity recorded in the Goods Receipt Note (GRN).
Invoice Qty
View
Displays the quantity mentioned in the vendor invoice.
PO Amount
View
Displays the amount recorded for the item in the Purchase Order.
Invoice Amount
View
Displays the amount mentioned for the item in the invoice.
Match
View
Displays the comparison result for the item.
View
Displays the number of Requests for Quotation (RFQs) related to the invoice.
Purchase Order
View
Displays the number of Purchase Orders related to the invoice.
GRN
View
Displays the number of Goods Receipt Notes (GRNs) related to the invoice.
Contract References
View
Displays the number of contract references associated with the invoice.
View
Displays the name or username of the person who performed the activity.
Date and Time
View
Displays when the activity occurred.
Changed Fields
View
Displays the invoice fields affected by an update and their recorded values.
Created Details
View
Displays the invoice information recorded when the invoice was created, such as Invoice ID: INV0011, Status: Draft, Vendor: HCL, Type: Invoice, and Due Date: Aug 31, 2026.
Vendor
A centralized hub for managing information about software vendors associated with the organization's IT environment.
What you see on the screen
The main screen displays a comprehensive list of vendors, providing a clear overview of the vendor landscape.
Details | Basic information
Label
Action
Search
The Infraon platform offers two distinct vendor roles.
This table summarizes the specific actions that Vendor Admin and Site User roles can perform for each module in the Infraon platform.
To manage vendor information within the Infraon Infinity portal, navigate to the Infraon Configuration section. From there, select "Infraon Portal" and then choose the "Vendor" module.
Select the Add Vendor optionlocated at the top right corner of the page, and add the below details respectively:
Vendor Name
Click the + icon in the Vendor option on the top right corner.
The vendor creation form includes three tabs: Organization Details, Address, and Representatives.
Refer to the table below for guidance on filling in each field.
Organization Details | Add Vendor
Click Next to proceed to the next tab – Organization Address.
Add Address| Add Vendor
to view how to add basic address details.
Follow the table below to add Contact, GSTIN, and Bank Details.
Other Details | Add Address
Once the address is added, users can select Edit and Delete to change the vendor’s address.
Click Next to proceed to the next tab – Representatives.
The Representatives tab is the third and final step in the "Add Vendor.” This section allows you to assign individuals representing the vendor organization in the system. These users can access the portal (if login is enabled) and perform actions based on their assigned roles. Adding representatives ensures clear accountability and secure access control for vendors.
To add a representative, click + AddUser and complete the necessary details. The login can be enabled or disabled based on the requirement. Below is a structured table explaining each label in the tab:
Once done, click on Submit to save the Vendor.
The Shipment section in the Vendor details page provides end-to-end visibility into shipments associated with the vendor’s Purchase Orders. Users can view shipment details such as shipment number, shipment status, destination, linked Purchase Order, shipped asset count, and shipment timeline.
Shipment-related documents, including E-Way Bill, Proforma Invoice, and Delivery Challan, are also available based on user permissions and shipment status.
Label
Action
Description / Example
User
Vendor Admin
✔️
✔️
✔️
✔️
❌
Site User
❌
❌
❌
✔️
❌
Organization
Vendor Admin
❌
❌
❌
✔️
❌
Site User
❌
❌
❌
✔️
❌
Organization Location
Vendor Admin
✔️
✔️
✔️
✔️
❌
Site User
✔️
✔️
✔️
✔️
❌
Dashboard
Vendor Admin
❌
❌
❌
✔️
❌
Site User
❌
❌
❌
✔️
❌
My Profile
Vendor Admin
❌
✔️
❌
✔️
❌
Site User
❌
✔️
❌
✔️
❌
Audit
Vendor Admin
❌
❌
❌
✔️
❌
Site User
❌
❌
❌
✔️
❌
History
Vendor Admin
❌
❌
❌
✔️
❌
Site User
❌
❌
❌
✔️
❌
Holiday
Vendor Admin
✔️
✔️
✔️
✔️
❌
Site User
✔️
✔️
✔️
✔️
❌
Password Policy
Vendor Admin
✔️
✔️
✔️
✔️
❌
Site User
✔️
✔️
✔️
✔️
❌
Leaves
Vendor Admin
✔️
✔️
✔️
✔️
❌
Site User
✔️
✔️
✔️
✔️
❌
Knowledge Base
Vendor Admin
❌
❌
❌
✔️
❌
Site User
❌
❌
❌
✔️
❌
CMDB
Vendor Admin
❌
❌
❌
✔️
❌
Site User
❌
❌
❌
✔️
❌
Software License
Vendor Admin
❌
❌
❌
✔️
❌
Site User
❌
❌
❌
✔️
❌
Vendor
Vendor Admin
✔️
✔️
✔️
✔️
❌
Site User
❌
❌
❌
✔️
❌
Contract
Vendor Admin
❌
❌
❌
✔️
❌
Site User
❌
❌
❌
✔️
❌
Project
Vendor Admin
❌
❌
❌
✔️
❌
Site User
❌
❌
❌
✔️
❌
Purchase Order
Vendor Admin
❌
❌
❌
✔️
❌
Site User
❌
❌
❌
✔️
❌
Status (Draft, New, and Publish)
Vendor Location
Web URL
Contact Person
Email
Phone Number
Description
Once the changes are made to satisfactory, click “Save” to proceed.
Text Input
Enter the official name of the vendor
Example:ABC Technologies.
Contact Person*
Text Input
Provide the full name of the primary contact person for this vendor
Example: John Doe.
Email*
Text Input
Provide a valid email address for vendor communication.
Example: vendor@example.com.
Phone Number
Country Code Dropdown + Input
Select the country code and enter the vendor’s contact number.
Example: +91 9876543210.
Risk
Dropdown
Select the vendor risk level: Low, Medium, High, or Critical. This helps categorize vendors based on compliance or operational risk.
Status
Dropdown
Indicates vendor onboarding stage.
Options: Draft (Creation), New (Open), Publish (Active).
Draft is the default for newly added vendors.
Country*
Dropdown
Select the vendor’s country of operation.
Example: India.
Enable Login
Toggle
Enables login access for the vendor representative. Only allow this if the vendor interacts directly within the system.
Password
Text Input
Add an eight-letter password for login.
User Approval
Select from the drop-down.
Options Include: Vendor Admin/ Site User.
Web URL
Text Input
Add the vendor’s official website URL.
Example: https://www.vendorexample.com.
Vendor ID Number
Text Input
Provide a unique internal/external identifier for the vendor, if applicable.
Example: VEN1024.
Date of Incorporation
Date Picker
Select the official incorporation date of the vendor organization from the calendar dropdown.
ID Type
Dropdown
Choose a supported ID type: Aadhar, Passport, or PAN.
This is used to validate the vendor's proof of identity.
ID Number
Text Input
Input the actual number based on the selected ID type.
Upload ID
Upload (Drag and Drop/Click)
You can upload a scanned copy or a photo of the proof of the selected ID. The file formats supported are PNG, JPEG, and JPG.
Add
Click Button
Clicking Add confirms the ID details and uploads them. This action is mandatory to save proof data before proceeding to the next step.
MSMED Details
Toggle
Enable if the vendor falls under the MSMED (Micro, Small & Medium Enterprises Development) Act.
MSMED Status
Dropdown (Visible only if enabled)
Select status: Low, Medium, High, or Critical, based on the MSMED evaluation of the vendor.
MSMED Category
Dropdown (Visible only if enabled)
Select whether the vendor is recognized under MSMED: Yes or No.
URN
Text Input
Enter the MSMED-provided Unique Registration Number (URN) if applicable. Example: MSMED12345.
Email ID of the vendor's contact person. Example: vendor@example.com
Phone Number
Select country code & enter
Provide the vendor contact number, including the country code.
Example: +91 98765XXX10
ID Number (GSTN)
Enter alphanumeric ID
GST identification number for the vendor. This is required for taxation purposes.
Example: 27AAGPM1234C1Z5
Upload ID (GSTN)
Upload document
Upload the supporting document for the entered GSTN.
Accepted formats: PNG, JPEG, JPG
IFSC Code
Enter IFSC code
Unique code to identify the vendor’s bank branch for domestic transfers.
Example: SBIN0000456
Bank Name
Enter bank name
Name of the bank where the vendor holds their account.
Example: State Bank of India
Currency
Select from the dropdown
Currency in which the vendor prefers payment. Default value shown: INR.
Beneficiary Name
Enter name
Name of the vendor account holder (must match bank records).
Example: EverestIMS Technologies Pvt Ltd
Account Number
Enter bank account number.
The vendor’s bank account number is used to receive payments.
Example: 123456789012
Re-enter Account Number
Re-enter bank account number.
The confirmation field is used to verify the vendor’s account number to avoid payment errors.
Provide a valid email address. This will be used for login if enabled.
Example: emily@example.com
Phone Number
Select Country Code + Type
Enter the representative’s mobile number.
Example: +91 9876543210
User Type*
Select from the dropdown.
Define the user’s role within the organization. Roles may vary depending on access level.
Enable Login
Toggle ON/OFF
Enable this if the user needs access to the system. Enabling this allows you to set credentials.
Password*
Type
Set a secure password for the user if login is enabled.
Site
Select from the dropdown
Assign the user to a specific site (if applicable).
Example: Bangalore HQ
Displays the unique identifier of the shipment, such as #SHIP0017.
Shipment Status
View
Displays the current status of the shipment, such as Completed or Delivered.
Destination
View
Displays the delivery address specified for the shipment.
Purchase Order
View
Displays the Purchase Order linked to the shipment, such as #PO-D-0341.
Asset Count
View
Displays the number of assets included in the shipment, such as 50 Assets.
Shipment Timeline
View
Displays the shipment’s progress and status updates throughout its lifecycle.
E-Way Bill
View
Allows users to upload, view, download, or delete the E-Way Bill based on permissions and shipment status.
Proforma Invoice
View
Allows users to manage the Proforma Invoice associated with the shipment.
Delivery Challan
View
Allows users to manage the Delivery Challan associated with the shipment.
History
View
Displays the shipment history and records of actions performed on the shipment and its documents.
Create / Edit / Cancel
View
Allows authorized users to create, modify, or cancel shipments based on their permissions and the current shipment status.
Audit / History Log
View
Records shipment and document-related activities for tracking and auditing purposes.
Read-only State
View
Shipment information becomes read-only when the shipment reaches a locked status according to the configured business rules.
Click to search, enabling efficient navigation through the vendor list.
Filter
Filter can be added based on the field (Vendor Name, Status, Location, Web URL, Contact Person, Email ID, and Phone Number) and select the respective condition from the drop-down box below.
Vendor Name
To quickly identify the vendor.
Status
Indicates the vendor's current standing (active, inactive, etc.).
Location
View the vendor's physical location.
Web URL
Access the vendor's website with a single click.
Contact Person
Identify the designated point of contact at the vendor company.
Email ID & Phone Number
Facilitate easy communication with the vendor.
Actions
Edit
To make changes to the vendor information.
Delete
Click to delete a specific vendor information from the inventory.
Role Name
Description
Site User
Add, edit, delete, and view organization locations, holidays, password policies, and leaves.
Upload the organization logo in PNG, JPEG, or JPG format. The maximum size allowed is 20 MB, with an aspect ratio of 4:4.
Label
Action
Description / Example
Contact Person Name
Enter the full name
Name of the individual representing the vendor.
Example: Rahul Sharma
Email Address
Label
Action
Description / Example
Name*
Type
Enter the full name of the representative.
Example: Emily Davis
Email*
Shipment
View
Displays all shipments associated with the vendor’s eligible Purchase Orders.
Shipment Number
Roles
Instructions to Add Vendor
Add Vendor
Fields marked with an asterisk (*) are mandatory to fill.
Click on “New Address” to add multiple addresses to the vendor.
Fields marked with an asterisk (*) are mandatory to fill.
Shipment
Example
A vendor can open the Shipment section and view #SHIP0017, its Completed status, destination, linked #PO-D-0341, and 50 Assets. The user can also access the associated E-Way Bill, Proforma Invoice, and Delivery Challan, if permitted.
Upon adding an asset to the Infraon portal, users will be presented with a default view showcasing key details about the asset. This information is a quick reference point and can be customized later to fit specific needs.
Asset Properties | Details
Label
Description/ Example
Asset Name
From the Asset grid page, filter the category SDH / PDH; on the filtered grid page, click on the Device Name or IP to view additional information. There are multiple sub-views with all the necessary information about the device. These are:
Inventory information includes basic details, additional properties, Custom Fields, and Health Summary.
The following section breaks down the details:
Device Details
Hostname
Device Type
Tags (Click on ‘Edit’ to add or remove the tags)
Audit the user login and logout entries within the asset management module. This allows IT administrators to identify which users have accessed specific IT assets (laptops, desktops) and when. This information can help troubleshoot access issues, monitor asset usage, and maintain security compliance.
The inventory agent gathers data on login and logout activity for each asset at regular intervals (inventory updates) and presents this data within the user logins and logouts module.
The asset details page displays a user login and logout cart. This module details the profile name, number of logins, and number of logouts associated with each user profile for the selected asset. Additionally, a date filter allows technicians to refine the displayed data for a specific timeframe.
The following section breaks down the details:
Asset History: Track an asset's entire journey, from initial purchase through use, maintenance, and eventual disposal.
Purchase Order Details: View crucial information from the purchase order, including the date, cost, supplier, and specifications.
Annual Maintenance Contract (AMC): Monitor active AMCs associated with the asset, displaying coverage period, service provider, and key terms.
Warranty Information: Access comprehensive warranty details like start/end dates, covered components, and claims history.
Displays detailed information about the software, including the software name, version, and license details, such as whether the license is purchased or subscription-based and its expiration date.
This section provides detailed OS-level and system metadata for the selected asset.
This section displays a complete list of applications installed on the selected asset. Users can view details, perform quick searches, or apply filters based on various fields.
SBOM provides a consolidated view of applications, software components, assets, and vulnerability information, enabling users to review software composition and assess associated risks.
SBOM | Top Panel Details
Label
Action
Description / Example
Software Bill of Materials (SBOM) provides an inventory of the software applications, components, and dependencies identified across assets. It helps users understand what software is installed, which components are associated with each application, and the vulnerabilities identified in those components. The SBOM data is presented at the organization level in the SBOM module.
How does SBOM work?
SBOM data is collected from scanned assets and used to identify applications and their associated software components and vulnerabilities. For example, if an asset has 7-Zip installed, the SBOM inventory can show the application, its version and vendor, the components or dependencies associated with it, and the vulnerabilities identified for those components. Users can then select the application to view its detailed information.
What do you see on the screen?
When you open the SBOM module, the SBOM Inventory page is displayed. The page contains summary cards at the top, followed by the inventory table. The left navigation also provides access to Inventory and Vulnerabilities.
Basic Details
Label
Action
Description/Example
Column Details
The inventory table provides application, asset, component, vulnerability, and scan information, allowing users to identify the software installed across scanned assets.
Label
Action
Description/Example
Column Details: Action Icons
Label
Action
Description/Example
SBOM Inventory Detail
When View is selected, the SBOM Inventory Detail sidebar opens on the right and provides detailed information about the selected application, its host, scan details, and associated vulnerabilities.
Label
Action
Description/Example
Components
When View Components is selected for an application, the Components page opens and displays the software components and dependencies associated with the selected application. Users can switch between All and Application views and choose either Grid View or Graph View to examine the component information.
Component Details
The component details provide information about the component, its source, licensing, dependencies, and other SBOM metadata.
Label
Action
Description/Example
SBOM Vulnerabilities provides a centralized view of vulnerabilities identified across the software components and applications discovered in scanned assets. It helps users review vulnerability severity, CVSS scores, fix states, affected packages, and scan information to support vulnerability assessment and remediation.
How does Vulnerability work?
Vulnerabilities are identified from the software components recorded in the SBOM data of scanned assets. The identified CVEs are consolidated in the Vulnerabilities page, where users can review the vulnerability details and prioritize them based on severity and fix state.
The SBOM Vulnerability table is documented with the columns CVE ID, Application Name, Package, Version, Severity, CVSS Score, Fix State, Scan Time, and Actions.
What do you see on the screen?
When you open SBOM > Vulnerabilities, the SBOM Vulnerabilities page is displayed. The page provides an overview of the identified vulnerabilities followed by the vulnerability inventory table. Users can review vulnerability information and select the available action to view detailed information about a specific vulnerability.
Column Details
The vulnerability table provides detailed information about each identified CVE, including the affected application and package, vulnerability severity, CVSS score, fix state, and scan information.
Label
Action
Description/Example
Action Icons
The Actions column allows users to open the detailed information of a selected vulnerability for further investigation.
Overview
Label
Action
Description/Example
Affected Software
Label
Action
Description/Example
CVE Lifecycle
Label
Action
Description/Example
Affected Software / Affected Product
Label
Action
Description/Example
Endpoint
Label
Action
Description/Example
The detailed specification confirms the CVE hero information, affected software, package information, description, data source, and references shown in the sidebar.
The SSL Certificates section displays SSL certificates discovered for a Windows device through the . The agent periodically scans the Windows certificate stores and configured endpoints to collect certificate information, synchronizes the discovered data with the Infraon server, and displays it for monitoring and compliance.
The dashboard provides an overview of all discovered certificates, their validity status, expiry information, and storage location. It also enables you to search, filter, sort, and review certificate details to proactively identify certificates that are nearing expiration or have already expired.
The SSL Certificates dashboard displays discovered SSL certificates for the selected Windows asset, along with summary cards, search, and certificate details for monitoring certificate validity and expiry.
SSL Certificate | Asset Information
Label
Action
Description / Example
The Gate Pass Records section displays the gate passes generated for the selected asset through the Move process. It provides a read-only view of the gate passes associated with the asset.
The Gate Pass Records section displays the gate passes associated with the selected asset.
Gate Pass | Basic Details
Label
Description / Example
Gate Pass | Status
The gate pass status is displayed as a status pill.
Status
Description
When multiple gate passes are available, the most recently created gate pass appears first.
Displays complete hardware information for all asset components. The data includes information collected by the Inventory Agent, as well as any additional details or custom properties added manually.
All hardware components are organized into tabs (e.g., CPU, Memory, Disk, Interface). Selecting a tab displays only the corresponding component details.
The hardware details include:
Shelf Number
Slot Number
Slot Name
Card Name
If additional properties or custom fields are configured for hardware components, they are displayed alongside the agent-collected data in the respective tab.
Search – Click to search within the selected hardware component.
Export – Click to download the hardware inventory in CSV, Excel (XLS), or PDF format.
Displays battery-related information for the asset, including:
Battery Health Percentage (calculated value)
Battery Status
Battery Chemistry
Cycle Count
Displays the overall system performance score based on hardware evaluation. The score ranges from 1.0 to 9.9, where higher values indicate better performance.
The overall WEI score is derived from the lowest score among the evaluated components.
Details Available:
The following performance metrics are displayed:
Processor Score: Performance of the CPU
Memory Score: Performance of system memory (RAM)
Graphics Score: Desktop graphics performance
3D Graphics (Direct3D) Score: Gaming and 3D rendering performance
This displays topology connections for the selected NE. Devices are marked in red/green based on their availability. Mouse over an asset to view details. Use action icons to navigate through, zoom in, and zoom out topology connections.
The following section breaks down the details:
Grid View – Click to view in a tabular format.
Map View – Click to view in a map view format.
Node – Click to see the below details:
Host Name
The Activity Log meticulously tracks asset changes, providing a comprehensive history of each asset. It records all modifications made by technicians, including changes to city, country, criticality, connection protocol, device credentials, and download job details.
Entries are organized by date and time, allowing for easy monitoring and auditing of asset history. This detailed log ensures that all key actions and updates are documented, facilitating better management and oversight of IT assets.
Asset ID
Device Type
IP Address
Make
Active Version
Ci Name
Model
Owner Details
Name
Mail ID
Mobile number
Edit – Click to make changes.
User Details
Name
Mail ID
Edit – Click to make changes.
Deallocate – Click to allocate a new user.
Resend Email – Click to resend the e-mail.
Attachment
Choose from the categories (Default, Procurement, Service, Retirement Documents).
Add – Click to add new attachments.
Asset Configuration
Creation Time
Last Update Time
Login Profile
Login Profile ID
Port Name
Port State
Port Number
SFP Installed
SFP Type
Expected Hardware
Installed Hardware
Serial Number
State
Design Capacity
Estimated Charge Remaining
Estimated Run Time
Full Charge Capacity
Device ID and Battery Name
Current Status
Disk Score: Performance of the primary disk
Last Assessment Time: Date and time when the score was last calculated
IP Address
Make
Model
Device Type
EMS Name
Firmware Version
Region
State
City
Location
Edge – Click to see the below details:
Description
Source IP
Source Device
Source Port
Destination Ip
Destination Device
Destination Port
Layer Rate
Services (Click to redirect to the Services page)
Export – Click to create a PDF of the current topology view.
Zoom Keys - Icons can be used to navigate through the topology diagram.
Arrow Keys - Icons can be used to navigate through the topology diagram.
Identify the asset with a user-friendly name.
Asset ID
A unique identifier is assigned to the asset within the system for easy tracking and reference.
IP Address
View the network address associated with the asset.
Status
Quickly understand the asset's current operational state (e.g., Active, Inactive, or Under Maintenance).
Manufacturer
Identify the company that produced the hardware asset.
OS Version
View the operating system version installed on the asset.
System SKU Number
Displays the unique System Stock Keeping Unit (SKU) number fetched directly from the discovery agent. This field helps in identifying the specific hardware model and configuration provided by the manufacturer. The value is auto-populated by the inventory agent when the asset is discovered and cannot be edited manually.
Example: 15AB-1234-XYZ
Actions
Edit
Modify any of the asset's details to ensure accuracy and reflect any changes.
Delete
Remove the asset from the inventory if it's no longer needed.
Add Owner
Assign a specific user as the asset's owner, facilitating responsibility and ownership tracking.
Schedule RDP
This functionality is available depending on the specific configuration. It allows users to schedule a remote desktop connection to the asset (useful for managing Windows-based devices remotely).
Add Owner
Click Add Owner to assign a user as the asset owner.
Assigns a user as the asset's owner for ownership tracking. If the assigned user is later marked inactive, they are automatically removed from the asset.
The change is reflected in the asset fields and recorded in the activity log.
Add User
Click Add User to assign a user to the asset.
Assigns a user as the asset user (used by). If the assigned user is marked inactive, they are automatically removed from the asset, ensuring assets remain linked only to active users.
All changes are tracked in the activity log.
Label
Description/ Example
No of Logins
Displays the total number of times a user profile has accessed this specific IT asset.
No of Logouts
Displays the number of times a user profile has ended a session on the IT asset.
Profile Name
Label
Description
Example
Alias
A custom label or nickname assigned to the asset (if configured)
EIMS-Laptop-BGLR
Build Number
Label
Action
Description / Example
Search
Type at least three characters to perform a search
Performs a global keyword search across application name, vendor, and type fields.
Filter
Critical
View
Displays the total number of Critical vulnerabilities identified across the scanned assets.
High
View
Search
Search
Allows users to search the inventory using a keyword.
Filter
Filter
Application Name
View
Displays the name of the application identified in the SBOM data.
Example: Google Chrome
Version
View
View
View
Opens the SBOM Inventory Detail sidebar for the selected application.
The sidebar provides application details, host information, scan information, vulnerability summary, and the associated CVE list.
View Components
Navigate
Application Details
View
Displays the application Version, SBOM Format, Components, and Vendor.
Host Info
View
All
Select
Displays all components available for the selected SBOM inventory record, including associated dependencies.
Application
CVE ID
View
Displays the unique identifier of the vulnerability.
Example: CVE-2024-1234
Application Name
View
Overview
View
Displays the overview of the selected vulnerability.
CVS Breakdown
Application Name
View
Displays the name of the application affected by the vulnerability.
Example: Antigravity IDE (User)
Hostname
View
Published
View
Displays the date when the CVE was originally published.
Example: Sep 14, 2019
NVD Updated
View
Product
View
Displays the affected product.
Example: notepad++
Vendor
View
Hostname
View
Displays the hostname of an endpoint associated with the affected software.
Example: 317-Ayush-EIMS
IP Address
View
Total Certificates
Click the card to view all discovered certificates.
Displays the total number of SSL certificates discovered for the selected Windows asset.
Example: 57.
Valid Certificates
Gate Pass ID
Displays the gate pass's unique identifier.
Status
Displays the gate pass's current status.
Process
Draft
The gate pass is in draft status.
Pending Approval
The gate pass is awaiting approval.
Approved
Sections
Details
User Logins/Logouts
What you see on the screen
Asset Lifecycle
Software
Operating System Details
The platform agent automatically fetches these fields from the device.
Application (Installed Software)
SBOM
SBOM Inventory
Vulnerability
Use case:
For example, if OpenSSL 1.1.1 is installed on an asset and a vulnerability such as CVE-2024-1234 is identified, the Vulnerabilities page displays the CVE, affected application and package, severity, CVSS score, fix state, and scan time. Users can select View to open the detailed vulnerability information.
SSL Certificates
The SSL Certificates section is available only for Windows devices discovered using the Inventory Agent. It is not available for manually added assets.
What you see on the screen
Gate Pass Records
Gate passes can only be created through an IMACD process. The Gate Pass Records section does not provide options to create, edit, or delete gate passes.
What you see on the screen
A newly generated gate pass is displayed in the asset's Gate Pass Records section after it is generated through an IMACD Move process.
Hardware Inventory
Battery Details
Windows Experience Index (WEI) Score
My Topology
Activity Log
Export - Audits can be downloaded in CSV, Excel, or PDF formats using the respective action icon.
This will typically be the user's network login name or alias.
Filter
The date filtering function allows technicians to narrow down the displayed data to a desired timeframe.
The Windows OS build number, indicating the system's software version level
22631
Device Type
Indicates whether the asset is a laptop, desktop, virtual machine, or other type of device.
Laptop
Last Boot-Up Time
Date and time when the asset was last restarted
2024-07-01 11:05:35
Organization
The name of the owning organization as registered in the platform
LENOVO
OS Installed By
Name of the user or technician who installed the OS
LENOVO
Product ID
The Windows product ID is assigned to the OS
00330-80000-00000-AA121
System Directory
The directory path of the operating system's system files
C:\WINDOWS\system32
Version
The full version of the installed operating system
10.0.22631
Windows Directory
The root directory of the Windows OS installation
C:\WINDOWS
Boot Device
The primary drive used to boot the operating system
C:
Description
Optional admin-entered notes or metadata about the asset
Windows 11 machine for R&D
Hostname
The network name assigned to the asset
093-Nithin-EIMS
Manufacturer
Hardware manufacturer of the device
Microsoft Corporation
OS Install Date
Date and time the operating system was installed
2023-07-17 11:02:03
OS Name
Full name of the operating system
Microsoft Windows 11 Pro
Product Key
Unique license key used to activate the Windows OS
TY4GC-JDJH7-VJ2WF-DY4X9-HCFC6
System Drive
Drive where the OS is installed
C:
Virtual Memory
Total amount of virtual memory available to the system
23.33 Gbytes
Select a field → Choose a condition → Enter a value
Applies field-specific filters. Supported
Fields: Name, Type, Vendor, Version. Conditions: equal to, not equal to, contains, not contain, in, not in.
Name
View only
Displays the name of the installed application.
Example: Cisco Webex Meetings
Vendor
View only
Displays the software vendor/publisher.
Example: Fortinet Technologies Inc
Type
View only
Indicates the software type.
Example: Other
Version
View only
Displays the installed version number.
Example: 7.0.0.9493
Install Date
View only
Shows the installation date of the application.
Example: 2023-11-07
Action
Click the delete icon to remove the application
Manually deletes the software record from the asset, typically used for incorrect or outdated entries.
Displays the total number of High vulnerabilities identified across the scanned assets.
Medium
View
Displays the total number of Medium vulnerabilities identified across the scanned assets.
Low
View
Displays the total number of Low vulnerabilities identified across the scanned assets.
Risk Distribution
View
Displays a stacked bar chart representing the distribution of vulnerabilities across different severity levels.
Total Apps
View
Displays the total number of distinct applications identified across the scanned assets.
Total Assets
View
Displays the total number of assets that have been scanned.
Allows users to refine the inventory results using Field, Condition, and Value.
Field
Select
Select the inventory field on which the filter should be applied.
Condition
Select
Select the required condition to determine how the field should be matched.
Value
Enter/Select
Enter or select the value to be matched against the selected field and condition.
Displays the version of the application.
Example: 124.0.6367.91
Vendor
View
Displays the vendor associated with the application.
Example: Google LLC
Hostname
View
Displays the hostname of the asset where the application was identified.
Example: workstation-01
IP Address
View
Displays the IP address associated with the host.
Example: 192.168.1.50
Components
View
Displays the number of software components or dependencies identified for the application.
Example: 312
Critical
View
Displays the number of Critical vulnerabilities associated with the application.
High
View
Displays the number of High vulnerabilities associated with the application.
Last Scanned
View
Displays the date and time when the application was last scanned.
Actions
Perform action
Provides actions to view inventory details, view components, and download the SBOM for the selected application.
Navigates to the Components page for the selected application, where users can view the identified components and switch between the available All and Application views and different display modes.
Displays the Hostname, IP Address, and Host ID associated with the application.
Scan Info
View
Displays the Generated Time and Last Scanned Time.
Vulnerability Summary
View
Displays the Critical, High, Medium, and Low vulnerability counts for the application.
CVE List
View
Displays the CVEs identified for the application along with their severity information.
Select
Displays components associated specifically with the selected application.
Version
View
Displays the version of the component.
Example: 1.1.1
Type
View
Displays the type of software component.
Supplier
View
Displays the supplier or organization that provides the component.
Origin
View
Displays the origin or source from which the component was obtained.
License
View
Displays the license associated with the component.
Description
View
Displays a description of the software component and its purpose.
Release Date
View
Displays the release date of the component version.
Checksum
View
Displays the checksum associated with the component for identification or integrity verification.
Dependencies
View
Displays the dependencies associated with the component.
Properties
View
Displays additional properties or metadata associated with the component.
Notes
View
Displays additional notes or information provided for the component.
Package URL (PURL)
View
Displays the Package URL (PURL) that uniquely identifies the software package.
Grid View
Select
Displays component information in a structured grid/table format, allowing users to view the available component details in columns.
Graph View
Select
Displays the components and their relationships in a graphical representation, making it easier to understand component and dependency relationships.
Displays the application associated with the vulnerability.
Example: Google Chrome
Package
View
Displays the software package affected by the vulnerability.
Example: openssl
Version
View
Displays the version of the affected package.
Example: 1.1.1
Severity
View
Displays the severity level of the vulnerability.
Example: Critical, High, Medium, or Low
CVSS Score
View
Displays the Common Vulnerability Scoring System (CVSS) score assigned to the vulnerability.
Example: 8.1
Fix State
View
Displays the current fix status of the vulnerability.
Example: Fixed / Unfixed
Scan Time
View
Displays the date and time when the vulnerability was identified during the scan.
Actions
Perform action
Provides actions available for the selected vulnerability, such as viewing its detailed information.
Affected Software
View
Displays the applications and software packages affected by the vulnerability.
Endpoints
View
Displays the number of endpoints affected by the vulnerability.
CVSS Breakdown
View
Displays the CVSS vector and individual metrics used to calculate the vulnerability's CVSS score.
Displays the potential impact on the confidentiality of information.
Example: High
Integrity
View
Displays the potential impact on the integrity of information.
Example: High
Availability
View
Displays the potential impact on the availability of the affected system or resource.
Example: High
Displays the hostname of the endpoint where the affected application is identified.
Example: 317-Ayush-EIMS
Package
View
Displays the software package affected by the vulnerability.
Example: Scintilla
Version
View
Displays the version of the affected package.
Example: 5.5.4
Displays the date when the CVE information was last updated in the NVD.
Patch Released
View
Displays whether a patch has been released for the vulnerability.
Example: Pending
Remediated
View
Displays whether the vulnerability has been remediated.
Example: Pending
Description
View
Displays the description of the vulnerability.
Example: SciLexer.dll in Scintilla in Notepad++ (x64) before 7.7 allows remote code execution or denial of service via Unicode characters in a crafted .ml file.
Reference(s)
View
Displays the available reference links associated with the CVE.
Example: Packet Storm, GitHub, Notepad++ download page, and Scintilla history.
Displays the vendor associated with the affected product.
Example: notepad-plus-plus
Version Range
View
Displays the affected version range.
Example: * – 7.7
Platform
View
Displays the platform associated with the affected product, when available.
Product
View
Displays additional affected products or components.
Example: scintilla
Displays the IP address associated with the affected endpoint.
Example: 172.31.0.1, 10.0.7.240
Application
View
Displays the application identified on the affected endpoint.
Example: TortoiseGit 2.17.0.2 (64 bit)
Hostname
View
Displays the hostname of the affected endpoint.
Example: 317-Ayush-EIMS
IP Address
View
Displays the IP address associated with the endpoint.
Example: 172.31.0.1, 10.0.7.240
Application
View
Displays the application associated with the vulnerability on the endpoint.
Example: Antigravity IDE (User)
Click the card to filter valid certificates.
Displays the number of certificates that are currently valid and filters the grid to show only valid certificates.
Example: 48.
Expiring Certificates
Click the card to filter certificates nearing expiration.
Displays the number of certificates that are approaching their expiry date and filters the grid accordingly.
Example: Expiring in next 30 days.
Expired Certificates
Click the card to filter expired certificates.
Displays the number of expired certificates and filters the grid to show only expired certificates.
Example: 9.
Search
Enter a keyword to search certificates.
Search certificates using the Subject, Issuer, or Certificate Description.
If no matching records are found, the system displays a No SSL Certificate Present message.
Subject / Issuer
View the certificate subject and issuing authority.
Displays the certificate subject and issuer information.
Filter can be added based on the Field and Condition from the drop-down box below.
Go to the Infraon platform page; click the Topology -> Topological Link on the left panel.
Navigate to Add -> Add Topology, enter the details, and click Submit.
Go to the Infraon platforn page; click the Topology -> Topological Link on the left panel.
Navigate to Add -> CSV File
Download the CSV file and enter the details required.
Upload the same CSV file and click Next.
Source Port
Select from the respective drop-down box.
Destination Node
Select from the respective drop-down box.
Destination Port
Select from the respective drop-down box.
Layer Rate
Select the OSI (Open System Interconnection) layer.
Direction
Bi-directional/ Unidirectional
Ring Name
Select a Ring for the Topology.
Confirm that the selected column matches and click Import.
Validate the CSV file and click Proceed with valid records.
Add
For new topologies, you can choose the guided ’Add topology’ option or manually import data from a CSV file.
To add a new Topology.
Export
Choose your export format: Download the topology as a separate CSV file or an Excel-compatible XLS file.
To Export the configuration
Edit
To Edit the changes to a Topology.
Trace Test
Click to enter the details in the respective call-out boxes. (Link Name, Description, Source Node, Source Port, Destination Node, Destination Port, Layer Rate, Direction, Ring Name)
It uses trace data to improve assertion capabilities and validate relationships between two nodes.
Label
Action/ Description
Link Name
Add a name for the Link.
Description
Provide a brief description of the topology.
Source Node
Steps to add a topology
Method 1: Manually
Method 2: CSV File
To Export the configuration, click on the 'Export' icon at the page’s top right corner.
Select from the respective drop-down box.
Add Contract
Infraon Infinity platform supports four contract types: Procurement, Software and Maintenance, System Integration and Project, Lease, Service, and Other Contracts. Follow the steps below to add a new contract seamlessly:
Navigate to the ‘New Contract’ button located at the top-right corner of the page.
Choose the appropriate category for the new contract from the predefined options.
Add Procurement Contract
The Procurement Contract type allows users to create and manage contracts related to procurement activities. Users can define contract details, vendor and ownership information, contract validity, notification settings, terms and conditions, and associated purchase items.
Add Procurement Contract | Basic Details
Label
Action
Description
Click the Next button to move to the Item Details section.
Add Procurement Contract | Item Details
Label
Action
Description
Click the Submit button to save the created contract.
The Support and Maintenance Contract type allows users to manage contracts related to asset support, maintenance services, warranties, and Annual Maintenance Contracts (AMC). Users can define contract properties, assign ownership, configure expiry notifications, specify terms and conditions, and associate assets with maintenance and warranty details.
Add Support and Maintenance Contract | Basic Details
Label
Action
Description
Once all details are entered, click ‘Next’ to proceed to the next section.
Add Support and Maintenance Contract | Item Details
Once all the details have been added, click “Submit” to add the software contract to the inventory.
The Service Contract type allows users to create and manage agreements for services provided by a vendor. Users can specify contract details, assign ownership and approval responsibilities, define contract validity and expiry notifications, and record the services offered, service-level agreements (SLAs), support details, and associated costs.
Service Contract | Basic Details
Click the Next button to go to the Item Details section.
Add Service Contract | Item Details
Click the Submit button to save the created contract.
The System Integration and Project Contract type allows users to create and manage contracts related to system integration projects and associated services. Users can define contract details, assign administrative and business responsibilities, configure visibility and approval settings, specify contract validity, and maintain terms and conditions.
Add System Integration and Project Contract | Basic Details
Click Submit to save the System Integration and Project Contract.
The Lease Contract type allows users to create and manage contracts for leased assets. Users can define contract details, assign administrative responsibilities, configure contract visibility, specify the contract period, and associate assets with lease start and end dates and applicable costs.
Add Lease Contract | Basic Details
Click Next to move to the Item Details section.
Add Lease Contract | Item Details
Click the Submit button to save the created contract.
The Other Contract type allows users to create and manage contracts that do not fall under the Procurement, Support and Maintenance, Service, System Integration and Project, or Lease categories.
Users can select a contract template, such as Insurance or NDA, and enter the relevant details based on the selected template. The available fields vary by contract type, including insurance-specific details or NDA terms.
Users can also assign contract ownership and approval responsibilities, configure visibility, specify the contract validity period, and maintain terms and conditions.
Add Other Contracts | Basic Details
Click the Next button to move to the Item Details page.
Add Other Contracts | Item Details
Click the Submit button to save the created contract.
Contract Name *
Enter text
Enter the name of the contract.
Add Items
Click
Click Add Items to add the required items to the contract.
License Type
Contract Name *
Enter text
Enter the name of the support and maintenance contract.
Parent Contract
Label
Action
Description
Add Item
Click
Click Add Items to add an item to the contract.
Name
Label
Action
Description
Contract Name *
Enter text
Enter the name of the service contract.
Label
Action
Description
Add Items
Click
Click Add Items to add a service to the contract.
Name
Label
Action
Description
Contract Name *
Enter text
Enter the name of the system integration or project contract.
Vendor *
Label
Action
Description
Contract Name *
Enter text
Enter the name of the lease contract.
Label
Action
Description
Add Items
Click
Click Add Items to add an item to the lease contract.
Name
Label
Action
Description
Contract Name *
Enter text
Enter the name of the contract.
Label
Action
Description
Add Items
Click
Click Add Items to add an insurance item to the contract.
Insurance Name
Add Software Contract
Note: Fields marked with Asterisk (*) are mandatory.
Add Service Contract
Add System Integration and Project Contract
Note: Fields marked with an asterisk (*) are mandatory. The default status and currency shown above are based on the supplied form details.
Add Lease Contract
Note: Fields marked with an asterisk (*) are mandatory. The labels Dropdown 90 and Number 9876 appear to be configured custom fields; replace them with their actual display names if available.
Add Other Contract
Note: The Item Details section is not available for NDA contracts.
Fields marked with an asterisk (*) are mandatory. The supplied details do not identify any additional item-specific fields for the Other Contract type. The repeated fields under Item Details appear to represent the contract form rather than a separate item grid.
Contract Template *
Select
Select the appropriate contract template.
Parent Contract
Select
Select an existing parent contract, if applicable.
Vendor *
Select
Select the vendor associated with the contract.
Manufacturer *
Select
Select the manufacturer associated with the contract.
Status
Display
Displays the contract status. The default status is Draft.
Currency
Display/Select
Specify the currency used for the contract. The default currency is INR.
Contract Admin
Select
Assign the user responsible for administering the contract.
Business Owners
Select
Select the business owners responsible for the contract.
Version
Enter text
Specify the contract version.
Approver Team
Select
Select the team responsible for approving the contract.
Visibility Type
Select
Select the visibility category for the contract. For example, Department.
Visibility to *
Select
Specify the users, departments, or other permitted entities that can access the contract, based on the selected visibility type.
Location
Select
Select the location associated with the contract. For example, Bangalore.
Dropdown 10 *
Select
Select a value from the configured dropdown options.
Description
Enter text
Enter a brief description of the contract.
Start Date
Select
Specify the date on which the contract becomes effective.
End Date *
Select
Specify the date on which the contract expires or ends.
Auto Renew
Enable/Disable
Enable this option if the contract should be automatically renewed, subject to the configured renewal process.
Notify Expiry
Enable/Disable
Enable this option to configure notifications before the contract expires.
Notify Before (in day(s)) *
Enter number
Specify how many days before the contract end date the expiry notification should be sent.
Notify To *
Select/Enter
Specify the recipient who should receive the contract expiry notification.
Terms and Conditions
Select
Select the applicable terms and conditions for the contract. For example, Purchase Orders (Dell Vendor) T&C.
Additional Terms and Conditions
Enter text
Enter any additional contractual terms or conditions that apply to the agreement.
Phone Number 01 *
Enter number
Enter the phone number required by the configured custom field.
Dropdown 90 *
Select
Select a value from the configured dropdown options. For example, dropdown 98.
Number 9876 *
Enter number
Enter the numeric value required by the configured custom field.
Terms and Conditions
S.No
Display
Displays the serial number of each terms and conditions entry.
Title
Display
Displays the title of the selected terms and conditions document. For example, Purchase Orders (Dell Vendor) T&C.
Action
Click
View the selected terms and conditions or delete them from the contract, as required.
Select
Specify the license type, such as Perpetual or Subscription.
Software Name
Select
Select the software associated with the item. Example: Adobe Acrobat (64-bit)-25.001.20937.
Quantity Type
Select
Specify the quantity measurement type. For example, User.
PO Number
Enter/Select
Specify the purchase order number associated with the item.
Count
Enter number
Enter the quantity of the item or licenses being procured.
Price Unit
Enter amount
Specify the price per unit.
Total
Display
Displays the total amount for the item based on its quantity and unit price.
Final Total
Display
Displays the final item amount after applicable calculations or adjustments.
Dropdown
Select
Select a value from the configured dropdown options.
Action
Click
You can delete the Line item.
Subtotal
Display
Displays the subtotal of the added items before applicable discounts, taxes, and shipping charges.
Additional Discount (%)
Enter number
Enter the additional discount percentage applicable to the contract.
Total CGST (%)
Enter number/Display
Specify or view the total Central Goods and Services Tax (CGST) percentage, as supported by the form.
Total SGST (%)
Enter number/Display
Specify or view the total State Goods and Services Tax (SGST) percentage, as supported by the form.
Total IGST (%)
Enter number/Display
Specify or view the total Integrated Goods and Services Tax (IGST) percentage, as supported by the form.
Shipping
Enter amount
Enter the shipping charges associated with the procurement items.
Total
Display
Displays the overall contract item amount after applicable discounts, taxes, and shipping charges.
Select
Select an existing parent contract, if applicable.
Vendor *
Select
Select the vendor providing support and maintenance services.
Manufacturer
Select
Select the manufacturer associated with the contract, if applicable.
Status
Display
Displays the contract status. The default status is Draft.
Currency
Display/Select
Specify the currency used for the contract. The default currency is INR.
Contract Admin *
Select
Assign the user responsible for administering the contract.
Business Owners
Select
Select the business owners responsible for the contract.
Version
Enter text
Specify the contract version.
Approver Team
Select
Select the team responsible for reviewing and approving the contract. The default approval team is displayed as Default Approval Team.
Visibility Type
Select
Select the visibility category for the contract.
Visibility to
Select
Specify the users, departments, or other permitted entities that can access the contract, based on the selected visibility type.
Description
Enter text
Enter a description of the support and maintenance contract.
Start Date
Select
Specify the date on which the contract becomes effective.
End Date *
Select
Specify the date on which the contract expires or ends.
Auto Renew
Enable/Disable
Enable this option if the contract should be automatically renewed, subject to the configured renewal process.
Notify Expiry
Enable/Disable
Enable this option to configure notifications before the contract expires.
Notify Before (in day(s)) *
Enter number
Specify how many days before the contract end date the expiry notification should be sent.
Notify To *
Enter/Select
Specify the recipient who should receive the contract expiry notification. For example, .
Terms and Conditions
Select
Select the applicable terms and conditions for the contract.
Additional Terms and Conditions
Enter text
Enter any additional terms or conditions that apply to the contract.
Text Area *
Enter text
Enter the information required by the configured multiline text field.
Phone Number 100 *
Enter number
Enter the phone number required by the configured custom field.
Text 789 *
Enter text
Enter the text value required by the configured custom field.
Dropdown 90 *
Select
Select a value from the configured dropdown options.
Number 9876 *
Enter number
Enter the numeric value required by the configured custom field.
Enter/Select
Specify the name of the item covered by the support and maintenance contract.
Related Assets
Select
Select the assets associated with the contract.
Warranty Expiry
Select
Specify the expiry date of the item's existing warranty.
Extended Warranty
Select/Enter
Specify the extended warranty details, based on the available field configuration.
AMC Expiry
Select
Specify the expiry date of the Annual Maintenance Contract (AMC).
Additional Amount
Enter amount
Enter any additional charges applicable to the item.
Price Unit
Enter amount
Specify the price per unit for the item.
Total
Display
Displays the total amount calculated for the item based on the applicable quantity and pricing details.
Final Total
Display
Displays the final amount for the item after applicable calculations or adjustments.
Dropdown
Select
Select a value from the configured dropdown options.
Radio
Select
Select one of the available options. For example, Option 1, Option 2, or Option 3, depending on the configured choices.
Action
Click
Click the delete option to delete the line item.
Parent Contract
Select
Select an existing parent contract, if applicable.
Vendor *
Select
Select the vendor providing the services.
Manufacturer
Select
Select the manufacturer associated with the contract, if applicable.
Status
Display
Displays the contract status. The default status is Draft.
Creation
Display
Displays the contract creation information, if provided by the application.
Currency
Display/Select
Specify the currency used for the contract. The default currency is INR.
Contract Admin *
Select
Assign the user responsible for administering the contract.
Business Owners
Select
Select the business owners responsible for the contract.
Version
Enter text
Enter the contract version.
Approver Team
Select
Select the team responsible for approving the contract. The default approval team is displayed as Default Approval Team.
Visibility Type
Select
Select the visibility category for the contract.
Visibility to
Select
Specify the users, departments, or other permitted entities that can access the contract, based on the selected visibility type.
Description
Enter text
Enter a description of the service contract.
Start Date
Select
Specify the date on which the contract becomes effective.
End Date *
Select
Specify the date on which the contract expires or ends.
Auto Renew
Enable/Disable
Enable this option if the contract should be automatically renewed, subject to the configured renewal process.
Notify Expiry
Enable/Disable
Enable this option to configure notifications before the contract expires.
Notify Before (in day(s)) *
Enter number
Specify how many days before the contract end date the expiry notification should be sent.
Notify To *
Enter/Select
Specify the recipient who should receive the contract expiry notification. For example, .
Terms and Conditions
Select
Select the applicable terms and conditions for the service contract.
Additional Terms and Conditions
Enter text
Enter any additional terms and conditions that apply to the contract.
Date
Select
Specify the date required by the configured custom field.
Dropdown 90 *
Select
Select a value from the configured dropdown options.
Number 9876 *
Enter number
Enter the numeric value required by the configured custom field.
Select
Select the name of the service associated with the contract.
Key Services Offered
Select
Select or specify the key services included in the contract.
SLA & Support
Select
Select or specify the applicable service-level agreement (SLA) and support arrangements.
Price
Enter amount
Enter the price associated with the service item.
Final Total
Display
Displays the final amount for the service item after applicable calculations or adjustments.
Dropdown
Select
Select a value from the configured dropdown options.
Action
Click
Click the delete option to delete the line item.
Subtotal
Display
Displays the subtotal of the added service items before applicable discounts, taxes, and shipping charges.
Additional Discount (%)
Enter number
Enter the additional discount percentage applicable to the service contract.
Total CGST (%)
Enter number/Display
Specify or view the total Central Goods and Services Tax (CGST) percentage, as supported by the form.
Total SGST (%)
Enter number/Display
Specify or view the total State Goods and Services Tax (SGST) percentage, as supported by the form.
Total IGST (%)
Enter number/Display
Specify or view the total Integrated Goods and Services Tax (IGST) percentage, as supported by the form.
Shipping
Enter amount
Enter the shipping charges, if applicable.
Total
Display
Displays the overall service contract amount after applicable discounts, taxes, and shipping charges.
Select
Select the vendor associated with the contract.
Manufacturer
Select
Select the manufacturer associated with the contract, if applicable.
Status
Display
Displays the contract status. The default status is Draft.
Currency
Display/Select
Specify the currency used for the contract. The default currency is INR.
Contract Admin *
Select
Assign the user responsible for administering the contract.
Business Owners
Select
Select the business owners responsible for the contract.
Version
Enter text
Specify the contract version.
Approver Team
Select
Select the team responsible for reviewing and approving the contract. The default approval team is displayed as Default Approval Team.
Visibility Type
Select
Select the visibility category for the contract.
Visibility to
Select
Specify the users, departments, or other permitted entities that can access the contract, based on the selected visibility type.
Description
Enter text
Enter a brief description of the contract.
Contract Description *
Enter text
Enter the detailed description of the system integration or project contract. The field displays the placeholder Insert Text Here.
Start Date
Select
Specify the date on which the contract becomes effective.
End Date *
Select
Specify the date on which the contract expires or ends.
Auto Renew
Enable/Disable
Enable this option if the contract should be automatically renewed, subject to the configured renewal process.
Notify Expiry
Enable/Disable
Enable this option to configure notifications before the contract expires.
Notify Before (in day(s)) *
Enter number
Specify how many days before the contract end date the expiry notification should be sent.
Notify To *
Enter/Select
Specify the recipient who should receive the contract expiry notification. For example, .
Terms and Conditions
Select
Select the applicable terms and conditions for the contract.
Additional Terms and Conditions
Enter text
Enter any additional contractual terms and conditions that apply to the agreement.
Parent Contract
Select
Select an existing parent contract, if applicable.
Vendor *
Select
Select the vendor or leasing provider associated with the contract.
Manufacturer
Select
Select the manufacturer associated with the leased asset, if applicable.
Status
Display
Displays the contract status. The default status is Draft.
Currency
Display/Select
Specify the currency used for the contract. The default currency is INR.
Contract Admin *
Select
Assign the user responsible for administering the contract.
Business Owners
Select
Select the business owners responsible for the contract.
Version
Enter text
Specify the contract version.
Approver Team
Select
Select the team responsible for reviewing and approving the contract. The default approval team is displayed as Default Approval Team.
Visibility Type
Select
Select the visibility category for the contract.
Visibility to
Select
Specify the users, departments, or other permitted entities that can access the contract, based on the selected visibility type.
DateTime * (Asia/Kolkata)
Select
Enter the date and time required by the configured field. The displayed time zone is Asia/Kolkata.
Description
Enter text
Enter a description of the lease contract.
Start Date
Select
Specify the date on which the contract becomes effective.
End Date *
Select
Specify the date on which the contract expires or ends.
Auto Renew
Enable/Disable
Enable this option if the contract should be automatically renewed, subject to the configured renewal process.
Notify Expiry
Enable/Disable
Enable this option to configure notifications before the contract expires.
Notify Before (in day(s)) *
Enter number
Specify how many days before the contract end date the expiry notification should be sent.
Notify To *
Enter/Select
Specify the recipient who should receive the contract expiry notification.
Example: .
Terms and Conditions
Select
Select the applicable terms and conditions for the lease contract.
Additional Terms and Conditions
Enter text
Enter any additional contractual terms and conditions.
Dropdown 90 *
Select
Select a value from the configured dropdown options.
Number 9876 *
Enter number
Enter the numeric value required by the configured custom field.
Enter/Select
Specify the name of the leased item.
Related Assets
Select
Select the assets associated with the lease contract.
Lease Start Date
Select
Specify the date on which the lease for the item begins.
Lease End Date
Select
Specify the date on which the lease for the item ends.
Additional Amount
Enter amount
Enter any additional charges applicable to the leased item.
Price Unit
Enter amount
Specify the price per unit for the leased item.
Total
Display
Displays the total amount calculated for the item based on the applicable quantity and pricing details.
Final Total
Display
Displays the final item amount after applicable calculations or adjustments.
Dropdown
Select
Select a value from the configured dropdown options.
Action
Click
The delete option is provided; you can delete the item list if needed.
Subtotal
Display
Displays the subtotal of the added items before applicable discounts, taxes, and shipping charges. The initial value is 0.
Additional Discount (%)
Enter number
Enter the additional discount percentage applicable to the lease contract. The initial value is 0.
Total CGST (%)
Enter number/Display
Specify or view the total Central Goods and Services Tax (CGST) percentage. The initial value is 0.
Total SGST (%)
Enter number/Display
Specify or view the total State Goods and Services Tax (SGST) percentage. The initial value is 0.
Total IGST (%)
Enter number/Display
Specify or view the total Integrated Goods and Services Tax (IGST) percentage. The initial value is 0.
Shipping
Enter amount
Enter the shipping charges, if applicable. The initial value is 0.
Total
Display
Displays the overall lease contract amount after applicable discounts, taxes, and shipping charges.
Contract Template *
Select
Select Insurance or NDA. The fields displayed depend on the selected template.
Insurance
Insurance Type *
Select
Select the insurance type. This field is displayed only when the Insurance template is selected.
Parent Contract
Select
Select an existing parent contract, if applicable.
Vendor *
Select
Select the vendor associated with the contract.
Manufacturer
Select
Select the manufacturer associated with the contract, if applicable.
Status
Display
Displays the contract status. The default status is Draft.
Currency
Display/Select
Displays or specifies the currency used for the contract. The default currency is INR.
Contract Admin
Select
Assign the user responsible for administering the contract.
Business Owners
Select
Select the business owners responsible for the contract.
Version
Enter text
Specify the contract version.
Approver Team
Select
Select the team responsible for reviewing and approving the contract. The default team is Default Approval Team.
Visibility Type
Select
Select the visibility category for the contract.
Visibility to
Select
Specify the permitted entities that can access the contract. For Insurance, this includes a Location field.
Description
Enter text
Enter a description of the contract.
NDA
Terms of NDA *
Enter text
Enter the NDA terms in the text field provided. This mandatory field is displayed only when the NDA template is selected.
Start Date
Select
Specify the date on which the contract becomes effective.
End Date
Select
Specify the date on which the contract expires or ends.
Auto Renew
Enable/Disable
Enable this option if the contract should be automatically renewed, subject to the configured renewal process.
Notify Expiry
Enable/Disable
Enable this option to configure notifications before the contract expires.
Notify Before (in day(s))
Enter number
Specify how many days before the contract end date the expiry notification should be sent, when applicable.
Notify To
Enter/Select
Specify the recipient who should receive the contract expiry notification, when applicable.
Terms and Conditions
Select
Select the applicable terms and conditions for the contract.
Additional Terms and Conditions
Enter text
Enter any additional terms and conditions that apply to the agreement.
Enter/Select
Enter or select the name of the insurance policy.
Related Users
Select
Select the users associated with the insurance policy.
Policy Number
Enter text
Enter the unique policy number associated with the insurance contract.
Coverage Details
Enter text
Enter details about the coverage provided by the insurance policy.
Coverage Amount
Enter amount
Specify the amount covered under the insurance policy.
Premium Amount
Enter amount
Enter the premium payable for the insurance policy.
Premium Frequency
Select
Select the frequency at which the insurance premium must be paid.
Action
Click
The delete option is provided; you can delete the item list if needed.
Click Add Report in the top-right corner of the Report page to create a new report. The Add Report page contains three tabs:
Category
Configuration
Filter
Each tab serves a specific purpose in setting up the report.
Category
Allows users to select the report category and the specific report they want to create. The selected report determines the type of data and reporting options available for configuration.
Label
Action
Description/Example
Label
Action
Description/Example
Label
Action
Description/Example
Label
Action
Description/Example
Label
Action
Description/Example
Label
Action
Description / Example
Label
Action
Description / Example
After selecting the specific Report, click Next to add Configuration.
Allows users to enter the report name and configure the report settings, such as selecting the required columns and other options available for the selected report. Users can preview the report and save the configuration.
Configuration boxes vary based on the selected Report. You will see three to four sections in the configuration tab. Refer to the table for more information.
Report Configuration | Specific Configuration
Label
Description
After selecting the appropriate boxes on the Configuration tab, click Next to add details on the Filter tab.
Allows users to define conditions to narrow down the report data. Users can apply available filters, such as asset tags, resource tags, and custom filters, depending on the selected report.
Filter options vary based on the selected Report. You will see three sections in the Filter tab.
You can apply a filter to see only the details you selected.
Add Report | Filter
Label
Description
After applying filters, click View Report to see your report on the Report dashboard.
The View Report option allows you to generate and preview the report based on the selected report configuration, filters, and other parameters.
The report preview displays the data based on the configuration and filters selected by the user. The displayed columns and data depend on the report type and the options selected during configuration.
For example, asset-related reports can display the columns selected during report configuration, while filters such as Duration, Asset Tag, and custom filters determine the data included in the report.
The Report Setup Options section explains the available fields and settings used to configure a report in Infraon. Users can select the required columns, define applicable devices using tags, configure custom filters, and link related reports.
Depending on the selected report type, additional configuration options may be available. These settings determine the data included in the report and how it is grouped, filtered, calculated, or displayed. The available options vary depending on the selected report type.
After selecting View Report, you can provide a title and description for the generated report.
Report Configuration | Title and Description
Field
Description
Report Configuration | Left Panel
Label
Action
Description/Example
Report Configuration | Specific Configuration
Label
Action
Description/Example
Click Data Privacy to open the Mask/Unmask Requester Information panel.
The Data Privacy panel provides controls for masking or unmasking requester information in the report.
Report Configuration | Data Privacy
Label
Action
Description/Example
Admins can enable hiding the requester’s info in reports to comply with data privacy regulations.
The report configuration screen provides Public and Private options to control the report's visibility.
Label
Action
Description/Example
Example:
Select the required users and/or teams to provide access to the private report.
Only the users and teams selected in the Assignee section are assigned to the private report.
Allows users to configure and manage report generation schedules by selecting the report format, scheduling frequency, execution date and time, and email delivery details. Users can enable or disable schedules, update existing configurations, and submit the report configuration.
Report Configuration | Schedule
Label
Action
Description/Example
For example: Scheduled on 6 October 2026, 12:00 (Asia/Kolkata)
The configured schedule can also be reflected in Schedule History, where details such as the report name, schedule type, execution times, status, file type, and generated file can be viewed.
The Preview Report displayed in the generated report depends on the selected report type and the configuration applied while creating the report.
The report displays the data relevant to the selected report and its configured columns, filters, timescale, and other report-specific settings.
Example
The data displayed varies according to the selected report.
An Agent Uptime Report displays agent and asset-related information based on the selected columns.
An SLA Report displays SLA-related information based on the selected SLA Profile, Metric, Timescale, and other applicable settings.
An Asset Delivery Penalty Report displays delivery and penalty-related information based on its configured fields.
Therefore, the report data varies depending on the selected report type and its configuration. The available columns and generated data are determined by the selected report.
Reports can be exported in the formats supported by the selected report, such as PDF, CSV, or XLSX. The exported report contains the data generated according to the configured report settings.
For reports with linked reports, the exported output can contain the linked report data as separate sections or tables. HTML export is also supported for applicable reports.
Inventory Agent Installation Report
Displays inventory agent installation and uptime details for managed assets. The report includes fields such as Agent Name, Asset Name, Serial Number, IP Address, Location, Installation Date, Last Contact Time, Agent Version, and Agent Uptime in Minutes. By default, the report displays all assets without applying any grouping. Users can optionally group the report by criteria such as Location to organize the results before previewing or saving the report. The report dynamically reflects updated asset and agent-related information after asset modifications. The report supports Send Now, Schedule Report, Clone, Edit, and Delete actions. Users can export the generated report in PDF, XLSX, and CSV formats.
Displays inventory agent installation and uptime details for managed assets. The report includes fields such as Agent Name, Asset Name, Serial Number, IP Address, Location, Installation Date, Last Contact Time, Agent Version, and Agent Uptime in Minutes. By default, the report displays all assets without applying any grouping. Users can optionally group the report by criteria such as Location to organize the results before previewing or saving the report. The report dynamically reflects updated asset and agent-related information after asset modifications. The report supports Send Now, Schedule Report, Clone, Edit, and Delete actions. Users can export the generated report in PDF, XLSX, and CSV formats.
Agent Uptime Report
View / Configure
Asset Audit Summary Report
Users can filter this report using options like Change Type, Custom Filters, and Location conditions.
Provides visibility into API consumption across API Users. By default, the report displays Date/Month, API User, Total Calls, Endpoint, Method, and Distinct IPs. Optional columns, such as Full Name and Email, can be included by selecting them. Data can be filtered using fields such as API User, Endpoint, Method, and Email to analyze API usage patterns. The report groups API activity by user, endpoint, and HTTP method, helping administrators monitor API consumption, identify frequently used endpoints, track unique source IP addresses, and review license utilization trends. Supports report preview, scheduling, and export in Excel, CSV, and PDF formats.
Asset Depreciation Report
Audit Reports
Users can select Audit Report, enter the report name, configure the required fields and custom filters, and preview the report. They can save, edit, clone, or delete the report. Users can generate the report after modifying the conditions and export it in Excel, CSV, or PDF formats. The report can be scheduled for email or folder delivery, including immediate delivery. Users can also select a timescale to filter the report data for a specific period.
Displays audit information based on the selected category, fields, custom conditions, values, and timescale. The report includes audit details such as Sl. No., Module, Event, and Description. Users can apply custom filters to refine the displayed audit data and select a timescale to generate the required results. The report can be previewed, generated, edited, cloned, or deleted based on the user's requirements. Users can export the report in Excel, CSV, and PDF formats and send it through email or folder dump either immediately or on a scheduled basis. For MSP users, the displayed data is based on the user's configured visibility.
Contracts Report
Users can select Contract List Report, configure the required columns and custom filters, and preview the report. They can select the required columns and apply custom filters before generating the report. Users can save, edit, clone, or delete the report. Users can schedule the report for delivery and send it by email by selecting the report type and recipient email addresses. Users can also select Group By options in the preview, with Contract selected by default.
Displays detailed contract information based on the selected columns and custom filters. The report includes fields such as Sl. No., Manufacturer, Contract Type, Vendor, Contract ID, Contract Name, Approver, and Billing Cycle. Users can configure the columns and filters to customize the report and optionally group the results by Contract to organize the displayed data. The report data is based on the user's visibility over contracts. Users can preview, save, edit, clone, delete, schedule, and email the report based on their requirements.
Contracts Summary Report
Users can select Contract Summary Report, configure the required columns and custom filters, and preview the report. They can modify the selected columns and filters before generating the report. Users can save, edit, clone, or delete the report. The report can be scheduled for delivery or sent by email to selected recipients. Users can also select Group By options in the preview, with Contract selected by default.
IMACD Summary Report
Click on the reports on the left panel and select the IMACD. Click on the IMACD report.
Provides a consolidated overview of the key metrics and statistics related to installation, movement, addition, changes, and destruction processes handled by the IT service management team. Helps monitor service delivery, identify areas for improvement, make data-driven decisions, and enhance customer satisfaction.
IMACD Report
Click Reports on the left panel and select IMACD. Click on the IMACD Report.
Purchase Order Summary Report
Users can configure this report by selecting required columns, applying filters, choosing Group By options (Vendor, Department), selecting Timescale Columns (Creation Time, Expected Delivery Date), and defining a Timescale. Users can also include vendor-related columns, such as Vendor Location and other mapped vendor details from the Vendor module.
Displays summarized Purchase Order details based on the selected configuration. The report includes default fields such as PO ID, PO Name, Vendor, Department, Status, Expected Delivery Date, Ordered Quantity, Received Quantity, Remaining Quantity, and Total Cost. Additional vendor-related columns can be selected to display mapped vendor information associated with the Purchase Order. Users can preview the report before saving and export it in Excel, CSV, and PDF formats.
Asset Delivery Penalty Report
Click Reports on the left panel and select Asset Delivery Penalty Report.
Blacklisted Software Details
Users can select the Blacklisted Software Details Report, configure the required fields, and preview the report. They can filter the report using asset tags or custom filters, select the required columns, and generate the report based on the selected conditions. Users can save, edit, clone, or delete the report. The report can be scheduled for email or folder delivery, including immediate delivery, and exported in Excel, CSV, or PDF formats.
Displays details of blacklisted software installed on managed assets. Users can filter the report based on asset tags, categories, conditions, and values and select the columns required for the report. The report data is generated according to the selected filters and columns and is displayed based on the logged-in user's visibility.
License Allocation History
Users can select License Allocation History Report, configure the report, and preview the results. They can apply custom filters and timescale settings, select the required columns, and generate the report based on the selected conditions. Users can save, edit, clone, or delete the report. The report can be scheduled for email or folder delivery, sent immediately, and exported in Excel, CSV, or PDF formats.
Statistics
You can modify your report by adding statistical details like CPU utilization, Availability, etc.
Columns
You can choose assets from the column. This column is optional; you can proceed to the next tab without filling it.
Show Top
Duration
Select the particular duration that you want to see on the report. By default, it is set to the last hour.
Asset Tag
Select any asset tag for your report.
Assignee
Title
Enter a name for the report.
Description
Enter a description for the report, if required.
Columns
Select or deselect the required report fields.
Allows you to select the required columns for the report. The selected fields are displayed as columns in the generated report and are included when the report is exported. Note: The available columns depend on the selected report type.
Applicable Device
Select
Asset Scope
Select the scope of assets to be included in the report.
Determines which assets are considered when generating the report.
Active
Data Privacy
Click Data Privacy to open the privacy settings.
Opens the Mask/Unmask Requester Information panel, where you can configure how requester information is displayed in reports.
Name
Enable or disable the toggle under Mask or Unmask.
Public
Select Public to make the report available according to the public report visibility settings.
A public report can be accessed by users who have the required report visibility permissions.
Private
Select Private to restrict the report's visibility.
Schedule
Click Schedule to open the scheduling panel.
Opens the Schedule settings for the report.
Report Type
Select the format in which the scheduled report should be generated.
Agent
Asset
Audit
Contracts
IMACD
Purchase Order
Software
Only users with Administrator privileges can view and access System Reports.
Release and Change reports include related record information during report extraction. While configuring the report, selecting the Relation column displays IDs of all linked records, such as Tickets, Changes, Problems, Releases, and Requests.
The Relation column lists related record IDs for each Release or Change.
If no relation is found, the column remains empty.
The Location Name / Installed Location filter supports the IN and IS conditions. Selecting IS allows you to choose an empty value to retrieve assets that lack a location assignment.
A custom field filter for Asset Custom Field (Zone, Circle, Time, etc.) is now available in all summary reports. These fields are part of the custom attributes added in IT Assets and help refine report data directly within the tool for quicker analysis. The export option remains available for full report downloads.
The Service Catalogue field is available as a custom filter in ITSM reports. Users can select one or more service catalogue entries while creating or editing a report.
When applied, the report data is filtered to display only records associated with the selected service catalog entries. The filter is supported in both report configuration and preview mode.
Configuration
Filter
Report Configuration
Report Setup Options
The configuration fields displayed in this section vary depending on the selected report type. These fields are available only for reports that require additional configuration.
Data Privacy
The Mask and Unmask options determine whether requester information is hidden or displayed. Ensure that unmasking is enabled only for users with the appropriate authorization.
Public and Private
Public and Private control the visibility of the report. They are separate from Data Privacy, which controls the masking or unmasking of requester information.
Schedule
Preview Report
Exporting the Report
Displays agents' uptime for assets over a selected time range, allowing users to analyze availability and operational duration. By default, the report shows overall uptime from the agent installation date to the current date. Users can apply predefined filters (e.g., Last 7 Days, Last 30 Days) or select a custom date range to view uptime for specific periods, such as weekly or monthly analysis. Supports filtering using asset tags and custom conditions, column selection, sorting, and preview before saving. Reports can be exported in CSV, XLSX, and PDF formats and scheduled for automated delivery via email or to a folder.
Click the Helpdesk Reports on the left panel and select the Depreciation Report
Generate the Depreciation Report for Assets and select the relevant report from the provided list. Submit the report request and select the financial year start date to generate the report based on your needs. The generated report provides accurate and up-to-date information about asset depreciation.
Asset Summary Report
The report also supports Nested Grouping, allowing users to group report data using multiple Group By levels. Users can select up to four grouping fields, and the exported report maintains the same grouping structure as displayed in the report view.
Provides a consolidated view of assets with configurable grouping and filtering options. Users can group assets using fields such as OS Name, Device Type, Status, Vendor, and other available asset attributes for reporting and audit purposes. The report supports a Split By option that breaks down asset counts by a selected attribute. When enabled, the report preview displays asset distribution with accurate split counts. The selected Split By configuration is retained during save, edit, view, and export operations.
Asset Detailed Report
Click on the Helpdesk Reports on the left panel and select the Asset Reports. Click on the Detailed Asset Report
Comprehensive asset hardware, software, and activity log in one report, with a detailed asset report by selected tags and duration, and generates information that contains the asset name, IP address, inventory details, and more.
Asset Allocation Report
Users can configure the report by selecting the required columns, asset tags, custom filters, and timescale before previewing or generating the report. Users can filter asset data based on Allocation Time, Deallocation Time, or Acceptance Time and apply conditions such as Serial Number or Location Name / Installed Location. The report can be exported in Excel, CSV, and PDF formats, scheduled for email or folder delivery, or sent immediately. Users can also edit, clone, or delete the report configuration.
Displays asset allocation information based on the selected columns, custom filters, asset tags, and timescale. The report supports Allocation Time, Deallocation Time, Acceptance Time, Acceptance timestamp, AMC Extension date, Asset Source, Service Hub, and Requester columns. Users can filter asset data using criteria such as Serial Number and Location Name / Installed Location, including assets with blank locations. The report can be filtered based on Allocation Time, Deallocation Time, or Acceptance Time and displays date and time values according to the user's current timezone. The report data is based on the logged-in user's visibility. Users can export the report in Excel, CSV, and PDF formats, including a Single Workbook Excel option, and can send or dump the report immediately or according to a configured schedule.
Asset Audit Report
Users can configure the report by selecting the required asset tags, custom filters, timescale, Sort By, and Sort Order before previewing or generating the report. Users can filter asset audit data using criteria such as Serial Number, Location Name / Installed Location, Asset Source, and Service Hub. The report can be exported in Excel, CSV, and PDF formats, including the Single Workbook Excel option. Users can schedule the report for email or folder delivery, or send or dump it immediately. The report can also be edited, cloned, or deleted based on their requirements.
Displays asset audit information based on the configured fields, filters, timescale, and sorting options. The report is used to review and analyze asset-related audit data according to the user's visibility and selected criteria. Users can configure custom filters, such as Serial Number, Location Name / Installed Location, and Asset Source, to refine the displayed data. The report supports previewing and generating results, exporting data in Excel, CSV, and PDF formats, scheduling email or folder delivery, and performing immediate email or folder dump actions. The Single Workbook Excel option allows the report data to be downloaded as a single Excel workbook.
Asset Replacement Report
Users can configure the report by selecting the required asset tags, custom filters, timescale, Sort By, and Sort Order before previewing or generating the report. Users can filter replacement data using custom criteria, including Device Type, where the selected device type is matched against the current or previous asset device type. The report can be exported in Excel, CSV, and PDF formats from both the report view and grid. Users can schedule the report for email or folder delivery, or send or dump it immediately. The report can also be edited, cloned, or deleted based on their requirements.
Displays asset replacement information based on the configured report fields, filters, timescale, and sorting options. The report lets users review asset replacement data and identify replacement-related information for current and previous assets. Users can apply asset tag and custom filters to refine the report data. The Device Type custom filter supports available device type values and filters the report when the selected value matches either the current or previous asset device type. The report supports previewing and generating updated results, exporting data in Excel, CSV, and PDF formats, scheduling email or folder delivery, and performing immediate email or folder delivery. Report data is displayed according to the logged-in user's visibility, and the selected timescale is included in the report data.
Asset Report
Users can configure the report by selecting the required columns, custom filters, Timescale Column, and time range before previewing or generating the report. The report supports fields such as PO Number, Recent Asset Allocation Time, Recent Asset Deallocation Time, Recent User Acceptance Time, Last Update Time, Agent Sync Time, AMC Extension Date, Serial Number, Location Name / Installed Location, Asset Source, Model Year, Service Hub, and supported Requester Columns. Users can apply custom filters such as Serial Number, Location Name / Installed Location, Asset Source, and PO Number to refine the report data. The report also supports an Asset Scope filter with Active and Deleted options, while Archived is available when the Asset Archival feature is enabled. When Deleted or Archived scope is selected, the corresponding deletion or archival information is automatically included in the report. Users can enable Show Stack Module to display stack module information grouped by asset. The report can be exported in Excel, CSV, and PDF formats.
Displays asset information based on the selected columns, filters, timescale, and asset scope. The report is used to view and analyze asset details, including allocation and deallocation information, user acceptance time, PO number, agent synchronization details, AMC extension information, asset source, model year, Service Hub, requester details, and other configured asset data. The Timescale Column supports options such as Last Sync Time, Deleted Time, and Archived Time, allowing users to generate report data for a selected time range. When Asset Scope is set to Deleted, the report displays Deleted Time, Deleted By, and Delete Source; when set to Archived, it displays Archived Time, Archived By, Archive Reason, and Archive Notes. These scope-specific columns are automatically included based on the selected scope. The report supports previewing, generating, filtering, and exporting data, while selected time-based information is displayed according to the user's timezone.
Asset Request / Owner Report
Users can configure the report by selecting the required asset columns and applying Duration, Tags, Assignee, and Custom Filters before previewing or submitting the report. Users can edit the selected columns, filters, assignee, tags, and timescale, or clone an existing report and modify its configuration. Custom filters can be applied using criteria such as Serial Number, Location Name / Installed Location, and Asset Source. The report also supports Requester Columns, which can be selected, expanded, collapsed, or selected using Select All. Users can export the report using the Single Workbook Excel option, which downloads the asset data as a single Excel workbook. The report can also be edited, cloned, or deleted based on the user's requirements.
Displays asset information based on the selected requester/owner, columns, duration, tags, assignee, and custom filter criteria. The report is used to view asset details associated with requesters or owners and to refine the displayed data using the available report configuration options. Users can select supported Requester Columns to display requester information, including correctly formatted dates and translated values, with multiple or no requesters handled in the report output. The report also supports fields such as AMC Extension Date, Asset Source, and Service Hub. Custom filters can be used to refine results by Serial Number, Location Name / Installed Location, or Asset Source, including filtering assets with blank locations using the IS condition. The report supports previewing and viewing the configured data, editing or cloning the configuration, and downloading the report using the Single Workbook Excel option.
Asset Wise Software License Allocation Summary
Users can configure the report by selecting Group By, Nested Grouping, Split By, and Custom Filters before previewing or generating the report. The Group By field defaults to Publisher and provides fields grouped under Asset, Asset Custom Field, Software License, and License Custom Field categories. Users can enable Nested Grouping to organize the report across multiple grouping levels, with each level displaying distinct Asset Count and License Count values. The Split By option provides a category-wise breakdown, including an Other bucket for missing values. Users can apply custom filters using Asset fields, Asset Custom Fields, Software License fields, and Software License custom fields. The report can be edited, cloned, viewed, and generated with updated configurations, and the generated data can be exported in Excel, CSV, and PDF formats.
Displays a summary of software license allocations across assets, grouped by the selected criteria. The report is used to analyze software license allocation at the asset level and distinguishes between Asset Count and License Count. Only assets with at least one active software license allocation are included in the report. Users can group the data by Publisher or other supported Asset, Asset Custom Field, Software License, and License Custom Field fields. Nested Grouping provides multiple levels of grouping with per-level asset and license counts, while Split By provides a breakdown based on the selected category. Custom filters can be applied to refine the report using software fields such as Publisher, License Type, and Vendor, as well as configured Software License custom fields.
Consumable Asset
Users can configure the report by selecting the required columns, custom filters, and custom field columns before previewing and saving the report. The report supports editing the selected columns and filters, cloning existing report configurations, and deleting reports. Users can schedule the report for delivery and use the Email Report option to send the report to specified recipients. The report data is displayed according to the user's visibility permissions over consumable assets. Users can also download the generated report in the selected format.
Displays consumable asset information based on the selected columns, custom filters, and custom field columns. The report is used to view and manage consumable asset data according to the user's configured report criteria and visibility permissions. Users can select standard and custom field columns to control the information displayed in the report and apply custom filters to refine the results. The report supports saving, editing, cloning, deleting, scheduling, and emailing the generated report. It is available under the Asset Reports category for asset-based licenses/subscribers and supports report export in the available formats.
Asset Wise Software License Allocation Summary
Users can configure the report by selecting Group By, Nested Grouping, Split By, and Custom Filters before previewing or generating the report. The Group By field defaults to Publisher and provides fields grouped under Asset, Asset Custom Field, Software License, and License Custom Field categories.
Users can enable Nested Grouping to organize the report across multiple grouping levels, with each level displaying distinct Asset Count and License Count values. The Split By option provides a category-wise breakdown, including an Other bucket for missing values.
Users can apply custom filters using Asset fields, Asset Custom Fields, Software License fields, and Software License custom fields. You can edit, clone, view, and generate the report with updated configurations, and export the generated data in Excel, CSV, and PDF formats.
Displays a summary of software license allocations across assets, grouped by the selected criteria. The report is used to analyze software license allocation at the asset level and distinguishes between Asset Count and License Count.
Only assets with at least one active software license allocation are included in the report. Users can group the data by Publisher or other supported Asset, Asset Custom Field, Software License, and License Custom Field fields. Nested Grouping provides multiple levels of grouping with per-level asset and license counts, while Split By provides a breakdown based on the selected category.
Custom filters can be applied to refine the report using software fields such as Publisher, License Type, and Vendor, as well as configured Software License custom fields.
Displays a summary of contract information based on the selected columns and custom filters. Users can configure the required columns and filters to customize the report and optionally group the results by Contract to organize the summary. The report data is displayed based on the user's visibility over contracts. Users can preview, save, edit, clone, delete, schedule, and email the report as required.
Provides a consolidated view of IMACD records while applying the same data visibility rules as the IMACD module grid. Ensures that users can access only the records they are authorized to view based on factors such as created-by, assignee, team routing, approval/review profile membership, and asset ownership/tag linkage. Helps users review and analyze IMACD data while maintaining consistent access control.
Provides a report of asset delivery penalty-related records while applying the same data visibility restrictions as the source module. Ensures that users can view only the records they are authorized to access, preventing restricted records from being exposed through the report. Helps users review asset delivery penalty information while maintaining secure and consistent data access.
Displays the history of software license allocation over the selected period. Users can apply custom filters and select a timescale to view allocation data for a specific period. The report supports configurable columns and allows users to control the visibility of the report by making it private for selected users or teams or public for all users.
Software by Publishers
Click on the reports on the left panel and select software reports.
Enable all columns in Software by Publish Reports. Gain detailed insights into respective assets, including application name, vendor, help link, and more. Filter by asset tag and custom criteria for comprehensive software tracking.
Software Details Report
Click on the reports on the left panel and select software reports.
Access detailed reports for respective software in Software Detail Reports. Identify software status as 'Discovered' if found through the agent, or 'Managed' if manually added.
Software Installation
Users can select Software Installation Report, choose the required columns, and configure filters before previewing the report. They can group the report by Asset Name, Application Name, Application Type, or Application Vendor, with Software selected by default. Users can modify the grouping, generate the updated report, and save the configuration. The report can be sent immediately or scheduled, cloned, edited, or deleted, and exported in Excel, CSV, or PDF formats.
Displays details of software installed on managed assets. The report provides information such as Asset Name, Application Vendor, and Application Version. Users can group the results based on different asset or application attributes to organize and analyze the installed software information. The report reflects the selected grouping and filter conditions when generated or exported.
Software Installed vs Purchase Report
Users can select Software Installed vs Purchased Report from the Software Reports category and apply optional custom filters before viewing the report. They can save, edit, clone, or delete the report and generate the report to view the software installation and purchase counts. Users can also schedule the report or send it to selected email addresses.
Displays a comparison between software purchased and software installed. The report provides details such as Software Name, Software Version, Total Purchased, Managed Installations, Remaining, and Compliance Status. The report helps users compare purchased licenses with managed installations and identify the remaining licenses and compliance status. The report is available for software subscribers/license users.
Software License Summary
Users can configure this report by selecting required columns, applying custom filters, choosing a Timescale Column (Effective From, AMC Start Date, AMC Expiry Date, End Date, Invoice Date), and defining a Timescale.
Displays software license details based on the selected configuration. The report includes fields such as License Name and Description (available by default), as well as selectable columns such as Free (available licenses) and Allocated (assigned licenses). Users can filter data using custom conditions and time-based criteria. The report supports preview before saving and allows export in Excel, CSV, and PDF formats. It helps track license usage, availability, and lifecycle based on selected time filters.
Software Metering Report
Users can select Software Metering Report, choose the required columns, and configure the Applicable Devices using Asset Tags. They can link related reports using Link Reports and select a date range using Timescale. The report can then be generated based on the selected columns, devices, linked reports, and time period.
Displays software metering information based on the configured metering rules and applicable devices. Users can select the required report columns, filter the report based on Asset Tags, link related reports, and specify a date range to view the required metering information.
You can select the top 5 or 10 to see only the top 5 or 10 reports.
Search
You can search for the desired column using the search tab.
Select all
Enabling it will select all the columns provided in the configuration section.
Asset Scope
Allows you to select the asset scope to include Active, Deleted, or Archived assets in the report. The asset scope option is only available in Asset Report.
Data Masking
Allows sensitive asset information to be masked, including IP Address, Host Name, Serial Number, MAC Address, and License Key. The data masking option is only available in Asset Report.
Resolution
You can select the resolution duration in minutes, hours, days, or months. Note: The resolution option is only available in Availability Report.
Module Name
Allows you to select the module for which the report data should be generated.
Select the assignee name to whom you want to send the report. Note: This option is only available in Incident Report and Incident Summary Report.
Create a Custom Filter
Create a custom filter by selecting a category, condition, and value to refine the report data based on specific requirements.
Use Applicable Devices to define the devices or records included in the report. You can select tags based on the report module. Example: For an Incident Report, select Incident Tag to include only incidents associated with the selected tags. Similarly, use Request Tag, Problem Tag, Change Tag, or Release Tag for their respective report types. If no Asset Tags are selected for a report where this filter is optional, the report can still be generated and may display the complete or unfiltered results.
Asset Tags
Select the required asset tags.
Filters the report based on the selected asset tags.
Custom filters
Click to create or configure custom filter conditions.
Allows you to define advanced conditions to control which records are included in the report.
Link Reports
Select the required reports from the available reports.
Allows related reports to be associated with the current report.
Select Active as the Asset Scope.
The report includes assets that are currently active.
SLA Profile*
Select the required SLA profile.
Defines the SLA profile to be used for generating the report.
Metric
Select the required metric.
Specifies the SLA metric used for the report. Example: Gold.
Timescale
Select the required time period.
Defines the period for which the SLA data is generated. Example: Current Month.
Penalty Configuration
Select the required penalty configuration.
Specifies the penalty configuration applied to the SLA report. Example: Test Incident Penalty.
Resource Only
Enable or disable the option.
Restricts the report to resource-related SLA data when enabled.
Group By
Select the field by which the report data should be grouped.
Groups the generated report data based on the selected field. Example: Team.
Timescale
Select the required reporting period.
Defines the time period for which the report data is generated. Example: Current Month.
Forecast Data
Select the forecast period.
Defines the future period for which forecast data is included in the report. Example: Next 60 Days.
Limit
Select the required result limit.
Specifies the number or category of results to be included in the report. Example: Top.
Threshold
Configure the threshold value or condition.
Defines the threshold used when evaluating or presenting report data.
Percentile
Configure the percentile value.
Specifies the percentile used for the report calculation or threshold evaluation.
Unit Scale
Select the required unit scale.
Defines the unit scale used to represent the report values. Example: Default.
Chart Type
Select the required chart type.
Defines how the report data is visually represented.
Resolution
Select the required resolution.
Defines the level of detail or granularity used when displaying the chart data.
Split By
Select the field by which the chart data should be divided.
Splits the displayed data based on the selected field.
Timescale
Select the required time period.
Defines the period for which the chart data is generated. Example: Last 60 Mins.
Financial Year Start
Select the month in which the financial year begins.
April means the financial year is calculated from April.
Limit
Select the required result limit.
Specifies the number of results displayed in the report. Example: Top 5.
Poll Points
Enter the required number of poll points.
Defines the number of polling points considered when generating the report data.
Show Stack Module
Enable or disable the toggle.
Controls whether stack module information is displayed in the report.
Mask: Obfuscates the requester's name in reports to protect personal information and comply with data privacy requirements.
Unmask: Displays the requester's name without masking for authorized access.
Contact
Enable or disable the toggle under Mask or Unmask.
Mask: Obfuscates the requester's contact information in reports. Unmask: Displays the requester's contact information without masking for authorized access.
Email
Enable or disable the toggle under Mask or Unmask.
Mask: Obfuscates the requester's email address in reports.
Unmask: Displays the requester's email address without masking for authorized access.
Save
Click Save to apply the selected privacy settings.
Saves the masking and unmasking preferences configured for requester name, contact information, and email address.
A private report is restricted and not available as a public report.
Select Private to restrict the report to specific users or teams.
When Private is selected, the Assignee section opens.
Assignee
Select User/Teams for private.
The Assignee section allows you to select the users or teams who can access the private report.
Users
Select one or more users from the list.
Displays the available users who can be assigned access to the private report. Each user displays their name and email address. Selects the user to whom the private report is assigned.
Teams
Select one or more teams from the list.
Displays the available teams that can be assigned access to the private report. Selects the team to whom the private report is assigned.
Cancel
Click Cancel.
Closes the Assignee section without applying the selection.
Submit
Click Submit.
Applies the selected users or teams to the private report.
Available formats shown in the Schedule panel are PDF, XLSX, and CSV.
Active
Enable or disable the toggle.
Enables or disables the configured report schedule.
Schedule Mode
Select the required scheduling frequency.
Available options include Once, Every, Daily, Weekly, and Monthly.
Date and Time
Specify when the report should be generated.
Example: 6 October 2026, 12:00 PM.
Email – To
Enter the recipient email address.
Specifies where the scheduled report should be sent.
Email – Subject
Enter the email subject.
Defines the subject of the email containing the scheduled report.
Email Body
Enter the message to be included in the email.
Allows you to provide additional information along with the scheduled report.
Update Schedule
Click Update Schedule to save the schedule.
Saves the selected report format, schedule frequency, date/time, and email details.
Submit
Click Submit after completing the report configuration.
Saves the report configuration. After the report is created, it can be accessed from the Reports page and generated when required.
Working on a Quotation
After an RFQ is created, it progresses through the configured workflow based on the organization's approval and procurement process. Open the RFQ to view its details, monitor its progress, communicate with vendors, review quotations, and complete the procurement lifecycle.
The RFQ view page contains the following sections:
Details
The Details section displays the quotation request information entered during RFQ creation, including the title, location, requester, dates, payment and shipping details, contact information, and description. This section also displays the workflow stage, current status, attachments, and vendor activity timeline. Users with the required permissions can update the RFQ status and upload supporting documents.
Item and Cost Details
The Item and Cost Details section displays all line items associated with the RFQ in a tabular format. You can review item details such as item name, type, category, quantity, and pricing information. The section also displays the calculated Subtotal, Tax, and Grand Total for the quotation, providing a consolidated cost summary.
Approval
The Approval section displays the approval workflow configured for the RFQ. It enables users to review the approval stages, view approver information and approval history, and perform approval or rejection actions based on their assigned permissions.
The Vendor section displays all vendors associated with the RFQ, along with their contact information and the status of their quotation communications. It helps procurement users monitor which vendors have received the RFQ, track vendor communications, and review the progress of quotation submissions throughout the procurement process.
The Quotation Comparison section allows you to compare quotations received from multiple vendors, evaluate pricing, identify the lowest quotation (L1), and award the RFQ to one or more vendors.
The section contains the following tabs:
Commercial Comparison
Summary and Award
The Commercial Comparison tab displays vendor quotations side by side, enabling you to compare pricing and identify the most suitable vendor.
Label
Action
Description / Example
The Summary and Award tab is used to finalize the vendor selection after evaluating the received quotations.
Label
Action
Description / Example
Line Item Comparison
Compare
Compares unit price and total price for each item across all vendors.
Example: Compare the Unit Price of Item 01 from three vendors before awarding.
Total Quote Amount
View
Displays the total quotation value submitted by each vendor.
Displays additional quotation information such as the quotation due date.
Select Vendor
Select
Choose the vendor who will receive the award.
Example: Select Nayana as the awarded vendor.
Vendor Rank
View
Displays the vendor ranking based on the quotation comparison.
Example: L1 indicates the lowest quotation.
Amount
View
Displays the submitted quotation amount for the selected vendor.
Reason if Non L1
Enter
Provide a justification when awarding the RFQ to a vendor other than the lowest bidder.
Example: Preferred vendor for faster delivery and an extended warranty.
Remarks
Enter
Add additional comments related to the vendor selection.
Example: Vendor approved after technical evaluation.
Submit Award
Click
Submits the vendor selection and completes the RFQ award process.
Vendor Quotation Cards
View
Displays each vendor's quotation amount, quotation version, submission date, and quotation validity.
Example: Vendor Nayana quoted ₹1,20,020 and is identified as L1.
L1 Indicator
View
Award Entire RFQ
Select
Awards all RFQ line items to a single vendor.
Example: Award the complete laptop procurement to Dell Technologies.
Split Award by Items
Select
Vendor
Quotation Comparison
Commercial Comparison
Summary and Award
The system automatically identifies the Lowest Quotation (L1) during commercial comparison.
You can award the RFQ to a single vendor or multiple vendors based on business requirements.
When a vendor other than L1 is selected, a justification must be provided before submitting the award.
After the award is submitted, the RFQ proceeds to the configured approval workflow and can be used to generate the corresponding Purchase Order.
Highlights the vendor offering the lowest quotation.
Example: The green L1 badge indicates the lowest commercial quote.
Awards individual line items to different vendors.
Example: Award laptops to Dell and accessories to HCL.
Create Knowledge Base
Import From CSV
The Bulk Upload feature lets you import multiple Knowledge Base articles (such as Articles, FAQ, Information, and Known Errors) via CSV files. It supports template download, data validation, and error handling for missing fields, duplicates, invalid file types, empty files, and oversized uploads.
Step 1: Go to the Knowledge Base page and click Create Knowledge Base → Import from CSV.
Step 2: Select the required category type, then click Download CSV File to download the empty template for preparing article data.
Step 3: Open the downloaded CSV file and fill in the required fields.
Title and Content must be provided.
Status must be either New or Published.
If the article is marked Private, add at least one User, Team, or User Tag.
Dates must follow the YYYY-MM-DD format.
Emails, tags, and URLs must be separated using semicolons (;).
Save the completed file in .csv format.
Step 4: Upload the prepared CSV file. Map each column to the corresponding system field on the Column Matching screen, then continue.
Step 5: The system validates all records. If there are issues—missing fields, duplicate titles, invalid file type, empty data, or oversized file—relevant error Messages are shown.
Step 6: Download invalid records if needed. Only valid entries will be imported.
Click Proceed with Valid Records to continue.
Step 7: Once the import is complete, the system shows “CSV uploaded successfully.” The imported articles will be added to the Knowledge Base and can be reviewed or updated.